With 94% of global enterprises now operating in the cloud as of 2026, the transition from legacy systems has become an inescapable strategic imperative. While the March 2029 end-of-life for Data Center products creates a clear timeline for migration, many leadership teams remain concerned that moving sensitive workloads might compromise their regulatory standing. You’re likely grappling with the intricacies of the Shared Responsibility Model, feeling the pressure to ensure that atlassian cloud security and compliance features align perfectly with your specific industry mandates.

We understand that the fear of data breaches during migration and the difficulty of mapping features to GDPR or HIPAA requirements can stall even the most vital digital transformations. This guide empowers you to master the complex security landscape, providing a clear roadmap to ensure your enterprise remains resilient and audit-ready. By implementing the advanced encryption protocols and data residency controls available in 2026, you’ll gain the confidence to scale without increasing your administrative burden.

We’ll explore the latest SOC 1 Type 2 attestations, the upcoming “Enterprise-Ready” Trust Program launching in October 2026, and the strategic advantages of Atlassian Guard Premium. This methodical approach transforms security from a perceived hurdle into a robust foundation for long-term operational stability.

Key Takeaways

  • Define the precise boundaries of the Shared Responsibility Model to establish a clear foundation of trust and accountability between your internal teams and the Atlassian platform.
  • Implement sophisticated atlassian cloud security and compliance features, including Atlassian Guard for centralized identity management and AES-256 encryption, to fortify your digital infrastructure.
  • Navigate the complexities of international regulatory standards by aligning your environment with the latest 2026 SOC 2 Type II and ISO/IEC 27001 audit benchmarks.
  • Adopt a “security by design” methodology by integrating automated compliance checks directly into your DevOps pipeline to mitigate legacy risks during cloud migration.
  • Leverage expert Atlassian Consulting to transition from fragmented security settings to a “Secure, Scalable, Stable” framework that ensures long-term operational resilience.

Understanding the Atlassian Cloud Shared Responsibility Model

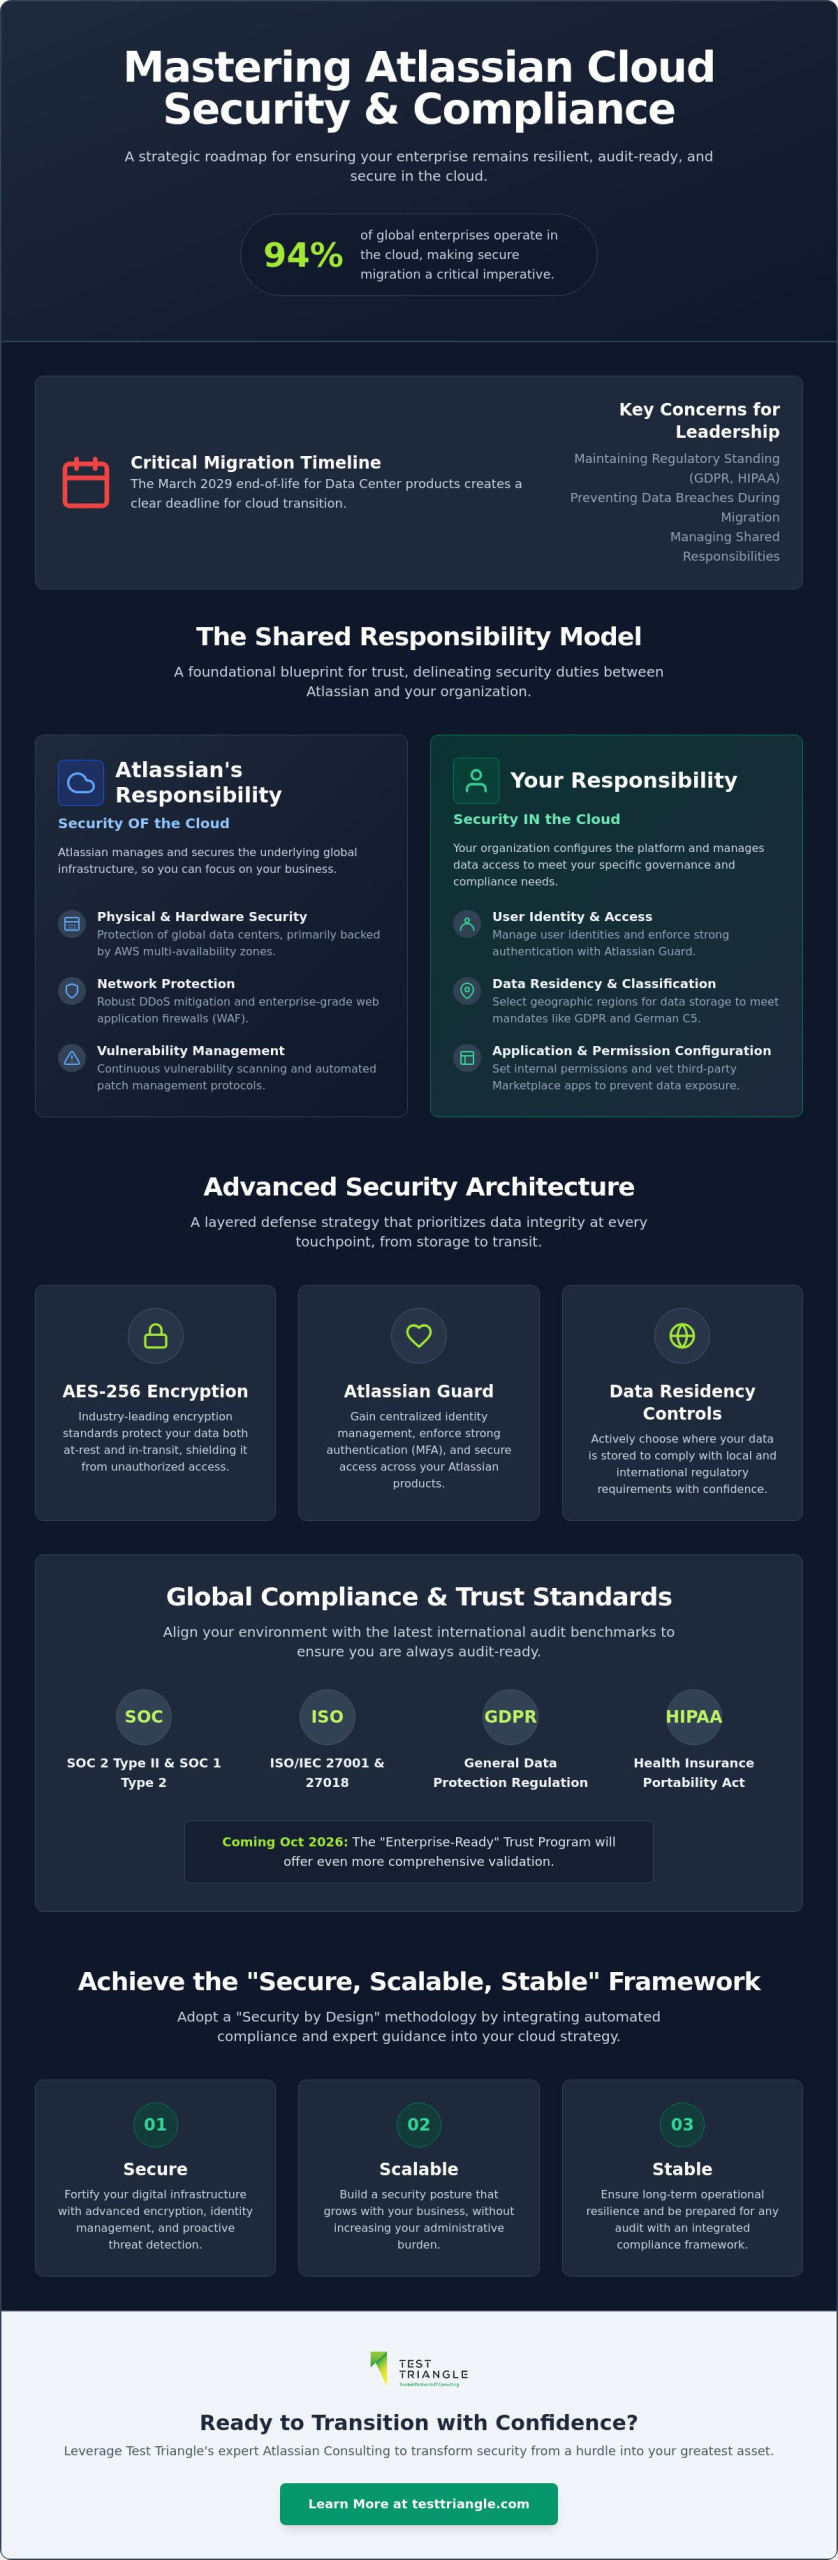
The Shared Responsibility Model functions as the foundational blueprint for trust between global enterprises and their cloud providers. It isn’t merely a technical division of labor; it’s a strategic framework that ensures organizational stability in a 2026 digital economy where data integrity is paramount. By clearly delineating which security layers are managed by the platform and which remain under your jurisdiction, this model allows leadership to allocate resources more effectively. Understanding these atlassian cloud security and compliance features is the first step toward building a resilient infrastructure that can withstand the evolving threat landscape.

The Infrastructure Layer: What Atlassian Protects

Atlassian assumes full ownership of the security “of” the cloud. This includes the physical protection of the global data center footprint, which is primarily backed by Amazon Web Services (AWS) across multiple availability zones. Their commitment to cloud security principles ensures that the underlying hardware and network layers are fortified against large-scale disruptions. You don’t have to worry about physical site access or the maintenance of server racks. Instead, you benefit from Atlassian’s sophisticated network-level protections, including robust DDoS mitigation and enterprise-grade web application firewalls. Their team manages continuous vulnerability scanning and automated patch management protocols, ensuring that the software foundation remains current without requiring manual intervention from your internal IT staff.

The Operational Layer: Your Strategic Obligations

While Atlassian secures the foundation, your organization is responsible for security “in” the cloud. This operational layer is where strategic Atlassian consulting and implementation becomes vital. You’re responsible for managing user identities, enforcing strong authentication via Atlassian Guard, and classifying data according to your internal risk profiles. In 2026, data residency has become a critical compliance requirement. You must actively select the specific geographic regions where your data resides to meet local legal mandates like GDPR or the German C5 standards. Additionally, the configuration of internal permissions and the vetting of third-party Marketplace apps fall squarely within your remit. Misconfigurations at this level are the most common cause of data exposure, making it essential to have a disciplined approach to access control. Utilizing the full suite of atlassian cloud security and compliance features requires an intentional effort to align platform capabilities with your unique corporate governance policies.

This partnership between Atlassian’s infrastructure and your operational oversight creates a comprehensive security posture. It reduces the total cost of ownership by offloading heavy lifting to the vendor while keeping you in the driver’s seat for data governance and user management.

Advanced Security Architecture: From Encryption to Atlassian Guard

Building on the shared responsibility framework, the technical architecture of the cloud environment provides the specific mechanisms required to protect corporate assets. These atlassian cloud security and compliance features represent a shift toward a holistic security posture that prioritizes data integrity at every touchpoint. In alignment with guidance from the Cloud Security Alliance, the platform implements a layered defense strategy that begins with industry-leading encryption standards. This approach ensures that information remains shielded from unauthorized access, whether it’s stored within an application or moving across the global network.

Encryption and Data Privacy Controls

Data at rest is secured using AES-256 encryption; meanwhile, data in transit relies on TLS 1.2 or higher to prevent interception. For enterprises with stringent regulatory needs, Bring Your Own Key (BYOK) capabilities allow for direct control over encryption keys. This ensures that even the cloud provider can’t access raw data without explicit authorization. Data residency features further enhance this control by allowing organizations to pin data to specific regions. In 2026, this includes expanded support for locations like Germany (C5 Type 2) and Spain (ENS). To further protect privacy, data scrubbing and anonymization tools are increasingly utilized in non-production environments to prevent the exposure of sensitive information during testing phases.

Atlassian Guard: The Enterprise Security Hub

Atlassian Guard serves as the central command center for identity and access management. It bridges the gap between your corporate directory and your cloud products, facilitating seamless Single Sign-On (SSO) with providers like Azure AD, Okta, or Google Workspace. By utilizing System for Cross-domain Identity Management (SCIM), organizations can automate user provisioning and de-provisioning. This automation is critical. It eliminates “zombie” accounts that often serve as entry points for unauthorized access. Key benefits of Guard include:

  • Enforced Security Policies: Mandatory Two-Factor Authentication (2FA) across the entire organization.
  • Centralized Visibility: A single pane of glass for monitoring user activity and API token usage.
  • Anomalous Behavior Detection: AI-driven insights that identify unusual patterns, such as rapid data egress or suspicious login attempts.

As we move through 2026, the architecture has evolved from perimeter-based defenses to a Zero Trust model. Access is no longer granted based on network location but through continuous identity verification. Since June 2026, user API token monitoring is available to all customers at no extra cost, providing a significant boost to visibility without increasing spend. To ensure these atlassian cloud security and compliance features are configured to your specific risk profile, speaking with an implementation partner can provide the necessary strategic oversight to maintain a secure and compliant environment.

Global Compliance Standards: GDPR, SOC 2, and Industry Specifics

The 2026 audit landscape demands more than just checkboxes; it requires a deep integration of regulatory controls into every workflow. Reviewing Atlassian’s SOC 2 Type II and SOC 3 reports for 2026 reveals a commitment to the highest standards of availability and confidentiality. These reports, alongside the SOC 1 Type 2 attestation achieved in Q4 2025 for Jira and Confluence, provide the transparent documentation necessary for enterprise risk assessments. By aligning with ISO/IEC 27001 and 27018, the platform offers a globally recognized benchmark for information security management that satisfies most jurisdictional requirements. However, the true strength of atlassian cloud security and compliance features lies in their ability to adapt to specific regional mandates, such as the German C5 Type 2 attestation provided in Q1 2026 or the ENS requirements in Spain slated for Q4 2026.

A significant challenge for many organizations remains the third-party ecosystem. To address this, the “Enterprise-Ready” Trust Program launches in October 2026, replacing the older “Cloud Fortified” badge with stricter standards for security and reliability. This program, combined with the “Runs on Atlassian” initiative for Forge apps, ensures that your Marketplace integrations don’t become a weak link in your compliance chain. For Australian enterprises, maintaining this chain includes ensuring that specialized financial tools like Trancher are integrated into a broader strategy for end-to-end AML/CTF program management. These initiatives allow for better control over data egress and ensure that app storage matches the data residency of the host product.

GDPR and Evolving Privacy Regulations

GDPR compliance has evolved beyond simple data processing agreements. Today, automated tools for the “right to be forgotten” allow administrators to execute data deletion and export requests across the entire site with precision. As AI adoption grows, managing data usage within Atlassian Rovo, which now serves over 5 million monthly active users, is paramount. Strategic governance ensures that AI-powered insights don’t inadvertently expose sensitive personal data, maintaining the integrity of your Data Processing Addendums (DPA). It’s essential to configure these tools to prevent unauthorized data egress while still leveraging the productivity gains of enterprise AI.

Industry-Specific Compliance: Pharma and Finance

For life sciences, GxP compliance is non-negotiable. The platform provides validated instances and comprehensive audit trails that allow for the meticulous tracking of every change, ensuring your environment remains audit-ready for health authority inspections. Similarly, financial institutions must navigate the complex requirements of BaFin, EBA, and APRA. Jira and Confluence are designed to support these standards through granular permission schemes and data residency pinning. Our expert Atlassian Consulting ensures these standards are met during implementation through rigorous validation and audit trail configuration. By leveraging these atlassian cloud security and compliance features, highly regulated firms can achieve a level of operational resilience that was previously difficult to maintain in a cloud-only environment.
Atlassian Cloud Security and Compliance Features: The 2026 Enterprise Strategic Guide

Security by Design: Integrating Compliance into Cloud Migration

Successful cloud migration requires a shift from reactive patching to a “Security by Design” philosophy. This methodology ensures that compliance isn’t an afterthought but a core component of the transition process. By leveraging atlassian cloud security and compliance features during the initial planning phases, enterprises can identify legacy risks that may have accumulated in on-premise environments over years of operation. This proactive stance reduces technical debt and streamlines cloud configurations, ensuring your new environment is built on a foundation of operational excellence and risk mitigation.

The Security Audit and Assessment Phase

Before any data moves, a comprehensive audit is essential to establish a baseline of trust. This begins with rigorous data classification to determine which workloads are suitable for the cloud and which require additional safeguards. It’s the ideal moment to implement the Principle of Least Privilege (PoLP) by cleaning up years of permission sprawl. Enterprises should also evaluate their ecosystem using the new “Enterprise-Ready” Trust Program, which replaces the Cloud Fortified badge in October 2026. Evaluating the security posture of Marketplace plugins is now more structured thanks to the Partner Security Incident Response Program established on June 18, 2026. This allows for a joint investigation of incidents affecting third-party apps, ensuring your entire ecosystem remains resilient and audit-ready from day one.

Continuous Compliance in a DevOps World

Security doesn’t end when the “migration complete” notification arrives. Integrating compliance checks into your DevOps Consulting pipeline ensures that custom integrations and configurations remain secure as they evolve. Real-time alerting and incident response planning are critical for maintaining visibility in complex cloud environments. For instance, the security bulletin from June 16, 2026, which addressed 76 high-severity and 24 critical vulnerabilities, highlights the need for rapid patch validation. By utilizing Software Test Automation Services, organizations can automatically verify that security patches don’t disrupt core functionalities. This continuous monitoring approach allows teams to respond to threats with agility while maintaining the integrity of their atlassian cloud security and compliance features.

Maintaining this level of technical rigor requires a partner who understands the intersection of security and speed. If you’re ready to build a compliant, high-performance cloud environment that scales with your ambition, contact our strategic consultants today to begin your security assessment.

Optimising Security with Test Triangle’s Atlassian Consulting

While the technical capabilities of the cloud platform are robust, the human element remains the deciding factor in enterprise resilience. Orchestrating the complex settings of atlassian cloud security and compliance features requires more than just a manual; it demands a strategic visionary who can align these tools with global business objectives. Test Triangle acts as a steady hand in this fast-changing technological landscape, employing a “Secure, Scalable, Stable” framework to ensure your digital infrastructure doesn’t just meet today’s standards but is prepared for the regulatory shifts of 2027 and beyond. By bridging the gap between raw technical features and business-critical compliance, we transform security from a cost center into a foundation for organizational progress.

Maintaining 24/7 security vigilance is a significant undertaking for internal IT departments already stretched by digital transformation demands. By leveraging our Managed Service Provider Subscription Fees model, organizations gain access to continuous monitoring and expert oversight that ensures no vulnerability goes unaddressed. This partnership model provides the peace of mind derived from risk reduction, allowing your leadership to focus on core innovation while we manage the intricacies of your cloud environment. We prioritize operational efficiency and systemic improvement, ensuring that your security posture evolves in tandem with your growth.

Strategic Roadmapping and Advisory

We don’t believe in one-size-fits-all solutions. Our consulting begins with tailored security configurations based on your specific industry risk profile, whether you’re navigating the GxP requirements of life sciences or the stringent mandates of the financial sector. We provide expert guidance on Atlassian Guard implementation and complex IAM integration with industry-leading platforms like Azure AD and Okta. To support these initiatives, our staffing solutions provide dedicated security experts who act as an extension of your team, ensuring that your atlassian cloud security and compliance features are managed with institutional maturity and technical rigor.

Long-Term Partnership and Support

Resilience is a continuous journey rather than a destination. We act as a reliable long-term collaborator, providing regular security health checks and compliance re-validation services to address the evolving threat landscape. Our approach includes training your team on Atlassian security best practices and threat awareness, empowering your workforce to become the first line of defense. This methodical and highly structured support system ensures that your organization remains audit-ready and resilient. To begin fortifying your infrastructure, contact Test Triangle today for a comprehensive Atlassian Cloud Security Assessment and secure your enterprise’s digital future.

Future-Proofing Your Enterprise Digital Ecosystem

The transition to a resilient cloud environment requires more than just deploying software; it necessitates a disciplined alignment of platform capabilities with rigorous corporate governance. By mastering the atlassian cloud security and compliance features discussed in this guide, your organization can move beyond the complexities of the Shared Responsibility Model to achieve a state of operational excellence. This strategic evolution ensures that your data remains protected, your audits stay green, and your teams remain empowered to innovate without the fear of security compromises or regulatory friction.

As an Atlassian Gold Solution Partner with ISO 27001 certified processes, Test Triangle provides the institutional maturity and technical rigor required to manage your most sensitive workloads. Our global delivery model offers 24/7 managed support, providing a Secure, Scalable, Stable foundation that acts as a reliable long-term collaborator for your business. We’re ready to help you bridge the gap between technical execution and long-term operational stability through expert-led managed services that grow with your ambition.

Secure Your Infrastructure with Test Triangle’s Atlassian Consulting and embrace the confidence of a fully compliant digital future.

Frequently Asked Questions

Is Atlassian Cloud more secure than on-premise Data Center deployments?

Atlassian Cloud provides superior security through centralized infrastructure management and rapid patch deployment. While Data Center relies on manual updates, cloud instances benefit from immediate vulnerability remediation, such as the 100 high and critical vulnerabilities addressed in June 2026. This model reduces the risk of zero-day exploits and allows your IT staff to focus on strategic governance rather than hardware maintenance.

How does Atlassian Guard help with enterprise compliance requirements?

Atlassian Guard serves as the primary engine for identity-based compliance by enforcing mandatory Two-Factor Authentication (2FA) and centralized Single Sign-On (SSO). It facilitates automated user provisioning via SCIM, which eliminates the risk of “zombie” accounts. These atlassian cloud security and compliance features provide the audit trails and access controls necessary to satisfy SOC 2 and ISO 27001 requirements across your entire digital ecosystem.

Where is my data stored in Atlassian Cloud and can I choose the location?

Your data is stored within a global network of AWS-backed data centers. Enterprise customers can utilize data residency controls to pin primary product data to specific geographic regions, such as Germany for C5 compliance or Spain for ENS requirements. This capability ensures that your organizational data remains within jurisdictional boundaries, satisfying local legal mandates and reducing the complexity of international privacy regulations.

What happens to my data security when I use Atlassian Marketplace apps?

Security for Marketplace apps is a shared responsibility between Atlassian, the app vendor, and your organization. To mitigate risks, you should prioritize apps within the “Enterprise-Ready” Trust Program or the “Runs on Atlassian” initiative. These programs ensure higher standards for data egress control and residency matching, providing a more secure and predictable environment for third-party integrations.

Does Atlassian Cloud support HIPAA compliance for healthcare organizations?

Yes, Atlassian Cloud supports HIPAA compliance for Jira, Confluence, and Jira Service Management. Organizations must enter into a Business Associate Agreement (BAA) and configure their instances to meet specific administrative and technical safeguards. This includes implementing strong encryption and granular access controls to ensure that Protected Health Information (PHI) is managed with the highest standards of confidentiality and integrity.

How can I automate security monitoring within Jira and Confluence?

Automation is achieved through Atlassian Guard’s proactive threat detection and real-time alerting systems. Since June 2026, all customers can monitor user API token usage at no extra cost to identify suspicious activity. Additionally, AI-driven insights within the platform detect anomalous user behaviors, such as rapid data exports, allowing for an immediate incident response that maintains the integrity of your atlassian cloud security and compliance features.

What is the Shared Responsibility Model in the context of Atlassian Cloud?

The Shared Responsibility Model defines the division of security obligations between the provider and the client. Atlassian is responsible for the security “of” the cloud, including physical hardware and network infrastructure. Conversely, your organization is responsible for security “in” the cloud, which encompasses user access management, data classification, and the secure configuration of your specific application instances.

How often does Atlassian undergo third-party security and compliance audits?

Atlassian undergoes rigorous third-party audits on a continuous basis to maintain its various certifications. For instance, Jira and Confluence were attested against SOC 1 Type 2 requirements in Q4 2025, and a German C5 Type 2 attestation was provided in Q1 2026. These regular evaluations ensure that the platform’s security controls remain effective against the evolving threat landscape and current global benchmarks.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.
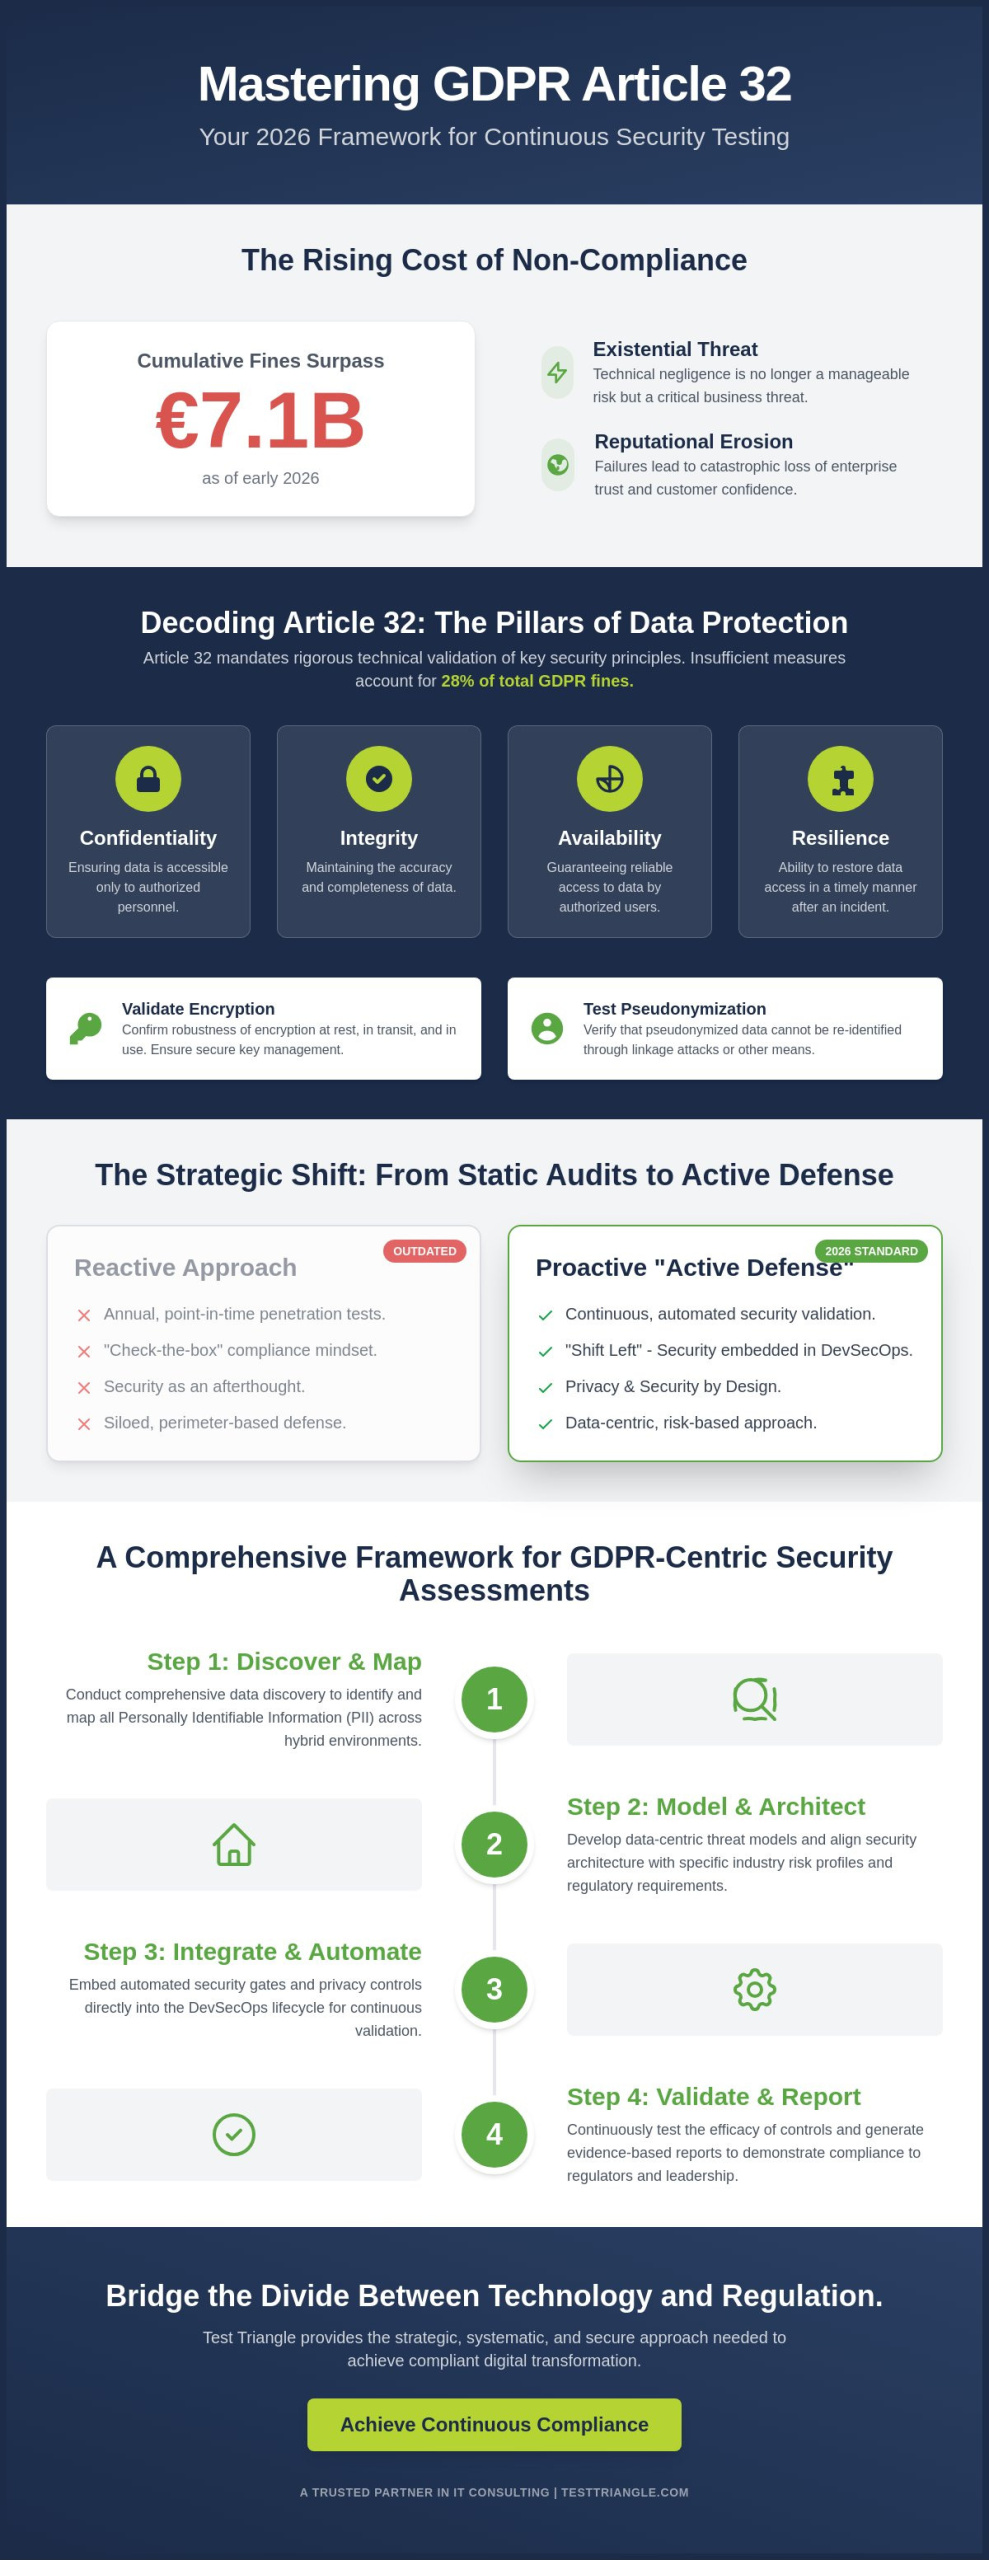
With cumulative GDPR fines surpassing €7.1 billion as of early 2026, the cost of technical negligence has evolved from a manageable risk into a potential existential threat for the global enterprise. You likely feel the pressure of the ambiguity surrounding “regular testing” in Article 32, which often leaves leadership questioning if their current protocols are sufficient to withstand modern regulatory scrutiny. Maintaining a consistent security posture across complex, hybrid cloud environments is a significant undertaking, especially as the enforcement of the EU AI Act in August 2026 adds another layer of complexity to data protection.

This guide provides a definitive roadmap to master the technical requirements of Article 32 and implement a robust framework for security testing for gdpr compliance that ensures your organization remains continuously protected. By aligning your security strategy with proven methodologies, you’ll reduce organizational risk and achieve a seamless integration of privacy controls into your digital transformation. We’ll examine the specific activities required to build a validation framework that is continuous, comprehensive, and compliant; ensuring your enterprise stays ahead of shifting global standards through a blend of human expertise and technical precision.

Key Takeaways

  • Transition from static compliance snapshots to a dynamic “active defense” posture to meet the heightened scrutiny of 2026 regulatory bodies.
  • Implement a systematic framework for security testing for gdpr compliance to validate the efficacy of technical controls like encryption and pseudonymization under Article 32.
  • Adopt a “shift left” strategy within the DevSecOps lifecycle by embedding automated security gates that identify vulnerabilities before they reach production environments.
  • Develop a data-centric assessment roadmap starting with comprehensive discovery and threat modeling to align security architecture with specific industry risk profiles.
  • Bridge the divide between technical execution and regulatory requirements through a strategic, systematic, and secure approach to digital assurance.

In the current regulatory climate, security testing for gdpr compliance has transitioned from a peripheral IT concern to a core executive mandate. It represents the systematic validation of technical controls designed to protect personal data from unauthorized access, accidental loss, or unlawful processing. As established by the General Data Protection Regulation (GDPR), organizations must prove their defenses are not just present but effective in real-world scenarios. By 2026, regulators have shifted their focus toward “active defense,” requiring enterprises to demonstrate that their security measures are reliable, resilient, and robust against sophisticated attack vectors.

The consequences of failing to validate these controls extend far beyond the tiered fine structure, which has already seen cumulative penalties exceed €7.1 billion since enforcement began. While the €1.2 billion in fines issued in 2025 highlights the immediate financial risk, technical negligence causes deeper damage through severe reputational erosion and a catastrophic loss of enterprise trust. As companies accelerate their digital transformation initiatives, the resulting expansion of attack surfaces for Personally Identifiable Information (PII) creates new, complex vulnerabilities. These evolving digital ecosystems require an evidence-based approach to security that connects technical execution directly to business stability.

The Reality of Article 32 in a Modern Tech Stack

Article 32 mandates the implementation of “appropriate technical and organizational measures” (TOMs) to ensure a level of security appropriate to the risk. In 2026, the rise of cloud-native architectures, microservices, and distributed data lakes has fundamentally complicated the definition of what constitutes an “appropriate” measure. Legacy security approaches that rely on perimeter defense are no longer sufficient in a world where data flows across borderless, hybrid environments. Modern validation must be data-centric, focusing on the integrity and availability of information within complex tech stacks to ensure that technical managers and executive leadership remain aligned on risk reduction.

From Check-the-Box to Strategic Assurance

Relying on annual penetration tests is an insufficient strategy for 2026 compliance because a single point-in-time audit cannot account for the rapid pace of continuous deployment. Strategic assurance requires embedding “Security by Design” directly into the software testing lifecycle, ensuring that privacy controls are verified at every stage of development. By moving away from reactive audits and toward proactive validation, organizations can maintain a posture that is integrated, iterative, and impactful. Ultimately, security testing for gdpr compliance is a continuous risk-mitigation strategy that evolves alongside the threat landscape to provide long-term operational stability.

Decoding Article 32: Technical Validation of Data Protection Measures

To achieve a state of continuous readiness, enterprises must move beyond superficial audits and embrace a rigorous technical validation of their data protection environments. Article 32 of the GDPR serves as the foundational legal framework for this requirement, explicitly mandating that organizations implement measures to ensure the confidentiality, integrity, availability, and resilience of processing systems. With insufficient technical and organizational measures under Article 32 accounting for 28% of total GDPR fines, security testing for gdpr compliance requires a sophisticated, compliance-driven approach that simulates real-world exploitation to verify that these four pillars remain uncompromised.

Technical validation is particularly critical when assessing the efficacy of pseudonymization and encryption. It isn’t enough to simply state that data is encrypted; testing must confirm that encryption remains robust across all states, including at rest, in transit, and in use. This process involves verifying that cryptographic keys are managed securely and that pseudonymized data cannot be re-identified through unauthorized correlation. By adopting a “Strategic, Systematic, Secure” methodology, organizations can provide the documented proof of technical efficacy that regulators demand.

Testing for Confidentiality and Data Integrity

Ensuring confidentiality requires a granular assessment of access controls and the potential for privilege escalation within the application architecture. As enterprises increasingly rely on interconnected ecosystems, API testing becomes a vital component in preventing unauthorized data leakage between disparate services. For complex, logic-based security flaws that automated scanners often miss, integrating Manual Testing ensures that human expertise identifies vulnerabilities in business logic that could lead to unauthorized data access. These efforts ensure that personal data remains shielded from internal and external threats alike.

Evaluating System Resilience and Availability

The “Restoration and Recovery” clause of Article 32 highlights the necessity of maintaining high availability and the ability to restore access to personal data in a timely manner following a physical or technical incident. Performance testing acts as a critical proxy for availability compliance, which is a cornerstone of comprehensive security testing for gdpr compliance, allowing teams to stress test systems under extreme loads to ensure stability during traffic surges or coordinated DDoS attempts. Verifying the “Ability to Restore” through rigorous backup validation testing confirms that disaster recovery protocols are not just theoretical but operational. If you’re looking to refine your technical validation strategy, you might consult with our strategic advisory team to ensure your framework meets these rigorous standards.

Security Testing for GDPR Compliance in 2026: A Strategic Enterprise Guide

Integrating Security Testing into the DevSecOps Lifecycle

To maintain a posture of continuous readiness in 2026, enterprises must move beyond reactive audits and embed security testing for gdpr compliance directly into the software development lifecycle. This “shift left” methodology ensures that privacy considerations are not an afterthought but a foundational requirement identified during the initial design and coding phases. By detecting vulnerabilities before they reach production, organizations can significantly reduce the risk of the massive fines and reputational erosion discussed earlier. This proactive approach aligns technical execution with the NIST Cybersecurity Framework, providing a structured path toward the “appropriate technical measures” mandated by Article 32.

The implementation of automated security gates within CI/CD pipelines acts as a critical checkpoint for persistent compliance. These gates allow for the rapid, repeatable validation of code against security benchmarks, ensuring that every deployment remains within the defined risk tolerance of the organization. Achieving this level of integration often requires specialized expertise, where DevOps Consulting serves as the strategic bridge between rapid delivery and regulatory rigor. Through this synergy, security becomes a silent enabler of digital transformation rather than a bottleneck to innovation.

Securing the Enterprise Ecosystem: Atlassian and ServiceNow

Modern enterprises frequently manage sensitive PII within specialized platforms, yet these environments often remain untested for privacy-specific vulnerabilities. A comprehensive strategy must include rigorous validation for Atlassian Implementation to ensure that collaborative data remains shielded from unauthorized internal access. Similarly, validating data privacy within ServiceNow Consulting workflows is essential to prevent third-party integrations from creating GDPR blind spots. These platforms require tailored security testing for gdpr compliance to ensure that automated service management doesn’t inadvertently lead to data exposure.

The Managed Service Advantage for Compliance

Maintaining a 24/7 security posture is an intensive undertaking that often stretches internal resources beyond their capacity. Utilizing a Managed Outsourcing model provides the “steady hand” needed for recurring security assessments and persistent monitoring. This approach allows enterprises to leverage specialized talent through strategic staffing, ensuring that security remains a constant priority. By delegating the technical execution of compliance-driven testing to a reliable long-term collaborator, leadership can focus on high-level strategic growth while maintaining the peace of mind that their digital infrastructure is managed with professional precision.

A Comprehensive Framework for GDPR-Centric Security Assessments

Establishing a resilient security posture requires a transition from broad data visibility to granular technical validation through a framework defined by Discovery, Defense, and Documentation. To ensure that security testing for gdpr compliance delivers tangible risk reduction, organizations must follow a structured five-step lifecycle that aligns technical execution with regulatory expectations:

  • Step 1: Data Discovery and Mapping: Establishing a complete inventory of personal data assets and flows is the prerequisite for any testing activity; you can’t protect what you haven’t identified.
  • Step 2: Threat Modeling: This involves identifying likely attack vectors specific to your industry and infrastructure, allowing for a prioritized defense strategy that addresses the most critical vulnerabilities first.
  • Step 3: Vulnerability Assessment and Penetration Testing (VAPT): As the core execution phase, this combines automated scanning with human-led exploitation to uncover deep-seated flaws in the security architecture that automated tools often miss.
  • Step 4: Remediation and Re-testing: Identified risks must be addressed through systematic patching or configuration changes, followed by rigorous re-testing to confirm the closure of the vulnerability loop.
  • Step 5: Documentation and Reporting: This final step creates the essential “audit trail” for regulators, providing the documented proof of technical efficacy required during a Data Protection Impact Assessment (DPIA) or a post-breach investigation.

Industry-Specific Testing Nuances: Pharma and Finance

In the pharmaceutical sector, security testing for gdpr compliance must often be harmonized with stringent GxP requirements to ensure data integrity across the entire drug development lifecycle. Managing these dual mandates requires a workforce that understands both clinical validation and data privacy; utilizing specialized Pharma IT Staffing ensures your team possesses the necessary regulatory fluency. Conversely, financial institutions face high-frequency testing demands due to the sensitive nature of transaction data and the rapid pace of fintech innovation, necessitating a “Continuous, Comprehensive, Compliant” validation model that mirrors their operational complexity.

Critical Testing Types for 2026 Compliance

Modern assessments must incorporate Static and Dynamic Application Security Testing (SAST/DAST) to identify vulnerabilities within both the source code and the running application environment. Additionally, Cloud Infrastructure Entitlement Management (CIEM) validation is essential for managing the complex permissions that often lead to data exposure in hybrid cloud settings. The “Gold Standard” of a 2026 security audit report is an evidence-based, machine-readable document that maps every technical remediation directly to the specific Article 32 control it satisfies. If you’re ready to implement a framework that balances technical rigor with regulatory precision, connect with our strategic consultants today.

Test Triangle: Your Strategic Partner for Compliant Digital Transformation

Test Triangle stands as the essential bridge between rigorous technical execution and the stringent demands of 2026 regulatory frameworks. By adopting a “Strategic, Systematic, Secure” approach to Software and Digital Assurance, we empower global enterprises to navigate the complexities of data protection with absolute confidence. Our team brings together multi-industry expertise and a globally-minded perspective to ensure that your security testing for gdpr compliance isn’t just a periodic checklist but a core component of your long-term operational stability. We focus on the peace of mind derived from risk reduction, allowing your leadership to focus on large-scale technological evolution while we manage the intricate details of your digital defense.

Our methodology connects deep technical proficiency with high-level business outcomes, ensuring that every validation activity provides a tangible benefit to the client’s security posture. We operate as a seasoned expert who values stability and precision, helping organizations move beyond fragmented security efforts toward a unified validation framework. By orchestrating a blend of human expertise and advanced technical tools, we provide a steady hand in a fast-changing technological landscape. This collaborative spirit ensures that your enterprise remains resilient against the sophisticated threats that define the modern digital era.

Beyond Testing: A Holistic IT Partnership

We recognize that maintaining a secure posture requires more than isolated audits; it demands a holistic partnership that leverages IT Service Management to foster long-term resilience and stability within your digital infrastructure. Our approach integrates specialized staffing solutions to ensure your internal teams are supported by experts who understand the nuances of platforms like ServiceNow and Atlassian. Global enterprises trust us for their complex digital evolutions because we act as a reliable long-term collaborator, deeply invested in their institutional maturity and scalable growth. This comprehensive support model ensures that security remains a constant, proactive force within your organization.

Next Steps for Your Compliance Roadmap

To begin roadmapping your 2026 compliance journey, we recommend performing a rigorous gap analysis of your current security testing frequency and evaluating the maturity of your DevSecOps integration. Identifying these areas for improvement is the first step toward reducing organizational risk and achieving a seamless integration of security into your digital transformation. We invite your leadership team to contact us for a comprehensive security assessment tailored to your enterprise’s unique requirements. By partnering with us, you ensure that your security testing for gdpr compliance remains robust, iterative, and fully aligned with the evolving global standards of data protection.

Securing Your Enterprise Future: The Path to Continuous Resilience

As the regulatory landscape matures, the transition from static, point-in-time audits to a model of continuous, comprehensive, and compliant validation has become an operational necessity. Enterprises must move beyond reactive measures and embrace a framework that integrates security testing for gdpr compliance into the core of their digital transformation strategy. By prioritizing the technical pillars of Article 32 and embedding automated safeguards within the DevSecOps lifecycle, organizations can achieve a state of persistent readiness that protects both their sensitive data and their market reputation.

Test Triangle acts as a reliable long-term collaborator for global enterprises navigating these complex technical requirements. As a strategic Atlassian and ServiceNow partner with specialized expertise in pharma and finance compliance, we provide the technical precision and regulatory fluency needed to manage diverse infrastructures across Europe, North America, and Asia. Our global delivery model ensures that your organization benefits from a steady hand in a fast-changing technological landscape, delivering the peace of mind that comes from professional risk reduction. Our approach is designed to be precise, proactive, and persistent, ensuring your digital evolution remains uncompromised.

Secure Your Enterprise: Schedule a GDPR Compliance Security Assessment with Test Triangle

The journey toward technical excellence is a collaborative evolution; we look forward to supporting your organization’s long-term success and operational stability.

Frequently Asked Questions

Does GDPR Article 32 explicitly require penetration testing?

While Article 32 does not explicitly name “penetration testing,” it mandates a process for regularly testing and evaluating the effectiveness of technical measures. Penetration testing is widely recognized by European data protection authorities as the standard method for fulfilling this requirement. It provides the empirical evidence needed to demonstrate that your “active defense” is functional and resilient against contemporary threats.

How often should an enterprise conduct security testing for GDPR compliance?

Enterprises should align testing frequency with their specific risk profile, typically conducting comprehensive security testing for gdpr compliance at least annually or following significant architectural changes. For high-risk processing environments, such as those in finance or pharma, a more frequent or continuous validation model is often necessary to maintain a defensible posture. This ensures that new vulnerabilities introduced during rapid deployment cycles are identified and remediated promptly.

What is the difference between a vulnerability scan and a GDPR penetration test?

A vulnerability scan is a broad, automated discovery process that identifies known security flaws within your infrastructure. In contrast, a GDPR penetration test is a targeted, human-led exercise that simulates actual exploitation to verify if those flaws can be used to access personal data. While scans provide high-level visibility, penetration tests offer the deep technical validation required to prove the resilience of your Article 32 controls.

Can automated security testing replace manual penetration testing for compliance?

Automated security testing cannot fully replace manual penetration testing because it lacks the cognitive ability to identify complex logic-based flaws or chain multiple minor vulnerabilities. Automation is highly effective for maintaining frequency within CI/CD pipelines, but manual testing provides the human expertise necessary to evaluate business logic and unauthorized data correlation. A balanced approach combines both to ensure comprehensive coverage across your entire digital ecosystem.

How do I prove to a regulator that my security testing is ‘appropriate’?

Proving that testing is “appropriate” requires detailed documentation that maps technical activities directly to the risks identified in your Data Protection Impact Assessment (DPIA). You must demonstrate a closed-loop remediation process where vulnerabilities are not only identified but also systematically patched and re-tested. This creates a machine-readable audit trail that provides regulators with evidence of your organization’s commitment to proactive data protection.

What are the common security testing pitfalls that lead to GDPR fines?

Common pitfalls include a “check-the-box” mentality that ignores the “ability to restore” clause or neglects the security of third-party API integrations. Many organizations also fail to include legacy systems in their scope, creating blind spots where personal data remains vulnerable. Avoiding these errors requires a strategic, systematic, and secure testing framework that addresses all four technical pillars of Article 32.

How does security testing change for organizations using Atlassian Cloud?

For organizations utilizing Atlassian Cloud, the focus of security testing for gdpr compliance shifts from server-level maintenance to the validation of platform configurations and shared responsibility models. Testing must prioritize user access controls, data residency settings, and the security of marketplace app integrations that may have access to your PII. This ensures that your collaborative environments remain compliant while leveraging the scalability of cloud-native enterprise software.

Is security testing required for internal-only employee data systems?

Yes, security testing is mandatory for internal-only systems because the GDPR protects all personal data, including that of your employees. HR databases and internal communication platforms often contain sensitive PII that requires the same level of technical validation as customer-facing applications. Neglecting these systems creates a significant risk of internal data breaches, which are subject to the same tiered fine structure as external violations.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.