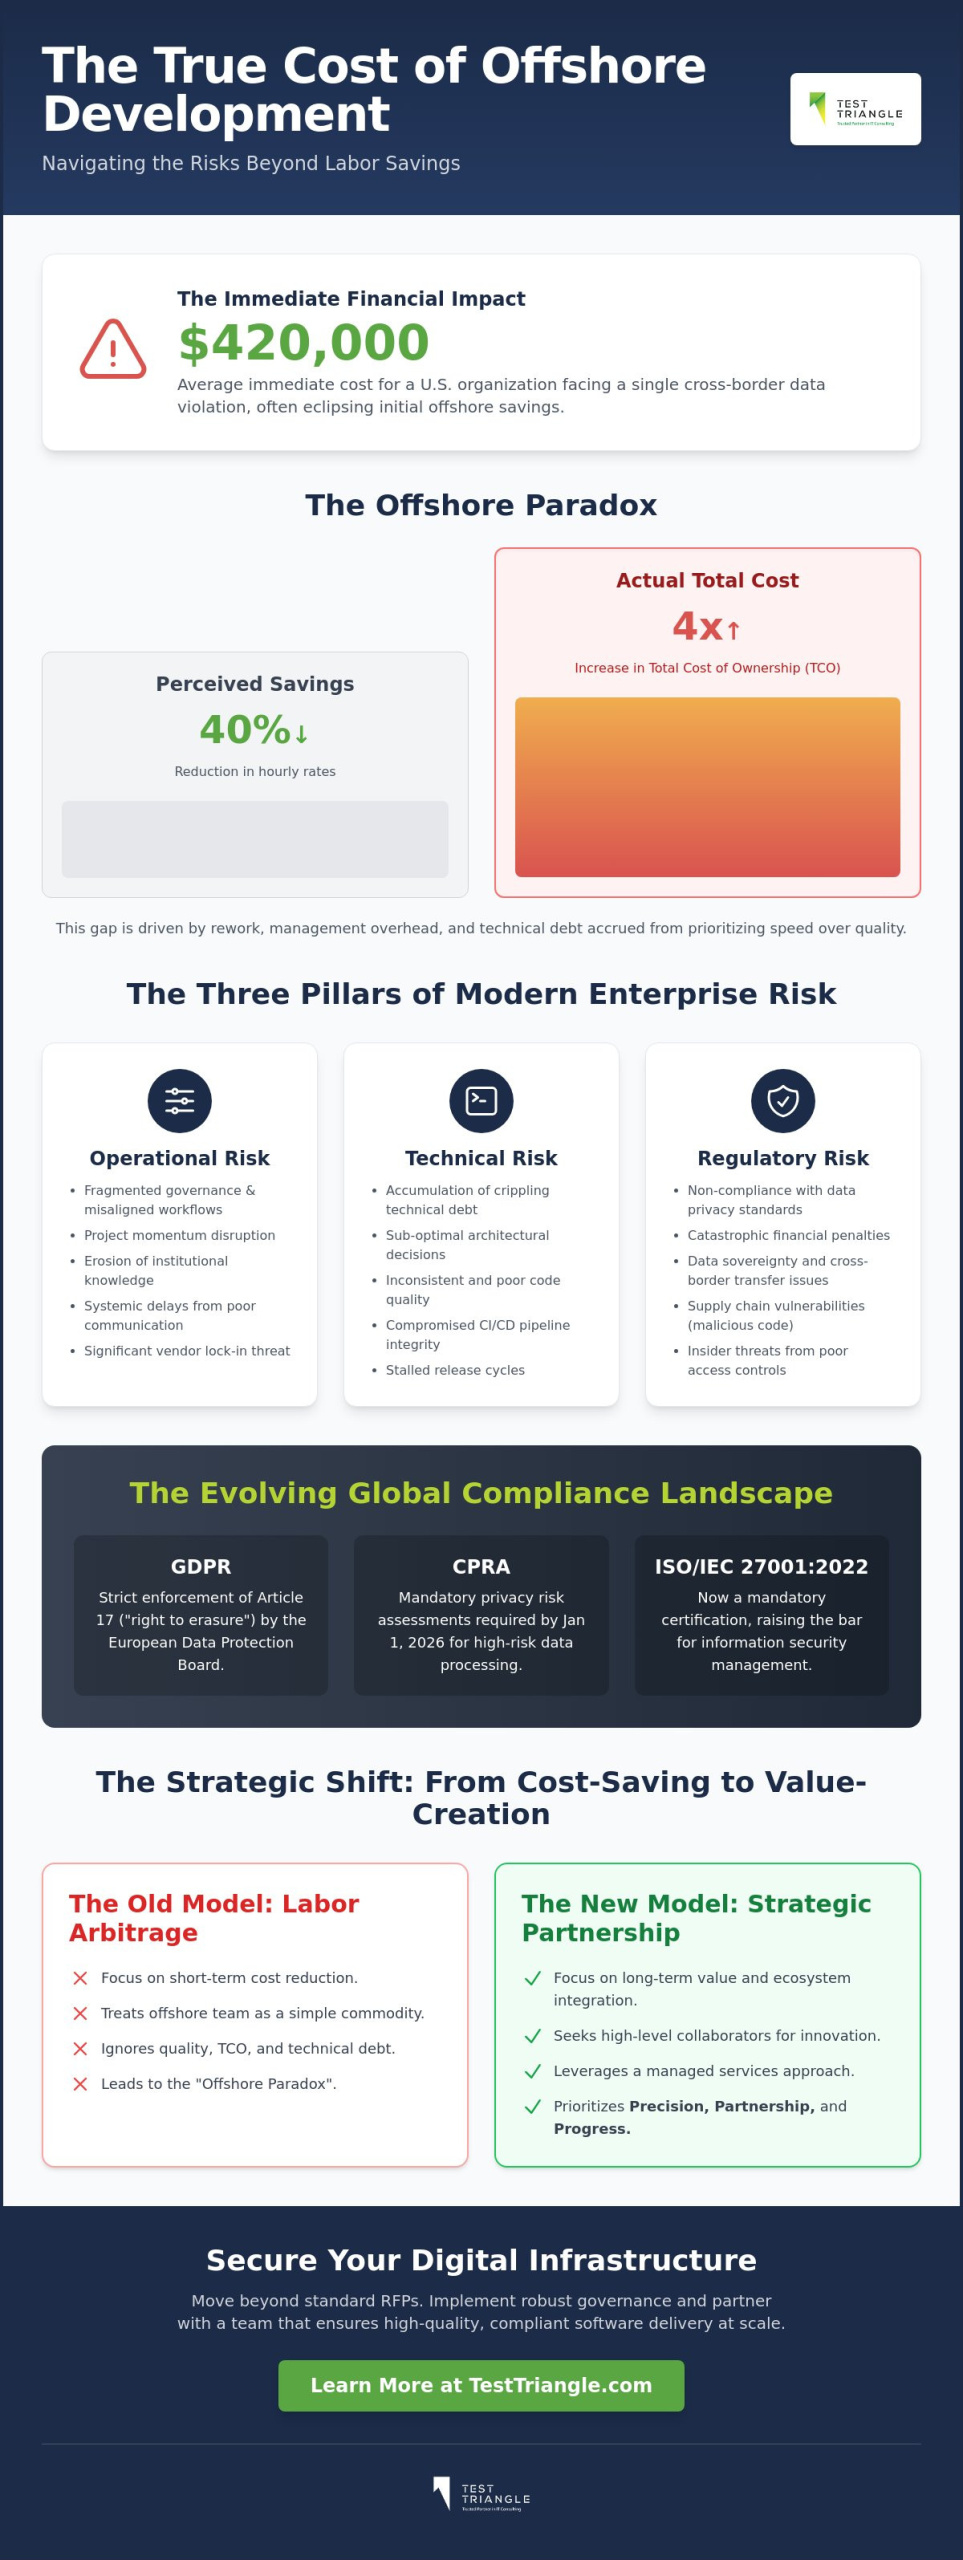
When a cross-border data violation occurs, the average U.S. organization faces $420,000 in immediate costs, a figure that often eclipses the initial savings of a distributed model. You understand that the risks of hiring offshore development teams involve more than just time zone friction; they encompass unpredictable code quality and the looming threat of technical debt in highly regulated sectors like Finance and Pharma. As global data privacy regulations tighten, including the now-mandatory ISO/IEC 27001:2022 certifications, the gap between a low-cost vendor and a strategic partner becomes a matter of institutional survival.

This article provides the methodology to evaluate, mitigate, and master these complexities to ensure your digital infrastructure remains secure and performant. We’ll explore a comprehensive risk-assessment checklist and governance strategies designed to facilitate high-quality, compliant software delivery at scale. By aligning technical execution with business outcomes, we help you secure the stability, precision, and progress necessary for long-term operational success.

Key Takeaways

  • Transition from simple labor arbitrage to strategic ecosystem integration to ensure your offshore model delivers long-term value rather than just short-term cost savings.
  • Identify and neutralize the risks of hiring offshore development teams by implementing rigorous data sovereignty protocols and intellectual property safeguards tailored for highly regulated sectors.
  • Evaluate the true total cost of ownership by accounting for the quality gap and technical debt that often result when speed is prioritized over architectural sustainability.
  • Establish robust governance through quality-centric KPIs and vendor selection processes that move beyond the standard Request for Proposal to verify actual operational maturity.
  • Leverage a managed service approach to achieve precision, partnership, and progress, ensuring high-compliance delivery across global digital infrastructures.

The Strategic Landscape of Offshore Development Risks in 2026

The global delivery landscape has undergone a fundamental transformation, shifting from a model of simple labor arbitrage to one of complex ecosystem integration. In 2026, enterprises no longer view distributed teams as a mere mechanism for reducing payroll; they seek high-level collaborators capable of driving large-scale technological evolution. However, this evolution introduces sophisticated risks of hiring offshore development teams that extend far beyond traditional logistical concerns. A foundational understanding of offshoring reveals that while the economic principles of comparative advantage remain, the execution has become significantly more precarious for those prioritizing immediate savings over long-term stability.

When global enterprises adopt a “low-cost-first” mindset, they often ignore the three pillars of risk that define modern software delivery. These pillars include:

  • Operational Risk: Disruptions in project momentum caused by fragmented governance and misaligned workflows.
  • Technical Risk: The accumulation of technical debt due to sub-optimal architectural decisions and inconsistent code quality.
  • Regulatory Risk: Non-compliance with evolving data privacy standards, such as the ISO/IEC 27001:2022 requirements, which can result in catastrophic financial penalties.

Success in this environment requires a transition toward managed outsourcing services that prioritize precision, partnership, and progress over bottom-line reduction.

The Shift from Cost-Saving to Value-Creation

Traditional offshoring models are failing because they don’t account for the speed of modern digital transformation. Many organizations fall victim to the “Offshore Paradox,” where a 40% reduction in hourly rates actually increases the total cost of ownership by a factor of four due to rework and management overhead. In this context, offshore risk is the quantifiable delta between projected labor savings and the realized technical debt accrued through sub-optimal architectural decisions. By focusing on staffing solutions that emphasize specialized expertise, companies can avoid the trap of prioritizing output volume over delivery value.

Categorising Modern Enterprise Vulnerabilities

Modern vulnerabilities often manifest within the technical infrastructure itself. If an offshore partner lacks robust environmental stability, it directly compromises the integrity of continuous integration and deployment (CI/CD) pipelines, leading to stalled release cycles. Furthermore, the risk of vendor lock-in remains a significant threat; without intentional knowledge transfer, enterprises lose internal institutional knowledge and become dangerously dependent on external entities. This erosion of transparency is frequently exacerbated by fragmented communication protocols, which turn minor misunderstandings into systemic project delays. Maintaining operational control requires a disciplined approach to governance that ensures technical managers and executive leadership remain aligned on every deliverable.

Security, Compliance, and Intellectual Property Vulnerabilities

Data sovereignty remains a primary concern for global enterprises navigating the legal complexities of cross-border data transfers. In 2026, the European Data Protection Board has made Article 17 of the GDPR, the right to erasure, a key enforcement priority. Organizations must also contend with the California Privacy Rights Act (CPRA) regulations that, as of January 1, 2026, require comprehensive privacy risk assessments for processing that presents a significant risk to consumers. These evolving mandates amplify the risks of hiring offshore development teams that lack a mature understanding of localized compliance frameworks. Beyond statutory data protection, vulnerabilities in the software supply chain emerge when using unverified resources, potentially introducing malicious code or unauthorized backdoors into production environments.

Mitigating insider threats requires more than just background checks. It demands a systemic architecture of least-privilege access and continuous monitoring. Unauthorized data access often stems from fragmented identity management between the onshore leadership and the offshore execution team. Establishing a unified security posture is essential to protect the integrity of your digital infrastructure. It’s about maintaining stability and precision throughout the development lifecycle.

Regulatory Compliance in Regulated Sectors

Maintaining GxP and HIPAA compliance presents unique challenges when development occurs in jurisdictions with non-equivalent legal protections. For organizations in the pharmaceutical and finance sectors, the necessity of Software and Digital Assurance Testing cannot be overstated. This approach ensures the creation of immutable audit trails and rigorous validation protocols required by global regulators. It’s also vital to confirm that your partner has completed the transition to the ISO/IEC 27001:2022 standard, as the previous 2013 version’s transition period ended on October 31, 2025. Ensuring these standards are met provides the peace of mind necessary for large-scale technological evolution.

Intellectual Property and Contractual Safeguards

Protecting proprietary algorithms requires contracts that go beyond standard service agreements. To effectively manage the risks of hiring offshore development teams, every offshore contract must include explicit clauses regarding the ownership of work product and the immediate transfer of intellectual property rights upon creation. Utilizing code escrow and secure, encrypted repository management further reduces the risk of asset loss. Standardizing security testing as a non-negotiable component of the Definition of Done (DoD) ensures that protection is baked into the development lifecycle rather than added as an afterthought. If you’re concerned about your current security posture, consulting with a strategic compliance partner can help bridge the gap between technical execution and regulatory certainty.

The ‘Hidden’ Operational Costs: Communication, Culture, and Technical Debt

Operational efficiency often suffers when organizations overlook the subtle friction points inherent in distributed delivery models. While the initial balance sheet might suggest significant savings, the risks of hiring offshore development teams frequently manifest as a “Quality Gap.” This occurs when external teams prioritize velocity and ticket closure over sustainable code architecture. This short-term focus creates a fragile foundation that complicates future scaling and integration efforts. When speed is the only metric, the resulting technical debt acts as a high-interest loan that your internal team will eventually have to repay with interest.

Time zone differences introduce another layer of complexity, often resulting in a 24-hour delay for critical bug fixes. If a production-grade issue is identified at the end of a domestic business day, it may sit idle for half a cycle before an offshore team even begins the triage process. This lag erodes your time-to-market and can be devastating in high-stakes environments like Finance or Pharma. Cultural nuances in requirements gathering also lead to “The Yes-Man” syndrome. This is a phenomenon where offshore partners agree to ambiguous or impossible specifications to avoid perceived conflict, ultimately leading to misaligned deliverables and expensive rework.

The Long-Term Burden of Technical Debt

Quick and dirty code might meet an immediate deadline, but it leads to exponential maintenance costs in later years. To mitigate this, organizations must integrate professional manual testing into their quality assurance strategy. While automation provides speed, manual oversight is essential for catching complex logic errors that automated scripts often miss. Establishing a rigorous code review process ensures that every pull request adheres to your internal standards, protecting your architectural integrity from the onset.

Bridging the Cultural and Communication Divide

Success requires a single source of truth to synchronize disparate workflows. Implementing tools like Jira and Confluence provides the necessary transparency to track progress and document decisions in real-time. Engaging in professional Atlassian Consulting allows you to optimize these platforms for global collaboration, ensuring that your governance model supports asynchronous communication. This structure prevents project bottlenecks, transforming a fragmented team into a cohesive, high-performing unit that values precision and operational stability.

A Framework for Risk Mitigation and Governance

Mitigating the risks of hiring offshore development teams requires a disciplined transition from tactical procurement to a strategic governance framework. While many organizations rely on a standard Request for Proposal (RFP) to vet potential partners, this approach often fails to uncover the operational maturity required for enterprise-grade delivery. A robust selection process must evaluate a vendor’s ability to integrate with your existing digital infrastructure and their commitment to institutional stability. By shifting from a simple “Offshore Staffing” mindset to a comprehensive managed service model, enterprises ensure higher levels of accountability and a shared investment in long-term business outcomes. This methodology replaces fragmented execution with a structured approach that prioritizes precision, performance, and protection.

Establishing transparency across the Software Development Life Cycle (SDLC) is only possible through the integration of shared Key Performance Indicators (KPIs). These metrics should move beyond simple output volume, such as lines of code or ticket velocity, to focus on qualitative benchmarks like defect density and architectural adherence. When governance is treated as a core pillar of the partnership, technical managers gain the visibility needed to manage complex digital assets with confidence. To ensure your distributed model is built on a foundation of technical rigor, speak with our strategic consultants about building a custom governance framework.

Establishing Rigorous Governance Protocols

Integrating Quality Assurance from Day One

Quality cannot be an afterthought in a distributed environment; it must be baked into the delivery pipeline through continuous testing. Utilizing Software Test Automation Services is essential for providing real-time oversight of remote teams, allowing every commit to be validated automatically against your security and functional requirements. By leveraging DevOps Consulting, organizations can build a unified delivery pipeline that synchronizes onshore leadership with offshore execution. This systemic improvement reduces the risks of hiring offshore development teams by creating a transparent, automated environment where progress is measurable and results are predictable.
Navigating the Strategic Risks of Hiring Offshore Development Teams in 2026

The Test Triangle Advantage: Precision, Partnership, and Progress

Test Triangle addresses the fundamental risks of hiring offshore development teams by replacing fragmented, “set and forget” models with a rigorous managed service framework. Our approach ensures that every line of code and every architectural decision aligns with your enterprise goals, effectively neutralizing the Quality Gap and technical debt discussed in previous sections. By integrating industry-leading platforms like Atlassian and ServiceNow directly into our delivery model, we provide the total project visibility necessary for executive leadership to maintain operational control over complex digital infrastructures. This combination of offshore cost-efficiency and local strategic oversight allows global organizations to scale with confidence, clarity, and control.

Our personality is that of a strategic visionary who remains deeply practical, ensuring that your long-term success is never sacrificed for short-term gains. We act as a steady hand in a fast-changing technological landscape, emphasizing organizational progress through the combination of human expertise and sophisticated technical tools. By choosing a partner that values stability, precision, and scalable growth, you empower your organization to navigate the complexities of 2026 with a reliable long-term collaborator at your side.

Managed Outsourcing: Beyond Simple Staffing

Our Managed Outsourcing Services provide the high-level governance that typical offshore teams lack, positioning us as a reliable corporate partner rather than a mere service provider. Having an Ireland-based strategic partner manage global delivery centers means you benefit from institutional maturity, ensuring that cultural and communication barriers are proactively dismantled. For instance, our methodologies have successfully reduced technical debt for global healthcare providers by implementing disciplined code review and automated validation protocols. This approach transforms global delivery from a source of operational anxiety into a driver of systemic improvement.

Enterprise-Grade IT Staffing for Global Compliance

We offer a unique approach to IT Staffing for specialized roles, particularly within the highly regulated Pharma and Finance sectors. Our rigorous vetting process ensures that every resource is not only technically proficient but also fully aligned with your specific compliance requirements and corporate culture. We recognize that stability and precision are non-negotiable in high-stakes environments, which is why our staffing models are built on a foundation of technical rigor and institutional maturity. To optimize your current delivery model and eliminate the risks of hiring offshore development teams, connect with our strategic consultants to audit your existing strategy and establish a path toward high-quality, compliant software delivery at scale.

Securing Your Enterprise Delivery for 2026 and Beyond

The landscape of 2026 demands more than just cost-efficiency; it requires a disciplined commitment to security and quality. Mitigating the risks of hiring offshore development teams involves a fundamental shift from tactical staffing to a managed service model that prioritizes data sovereignty and architectural integrity. By establishing rigorous governance and integrating quality assurance into the core of your SDLC, you ensure that global delivery remains a catalyst for growth rather than a source of technical debt.

As a strategic Atlassian and ServiceNow partner with specialized expertise in Pharma and Finance compliance, Test Triangle provides the institutional maturity necessary for high-stakes environments. Our global reach is anchored by local, Dublin-based leadership, offering the precision and stability required to manage complex digital infrastructures with confidence. This combined approach ensures that technical managers and executive leadership remain aligned on every deliverable, fostering a spirit of partnership and support.

Secure your digital transformation with Test Triangle’s Managed Services and experience the peace of mind that comes from a reliable long-term collaboration. Your path to scalable, compliant, and high-quality software delivery starts with a partner dedicated to your long-term operational success.

Frequently Asked Questions

What are the most common security risks when hiring offshore development teams?

The most common security risks include data sovereignty violations, supply chain compromises, and unmonitored insider threats. In 2026, the risks of hiring offshore development teams are amplified by stricter privacy laws like the CPRA and updated GDPR enforcement. Organizations must implement zero-trust architectures and continuous monitoring to prevent unauthorized access to sensitive digital infrastructure, ensuring that remote resources remain as secure as internal assets.

How can I protect my intellectual property when working with offshore developers?

Protecting intellectual property requires a multi-layered approach that combines ironclad contractual safeguards with technical enforcement. Secure your proprietary algorithms by including explicit IP transfer clauses in every agreement and utilizing encrypted code repositories with strict access controls. Implementing code escrow services provides an additional fail-safe, ensuring that your organization retains full ownership and access to the work product even if the partnership dissolves, thereby maintaining institutional stability.

Is it possible to maintain high code quality with a low-cost offshore team?

Maintaining high code quality with a low-cost team is achievable only through a disciplined governance framework and professional oversight. While lower hourly rates often signal a “Quality Gap,” integrating automated testing and rigorous code reviews can mitigate the accumulation of technical debt. Success depends on shifting the focus from output volume to qualitative benchmarks, ensuring that the final deliverable meets enterprise-grade standards without sacrificing the initial cost-efficiency of the distributed model.

How do I manage the time zone differences effectively in a DevOps environment?

Effective time zone management in a DevOps environment relies on robust asynchronous communication and a “Single Source of Truth.” By leveraging platforms like Jira and Confluence, teams can synchronize workflows without requiring real-time overlap for every task. This structure prevents project bottlenecks and ensures that continuous integration and deployment pipelines remain active, transforming potential 24-hour delays into a rhythmic, around-the-clock development cycle that accelerates your time-to-market.

What compliance standards should I look for in an offshore development partner?

Essential compliance standards for offshore partners include ISO/IEC 27001:2022 for information security and SOC 2 for operational controls. In specialized sectors like Finance or Pharma, you must also verify adherence to GxP or HIPAA requirements to ensure audit readiness. Selecting a partner with these official endorsements provides the peace of mind necessary for large-scale technological evolution, ensuring that your global delivery centers operate within recognized global benchmarks.

What happens if an offshore project fails to meet its technical requirements?

When an offshore project fails to meet technical requirements, the primary recourse is the enforcement of predefined Service Level Agreements (SLAs). These agreements should include specific remediation protocols and financial penalties for non-compliance with quality metrics. To prevent such failures, conduct regular third-party audits and maintain a transparent delivery pipeline, allowing you to identify and correct architectural deviations before they evolve into systemic project failures or unmanageable technical debt.

How does managed outsourcing differ from traditional offshore staffing?

Managed outsourcing differs from traditional staffing by providing a comprehensive governance layer and end-to-end accountability. While traditional staffing merely provides labor, managed outsourcing integrates strategic oversight, quality assurance, and project management into a cohesive service. This model addresses the risks of hiring offshore development teams by ensuring that the provider is deeply invested in your long-term success, offering a steady hand to manage complex digital transformations.

Can offshore teams effectively integrate with Atlassian or ServiceNow platforms?

Offshore teams can effectively integrate with Atlassian or ServiceNow platforms when supported by specialized consulting expertise. These ecosystems provide the necessary project visibility and ITSM rigor to synchronize global delivery centers with onshore leadership. Professional implementation ensures that your distributed workflows are optimized for transparency and precision, allowing technical managers to track every deliverable within a unified, high-performance environment that supports organizational progress.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.
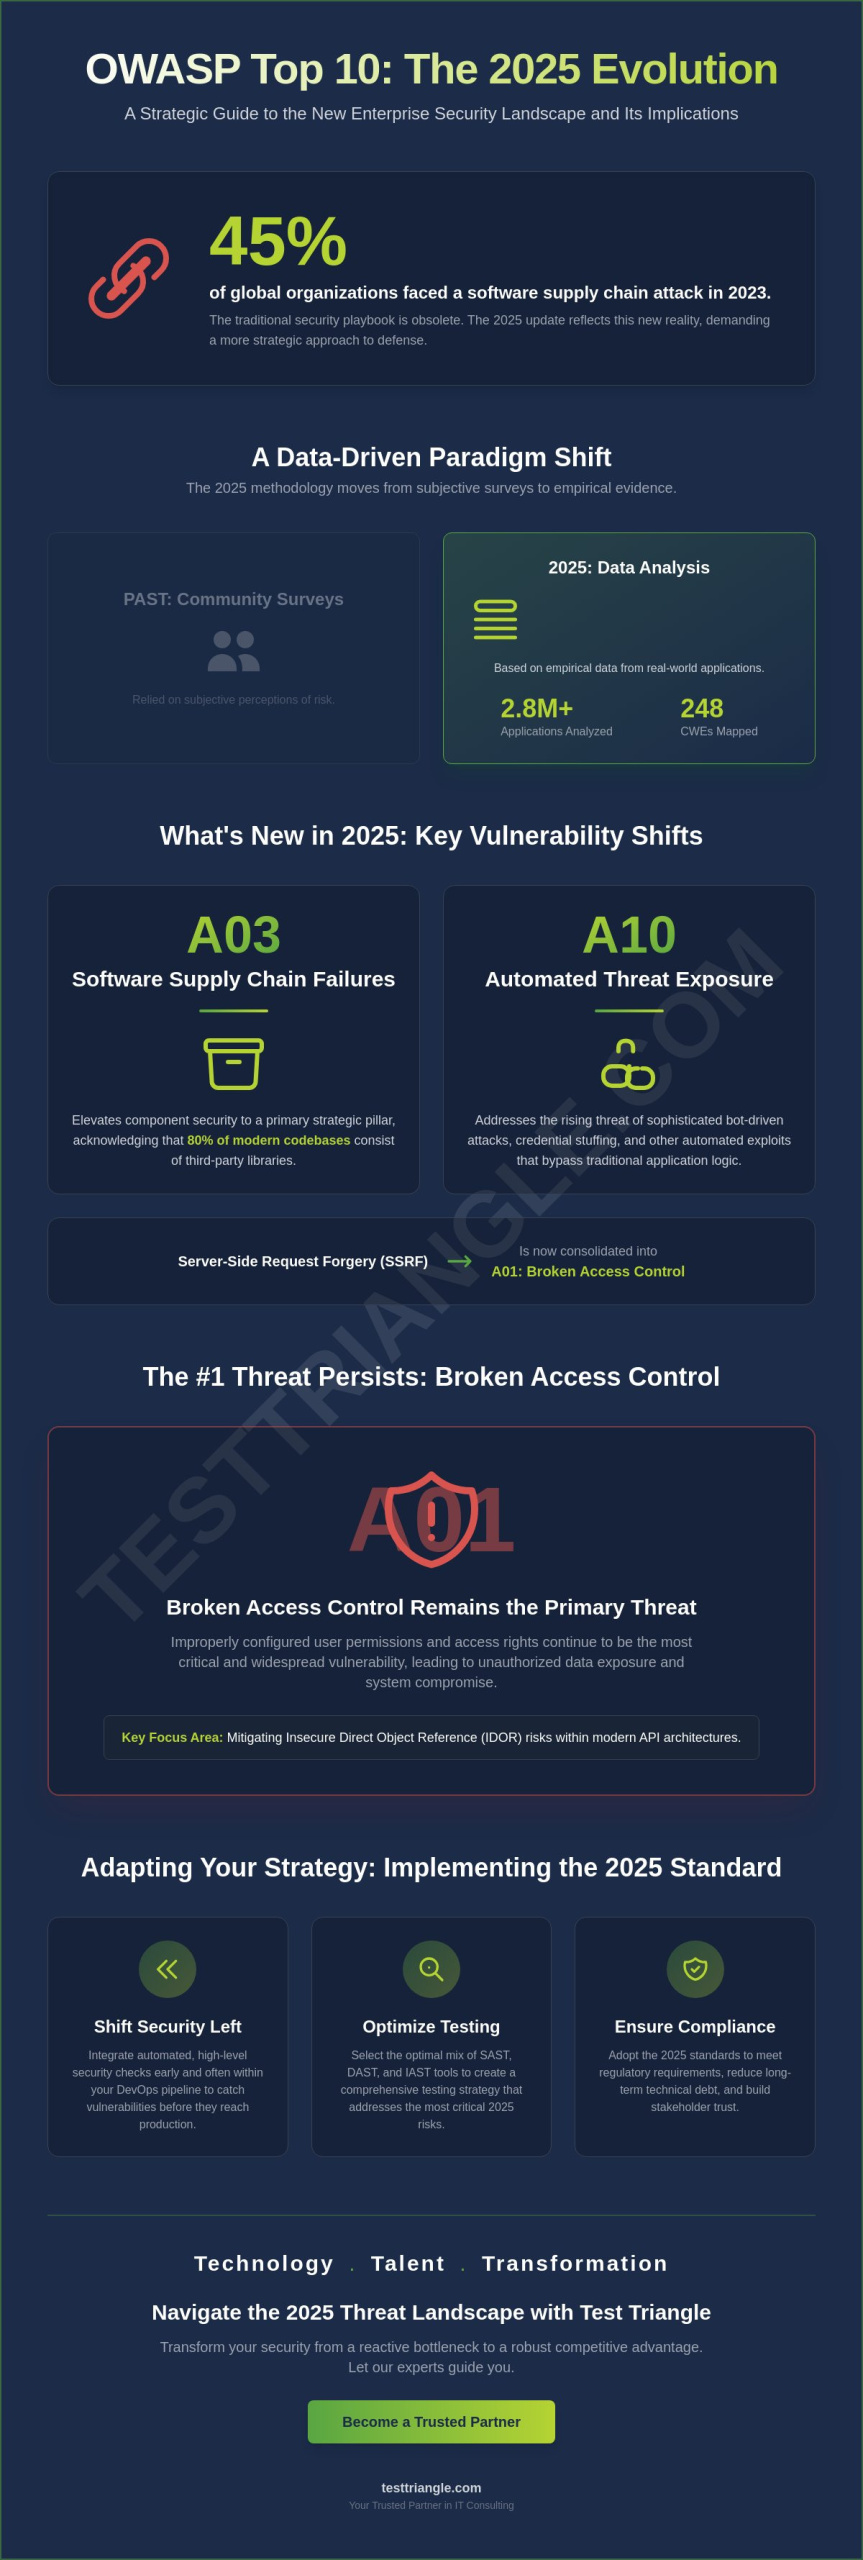
In a landscape where 45% of global organizations reported a software supply chain attack in 2023, the traditional security playbook is rapidly becoming obsolete. You’ve likely felt the mounting pressure of integrating complex security protocols into high-velocity DevOps pipelines while managing an increasingly volatile risk surface. It’s difficult to maintain a flawless defense when vulnerability categories evolve faster than your internal documentation can keep pace. Staying ahead of the owasp top 10 2025 news is no longer just a compliance checkbox; it’s a strategic requirement for any enterprise committed to long-term operational stability.

By aligning technical rigor with strategic foresight, Test Triangle helps global businesses transform their security posture from a reactive bottleneck into a robust competitive advantage. In this article, you’ll discover the critical updates in the 2025 framework and learn how to leverage these insights to optimize your testing strategy. We’ll provide a clear understanding of emerging risks and actionable steps for compliance. Our goal is to empower your team to drive digital transformation through our core philosophy: Technology. Talent. Transformation. As your Trusted Partner, we’ll ensure your security roadmap is both visionary and deeply practical.

Key Takeaways

  • By analyzing data from millions of applications, you will understand how the latest owasp top 10 2025 news reshapes the global standard for enterprise application security and risk awareness.
  • Identify the two entirely new vulnerability categories introduced this year and learn why the consolidation of SSRF into Access Control requires a strategic update to your defense protocols.
  • Gain actionable insights into why Broken Access Control remains the primary threat to digital stability and how to effectively mitigate IDOR risks within modern API architectures.
  • Elevate your DevOps pipeline by integrating high-level security checks and selecting the optimal mix of SAST, DAST, and IAST tools to address the most critical 2025 risks.
  • Leverage our “Technology, Talent, and Transformation” framework to transition from a reactive security posture to a robust, architected defense led by a trusted strategic partner.

The Evolution of Web Security: Understanding the OWASP Top 10 2025

The OWASP Top 10 remains the definitive global benchmark for application security awareness, providing a critical lens through which enterprises view digital risk. As organizations prepare for the 2026 fiscal year, the latest owasp top 10 2025 news signals a fundamental change in the security paradigm. By moving beyond a simple list of technical flaws, the OWASP organization now provides a strategic roadmap for systemic resilience. This update isn’t just a routine refresh. It’s a call to action for enterprises to shift their focus from identifying symptoms to addressing the root-cause vulnerabilities that lead to catastrophic breaches.

Strategic security requires a steady hand and a clear vision. By aligning with these updated standards, Test Triangle helps global enterprises leverage technology to protect their most valuable assets. This evolution is critical for any firm navigating digital transformation, as it establishes a foundation of trust and operational stability. Security is no longer a peripheral concern; it’s the core of business continuity and enterprise growth.

The Methodology Behind the 2025 Update

The 2025 update utilizes a rigorous, data-driven approach that analyzes 2.8 million applications across diverse industries. This methodology marks a departure from the community-survey models used in previous years, which often relied on subjective perceptions of risk. By mapping findings to 248 specific Common Weakness Enumerations (CWEs), the framework provides an empirical basis for security investment. This granular detail allows IT leaders to:

  • Identify high-frequency vulnerabilities across complex application portfolios.
  • Optimize resource allocation by targeting systemic weaknesses rather than isolated bugs.
  • Drive measurable improvements in code quality and deployment safety.

This evidence-based strategy ensures that the latest owasp top 10 2025 news reflects the actual threats facing modern digital infrastructures. It allows for a more disciplined approach to risk management that prioritizes actual data over industry trends.

Why Compliance with 2025 Standards Matters

Adhering to the 2025 standards is essential for maintaining regulatory compliance in highly scrutinized sectors like finance and healthcare. By adopting these benchmarks, organizations demonstrate a commitment to superior security that satisfies both auditors and stakeholders. Implementing these standards early reduces the long-term maintenance costs and technical debt that typically follow a security breach. It’s a proactive investment in the brand’s reputation and operational integrity. As a Trusted Partner, Test Triangle emphasizes that security isn’t a hurdle to innovation but an accelerant for growth. Through the synergy of Technology, Talent, and Transformation, businesses can achieve a robust security posture that supports long-term success and global scalability.

What’s New in 2025? Key Shifts in the Vulnerability Landscape

By analyzing the strategic updates within the official OWASP Top 10 2025, global enterprises can identify a decisive pivot toward systemic architectural integrity. The latest owasp top 10 2025 news reveals that security is no longer confined to isolated code quality; it now encompasses the entire digital ecosystem. This shift reflects a landscape where 80% of modern application codebases consist of third-party libraries, necessitating a broader defensive perimeter.

The 2025 update introduces two entirely new categories that address the complexities of modern automation and artificial intelligence. First, A03:2025 – Software Supply Chain Failures elevates component security from a sub-task to a primary strategic pillar. Second, A10:2025 – Automated Threat Exposure addresses the rise of sophisticated bot-driven attacks and credential stuffing that bypass traditional logic. By integrating these categories, the OWASP Foundation acknowledges that cloud-native environments and configuration-driven apps require more than just “patching”; they require a robust, zero-trust architecture.

The consolidation of Server-Side Request Forgery (SSRF) into Access Control highlights a logical evolution in risk management. Security architects now recognize that SSRF is fundamentally a failure to enforce authorization at the network or service boundary. By grouping these risks, the 2025 framework helps organizations streamline their remediation efforts through a unified policy engine.

A03:2025 – Software Supply Chain Failures

The elevation of supply chain security to a standalone priority stems from a 45% increase in attacks targeting CI/CD pipelines and developer environments since 2022. Modern risks aren’t just limited to “old” code; they involve unverified APIs, compromised build tools, and malicious dependencies hidden in deep package trees. Software Supply Chain Failures represent the risk of unverified components. By leveraging strategic security testing, businesses can validate every link in their delivery chain to ensure that third-party integrations don’t become Trojan horses for enterprise data.

Consolidation and Re-ranking: The 2021 vs 2025 View

The hierarchy of risk has shifted significantly to reflect the reality of cloud-heavy infrastructures. Security Misconfiguration has climbed to the #2 spot, driven by the fact that 65% of cloud breaches now originate from preventable configuration errors rather than complex exploits.

  • A01: Broken Access Control (Remains #1 due to its persistent impact on data privacy)
  • A02: Security Misconfiguration (Moved up from #4 in 2021)
  • A03: Software Supply Chain Failures (New standalone category for 2025)
  • A04: Cryptographic Failures (Shifted down slightly as encryption standards mature)
  • A05: Injection (Now includes broader AI-driven injection patterns)

Merging standalone categories into broader umbrellas allows the OWASP Top 10 2025 news to focus on the root causes of failure rather than specific symptoms. This approach empowers a Trusted Partner to help clients build more resilient systems through Technology. Talent. Transformation.

OWASP Top 10 2026 News: Strategic Implications for Enterprise Security

Dominant Risks: Why Broken Access Control and Misconfigurations Still Lead

The OWASP Top 10 2025 reinforces a critical reality for enterprise leaders: Broken Access Control remains the most pervasive threat to digital integrity. Data from the OWASP Foundation indicates that 94% of applications tested exhibited some form of broken access control, with a mean incidence rate of 3.81%. This persistence is driven by the proliferation of modern APIs, where Insecure Direct Object References (IDOR) allow unauthorized users to manipulate parameters to access sensitive data. By failing to implement rigorous server-side validation, developers inadvertently leave doors open for catastrophic data exfiltration.

Recent owasp top 10 2025 news highlights that modern software engineering relies too heavily on vulnerable default configurations. While automated security testing identifies approximately 60% of common vulnerabilities, it often misses the nuanced logic flaws that lead to these breaches. By combining automated scans with strategic oversight, Test Triangle helps organizations identify these flaws early in the lifecycle, preventing costly post-deployment remediation.

The Complexity of Access Control in Distributed Systems

Managing permissions becomes exponentially harder as enterprises scale their microservices and Atlassian ecosystems. In a distributed architecture, a single user request might traverse 12 or more distinct services, increasing the surface area for privilege escalation. By adopting a “Least Privilege” architectural principle, organizations ensure that every module operates with the minimum necessary permissions. This strategic approach prevents lateral movement during a breach. Our teams leverage deep expertise in Jira and ServiceNow to optimize identity and access management (IAM) protocols, ensuring that your Technology. Talent. Transformation. strategy remains secure.

Mitigating Security Misconfigurations

Security misconfigurations frequently occur in cloud environments where 65% of breaches originate from human error in setting up container orchestration. By implementing “Security as Code,” enterprises automate the deployment of hardened configurations, preventing the drift that occurs during rapid release cycles. While automated scans catch open ports or default passwords, they cannot fully grasp complex business logic. Integrating Manual Testing alongside automated tools provides a robust defense against sophisticated exploits.

As a Trusted Partner, Test Triangle delivers a superior level of security by combining technical precision with strategic oversight. We ensure that every configuration aligns with global compliance standards, protecting your digital assets from the evolving threats identified in the owasp top 10 2025 news

Implementing the 2025 Standard: Shifting Security Left in your DevOps Pipeline

By embedding rigorous security protocols directly into the CI/CD pipeline, global enterprises can identify and neutralize vulnerabilities before they ever reach a production environment. The latest owasp top 10 2025 news confirms that reactive security models are failing to keep pace with rapid deployment cycles. To maintain a robust defense, organizations must leverage a strategic mix of Static Application Security Testing (SAST), Dynamic Application Security Testing (DAST), and Interactive Application Security Testing (IAST). This multi-layered toolset allows teams to scan source code, analyze running applications, and monitor execution flows simultaneously.

Building a “Security Culture” is the foundation of this transformation. When developers take direct ownership of code safety, the burden on security teams decreases and software quality improves. It’s a shift that requires more than just tools; it demands a fundamental change in how teams perceive their roles. By empowering engineers with the right training, enterprises ensure that security is a shared responsibility rather than an isolated checkpoint.

Automation vs. Manual Expertise

Automated tools excel at identifying 85% of common vulnerabilities, such as injection flaws or broken access controls, at incredible speeds. They provide the technical backbone of a modern security strategy. Human expertise remains indispensable for addressing A04:2025 – Insecure Design. This category focuses on architectural flaws that require a deep understanding of business logic which software can’t yet replicate.

To scale these efforts effectively, many organizations utilize QA Outsourcing to gain access to specialized talent. These experts interpret complex data and provide the human insight needed to solve nuanced problems. By blending automation with manual penetration testing, businesses achieve a level of precision that tools alone can’t provide. The owasp top 10 2025 news updates suggest that shifting security left is no longer optional for competitive enterprises.

Securing the Atlassian and ServiceNow Environments

Applying OWASP 2025 principles to enterprise platforms like Jira Service Management and ServiceNow is critical for maintaining operational integrity. Custom plugins and third-party integrations often serve as overlooked entry points for attackers. During a complex AWS cloud migration, security must be integrated into the architecture from the very first day. This proactive stance prevents the accumulation of technical debt and ensures that digital transformation services deliver long-term value.

By prioritizing security during platform upgrades and cloud transitions, enterprises protect their most sensitive data assets. Test Triangle acts as a Strategic Architect in these scenarios, ensuring your ecosystem is both agile and resilient. Partner with Test Triangle to secure your enterprise DevOps pipeline today.

Test Triangle serves as a Strategic Architect for global enterprises, ensuring that security isn’t just a reactive measure but a foundational pillar of operational stability. By aligning our custom security testing services with the latest owasp top 10 2025 news, we empower organizations to mitigate risks before they manifest as costly breaches. Our methodology centers on a proven triad: Technology, Talent, and Transformation. This framework allows us to provide a steady hand in a fast-changing landscape, helping firms in sectors like Banking and Life Sciences maintain flawless digital infrastructures. We’ve built our reputation on being a Trusted Partner that’s deeply invested in the long-term success of our clients.

By combining technical expertise with adaptable delivery models, Test Triangle helps businesses reduce costs while elevating their security posture. We don’t just provide a service; we deliver a comprehensive roadmap that addresses the unique challenges of the 2025 threat environment. Our global presence ensures that we can support complex infrastructures across multiple time zones, providing the reliability that modern enterprises demand.

Technology: Advanced Tooling and Integration

By leveraging our expertise in industry-leading security platforms, we help businesses optimize their existing stacks for maximum visibility. Our consultants refine DevOps pipelines to incorporate real-time vulnerability feedback, ensuring that security is a continuous process rather than a final gate. This proactive integration reduces the time to remediation by approximately 40% in high-velocity development environments. We’ve mastered the art of technical integration, specifically by embedding automated OWASP 2025 security checks into Atlassian workflows to ensure that Jira Service Management becomes a central hub for risk remediation. This approach ensures that developers receive actionable security data without leaving their primary work environment.

Talent and Transformation: Long-term Strategic Partnership

Addressing the sophisticated risks highlighted in the owasp top 10 2025 news requires more than software; it demands specialized human intelligence. We bridge the global skills gap by providing the elite talent needed to manage complex security environments, from penetration testers to DevSecOps engineers. Our flexible engagement models allow us to act as a Strategic Architect, driving digital transformation that’s secure by design rather than by accident. By embedding security into the very fabric of the development culture, we’ve helped clients ensure that 90% of new features meet rigorous security standards before they ever reach production. This cultural shift is essential for maintaining a robust defense in an era of automated attacks.

Our commitment to excellence is reflected in our ability to scale security teams rapidly to meet emerging threats. Whether you’re navigating a migration or securing a new AI-driven application, our consultants provide the precision and discipline required for success. Consult with our experts on your OWASP 2025 security roadmap to begin your journey toward a more robust and resilient digital future.

Fortifying Your Enterprise Against the 2025 Vulnerability Landscape

Adapting to the latest owasp top 10 2025 news requires more than a reactive posture; it demands a strategic overhaul of your development lifecycle. By prioritizing the mitigation of Broken Access Control and addressing persistent misconfigurations, global enterprises can reduce their attack surface before code ever reaches production. Organizations operating within high-compliance sectors like Pharmaceuticals and Finance must align their DevOps pipelines with these updated 2025 standards to maintain operational integrity. Shifting security left ensures that vulnerabilities are identified early, helping organizations avoid the $4.45 million average cost of a data breach reported by IBM in 2023.

As an Authorized Atlassian and ServiceNow Strategic Partner, Test Triangle provides the specialized expertise needed to navigate these complex shifts. Our global delivery model is built on the pillars of Technology, Talent, and Transformation, ensuring your digital infrastructure remains robust against emerging threats. By choosing a Trusted Partner with a proven track record in rigorous regulatory environments, you’re investing in a secure and scalable future. We’re ready to help you optimize your security strategy and drive long-term resilience.

Contact Test Triangle for a Comprehensive OWASP 2025 Security Audit

Frequently Asked Questions

What is the most significant change in the OWASP Top 10 2025?

The elevation of Software Supply Chain Failures to a primary risk category is the most critical update in the 2025 list. This shift responds to a 40% increase in supply chain attacks documented in the 2024 ENISA Threat Landscape report. By prioritizing this category, OWASP encourages global enterprises to move beyond internal code audits and scrutinize third-party dependencies. This strategic focus ensures that your security posture remains robust against complex, multi-stage digital intrusions.

How does A03:2025 Software Supply Chain Failures differ from previous versions?

A03:2025 expands its scope by focusing explicitly on the provenance and security of external components. While the 2021 version touched on integrity, the 2025 update demands rigorous verification of the 80% of modern application code that typically originates from open-source libraries. This change requires organizations to implement automated Software Bill of Materials (SBOM) management. By adopting these measures, your team can effectively mitigate risks associated with unverified third-party scripts and plugins.

Is SSRF still a standalone category in the 2025 OWASP list?

Server-Side Request Forgery (SSRF) remains a distinct category, though its ranking has shifted based on 2024 exploit frequency data. Organizations must still treat SSRF as a high-priority threat because it allows attackers to bypass firewalls and access internal microservices. This persistence in the owasp top 10 2025 news highlights the ongoing vulnerability of cloud-native architectures where metadata services are frequently targeted. You shouldn’t overlook this risk just because other categories have gained more visibility.

Why did Security Misconfiguration move up to the second position in 2025?

Security Misconfiguration rose to the number two spot because it accounts for 35% of successful cloud breaches identified in 2024 industry data. As enterprises accelerate their digital transformation, the complexity of managing permissions across thousands of containers often leads to human error. By addressing this early, your team can prevent the unauthorized access that stems from default credentials and overly permissive cloud buckets. It’s a vital area where automated configuration audits can deliver immediate security improvements.

How can my organization transition from the 2021 to the 2025 OWASP standards?

Transitioning requires an immediate gap analysis to map your current 2021 controls against the updated 2025 risk definitions. You should update your DevSecOps pipelines by January 2026 to include specific checks for supply chain integrity and advanced configuration validation. Through the synergy of Technology, Talent, and Transformation, Test Triangle acts as a Strategic Architect during this process. We help you leverage automated tools to align your security roadmap with these evolving global standards flawlessly.

What tools are best for testing against the OWASP Top 10 2025?

Effective testing requires a combination of Static Analysis Security Testing (SAST) and Dynamic Analysis Security Testing (DAST) tools like Checkmarx or Burp Suite Professional. To address the latest owasp top 10 2025 news, you must also integrate Software Composition Analysis (SCA) tools such as Snyk to monitor third-party vulnerabilities. These platforms provide the technical rigor needed to identify complex flaws like insecure direct object references. Using integrated tools within Jira Service Management ensures that your remediation workflows remain efficient.

Does OWASP Top 10 2025 apply to mobile applications or just web apps?

The OWASP Top 10 2025 focuses primarily on web application risks, though many of its principles apply to the backend APIs used by mobile apps. For mobile-specific threats, organizations should refer to the OWASP Mobile Top 10, which was last updated in late 2023. By combining both standards, enterprises ensure a flawless security layer across their entire digital ecosystem. This approach protects both browser-based interfaces and native mobile applications from common vulnerabilities like broken access control and data leaks.

How often does OWASP update its Top 10 list?

OWASP typically updates the Top 10 list every three to four years, with previous iterations released in 2017, 2021, and now 2025. These updates rely on data contributed by over 500 security organizations and hundreds of thousands of vulnerability reports. This structured cadence allows your business to plan long-term security investments while staying informed about the most prevalent threats. As a Trusted Partner, we monitor these cycles to ensure your defensive strategies evolve alongside the changing technological landscape.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.
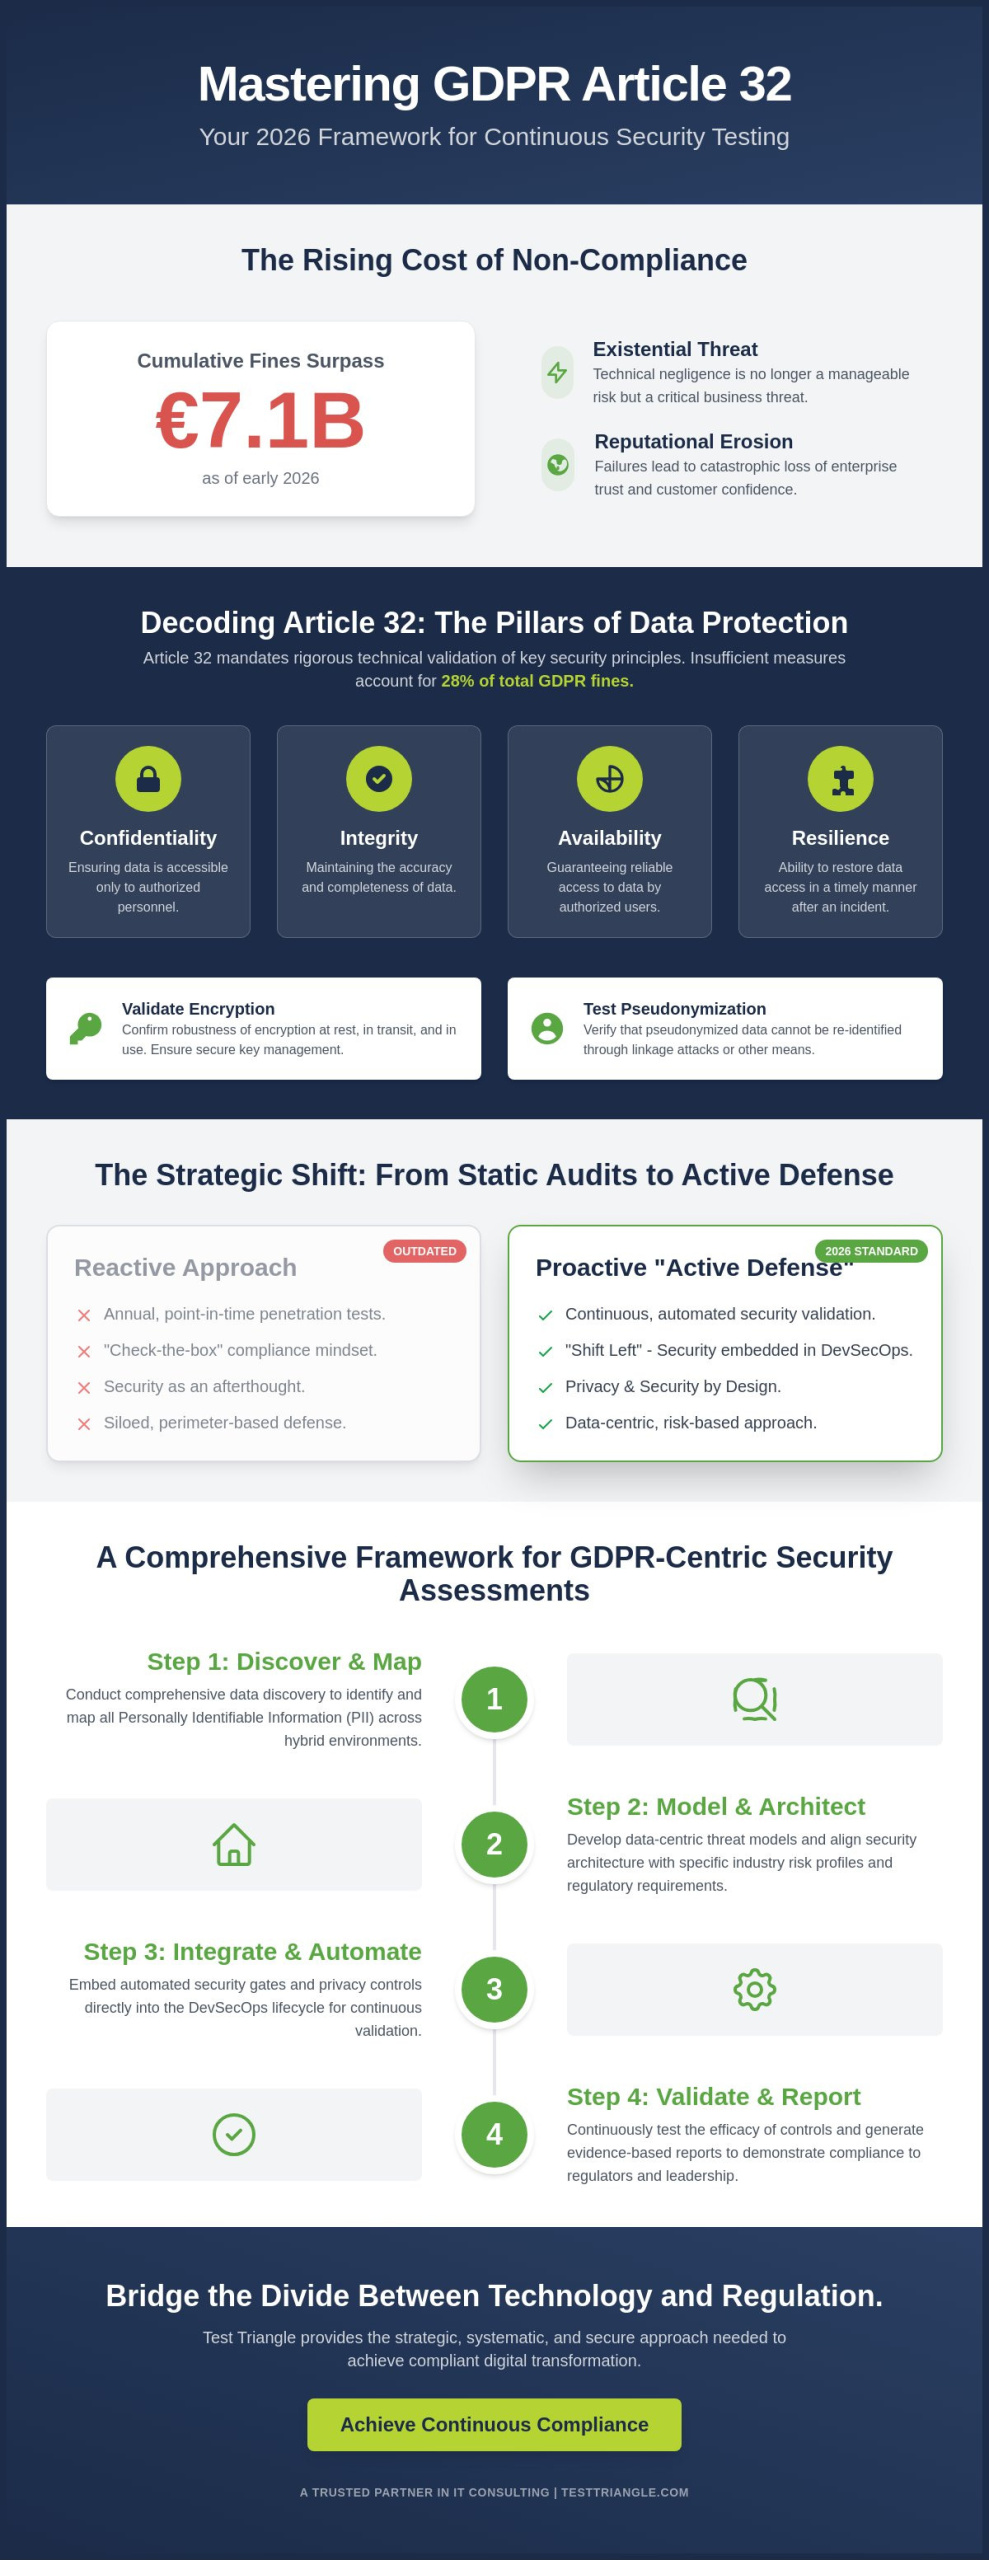

With cumulative GDPR fines surpassing €7.1 billion as of early 2026, the cost of technical negligence has evolved from a manageable risk into a potential existential threat for the global enterprise. You likely feel the pressure of the ambiguity surrounding “regular testing” in Article 32, which often leaves leadership questioning if their current protocols are sufficient to withstand modern regulatory scrutiny. Maintaining a consistent security posture across complex, hybrid cloud environments is a significant undertaking, especially as the enforcement of the EU AI Act in August 2026 adds another layer of complexity to data protection.

This guide provides a definitive roadmap to master the technical requirements of Article 32 and implement a robust framework for security testing for gdpr compliance that ensures your organization remains continuously protected. By aligning your security strategy with proven methodologies, you’ll reduce organizational risk and achieve a seamless integration of privacy controls into your digital transformation. We’ll examine the specific activities required to build a validation framework that is continuous, comprehensive, and compliant; ensuring your enterprise stays ahead of shifting global standards through a blend of human expertise and technical precision.

Key Takeaways

  • Transition from static compliance snapshots to a dynamic “active defense” posture to meet the heightened scrutiny of 2026 regulatory bodies.
  • Implement a systematic framework for security testing for gdpr compliance to validate the efficacy of technical controls like encryption and pseudonymization under Article 32.
  • Adopt a “shift left” strategy within the DevSecOps lifecycle by embedding automated security gates that identify vulnerabilities before they reach production environments.
  • Develop a data-centric assessment roadmap starting with comprehensive discovery and threat modeling to align security architecture with specific industry risk profiles.
  • Bridge the divide between technical execution and regulatory requirements through a strategic, systematic, and secure approach to digital assurance.

In the current regulatory climate, security testing for gdpr compliance has transitioned from a peripheral IT concern to a core executive mandate. It represents the systematic validation of technical controls designed to protect personal data from unauthorized access, accidental loss, or unlawful processing. As established by the General Data Protection Regulation (GDPR), organizations must prove their defenses are not just present but effective in real-world scenarios. By 2026, regulators have shifted their focus toward “active defense,” requiring enterprises to demonstrate that their security measures are reliable, resilient, and robust against sophisticated attack vectors.

The consequences of failing to validate these controls extend far beyond the tiered fine structure, which has already seen cumulative penalties exceed €7.1 billion since enforcement began. While the €1.2 billion in fines issued in 2025 highlights the immediate financial risk, technical negligence causes deeper damage through severe reputational erosion and a catastrophic loss of enterprise trust. As companies accelerate their digital transformation initiatives, the resulting expansion of attack surfaces for Personally Identifiable Information (PII) creates new, complex vulnerabilities. These evolving digital ecosystems require an evidence-based approach to security that connects technical execution directly to business stability.

The Reality of Article 32 in a Modern Tech Stack

Article 32 mandates the implementation of “appropriate technical and organizational measures” (TOMs) to ensure a level of security appropriate to the risk. In 2026, the rise of cloud-native architectures, microservices, and distributed data lakes has fundamentally complicated the definition of what constitutes an “appropriate” measure. Legacy security approaches that rely on perimeter defense are no longer sufficient in a world where data flows across borderless, hybrid environments. Modern validation must be data-centric, focusing on the integrity and availability of information within complex tech stacks to ensure that technical managers and executive leadership remain aligned on risk reduction.

From Check-the-Box to Strategic Assurance

Relying on annual penetration tests is an insufficient strategy for 2026 compliance because a single point-in-time audit cannot account for the rapid pace of continuous deployment. Strategic assurance requires embedding “Security by Design” directly into the software testing lifecycle, ensuring that privacy controls are verified at every stage of development. By moving away from reactive audits and toward proactive validation, organizations can maintain a posture that is integrated, iterative, and impactful. Ultimately, security testing for gdpr compliance is a continuous risk-mitigation strategy that evolves alongside the threat landscape to provide long-term operational stability.

Decoding Article 32: Technical Validation of Data Protection Measures

To achieve a state of continuous readiness, enterprises must move beyond superficial audits and embrace a rigorous technical validation of their data protection environments. Article 32 of the GDPR serves as the foundational legal framework for this requirement, explicitly mandating that organizations implement measures to ensure the confidentiality, integrity, availability, and resilience of processing systems. With insufficient technical and organizational measures under Article 32 accounting for 28% of total GDPR fines, security testing for gdpr compliance requires a sophisticated, compliance-driven approach that simulates real-world exploitation to verify that these four pillars remain uncompromised.

Technical validation is particularly critical when assessing the efficacy of pseudonymization and encryption. It isn’t enough to simply state that data is encrypted; testing must confirm that encryption remains robust across all states, including at rest, in transit, and in use. This process involves verifying that cryptographic keys are managed securely and that pseudonymized data cannot be re-identified through unauthorized correlation. By adopting a “Strategic, Systematic, Secure” methodology, organizations can provide the documented proof of technical efficacy that regulators demand.

Testing for Confidentiality and Data Integrity

Ensuring confidentiality requires a granular assessment of access controls and the potential for privilege escalation within the application architecture. As enterprises increasingly rely on interconnected ecosystems, API testing becomes a vital component in preventing unauthorized data leakage between disparate services. For complex, logic-based security flaws that automated scanners often miss, integrating Manual Testing ensures that human expertise identifies vulnerabilities in business logic that could lead to unauthorized data access. These efforts ensure that personal data remains shielded from internal and external threats alike.

Evaluating System Resilience and Availability

The “Restoration and Recovery” clause of Article 32 highlights the necessity of maintaining high availability and the ability to restore access to personal data in a timely manner following a physical or technical incident. Performance testing acts as a critical proxy for availability compliance, which is a cornerstone of comprehensive security testing for gdpr compliance, allowing teams to stress test systems under extreme loads to ensure stability during traffic surges or coordinated DDoS attempts. Verifying the “Ability to Restore” through rigorous backup validation testing confirms that disaster recovery protocols are not just theoretical but operational. If you’re looking to refine your technical validation strategy, you might consult with our strategic advisory team to ensure your framework meets these rigorous standards.

Security Testing for GDPR Compliance in 2026: A Strategic Enterprise Guide

Integrating Security Testing into the DevSecOps Lifecycle

To maintain a posture of continuous readiness in 2026, enterprises must move beyond reactive audits and embed security testing for gdpr compliance directly into the software development lifecycle. This “shift left” methodology ensures that privacy considerations are not an afterthought but a foundational requirement identified during the initial design and coding phases. By detecting vulnerabilities before they reach production, organizations can significantly reduce the risk of the massive fines and reputational erosion discussed earlier. This proactive approach aligns technical execution with the NIST Cybersecurity Framework, providing a structured path toward the “appropriate technical measures” mandated by Article 32.

The implementation of automated security gates within CI/CD pipelines acts as a critical checkpoint for persistent compliance. These gates allow for the rapid, repeatable validation of code against security benchmarks, ensuring that every deployment remains within the defined risk tolerance of the organization. Achieving this level of integration often requires specialized expertise, where DevOps Consulting serves as the strategic bridge between rapid delivery and regulatory rigor. Through this synergy, security becomes a silent enabler of digital transformation rather than a bottleneck to innovation.

Securing the Enterprise Ecosystem: Atlassian and ServiceNow

Modern enterprises frequently manage sensitive PII within specialized platforms, yet these environments often remain untested for privacy-specific vulnerabilities. A comprehensive strategy must include rigorous validation for Atlassian Implementation to ensure that collaborative data remains shielded from unauthorized internal access. Similarly, validating data privacy within ServiceNow Consulting workflows is essential to prevent third-party integrations from creating GDPR blind spots. These platforms require tailored security testing for gdpr compliance to ensure that automated service management doesn’t inadvertently lead to data exposure.

The Managed Service Advantage for Compliance

Maintaining a 24/7 security posture is an intensive undertaking that often stretches internal resources beyond their capacity. Utilizing a Managed Outsourcing model provides the “steady hand” needed for recurring security assessments and persistent monitoring. This approach allows enterprises to leverage specialized talent through strategic staffing, ensuring that security remains a constant priority. By delegating the technical execution of compliance-driven testing to a reliable long-term collaborator, leadership can focus on high-level strategic growth while maintaining the peace of mind that their digital infrastructure is managed with professional precision.

A Comprehensive Framework for GDPR-Centric Security Assessments

Establishing a resilient security posture requires a transition from broad data visibility to granular technical validation through a framework defined by Discovery, Defense, and Documentation. To ensure that security testing for gdpr compliance delivers tangible risk reduction, organizations must follow a structured five-step lifecycle that aligns technical execution with regulatory expectations:

  • Step 1: Data Discovery and Mapping: Establishing a complete inventory of personal data assets and flows is the prerequisite for any testing activity; you can’t protect what you haven’t identified.
  • Step 2: Threat Modeling: This involves identifying likely attack vectors specific to your industry and infrastructure, allowing for a prioritized defense strategy that addresses the most critical vulnerabilities first.
  • Step 3: Vulnerability Assessment and Penetration Testing (VAPT): As the core execution phase, this combines automated scanning with human-led exploitation to uncover deep-seated flaws in the security architecture that automated tools often miss.
  • Step 4: Remediation and Re-testing: Identified risks must be addressed through systematic patching or configuration changes, followed by rigorous re-testing to confirm the closure of the vulnerability loop.
  • Step 5: Documentation and Reporting: This final step creates the essential “audit trail” for regulators, providing the documented proof of technical efficacy required during a Data Protection Impact Assessment (DPIA) or a post-breach investigation.

Industry-Specific Testing Nuances: Pharma and Finance

In the pharmaceutical sector, security testing for gdpr compliance must often be harmonized with stringent GxP requirements to ensure data integrity across the entire drug development lifecycle. Managing these dual mandates requires a workforce that understands both clinical validation and data privacy; utilizing specialized Pharma IT Staffing ensures your team possesses the necessary regulatory fluency. Conversely, financial institutions face high-frequency testing demands due to the sensitive nature of transaction data and the rapid pace of fintech innovation, necessitating a “Continuous, Comprehensive, Compliant” validation model that mirrors their operational complexity.

Critical Testing Types for 2026 Compliance

Modern assessments must incorporate Static and Dynamic Application Security Testing (SAST/DAST) to identify vulnerabilities within both the source code and the running application environment. Additionally, Cloud Infrastructure Entitlement Management (CIEM) validation is essential for managing the complex permissions that often lead to data exposure in hybrid cloud settings. The “Gold Standard” of a 2026 security audit report is an evidence-based, machine-readable document that maps every technical remediation directly to the specific Article 32 control it satisfies. If you’re ready to implement a framework that balances technical rigor with regulatory precision, connect with our strategic consultants today.

Test Triangle: Your Strategic Partner for Compliant Digital Transformation

Test Triangle stands as the essential bridge between rigorous technical execution and the stringent demands of 2026 regulatory frameworks. By adopting a “Strategic, Systematic, Secure” approach to Software and Digital Assurance, we empower global enterprises to navigate the complexities of data protection with absolute confidence. Our team brings together multi-industry expertise and a globally-minded perspective to ensure that your security testing for gdpr compliance isn’t just a periodic checklist but a core component of your long-term operational stability. We focus on the peace of mind derived from risk reduction, allowing your leadership to focus on large-scale technological evolution while we manage the intricate details of your digital defense.

Our methodology connects deep technical proficiency with high-level business outcomes, ensuring that every validation activity provides a tangible benefit to the client’s security posture. We operate as a seasoned expert who values stability and precision, helping organizations move beyond fragmented security efforts toward a unified validation framework. By orchestrating a blend of human expertise and advanced technical tools, we provide a steady hand in a fast-changing technological landscape. This collaborative spirit ensures that your enterprise remains resilient against the sophisticated threats that define the modern digital era.

Beyond Testing: A Holistic IT Partnership

We recognize that maintaining a secure posture requires more than isolated audits; it demands a holistic partnership that leverages IT Service Management to foster long-term resilience and stability within your digital infrastructure. Our approach integrates specialized staffing solutions to ensure your internal teams are supported by experts who understand the nuances of platforms like ServiceNow and Atlassian. Global enterprises trust us for their complex digital evolutions because we act as a reliable long-term collaborator, deeply invested in their institutional maturity and scalable growth. This comprehensive support model ensures that security remains a constant, proactive force within your organization.

Next Steps for Your Compliance Roadmap

To begin roadmapping your 2026 compliance journey, we recommend performing a rigorous gap analysis of your current security testing frequency and evaluating the maturity of your DevSecOps integration. Identifying these areas for improvement is the first step toward reducing organizational risk and achieving a seamless integration of security into your digital transformation. We invite your leadership team to contact us for a comprehensive security assessment tailored to your enterprise’s unique requirements. By partnering with us, you ensure that your security testing for gdpr compliance remains robust, iterative, and fully aligned with the evolving global standards of data protection.

Securing Your Enterprise Future: The Path to Continuous Resilience

As the regulatory landscape matures, the transition from static, point-in-time audits to a model of continuous, comprehensive, and compliant validation has become an operational necessity. Enterprises must move beyond reactive measures and embrace a framework that integrates security testing for gdpr compliance into the core of their digital transformation strategy. By prioritizing the technical pillars of Article 32 and embedding automated safeguards within the DevSecOps lifecycle, organizations can achieve a state of persistent readiness that protects both their sensitive data and their market reputation.

Test Triangle acts as a reliable long-term collaborator for global enterprises navigating these complex technical requirements. As a strategic Atlassian and ServiceNow partner with specialized expertise in pharma and finance compliance, we provide the technical precision and regulatory fluency needed to manage diverse infrastructures across Europe, North America, and Asia. Our global delivery model ensures that your organization benefits from a steady hand in a fast-changing technological landscape, delivering the peace of mind that comes from professional risk reduction. Our approach is designed to be precise, proactive, and persistent, ensuring your digital evolution remains uncompromised.

Secure Your Enterprise: Schedule a GDPR Compliance Security Assessment with Test Triangle

The journey toward technical excellence is a collaborative evolution; we look forward to supporting your organization’s long-term success and operational stability.

Frequently Asked Questions

Does GDPR Article 32 explicitly require penetration testing?

While Article 32 does not explicitly name “penetration testing,” it mandates a process for regularly testing and evaluating the effectiveness of technical measures. Penetration testing is widely recognized by European data protection authorities as the standard method for fulfilling this requirement. It provides the empirical evidence needed to demonstrate that your “active defense” is functional and resilient against contemporary threats.

How often should an enterprise conduct security testing for GDPR compliance?

Enterprises should align testing frequency with their specific risk profile, typically conducting comprehensive security testing for gdpr compliance at least annually or following significant architectural changes. For high-risk processing environments, such as those in finance or pharma, a more frequent or continuous validation model is often necessary to maintain a defensible posture. This ensures that new vulnerabilities introduced during rapid deployment cycles are identified and remediated promptly.

What is the difference between a vulnerability scan and a GDPR penetration test?

A vulnerability scan is a broad, automated discovery process that identifies known security flaws within your infrastructure. In contrast, a GDPR penetration test is a targeted, human-led exercise that simulates actual exploitation to verify if those flaws can be used to access personal data. While scans provide high-level visibility, penetration tests offer the deep technical validation required to prove the resilience of your Article 32 controls.

Can automated security testing replace manual penetration testing for compliance?

Automated security testing cannot fully replace manual penetration testing because it lacks the cognitive ability to identify complex logic-based flaws or chain multiple minor vulnerabilities. Automation is highly effective for maintaining frequency within CI/CD pipelines, but manual testing provides the human expertise necessary to evaluate business logic and unauthorized data correlation. A balanced approach combines both to ensure comprehensive coverage across your entire digital ecosystem.

How do I prove to a regulator that my security testing is ‘appropriate’?

Proving that testing is “appropriate” requires detailed documentation that maps technical activities directly to the risks identified in your Data Protection Impact Assessment (DPIA). You must demonstrate a closed-loop remediation process where vulnerabilities are not only identified but also systematically patched and re-tested. This creates a machine-readable audit trail that provides regulators with evidence of your organization’s commitment to proactive data protection.

What are the common security testing pitfalls that lead to GDPR fines?

Common pitfalls include a “check-the-box” mentality that ignores the “ability to restore” clause or neglects the security of third-party API integrations. Many organizations also fail to include legacy systems in their scope, creating blind spots where personal data remains vulnerable. Avoiding these errors requires a strategic, systematic, and secure testing framework that addresses all four technical pillars of Article 32.

How does security testing change for organizations using Atlassian Cloud?

For organizations utilizing Atlassian Cloud, the focus of security testing for gdpr compliance shifts from server-level maintenance to the validation of platform configurations and shared responsibility models. Testing must prioritize user access controls, data residency settings, and the security of marketplace app integrations that may have access to your PII. This ensures that your collaborative environments remain compliant while leveraging the scalability of cloud-native enterprise software.

Is security testing required for internal-only employee data systems?

Yes, security testing is mandatory for internal-only systems because the GDPR protects all personal data, including that of your employees. HR databases and internal communication platforms often contain sensitive PII that requires the same level of technical validation as customer-facing applications. Neglecting these systems creates a significant risk of internal data breaches, which are subject to the same tiered fine structure as external violations.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.