With 94% of global enterprises now operating in the cloud as of 2026, the transition from legacy systems has become an inescapable strategic imperative. While the March 2029 end-of-life for Data Center products creates a clear timeline for migration, many leadership teams remain concerned that moving sensitive workloads might compromise their regulatory standing. You’re likely grappling with the intricacies of the Shared Responsibility Model, feeling the pressure to ensure that atlassian cloud security and compliance features align perfectly with your specific industry mandates.

We understand that the fear of data breaches during migration and the difficulty of mapping features to GDPR or HIPAA requirements can stall even the most vital digital transformations. This guide empowers you to master the complex security landscape, providing a clear roadmap to ensure your enterprise remains resilient and audit-ready. By implementing the advanced encryption protocols and data residency controls available in 2026, you’ll gain the confidence to scale without increasing your administrative burden.

We’ll explore the latest SOC 1 Type 2 attestations, the upcoming “Enterprise-Ready” Trust Program launching in October 2026, and the strategic advantages of Atlassian Guard Premium. This methodical approach transforms security from a perceived hurdle into a robust foundation for long-term operational stability.

Key Takeaways

  • Define the precise boundaries of the Shared Responsibility Model to establish a clear foundation of trust and accountability between your internal teams and the Atlassian platform.
  • Implement sophisticated atlassian cloud security and compliance features, including Atlassian Guard for centralized identity management and AES-256 encryption, to fortify your digital infrastructure.
  • Navigate the complexities of international regulatory standards by aligning your environment with the latest 2026 SOC 2 Type II and ISO/IEC 27001 audit benchmarks.
  • Adopt a “security by design” methodology by integrating automated compliance checks directly into your DevOps pipeline to mitigate legacy risks during cloud migration.
  • Leverage expert Atlassian Consulting to transition from fragmented security settings to a “Secure, Scalable, Stable” framework that ensures long-term operational resilience.

Understanding the Atlassian Cloud Shared Responsibility Model

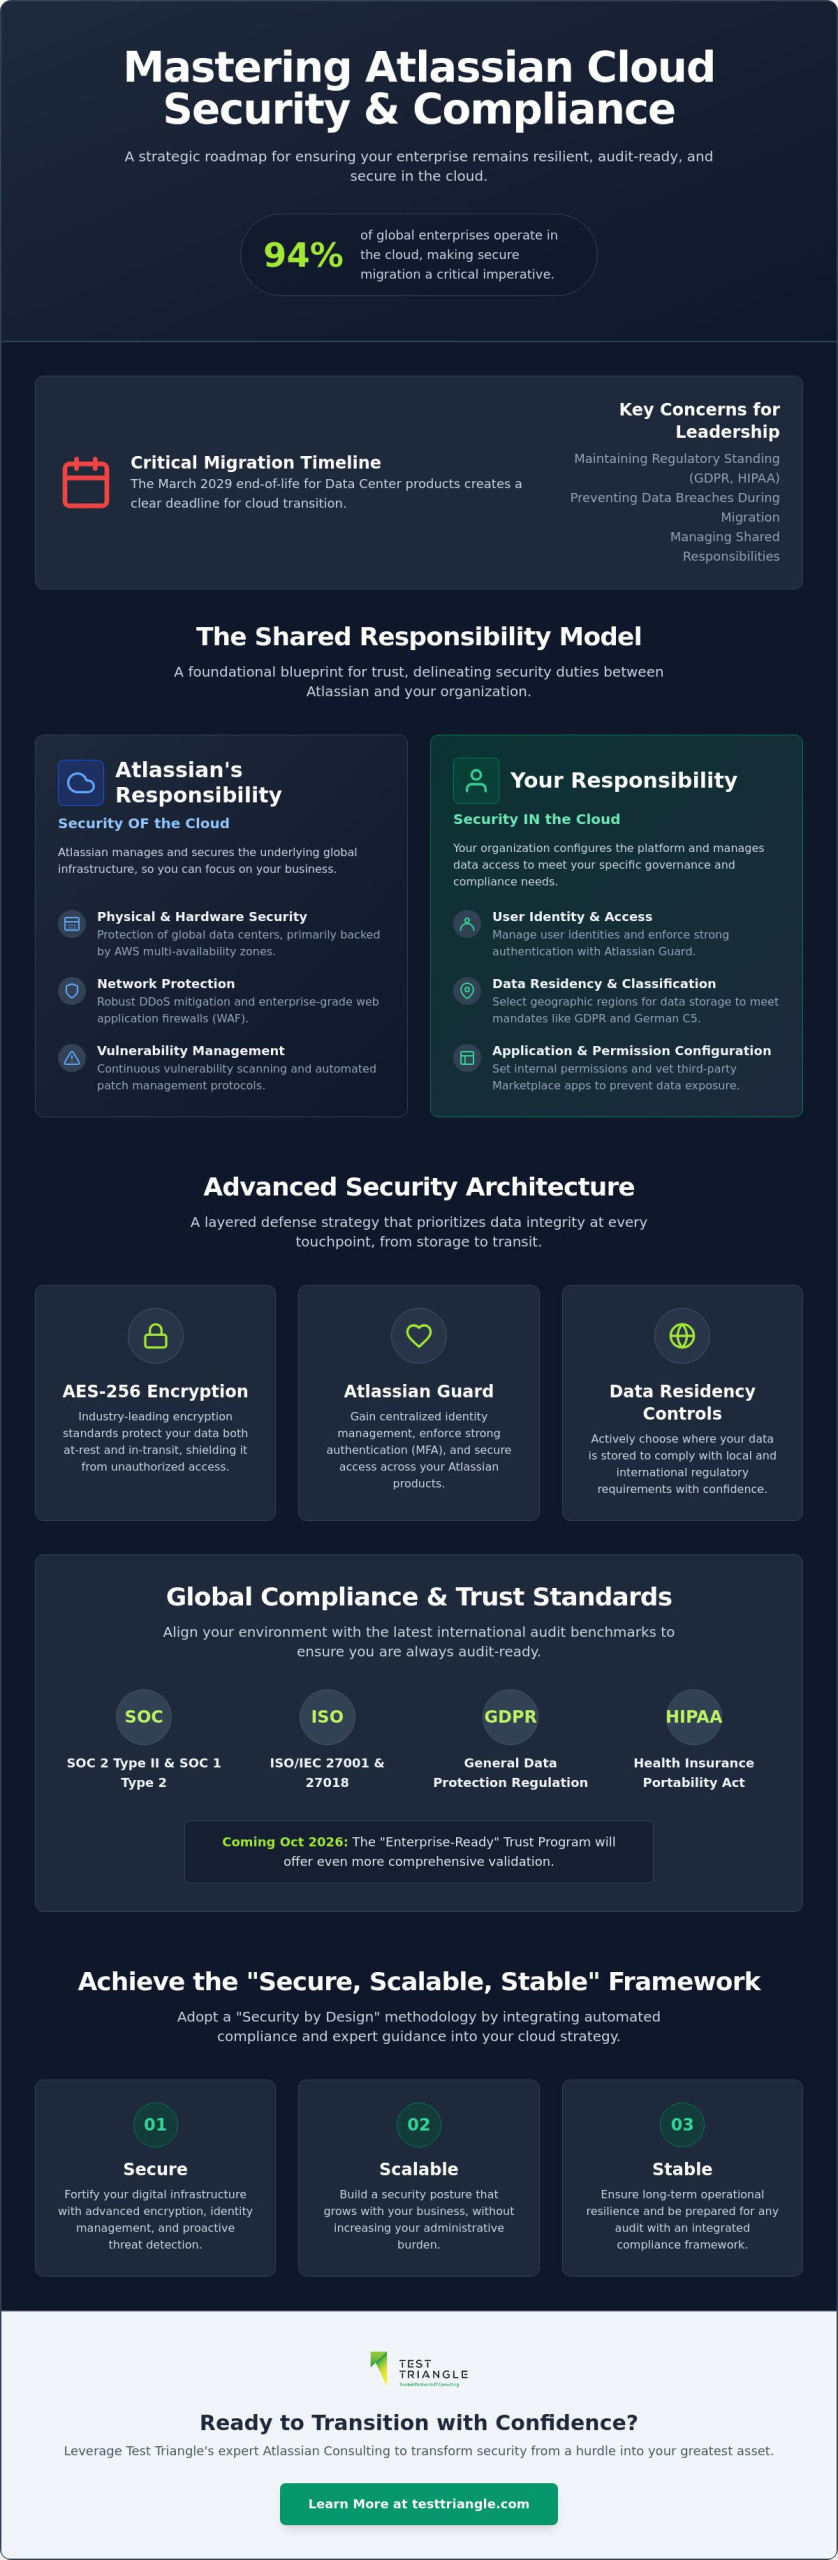
The Shared Responsibility Model functions as the foundational blueprint for trust between global enterprises and their cloud providers. It isn’t merely a technical division of labor; it’s a strategic framework that ensures organizational stability in a 2026 digital economy where data integrity is paramount. By clearly delineating which security layers are managed by the platform and which remain under your jurisdiction, this model allows leadership to allocate resources more effectively. Understanding these atlassian cloud security and compliance features is the first step toward building a resilient infrastructure that can withstand the evolving threat landscape.

The Infrastructure Layer: What Atlassian Protects

Atlassian assumes full ownership of the security “of” the cloud. This includes the physical protection of the global data center footprint, which is primarily backed by Amazon Web Services (AWS) across multiple availability zones. Their commitment to cloud security principles ensures that the underlying hardware and network layers are fortified against large-scale disruptions. You don’t have to worry about physical site access or the maintenance of server racks. Instead, you benefit from Atlassian’s sophisticated network-level protections, including robust DDoS mitigation and enterprise-grade web application firewalls. Their team manages continuous vulnerability scanning and automated patch management protocols, ensuring that the software foundation remains current without requiring manual intervention from your internal IT staff.

The Operational Layer: Your Strategic Obligations

While Atlassian secures the foundation, your organization is responsible for security “in” the cloud. This operational layer is where strategic Atlassian consulting and implementation becomes vital. You’re responsible for managing user identities, enforcing strong authentication via Atlassian Guard, and classifying data according to your internal risk profiles. In 2026, data residency has become a critical compliance requirement. You must actively select the specific geographic regions where your data resides to meet local legal mandates like GDPR or the German C5 standards. Additionally, the configuration of internal permissions and the vetting of third-party Marketplace apps fall squarely within your remit. Misconfigurations at this level are the most common cause of data exposure, making it essential to have a disciplined approach to access control. Utilizing the full suite of atlassian cloud security and compliance features requires an intentional effort to align platform capabilities with your unique corporate governance policies.

This partnership between Atlassian’s infrastructure and your operational oversight creates a comprehensive security posture. It reduces the total cost of ownership by offloading heavy lifting to the vendor while keeping you in the driver’s seat for data governance and user management.

Advanced Security Architecture: From Encryption to Atlassian Guard

Building on the shared responsibility framework, the technical architecture of the cloud environment provides the specific mechanisms required to protect corporate assets. These atlassian cloud security and compliance features represent a shift toward a holistic security posture that prioritizes data integrity at every touchpoint. In alignment with guidance from the Cloud Security Alliance, the platform implements a layered defense strategy that begins with industry-leading encryption standards. This approach ensures that information remains shielded from unauthorized access, whether it’s stored within an application or moving across the global network.

Encryption and Data Privacy Controls

Data at rest is secured using AES-256 encryption; meanwhile, data in transit relies on TLS 1.2 or higher to prevent interception. For enterprises with stringent regulatory needs, Bring Your Own Key (BYOK) capabilities allow for direct control over encryption keys. This ensures that even the cloud provider can’t access raw data without explicit authorization. Data residency features further enhance this control by allowing organizations to pin data to specific regions. In 2026, this includes expanded support for locations like Germany (C5 Type 2) and Spain (ENS). To further protect privacy, data scrubbing and anonymization tools are increasingly utilized in non-production environments to prevent the exposure of sensitive information during testing phases.

Atlassian Guard: The Enterprise Security Hub

Atlassian Guard serves as the central command center for identity and access management. It bridges the gap between your corporate directory and your cloud products, facilitating seamless Single Sign-On (SSO) with providers like Azure AD, Okta, or Google Workspace. By utilizing System for Cross-domain Identity Management (SCIM), organizations can automate user provisioning and de-provisioning. This automation is critical. It eliminates “zombie” accounts that often serve as entry points for unauthorized access. Key benefits of Guard include:

  • Enforced Security Policies: Mandatory Two-Factor Authentication (2FA) across the entire organization.
  • Centralized Visibility: A single pane of glass for monitoring user activity and API token usage.
  • Anomalous Behavior Detection: AI-driven insights that identify unusual patterns, such as rapid data egress or suspicious login attempts.

As we move through 2026, the architecture has evolved from perimeter-based defenses to a Zero Trust model. Access is no longer granted based on network location but through continuous identity verification. Since June 2026, user API token monitoring is available to all customers at no extra cost, providing a significant boost to visibility without increasing spend. To ensure these atlassian cloud security and compliance features are configured to your specific risk profile, speaking with an implementation partner can provide the necessary strategic oversight to maintain a secure and compliant environment.

Global Compliance Standards: GDPR, SOC 2, and Industry Specifics

The 2026 audit landscape demands more than just checkboxes; it requires a deep integration of regulatory controls into every workflow. Reviewing Atlassian’s SOC 2 Type II and SOC 3 reports for 2026 reveals a commitment to the highest standards of availability and confidentiality. These reports, alongside the SOC 1 Type 2 attestation achieved in Q4 2025 for Jira and Confluence, provide the transparent documentation necessary for enterprise risk assessments. By aligning with ISO/IEC 27001 and 27018, the platform offers a globally recognized benchmark for information security management that satisfies most jurisdictional requirements. However, the true strength of atlassian cloud security and compliance features lies in their ability to adapt to specific regional mandates, such as the German C5 Type 2 attestation provided in Q1 2026 or the ENS requirements in Spain slated for Q4 2026.

A significant challenge for many organizations remains the third-party ecosystem. To address this, the “Enterprise-Ready” Trust Program launches in October 2026, replacing the older “Cloud Fortified” badge with stricter standards for security and reliability. This program, combined with the “Runs on Atlassian” initiative for Forge apps, ensures that your Marketplace integrations don’t become a weak link in your compliance chain. For Australian enterprises, maintaining this chain includes ensuring that specialized financial tools like Trancher are integrated into a broader strategy for end-to-end AML/CTF program management. These initiatives allow for better control over data egress and ensure that app storage matches the data residency of the host product.

GDPR and Evolving Privacy Regulations

GDPR compliance has evolved beyond simple data processing agreements. Today, automated tools for the “right to be forgotten” allow administrators to execute data deletion and export requests across the entire site with precision. As AI adoption grows, managing data usage within Atlassian Rovo, which now serves over 5 million monthly active users, is paramount. Strategic governance ensures that AI-powered insights don’t inadvertently expose sensitive personal data, maintaining the integrity of your Data Processing Addendums (DPA). It’s essential to configure these tools to prevent unauthorized data egress while still leveraging the productivity gains of enterprise AI.

Industry-Specific Compliance: Pharma and Finance

For life sciences, GxP compliance is non-negotiable. The platform provides validated instances and comprehensive audit trails that allow for the meticulous tracking of every change, ensuring your environment remains audit-ready for health authority inspections. Similarly, financial institutions must navigate the complex requirements of BaFin, EBA, and APRA. Jira and Confluence are designed to support these standards through granular permission schemes and data residency pinning. Our expert Atlassian Consulting ensures these standards are met during implementation through rigorous validation and audit trail configuration. By leveraging these atlassian cloud security and compliance features, highly regulated firms can achieve a level of operational resilience that was previously difficult to maintain in a cloud-only environment.
Atlassian Cloud Security and Compliance Features: The 2026 Enterprise Strategic Guide

Security by Design: Integrating Compliance into Cloud Migration

Successful cloud migration requires a shift from reactive patching to a “Security by Design” philosophy. This methodology ensures that compliance isn’t an afterthought but a core component of the transition process. By leveraging atlassian cloud security and compliance features during the initial planning phases, enterprises can identify legacy risks that may have accumulated in on-premise environments over years of operation. This proactive stance reduces technical debt and streamlines cloud configurations, ensuring your new environment is built on a foundation of operational excellence and risk mitigation.

The Security Audit and Assessment Phase

Before any data moves, a comprehensive audit is essential to establish a baseline of trust. This begins with rigorous data classification to determine which workloads are suitable for the cloud and which require additional safeguards. It’s the ideal moment to implement the Principle of Least Privilege (PoLP) by cleaning up years of permission sprawl. Enterprises should also evaluate their ecosystem using the new “Enterprise-Ready” Trust Program, which replaces the Cloud Fortified badge in October 2026. Evaluating the security posture of Marketplace plugins is now more structured thanks to the Partner Security Incident Response Program established on June 18, 2026. This allows for a joint investigation of incidents affecting third-party apps, ensuring your entire ecosystem remains resilient and audit-ready from day one.

Continuous Compliance in a DevOps World

Security doesn’t end when the “migration complete” notification arrives. Integrating compliance checks into your DevOps Consulting pipeline ensures that custom integrations and configurations remain secure as they evolve. Real-time alerting and incident response planning are critical for maintaining visibility in complex cloud environments. For instance, the security bulletin from June 16, 2026, which addressed 76 high-severity and 24 critical vulnerabilities, highlights the need for rapid patch validation. By utilizing Software Test Automation Services, organizations can automatically verify that security patches don’t disrupt core functionalities. This continuous monitoring approach allows teams to respond to threats with agility while maintaining the integrity of their atlassian cloud security and compliance features.

Maintaining this level of technical rigor requires a partner who understands the intersection of security and speed. If you’re ready to build a compliant, high-performance cloud environment that scales with your ambition, contact our strategic consultants today to begin your security assessment.

Optimising Security with Test Triangle’s Atlassian Consulting

While the technical capabilities of the cloud platform are robust, the human element remains the deciding factor in enterprise resilience. Orchestrating the complex settings of atlassian cloud security and compliance features requires more than just a manual; it demands a strategic visionary who can align these tools with global business objectives. Test Triangle acts as a steady hand in this fast-changing technological landscape, employing a “Secure, Scalable, Stable” framework to ensure your digital infrastructure doesn’t just meet today’s standards but is prepared for the regulatory shifts of 2027 and beyond. By bridging the gap between raw technical features and business-critical compliance, we transform security from a cost center into a foundation for organizational progress.

Maintaining 24/7 security vigilance is a significant undertaking for internal IT departments already stretched by digital transformation demands. By leveraging our Managed Service Provider Subscription Fees model, organizations gain access to continuous monitoring and expert oversight that ensures no vulnerability goes unaddressed. This partnership model provides the peace of mind derived from risk reduction, allowing your leadership to focus on core innovation while we manage the intricacies of your cloud environment. We prioritize operational efficiency and systemic improvement, ensuring that your security posture evolves in tandem with your growth.

Strategic Roadmapping and Advisory

We don’t believe in one-size-fits-all solutions. Our consulting begins with tailored security configurations based on your specific industry risk profile, whether you’re navigating the GxP requirements of life sciences or the stringent mandates of the financial sector. We provide expert guidance on Atlassian Guard implementation and complex IAM integration with industry-leading platforms like Azure AD and Okta. To support these initiatives, our staffing solutions provide dedicated security experts who act as an extension of your team, ensuring that your atlassian cloud security and compliance features are managed with institutional maturity and technical rigor.

Long-Term Partnership and Support

Resilience is a continuous journey rather than a destination. We act as a reliable long-term collaborator, providing regular security health checks and compliance re-validation services to address the evolving threat landscape. Our approach includes training your team on Atlassian security best practices and threat awareness, empowering your workforce to become the first line of defense. This methodical and highly structured support system ensures that your organization remains audit-ready and resilient. To begin fortifying your infrastructure, contact Test Triangle today for a comprehensive Atlassian Cloud Security Assessment and secure your enterprise’s digital future.

Future-Proofing Your Enterprise Digital Ecosystem

The transition to a resilient cloud environment requires more than just deploying software; it necessitates a disciplined alignment of platform capabilities with rigorous corporate governance. By mastering the atlassian cloud security and compliance features discussed in this guide, your organization can move beyond the complexities of the Shared Responsibility Model to achieve a state of operational excellence. This strategic evolution ensures that your data remains protected, your audits stay green, and your teams remain empowered to innovate without the fear of security compromises or regulatory friction.

As an Atlassian Gold Solution Partner with ISO 27001 certified processes, Test Triangle provides the institutional maturity and technical rigor required to manage your most sensitive workloads. Our global delivery model offers 24/7 managed support, providing a Secure, Scalable, Stable foundation that acts as a reliable long-term collaborator for your business. We’re ready to help you bridge the gap between technical execution and long-term operational stability through expert-led managed services that grow with your ambition.

Secure Your Infrastructure with Test Triangle’s Atlassian Consulting and embrace the confidence of a fully compliant digital future.

Frequently Asked Questions

Is Atlassian Cloud more secure than on-premise Data Center deployments?

Atlassian Cloud provides superior security through centralized infrastructure management and rapid patch deployment. While Data Center relies on manual updates, cloud instances benefit from immediate vulnerability remediation, such as the 100 high and critical vulnerabilities addressed in June 2026. This model reduces the risk of zero-day exploits and allows your IT staff to focus on strategic governance rather than hardware maintenance.

How does Atlassian Guard help with enterprise compliance requirements?

Atlassian Guard serves as the primary engine for identity-based compliance by enforcing mandatory Two-Factor Authentication (2FA) and centralized Single Sign-On (SSO). It facilitates automated user provisioning via SCIM, which eliminates the risk of “zombie” accounts. These atlassian cloud security and compliance features provide the audit trails and access controls necessary to satisfy SOC 2 and ISO 27001 requirements across your entire digital ecosystem.

Where is my data stored in Atlassian Cloud and can I choose the location?

Your data is stored within a global network of AWS-backed data centers. Enterprise customers can utilize data residency controls to pin primary product data to specific geographic regions, such as Germany for C5 compliance or Spain for ENS requirements. This capability ensures that your organizational data remains within jurisdictional boundaries, satisfying local legal mandates and reducing the complexity of international privacy regulations.

What happens to my data security when I use Atlassian Marketplace apps?

Security for Marketplace apps is a shared responsibility between Atlassian, the app vendor, and your organization. To mitigate risks, you should prioritize apps within the “Enterprise-Ready” Trust Program or the “Runs on Atlassian” initiative. These programs ensure higher standards for data egress control and residency matching, providing a more secure and predictable environment for third-party integrations.

Does Atlassian Cloud support HIPAA compliance for healthcare organizations?

Yes, Atlassian Cloud supports HIPAA compliance for Jira, Confluence, and Jira Service Management. Organizations must enter into a Business Associate Agreement (BAA) and configure their instances to meet specific administrative and technical safeguards. This includes implementing strong encryption and granular access controls to ensure that Protected Health Information (PHI) is managed with the highest standards of confidentiality and integrity.

How can I automate security monitoring within Jira and Confluence?

Automation is achieved through Atlassian Guard’s proactive threat detection and real-time alerting systems. Since June 2026, all customers can monitor user API token usage at no extra cost to identify suspicious activity. Additionally, AI-driven insights within the platform detect anomalous user behaviors, such as rapid data exports, allowing for an immediate incident response that maintains the integrity of your atlassian cloud security and compliance features.

What is the Shared Responsibility Model in the context of Atlassian Cloud?

The Shared Responsibility Model defines the division of security obligations between the provider and the client. Atlassian is responsible for the security “of” the cloud, including physical hardware and network infrastructure. Conversely, your organization is responsible for security “in” the cloud, which encompasses user access management, data classification, and the secure configuration of your specific application instances.

How often does Atlassian undergo third-party security and compliance audits?

Atlassian undergoes rigorous third-party audits on a continuous basis to maintain its various certifications. For instance, Jira and Confluence were attested against SOC 1 Type 2 requirements in Q4 2025, and a German C5 Type 2 attestation was provided in Q1 2026. These regular evaluations ensure that the platform’s security controls remain effective against the evolving threat landscape and current global benchmarks.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.
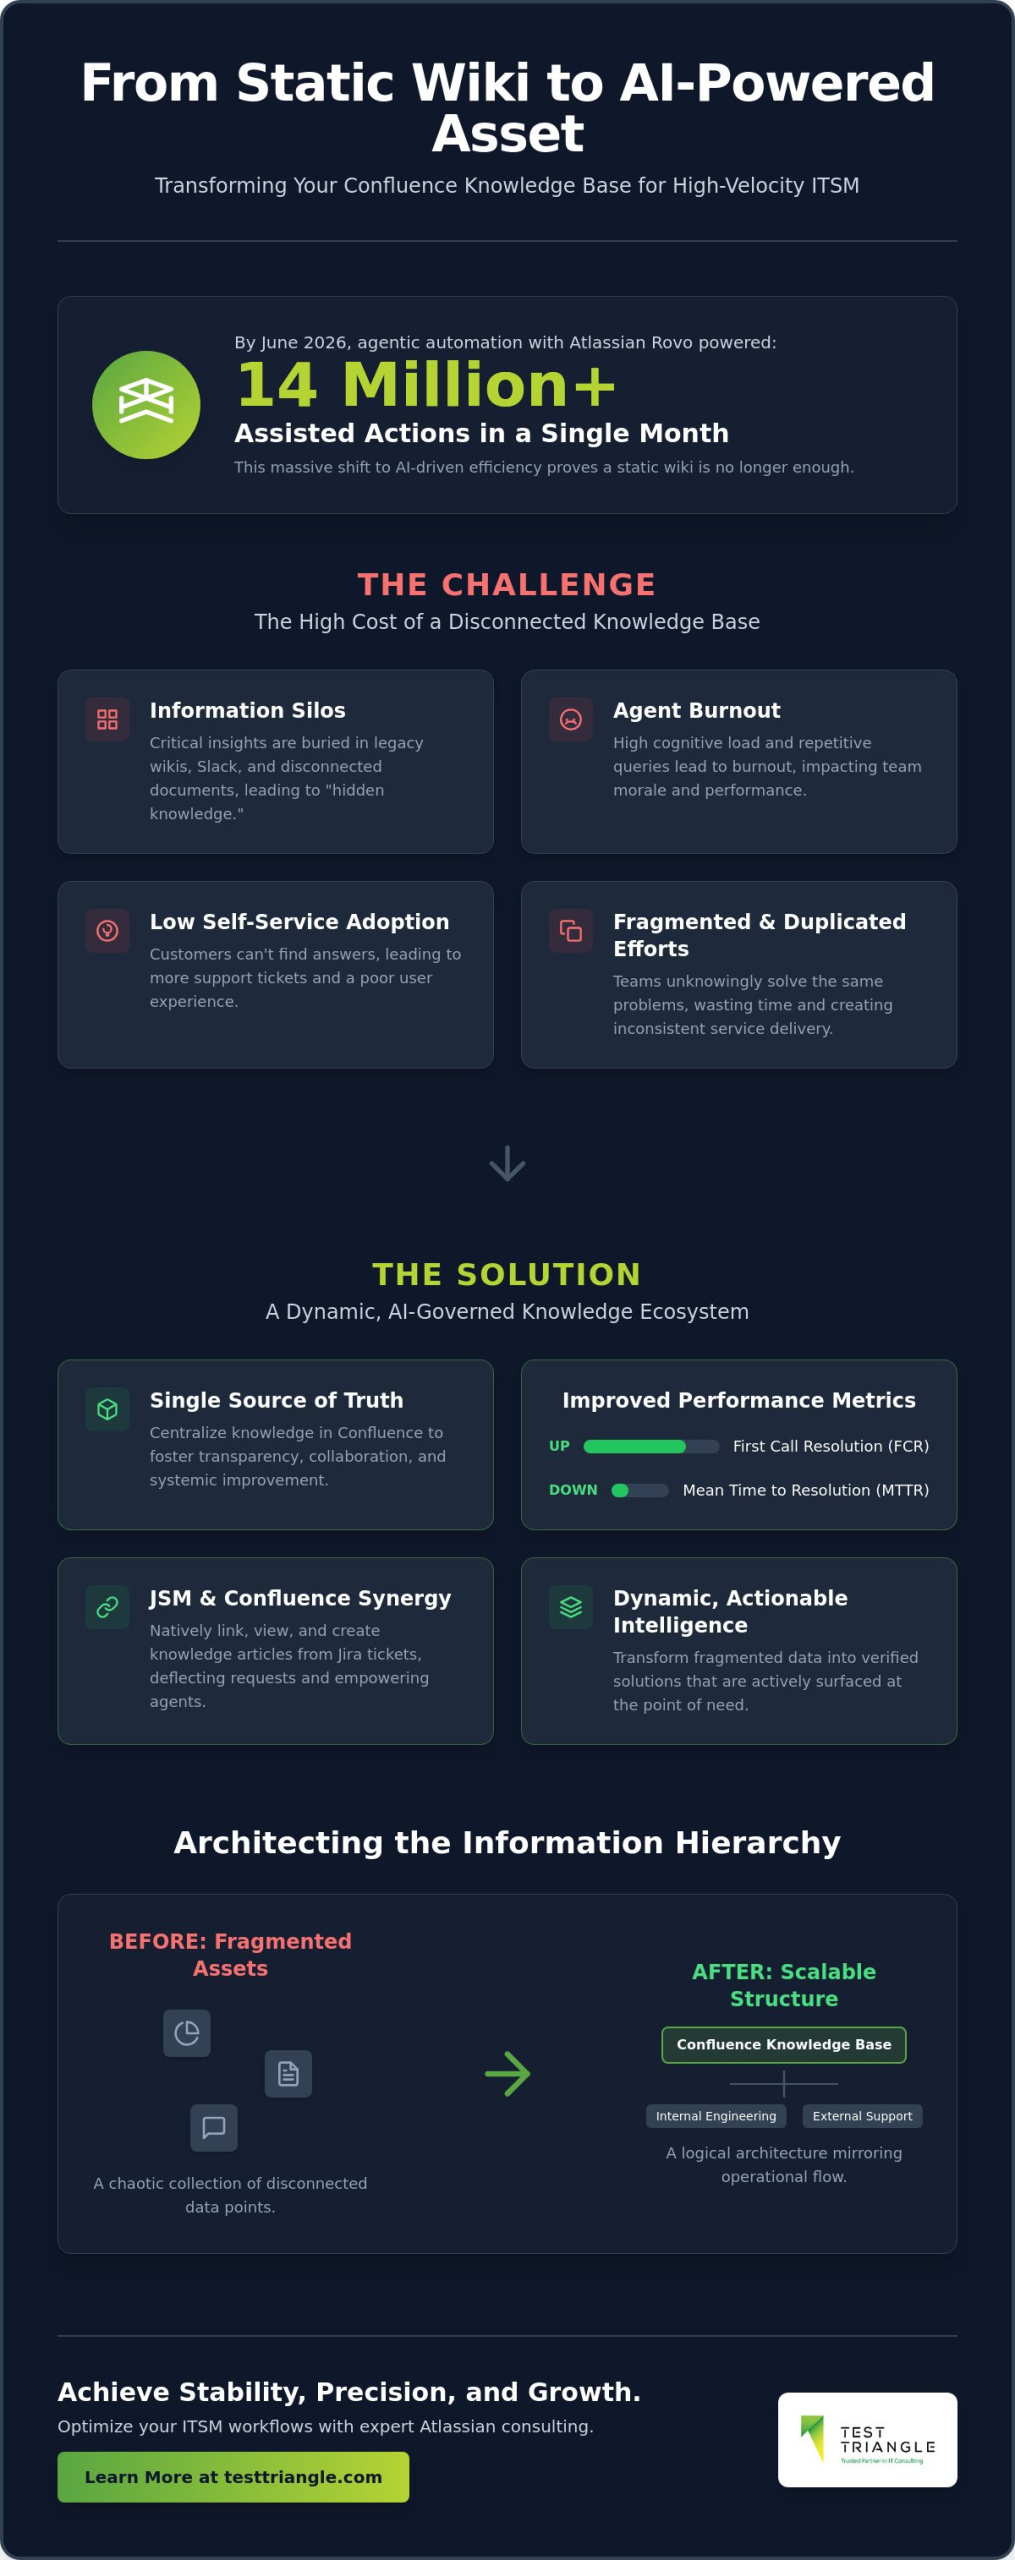
Did you know that by June 2026, agentic automation powered by Atlassian Rovo supported more than 14 million assisted actions in a single month? This massive shift toward AI-driven efficiency highlights a critical reality for global enterprises: a static wiki is no longer enough to support modern service delivery. To maintain operational stability, your organization needs a robust confluence knowledge base for itsm that functions as a dynamic, AI-governed engine rather than a forgotten digital archive.

We recognize that information silos across Slack and legacy wikis often lead to low self-service adoption and agent burnout, creating a fragmented landscape that hinders organizational progress. This guide demonstrates how to transform these disparate data points into a high-velocity asset by leveraging strategic Atlassian governance to drive precision, performance, and progress. You’ll discover the methodology required to establish a single source of truth, increase first-call resolution rates, and secure a seamless integration between Jira Service Management and Confluence. By bridging the gap between technical execution and business outcomes, we’ll outline a path toward a scalable, secure, and sophisticated knowledge ecosystem that empowers your workforce and satisfies your customers.

Key Takeaways

  • Understand the evolution from static documentation to a dynamic ecosystem, positioning a confluence knowledge base for itsm as a high-velocity asset that drives organizational progress.
  • Master the architectural principles of information hierarchy to establish a scalable source of truth that bridges the gap between internal engineering and external support.
  • Harness the capabilities of Atlassian Rovo to eliminate information silos, enabling teams to surface critical insights across fragmented SaaS tools with AI-driven precision.
  • Follow a structured implementation roadmap to audit and transition legacy assets into optimized templates that reduce agent burnout and accelerate resolution.
  • Leverage strategic Atlassian consulting to achieve the stability, precision, and growth necessary for managing complex digital infrastructures.

The Strategic Role of a Confluence Knowledge Base in Modern ITSM

In the high-velocity environment of 2026, the traditional wiki has evolved into a sophisticated engine for operational stability. A confluence knowledge base for itsm is no longer a passive repository of “how-to” articles; it’s a strategic asset that powers the entire service lifecycle. By 2026, the paradigm has shifted from static documentation to dynamic knowledge sharing. This evolution ensures that information isn’t just stored but is actively surfaced at the point of need, transforming fragmented data into actionable intelligence. This transition is essential for organizations aiming to achieve institutional maturity and maintain a competitive edge in complex digital landscapes.

Effective knowledge management serves as a cornerstone of the ITIL 4 Service Value System, ensuring that every service interaction contributes to value co-creation. When teams integrate their knowledge assets directly into IT Service Management (ITSM) frameworks, the impact on performance metrics is profound. We see a direct correlation between advanced knowledge governance and improvements in First Call Resolution (FCR) and Mean Time to Resolution (MTTR). By providing agents with immediate access to verified solutions, enterprises reduce the cognitive load on staff, mitigate agent burnout, and deliver the peace of mind that comes from predictable, high-quality service outcomes.

Breaking Down Information Silos in Global Enterprises

Fragmented data remains a significant barrier to organizational progress. In many global enterprises, critical insights are often buried within legacy wikis, disconnected PDF repositories, or transient chat histories. These silos create “hidden knowledge” that is inaccessible to the broader team, leading to duplicated efforts and inconsistent service delivery. Confluence acts as a unified layer that bridges these gaps, providing a single source of truth for cross-functional DevOps and IT teams. This centralized approach fosters a culture of transparency and collaboration, allowing organizations to capitalize on their collective expertise and drive systemic improvement through stability, precision, and growth.

The Symbiosis of Jira Service Management and Confluence

The native integration between Jira Service Management and Confluence creates a powerful synergy that redefines the agent and customer experience. Within the agent workspace, team members can view, link, or even create knowledge articles directly from a ticket, ensuring that the confluence knowledge base for itsm stays current with real-world issues. Simultaneously, customer portals leverage this data to deflect incoming requests by suggesting relevant articles as users type their queries. Implementing professional IT Service Management solutions ensures this integration is optimized for high-velocity delivery, allowing your organization to scale its support capabilities without a linear increase in headcount. This collaborative framework positions your company as a reliable long-term partner capable of navigating the complexities of modern digital infrastructure.

Architecting the Information Hierarchy for High-Velocity Service Delivery

Establishing a high-performance confluence knowledge base for itsm requires a logical architecture that mirrors your organization’s operational flow rather than just a collection of documents. By designing a scalable space structure that distinguishes between internal engineering documentation and external customer support content, enterprises can ensure that technical staff and end-users access the precise information they require without cognitive overhead. This structural precision is supported by rigorous naming conventions and metadata standards, which empower search algorithms to surface relevant articles with surgical accuracy. When sensitive technical data is involved, utilizing page restrictions and granular permissions becomes a critical component of your risk reduction strategy, maintaining security without sacrificing the speed of service delivery.

Preventing “knowledge rot” is a primary challenge for global organizations, requiring a proactive content lifecycle policy that identifies and archives outdated entries. Without these safeguards, the accumulation of irrelevant documentation can lead to agent confusion and increased resolution times. Implementing a structured hierarchy allows your team to move from a state of reactive information gathering to a proactive, solution-oriented environment. If you’re looking for guidance on refining these structures, discussing your knowledge architecture with our specialists can provide the clarity needed for long-term success.

Designing Spaces for Scalability and Precision

Strategic space organization begins with a clear distinction between Global Knowledge Spaces, which house universal policies, and Departmental Workspaces, which contain specialized technical insights. By employing Space Categories, administrators can organize content for different user personas, ensuring that a DevOps engineer and a front-office clerk see the most relevant data for their specific roles. Integrating Atlassian implementation best practices during the initial setup phase ensures that the technical architecture remains resilient as your digital infrastructure evolves, providing a steady hand in a fast-changing technological landscape.

Implementing Robust Governance and Content Lifecycle

Knowledge Governance is the systematic oversight of content accuracy and relevance. This discipline requires clearly defined roles, including Knowledge Owners who oversee space strategy, Subject Matter Experts (SMEs) who verify technical accuracy, and Knowledge Managers who facilitate the overall flow of information. To maintain institutional maturity, we recommend a 90-day review cycle for critical ITSM documentation, such as Runbooks and Post-Incident Reports (PIRs). Adhering to these ensures that your confluence knowledge base for itsm remains a reliable, high-velocity asset that supports operational stability and empowers your workforce through large-scale technological evolution.

Leveraging Atlassian Intelligence and Rovo for Knowledge Discovery

In the high-velocity technological landscape of 2026, the ability to surface relevant information across disparate platforms has become the defining characteristic of an elite service desk. Atlassian Rovo serves as a sophisticated AI operating layer that connects work and knowledge, not just within your confluence knowledge base for itsm, but across more than 50 connected third-party applications. By June 2026, Rovo supported more than 14 million assisted actions in a single month, demonstrating its maturity as a tool for global enterprises. This AI-driven discovery engine understands user intent with surgical precision, ensuring that customers find exact solutions through self-service portals while agents receive real-time recommendations during active incident management. By integrating these capabilities, organizations can move beyond simple keyword searches to a model of intelligent knowledge surfacing that significantly reduces cognitive load.

While the benefits are substantial, we recognize the inherent risks associated with AI-generated content, particularly regarding technical accuracy. Addressing the challenge of “AI Hallucinations” requires a disciplined human-in-the-loop validation process where Subject Matter Experts (SMEs) verify AI-drafted articles before they’re published to the wider organization. This strategic oversight ensures that while Atlassian Intelligence handles the heavy lifting of summarization and tone adjustment, the technical integrity of your documentation remains uncompromised. Adhering to these ITIL best practices ensures that AI remains a tool for augmentation rather than a source of operational risk.

Rovo: The AI Search Engine for the Modern Enterprise

Rovo’s ability to index data from third-party applications like Slack, Google Drive, and GitHub eliminates the friction of context switching by providing a unified search experience. Beyond simple discovery, Rovo Agents can be deployed to automate repetitive knowledge tasks, such as identifying and updating “Known Errors” based on recent deployment logs or developer commits. For organizations looking to bridge the gap between development and operations, our insights on DevOps Consulting offer a blueprint for integrating these AI agents directly into the CI/CD pipeline. This systemic improvement allows your team to maintain a high-velocity confluence knowledge base for itsm that evolves at the same pace as your software delivery.

Enhancing the Agent Experience with Atlassian Intelligence

Atlassian Intelligence provides a suite of internal tools designed to accelerate agent workflows, such as the ability to draft comprehensive Post-Incident Reports (PIRs) directly from Jira ticket history. This feature extracts key timelines, root causes, and resolution steps, allowing agents to focus on strategic improvements rather than administrative documentation. Additionally, the “Smart Links” feature provides instant context for technical terms or internal projects without requiring the user to leave the page. Ultimately, AI in ITSM is a force multiplier that converts raw data into actionable intelligence at the point of service. This approach empowers technical managers and executive leadership alike by fostering an environment of institutional maturity and operational stability.

Confluence Knowledge Base for ITSM: A Strategic Guide to Enterprise Knowledge Management in 2026

Implementation Roadmap: Transitioning from Static to Dynamic Knowledge

Transitioning to a high-velocity confluence knowledge base for itsm requires more than a simple data transfer; it demands a structured audit of existing assets to identify critical gaps in technical documentation. By analyzing legacy wikis, shared drives, and disconnected repositories, organizations can determine which assets remain relevant and which require immediate decommissioning to prevent information bloat. Once this audit is complete, selecting and customizing ITSM-specific templates, such as standardized “How-to” guides, “Known Errors” logs, and “Change Plans,” ensures that all future content adheres to a consistent, professional standard. This methodical approach establishes a foundation for operational stability and systemic improvement across the entire service value chain.

Executing a phased migration strategy is essential for minimizing operational downtime during large-scale digital transformations. We recommend launching a pilot program with a “Champion Team,” a small, versatile group of technical experts who can refine the structure and workflows before a global rollout occurs. To measure the success of this transition, enterprises must establish clear KPIs for knowledge health. Metrics such as “Article Usefulness” scores and “Deflection Rate” provide tangible evidence of the system’s impact on service efficiency, ensuring that technical managers and executive leadership can track organizational progress with precision. This disciplined framework allows for the combination of human expertise and technical tools to deliver a superior service experience.

The Data Migration and Cleanup Phase

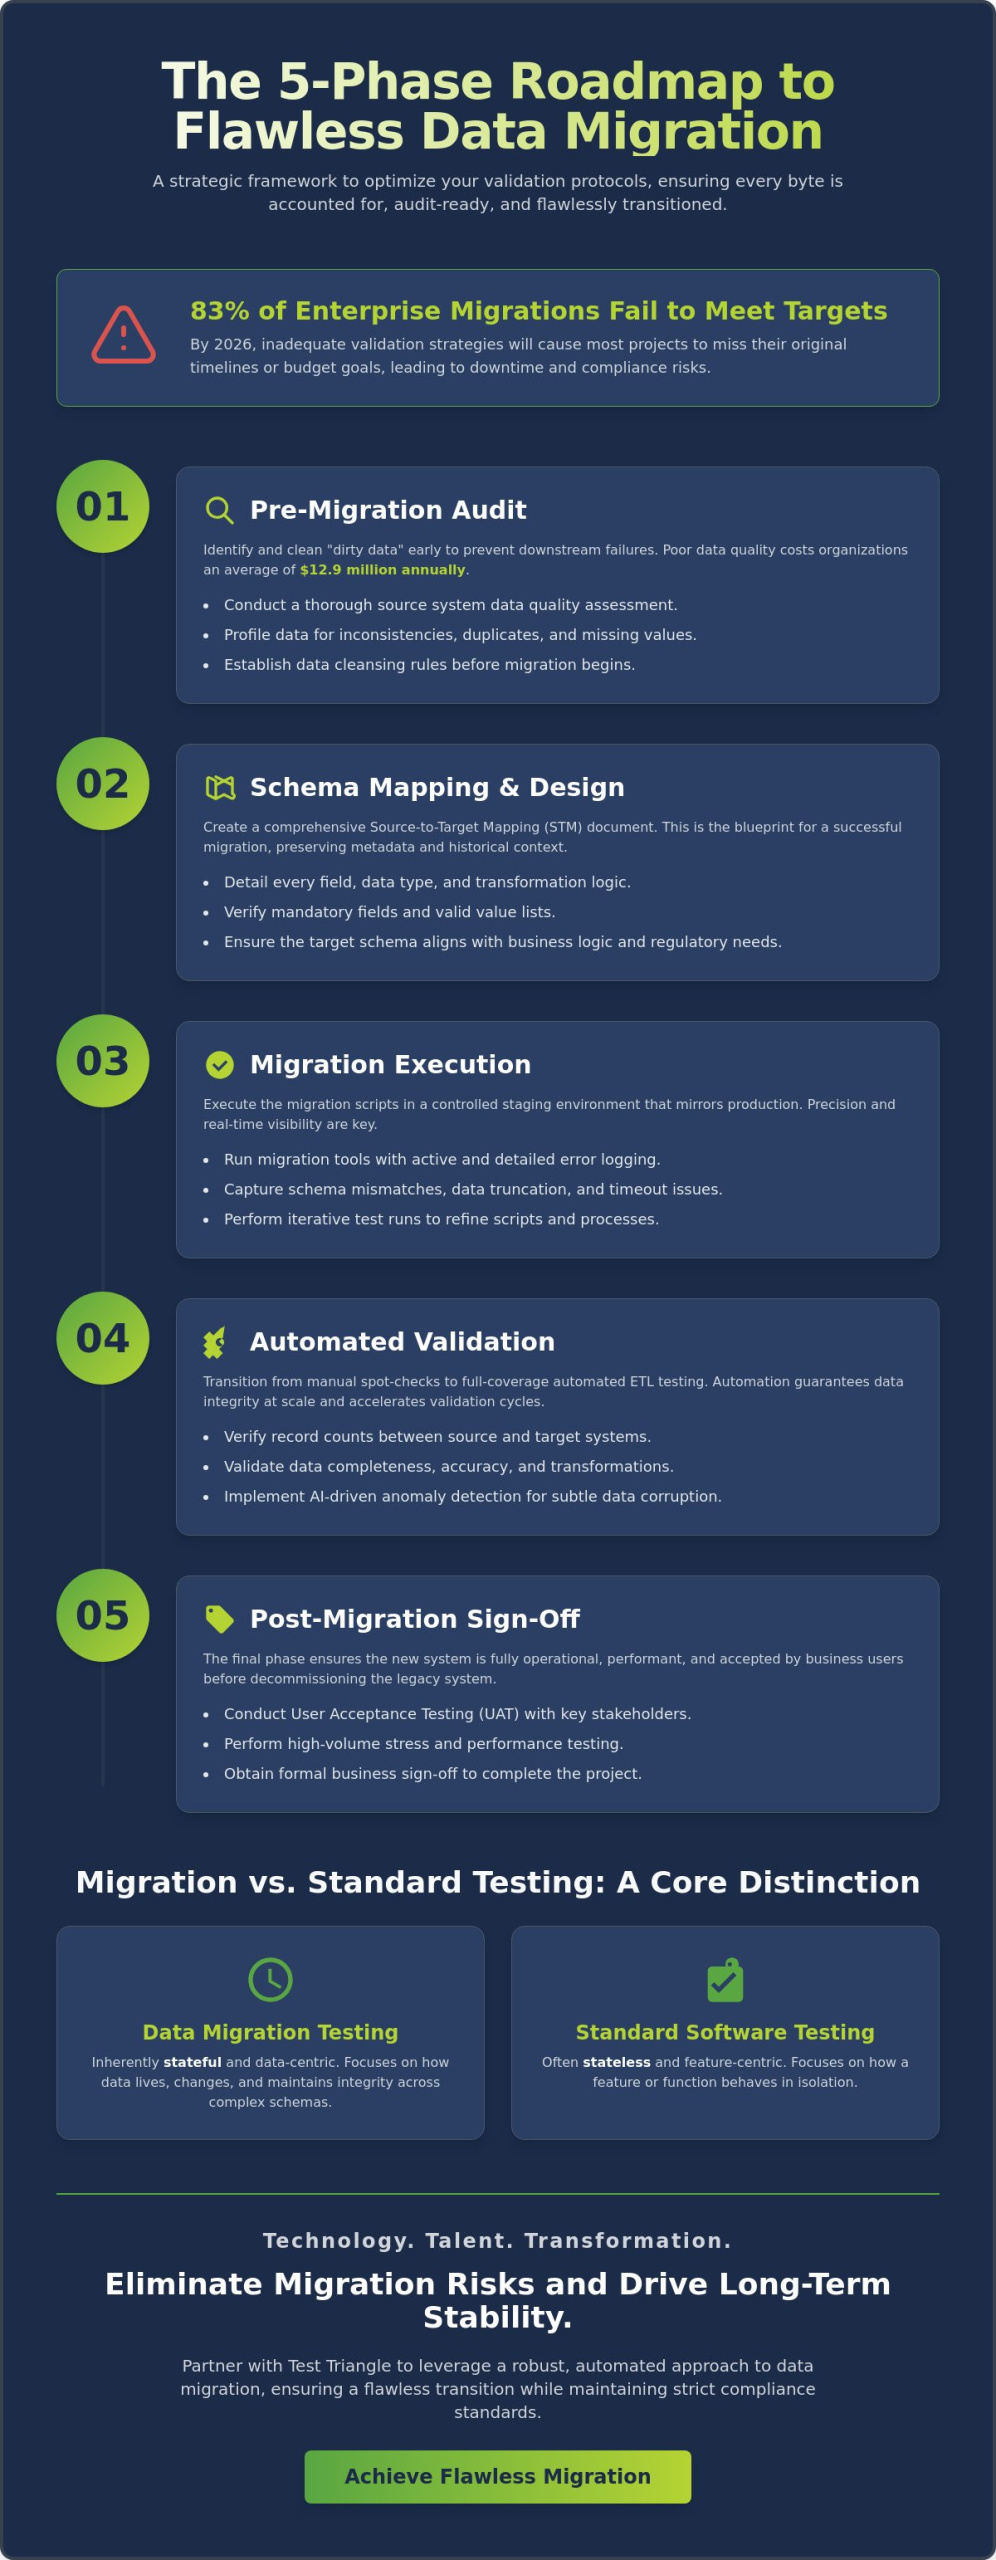
A critical component of this roadmap is the “ROT” analysis, which requires teams to Remove, Outdate, or Transform legacy content. This process ensures that the new environment isn’t polluted with redundant or trivial information that could lead to agent burnout. During the technical migration, preserving link integrity is paramount to prevent broken cross-references that frustrate both agents and customers. Leveraging Software and Digital Assurance Testing ensures data parity after the migration, confirming that the technical architecture remains robust and secure. This level of rigor is what distinguishes a seasoned expert from a mere service provider in the complex landscape of enterprise IT.

Training and Cultural Adoption Strategies

Sustainable success relies on shifting the organizational mindset from “Knowledge is Power” to “Knowledge Sharing is Power.” Adopting a Knowledge Centered Service (KCS) methodology encourages continuous content creation as a natural byproduct of the problem-solving process, ensuring the confluence knowledge base for itsm remains a living asset. To drive this cultural evolution, we propose gamification strategies that reward Subject Matter Experts (SMEs) for their contributions and peer-reviewed accuracy. This approach fosters a spirit of partnership and support, ensuring that knowledge management becomes a core competency of the enterprise, ultimately delivering stability, scalability, and success. If your organization is ready to modernize its service delivery, consult with our Atlassian experts to begin your strategic implementation roadmap today.

Optimizing ITSM Workflows with Test Triangle’s Atlassian Consulting

Test Triangle operates as a strategic visionary in the Atlassian ecosystem, providing the high-level expertise required to transform a standard confluence knowledge base for itsm into a bespoke enterprise asset. While the technical tools provide the framework, it’s our deep institutional maturity that allows us to align these platforms with your specific business outcomes. By leveraging our “Partner Approach” to digital transformation, we ensure that every configuration choice serves the dual goals of risk reduction and operational stability. This expert oversight significantly reduces the “Time to Value” for new deployments, allowing global enterprises to bypass common implementation pitfalls and achieve immediate systemic improvement. Our methodology connects technical rigor with a deep understanding of your operational needs, ensuring that the transition from fragmented information to a unified truth is both seamless and sustainable.

We don’t just implement software; we engineer environments that foster collaboration and empower your workforce through human expertise and technical tools. This collaborative framework positions our team as a steady hand in a fast-changing technological landscape, emphasizing organizational progress through a combination of precision, performance, and progress. As a reliable long-term collaborator, we’re deeply invested in your long-term success and operational stability, ensuring that your digital infrastructure remains resilient as your organization evolves.

Customized ITSM Solutions for Regulated Industries

For organizations operating within highly regulated sectors such as finance, healthcare, and pharmaceuticals, a generic knowledge setup is insufficient to meet modern standards. We specialize in tailoring Confluence to meet stringent compliance requirements, ensuring that every article and workflow maintains a robust audit trail for future reviews. This level of precision is explored further in our Atlassian Partner Guide, which outlines the methodology for scaling enterprise quality across complex digital infrastructures. By prioritizing security and standards, we provide the peace of mind necessary for large-scale technological evolution in even the most scrutinized industries.

Maximizing ROI Through Strategic Atlassian Licensing

Achieving a high return on investment requires a disciplined approach to license management within the Atlassian Cloud ecosystem. Test Triangle optimizes your license spend by ensuring that your subscription tiers align perfectly with your actual usage and growth projections, preventing unnecessary overhead. Beyond the initial setup, our Managed Outsourcing Services provide recurring monthly support that addresses system maintenance, updates, and ongoing environment optimization. This steady hand ensures that your confluence knowledge base for itsm remains a high-velocity asset that grows alongside your organization, delivering stability, scalability, and success. Partner with Test Triangle for your Atlassian Transformation to secure the stability and growth your enterprise demands.

Scaling Success, Securing Stability, Sustaining Growth

The transition from fragmented documentation to a high-velocity knowledge ecosystem requires a disciplined combination of technical precision and strategic governance. By architecting a robust information hierarchy and leveraging the agentic automation of Atlassian Rovo, global enterprises can transform their service delivery from a reactive cost center into a proactive, AI-powered asset. Establishing a confluence knowledge base for itsm isn’t merely a software implementation; it’s a commitment to institutional maturity that empowers your workforce and satisfies your customers through predictable, high-quality outcomes. This journey involves bridging the gap between technical execution and business value, ensuring that your organization remains resilient in a fast-changing technological landscape.

As an Atlassian Platinum Solution Partner with a global presence, Test Triangle acts as a steady hand for organizations navigating complex legacy-to-cloud migrations across diverse, highly regulated industries. We position ourselves as a reliable long-term collaborator, deeply invested in your operational stability and long-term success. Our experts provide the strategic visionary perspective needed to reduce risk and maximize the ROI of your Atlassian ecosystem. Accelerate your ITSM maturity with Test Triangle’s Atlassian Consulting and secure the future of your enterprise knowledge management. We’re ready to help you turn your digital infrastructure into a competitive advantage.

Frequently Asked Questions

How does Confluence integrate with Jira Service Management for ITSM?

Confluence integrates with Jira Service Management by establishing a direct link between service tickets and your documentation repository, allowing agents to surface solutions without leaving their active workspace. This native synergy enables automated article suggestions within the customer portal, which effectively deflects common requests before they enter the support queue.

What are the best templates for an IT knowledge base in Confluence?

The most effective templates for an IT knowledge base include standardized “How-to” articles, “Known Error” logs, and comprehensive “Post-Incident Reports” (PIRs). These structured frameworks ensure that all technical documentation remains consistent, professional, and easily searchable across the entire enterprise service value chain.

Can Confluence handle complex permissions for external customer documentation?

Yes, Confluence provides granular page restrictions and space-level permissions that allow organizations to manage sensitive technical data while maintaining public-facing support content. This dual-layered security model ensures that internal engineering details remain protected while end-users receive the precise information they need for self-service resolution.

How does Atlassian Rovo change the way teams find knowledge in 2026?

In 2026, Atlassian Rovo revolutionizes discovery by indexing information across more than 50 third-party applications, including Slack, Google Drive, and GitHub. This capability allows a confluence knowledge base for itsm to serve as a unified search hub, surfacing relevant insights with AI-driven intent regardless of where the data was originally created.

What is the difference between a service desk and a knowledge base?

A service desk is a transactional platform designed for managing incoming requests and incidents, whereas a knowledge base is a centralized repository for storing verified solutions and documentation. While the service desk facilitates the interaction between the user and the agent, the knowledge base provides the intelligence required to resolve issues with precision and speed.

How often should we audit our Confluence knowledge base articles?

We recommend a structured 90-day review cycle for critical documentation, supplemented by trigger-based audits following major software releases or significant system changes. This proactive approach prevents the accumulation of outdated information and ensures that your knowledge assets remain a reliable source of truth for both agents and customers.

What are the common mistakes when setting up a Confluence KB for IT teams?

Common errors include failing to establish clear naming conventions and neglecting to implement a formal governance policy for the content lifecycle. Without these structural safeguards, a confluence knowledge base for itsm can quickly become a fragmented archive of irrelevant data, leading to low user adoption and increased agent burnout.

How can we measure the ROI of our knowledge management strategy?

Measuring the ROI of your knowledge strategy requires a disciplined analysis of request deflection rates, which quantify the number of tickets avoided through effective self-service. Additionally, tracking improvements in Mean Time to Resolution (MTTR) and First Call Resolution (FCR) provides tangible evidence of how a high-velocity knowledge ecosystem reduces operational costs and enhances service quality.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.
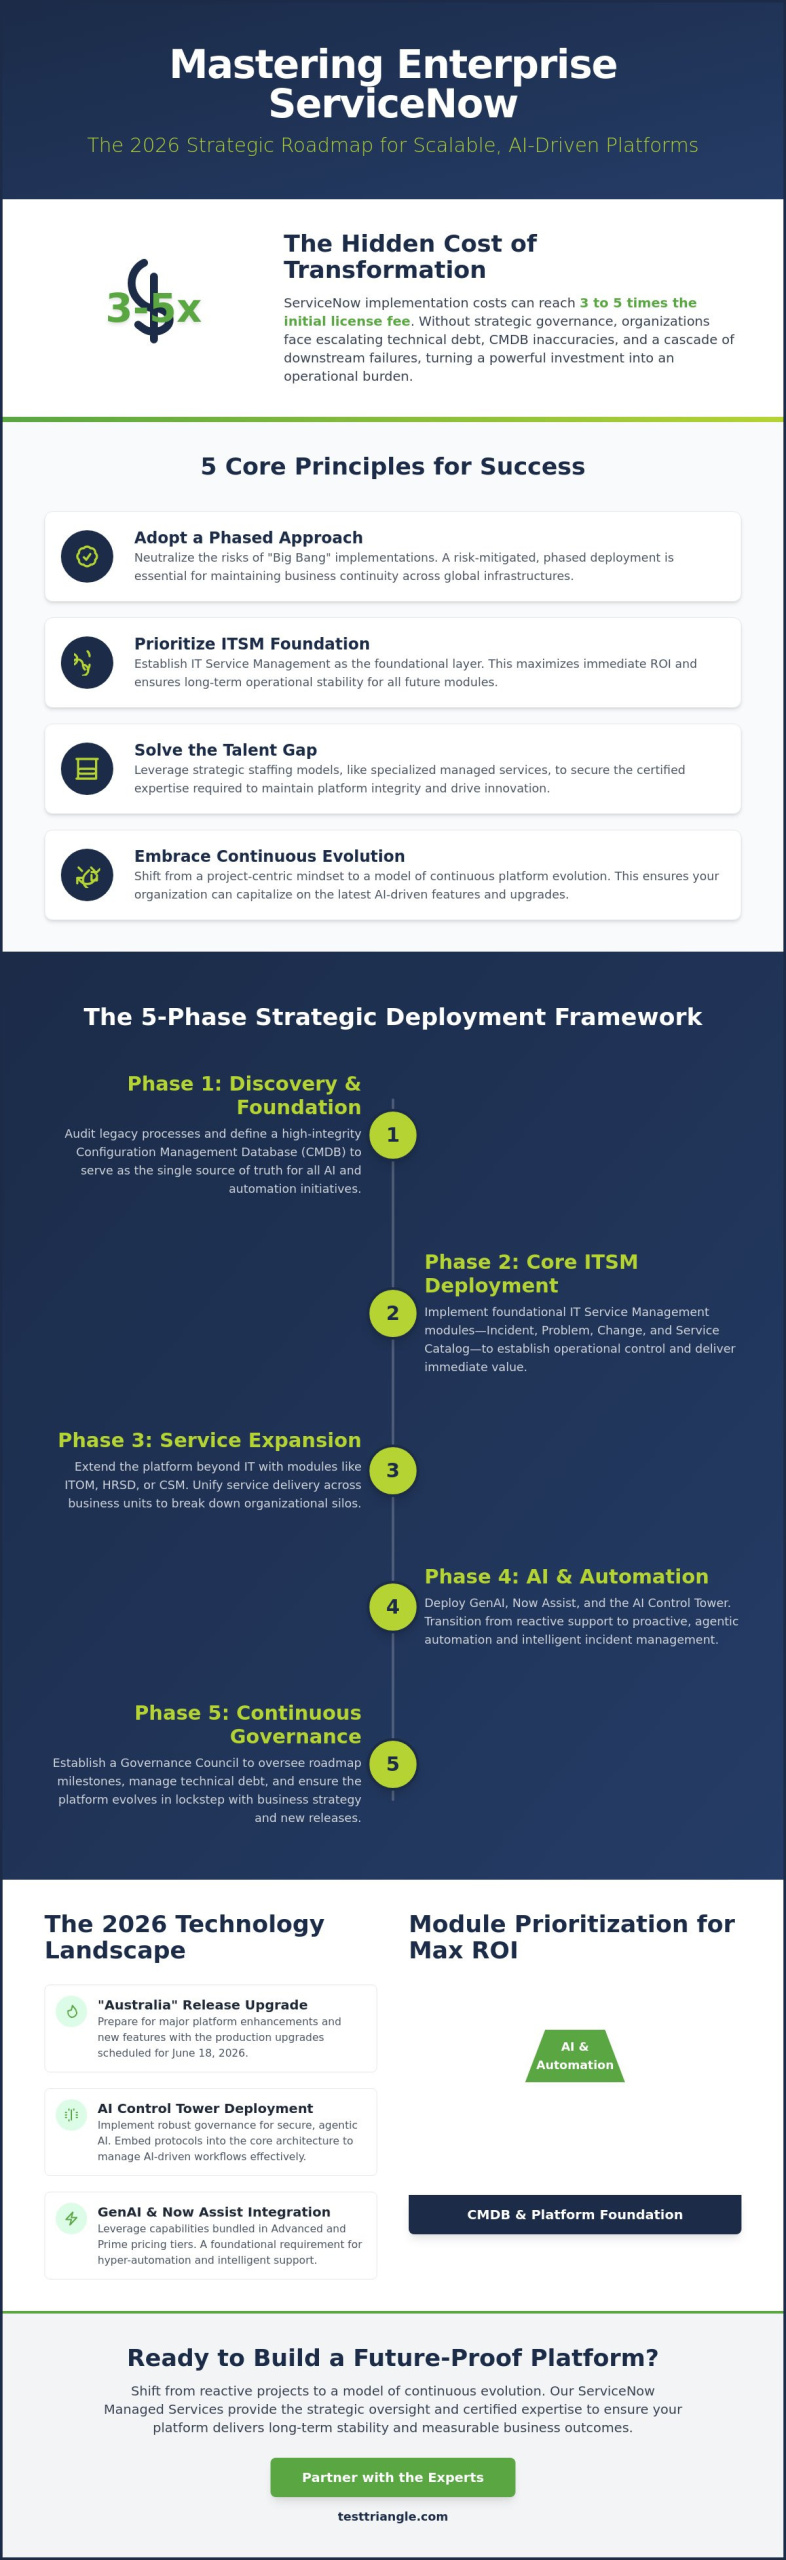

With ServiceNow implementation costs typically reaching three to five times the initial license fee, the strategic challenge for global organizations isn’t just the initial purchase; it’s the persistent governance of a rapidly evolving digital ecosystem. You’ve likely seen how unmanaged technical debt and CMDB inaccuracies can turn a transformative vision into a series of downstream failures. To solve this, sophisticated servicenow managed services for enterprises provide the technical rigor, strategic oversight, and specialized talent required to maintain platform integrity. We focus on delivering precision, performance, and progress through a methodology that connects architectural health to measurable business outcomes.

This guide offers a comprehensive 2026 roadmap designed to help you master the complexities of enterprise-scale deployments with a structured, risk-mitigated approach. You’ll learn how to align IT workflows with your broader corporate objectives while ensuring your platform remains scalable as you grow. We’ll preview the critical phases of the “Australia” release upgrade, the integration of the new Prime pricing tier capabilities, and the deployment of the AI Control Tower for secure, agentic automation. By the end of this article, you’ll have a clear path to achieve long-term operational stability and a platform that evolves alongside your enterprise.

Key Takeaways

  • Learn why a phased, risk-mitigated approach to deployment is essential for maintaining business continuity across global infrastructures, effectively neutralizing the risks associated with high-stakes “Big Bang” implementations.
  • Leverage specialized servicenow managed services for enterprises to navigate the 2026 strategic roadmap, ensuring that technical configurations remain precisely aligned with high-level corporate objectives and systemic growth.
  • Identify the optimal order of operations for module integration, prioritizing IT Service Management as the foundational layer to maximize immediate return on investment and long-term operational stability.
  • Solve the persistent talent gap by evaluating strategic staffing models that secure the certified expertise required to maintain platform integrity amidst a rapidly changing technological landscape.
  • Shift from a project-centric mindset to a model of continuous platform evolution, ensuring your organization is positioned to capitalize on the latest AI-driven features and version upgrades.

The Architecture of Success: Defining the ServiceNow Implementation Roadmap

The architecture of success in modern digital infrastructure isn’t built on static project plans; it’s forged through a living strategic document that synchronizes complex IT workflows with overarching corporate goals. For global organizations, the “Big Bang” deployment model often results in catastrophic operational friction, making a phased transition the superior choice for maintaining business continuity while scaling technical capabilities. Establishing a robust, multi-year roadmap serves as a definitive risk-mitigation tool for large-scale digital transformation. In 2026, the “Assess, Align, Accelerate” framework has become the industry benchmark, particularly as firms prepare for the “Australia” release production upgrades scheduled for June 18. By utilizing servicenow managed services for enterprises, leadership teams can ensure this framework isn’t just theoretical but translates into tangible platform stability, precision, and progress.

Strategic Alignment and Executive Buy-in

Successful platform adoption requires a shift from purely technical metrics to specific corporate KPIs. By mapping platform capabilities directly to business outcomes, such as reducing mean time to resolution or improving employee retention through seamless service delivery, IT leaders can secure sustained funding. We recommend establishing a Governance Council to oversee roadmap milestones, ensuring that every configuration choice supports the enterprise’s long-term vision. Identifying “Quick Wins” during the initial ninety days is essential to demonstrate immediate value to stakeholders, effectively justifying the implementation costs which typically range from three to five times the first-year license fee.

The 2026 Landscape: AI and Hyper-automation

Since its inception, ServiceNow has evolved from a ticketing tool into a comprehensive workflow engine that now prioritizes agentic AI. The 2026 roadmap must integrate GenAI and Now Assist into early phases, especially as these capabilities are now bundled within the Advanced and Prime pricing tiers. Preparing data structures for AI-driven incident management is no longer optional; it’s a foundational requirement for hyper-automation. Strategic servicenow managed services for enterprises focus on future-proofing the platform against evolving regulatory requirements, such as the June 2026 Chemical Regulatory framework, by ensuring that data governance and AI Control Tower protocols are embedded into the core architecture from day one. This proactive approach leads to a scalable, secure, and sophisticated digital environment that empowers the global workforce.

The 5-Phase Strategic Framework for Enterprise Deployment

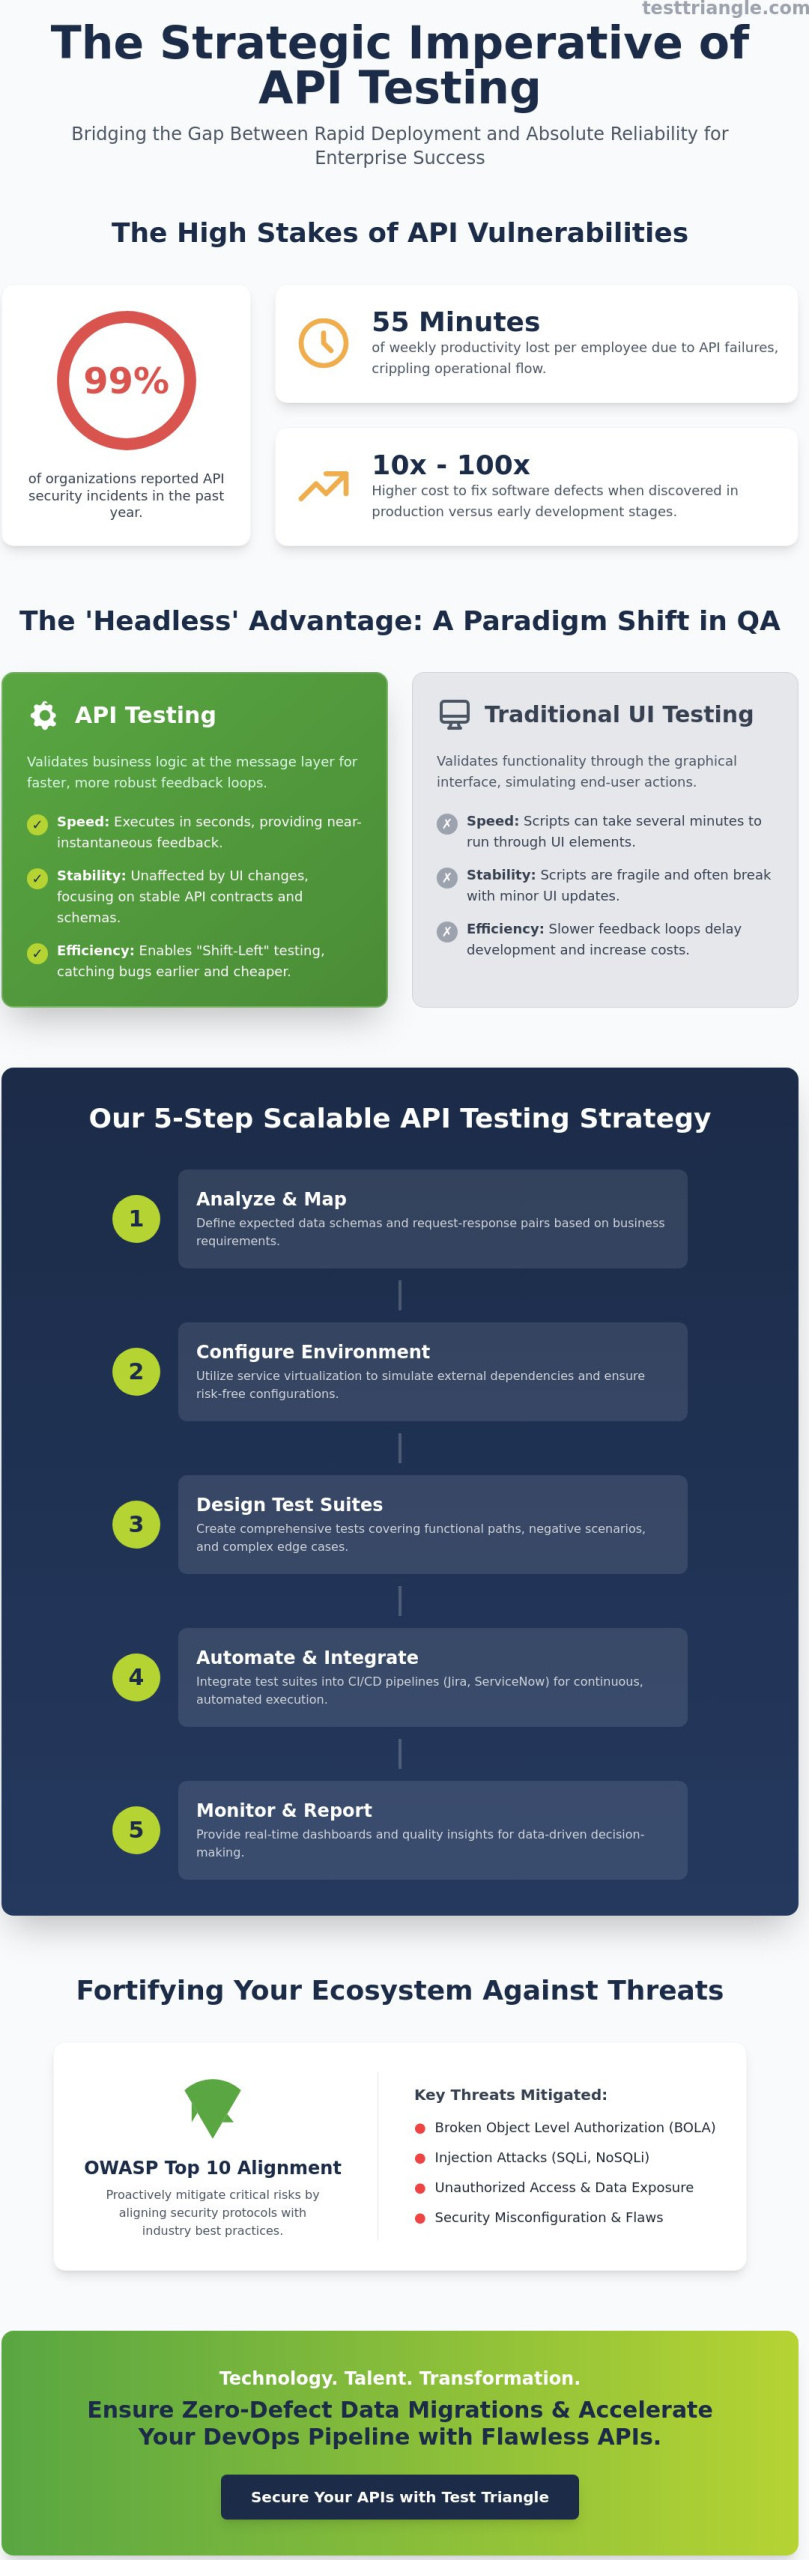
Executing a global deployment requires more than just technical configuration; it demands a methodical progression that balances speed with architectural integrity. By adopting a five-phase framework, organizations can transform their digital infrastructure from a collection of siloed tools into a unified engine for growth. High-tier servicenow managed services for enterprises provide the necessary guardrails during this transition, ensuring that each phase builds upon a stable foundation rather than compounding technical debt. This disciplined approach allows leadership to maintain visibility while the platform scales across diverse business units.

Phase 1 focuses on Discovery and Foundation, where teams audit legacy processes to define the core Configuration Management Database (CMDB). This stage is critical because ServiceNow’s AI-driven strategy relies heavily on high-quality data to fuel automation and agentic AI. Phase 2 moves into Core ITSM Deployment, establishing incident, problem, and change management workflows that standardize service delivery. Once these essentials are in place, Phase 3 introduces IT Operations Management (ITOM) for full-stack observability. Phase 4 extends the platform’s reach into HR Service Delivery (HRSD) or Strategic Portfolio Management (SPM), aligning technical output with business value. Finally, Phase 5 centers on Continuous Optimization, where the platform is refined to meet shifting enterprise needs.

Phase 1: The Criticality of a Clean CMDB

The CMDB acts as the single source of truth for the entire roadmap. If the data within this database is fragmented or outdated, every downstream process, from automated ticket routing to AI-driven insights, will fail. Enterprises must decide between automated discovery tools and manual data entry, though automation is almost always preferred for maintaining accuracy at scale. Avoiding the “garbage in, garbage out” trap requires a disciplined approach to data governance that starts on day one. It’s the difference between a platform that provides clarity and one that creates confusion.

Scaling Through Managed Services

As the deployment matures, the focus shifts from initial setup to long-term operational health. Transitioning to professional Managed Service Provider (MSP) support through servicenow managed services for enterprises allows internal IT teams to focus on innovation while experts handle the complexities of platform maintenance. This model ensures stability through recurring optimization audits and dedicated helpdesk support that scales with your needs. To ensure your platform remains a high-performance asset, it’s vital to discuss your specific operational requirements with a strategic partner. This partnership provides the institutional maturity needed to manage the “Australia” release and future platform evolutions with precision.

Order of Operations: Prioritising Modules for Maximum ROI

Determining the precise sequence of module activation is a high-stakes decision that dictates the speed of realized value across the organization. While the platform’s versatility is vast, establishing IT Service Management (ITSM) as the foundational layer remains the strategic standard for 90% of enterprises. This preference isn’t merely traditional; it’s a structural necessity because ITSM provides the essential data taxonomies and service schemas required to support more advanced automation. By utilizing servicenow managed services for enterprises, leadership teams can navigate these priorities with a steady hand, ensuring that each new capability rests on a stable, high-performance base that supports systemic growth.

When comparing early ITOM (IT Operations Management) versus HRSD (HR Service Delivery) integration, the choice typically hinges on the organization’s most pressing operational friction. If the enterprise suffers from frequent service outages or lacks visibility into complex cloud infrastructures, ITOM offers the immediate benefit of full-stack observability. Conversely, if the primary goal is to centralize and automate employee requests across global offices, HRSD provides a more visible impact on internal productivity. A common objection arises regarding whether industry-specific modules should be implemented first to address niche requirements. While these modules offer deep functionality, deploying them before the core ITSM engine often creates architectural silos that are difficult to reconcile during later stages of the roadmap.

For organizations focused on technical agility, integrating ServiceNow with Atlassian ecosystems is a critical milestone for achieving DevOps synergy. This connection creates a seamless bridge between the service desk and the development pipeline, allowing for automated ticket synchronization and improved visibility. By aligning these industry-leading platforms, enterprises can achieve a level of speed, security, and scalability that traditional siloed approaches cannot match.

The ITSM-First Approach

Standardizing service desks through an ITSM-first strategy is the most effective way to reduce operational friction and create a unified user experience. By mapping incident management directly to business impact levels, IT teams can prioritize resources based on actual financial or operational risk. The minimum viable platform for a successful enterprise launch consists of a governed CMDB core, a functional incident management workflow, and a standardized service portal. This foundational setup allows the enterprise to capture clean data from day one, which is essential for fueling the AI-driven insights promised in the 2026 roadmap.

Expanding to ITOM and Beyond

Once the foundation is secure, leveraging AIOps within the ITOM module allows organizations to transition from reactive firefighting to proactive maintenance. This evolution is particularly powerful when integrating ServiceNow with AWS cloud environments, where automated discovery and event management can significantly reduce mean time to resolution. Linking your ServiceNow Implementation to broader DevOps Consulting goals ensures that your platform doesn’t just manage services but actively accelerates digital transformation. This strategic expansion transforms the platform into a versatile engine for enterprise-wide innovation and long-term stability.

ServiceNow Managed Services for Enterprises: The 2026 Strategic Roadmap

Overcoming the Talent Gap: Staffing Your Roadmap

The primary bottleneck for global organizations executing a 2026 roadmap isn’t the platform’s architecture; it’s the acute shortage of certified ServiceNow architects and developers. This talent gap often halts progress between the discovery and deployment phases, as enterprises struggle to secure specialists who understand the nuances of the “Australia” release and its bundled AI capabilities. The “Build vs. Buy” dilemma is a constant pressure for IT leadership. While training internal staff is a valuable long-term objective, the immediate requirements of a high-stakes rollout often demand the technical rigor and institutional maturity that only servicenow managed services for enterprises can provide. Specialized recruiters play a vital role here, sourcing hard-to-find talent that bridges the gap between technical execution and business strategy.

To maintain momentum without inflating permanent headcount, many organizations utilize IT Staffing Services to fill tactical gaps during the most labor-intensive milestones. This approach allows for a versatile staffing model that adjusts to the project’s pulse, ensuring that your roadmap doesn’t stall due to a lack of specialized human capital. If your organization is facing a critical expertise shortage, it is time to consult with our staffing experts to secure the certified talent necessary for a seamless deployment.

Hybrid Staffing Models for Global Rollouts

Balancing permanent on-site leadership with remote offshore resources is a proven strategy for maintaining 24/7 development cycles. Using contract specialists for high-intensity Phase 2 and 3 milestones allows enterprises to scale their technical capacity rapidly without the long-term burden of high overhead. This model frequently utilizes margin-based billing for temporary tech staff, providing a cost-effective way to access elite skills during critical transition periods. It’s a disciplined approach that prioritizes operational speed while maintaining strict budget control.

Quality Assurance and Testing Roles

Manual and Automation Testing are non-negotiable requirements for any enterprise roadmap. Integrating QA engineers early in the deployment process prevents the accumulation of technical debt that can cripple a platform’s performance over time. System Integration Testing (SIT) is particularly crucial in multi-platform environments where ServiceNow must communicate flawlessly with AWS, Atlassian, or legacy ERP systems. Following a structured testing guide ensures that every configuration is validated against rigorous security and performance standards before reaching production, safeguarding the integrity of your digital ecosystem.

The Final Milestone: Partnership and Long-Term Evolution

The final milestone in a successful enterprise deployment is the fundamental shift from a project-centric view to a platform-centric philosophy. While the initial go-live represents a significant achievement, the true value of servicenow managed services for enterprises is realized through continuous, incremental evolution. This “platform mindset” ensures that your digital infrastructure remains responsive to shifting market conditions rather than becoming a legacy burden. Precision drives progress. To maintain this momentum, regular version upgrades are essential. With the “Australia” release production upgrades scheduled for June 18, 2026, organizations must stay current to access critical innovations like the AI Control Tower or the bundled Now Assist capabilities now included in the Prime pricing tier. Neglecting these updates doesn’t just stall innovation; it increases security risks and technical debt.

As a seasoned expert in the field, Test Triangle acts as a steady hand in this fast-changing landscape, positioning itself as the strategic collaborator for your IT Service Management solutions. We focus on the peace of mind derived from risk reduction and the empowerment found in large-scale technological evolution. Stability requires constant motion. Transitioning to a managed model allows your internal leadership to focus on high-level strategy while we manage the technical rigor of platform health, ensuring your investment continues to deliver measurable ROI long after the initial implementation.

Measuring Roadmap Maturity

Determining the success of your deployment requires tracking key performance indicators (KPIs) that reflect real business impact. We recommend focusing on metrics such as the reduction in mean time to resolution (MTTR), the accuracy of CMDB data, and overall user adoption rates across different modules. Annual “Health Checks” are a non-negotiable part of this process. These audits identify system bloat and misconfigurations before they cause downstream failures. By leveraging the strategic trinity of Atlassian, ServiceNow, and AWS, organizations can achieve a level of enterprise-wide agility that ensures every workflow is optimized for speed and security.

Ready to Accelerate Your Transformation?

Our “Assess, Align, Accelerate” value proposition is designed to lead your organization from a general need for improvement to a specific, high-performance technical solution. This methodical approach ensures that your ServiceNow environment remains a scalable asset that grows alongside your enterprise. We invite you to explore Test Triangle’s comprehensive IT services to see how our versatile staffing and implementation models can support your long-term goals. Reviewing your strategic roadmap with a consultant today is the best way to ensure your digital infrastructure is prepared for the complexities of the 2026 landscape. Your roadmap is the bridge between technology and business outcome.

Mastering the Evolution of Enterprise Workflows

Achieving operational excellence at scale requires a transition from reactive maintenance to a disciplined, phased strategy that prioritizes architectural health and specialized expertise. By following a structured roadmap, organizations can ensure their digital infrastructure remains resilient while capitalizing on agentic AI and automated governance. Utilizing servicenow managed services for enterprises provides the institutional maturity needed to navigate complex version upgrades and talent shortages with confidence. We focus on delivering precision, performance, and progress through a methodology that transforms technical debt into a scalable engine for growth.

As a ServiceNow Authorized Partner with a global presence across Europe, North America, and Asia, Test Triangle is uniquely positioned to support high-compliance sectors like Finance and Pharma. We act as a reliable long-term collaborator, ensuring your platform aligns with both technical benchmarks and overarching business goals. It’s time to secure your digital future and eliminate the friction of unmanaged systems. Book a Strategic ServiceNow Roadmap Consultation with Test Triangle to refine your deployment strategy. Your journey toward a more efficient and empowered enterprise begins with a single, strategic step.

Frequently Asked Questions

What is the typical timeline for a ServiceNow enterprise implementation?

A standard enterprise-scale deployment typically spans six to twelve months, though the exact duration depends on the complexity of legacy integrations and the scope of the initial modules. While smaller organizations might achieve a go-live in a shorter window, global firms require a more methodical pace to ensure data integrity and user adoption across multiple business units. This timeline includes the critical discovery phase and the subsequent iterative testing cycles necessary for a risk-mitigated launch.

Should we start with ITSM or ITOM in our roadmap?

Enterprises should almost always prioritize IT Service Management (ITSM) as the foundational layer of their roadmap. Because ITSM establishes the core service taxonomies and incident workflows, it provides the essential data structure required for IT Operations Management (ITOM) to function effectively. Starting with ITSM allows teams to standardize the user experience before introducing the advanced observability and AIOps capabilities offered by ITOM.

How much does a ServiceNow implementation usually cost for a global firm?

Total investment for a global firm is determined by a combination of licensing tiers, implementation complexity, and ongoing support requirements. Since ServiceNow operates on a custom-quote basis, organizations must account for the fulfiller base size and the number of integrated business units when budgeting. Utilizing servicenow managed services for enterprises helps manage these costs by providing a predictable expenditure model for long-term maintenance and platform evolution.

What are the most common reasons for ServiceNow roadmap failure?

Roadmap failures most frequently stem from poor governance, inadequate data quality in the CMDB, and a lack of specialized technical talent. When organizations treat the platform as a one-time project rather than a living ecosystem, they often accumulate technical debt that hinders future upgrades. Success requires a disciplined approach that aligns technical configuration with high-level business objectives while maintaining a steady hand through continuous platform evolution.

How do we handle data migration from legacy systems to ServiceNow?

Handling data migration requires a rigorous “clean as you go” strategy to avoid transferring legacy inaccuracies into the new environment. Teams should utilize automated discovery tools to validate existing assets while manually auditing critical service relationships to ensure the CMDB remains a single source of truth. This process often involves a phased migration where data is mapped, transformed, and validated in a staging environment before the final production cutover.

What is the role of a ServiceNow Implementation Specialist versus a Generalist?

A ServiceNow Implementation Specialist possesses deep, certified expertise in specific modules like HRSD or ITOM, ensuring that complex configurations follow industry best practices. In contrast, a Generalist provides broader oversight of the platform’s daily operations and basic maintenance tasks. For global organizations, the strategic visionary role of a Specialist is essential during the high-intensity deployment phases to prevent architectural silos and ensure long-term scalability.

Can ServiceNow be integrated with Atlassian Jira for DevOps?

Integrating ServiceNow with Atlassian Jira is a standard practice for organizations seeking to achieve seamless ticket synchronization between service desks and development teams. This connection allows developers to remain within their preferred environment while IT managers maintain visibility and governance within the ServiceNow platform. By aligning these industry-leading tools, enterprises can accelerate delivery cycles while maintaining strict compliance and security standards.

How often should we update our ServiceNow roadmap?

Roadmaps should be reviewed and updated at least quarterly to account for platform release cycles and shifting business priorities. This methodical rhythm allows leadership to adjust the order of operations based on realized ROI and emerging operational needs. Regular updates ensure that your organization is prepared to leverage the latest innovations and bundled AI capabilities, keeping the platform aligned with your broader digital transformation goals.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.

A media company serving 50TB of content monthly currently pays approximately $4,500 every month in AWS egress fees alone, illustrating how data gravity often evolves into a significant barrier to organizational agility. While the European Data Act has successfully pressured providers to waive certain exit fees for migrating customers, the true challenge of avoiding vendor lock-in with aws remains embedded in a complex web of proprietary APIs and specialized networking charges. You likely recognize the persistent tension between leveraging high level cloud innovation and the strategic necessity of maintaining long term digital sovereignty. It’s a delicate balance where the immediate speed of deployment must never compromise your future ability to pivot, migrate, or negotiate from a position of strength.

This guide provides a comprehensive roadmap for achieving enterprise autonomy through strategic agnosticism and robust architectural abstractions. You’ll master the frameworks required to evaluate service risks, optimize cross region data transfers, and implement automated testing that validates your portability at every stage. By aligning your technical execution with business outcomes, we’ll explore how to build a cloud smart infrastructure that delivers precision, portability, and progress. Our objective is to ensure your organization remains a steady hand in a fast changing landscape, empowered by a clear strategy for long term operational stability and the peace of mind that comes from true technological independence.

Key Takeaways

  • Assess the multidimensional risks of cloud dependency by identifying the technical, financial, operational, and mental pillars that define your organization’s current migration readiness.
  • Master the architectural abstractions required for avoiding vendor lock-in with aws, utilizing containerized runtimes and the adapter pattern to effectively decouple core application logic from proprietary service dependencies.
  • Transition from theoretical exit plans to validated operational reality by implementing contract testing suites that ensure consistent microservice behavior across heterogeneous cloud environments.
  • Strengthen your strategic leverage through a Cloud Center of Excellence that integrates Atlassian-driven governance into standard ITSM cycles for continuous, collaborative, and compliant portability oversight.
  • Apply the Test Triangle framework to synthesize DevOps discipline with digital assurance, ensuring your enterprise infrastructure remains versatile, scalable, and inherently exit-ready.

Understanding the Dimensions of AWS Vendor Lock-in in 2026

The 2026 cloud environment demands a sophisticated grasp of Understanding Vendor Lock-in, which manifests across four distinct pillars: technical, financial, operational, and mental. Technical lock-in occurs through the adoption of proprietary service architectures, while financial lock-in is reinforced by complex discount structures. Operational lock-in stems from rigid internal processes tailored to a specific provider. Mental lock-in represents the most subtle barrier, reflecting an organizational bias that treats one provider’s ecosystem as the only viable path for innovation. Successfully avoiding vendor lock-in with aws requires addressing these dimensions simultaneously to maintain true strategic autonomy and operational stability.

Data gravity has emerged as the most significant migration hurdle in 2026. As enterprises accumulate petabytes of information, the sheer mass of data creates a pulling force that makes moving workloads prohibitively expensive. Egress fees remain a primary weapon for restricting movement; for instance, a SaaS API handling 10TB of monthly response payloads can face roughly $900 in egress costs. This creates a friction-filled environment where the cost of data extraction often outweighs the benefits of platform diversification. Organizations must weigh the “Innovation Premium” of using native, high-level services against the “Portability Tax” incurred when building cloud-agnostic layers that require additional management overhead.

Technical vs. Economic Lock-in

Proprietary APIs create a sticky architecture by embedding cloud-specific logic directly into your application code, necessitating expensive and time-consuming rewrites during any migration attempt. This technical debt is often compounded by economic commitments such as Reserved Instances and Savings Plans, which provide immediate cost relief but significantly reduce your future bargaining power. By locking into multi-year contracts for compute capacity, enterprises often find themselves unable to capitalize on emerging price wars or superior performance tiers from competitors. Economic lock-in occurs when the cumulative costs of migration exceed the projected long-term savings of moving to a new provider.

The Skills Gap: Operational Dependency

Operational dependency often hides within your engineering team’s expertise. When a DevOps team is exclusively certified in AWS technologies, they become a form of silent lock-in that limits your organization’s ability to explore alternative platforms or hybrid strategies. Cultivating a cross-cloud mindset through diverse training programs is essential for maintaining agility and avoiding vendor lock-in with aws at the human capital level. Many enterprises are now leveraging specialized IT Staffing Services to bridge these talent gaps, ensuring they have access to the versatile expertise required to manage platform transitions without disrupting their core business functions or long-term growth objectives.

Architectural Strategies for Cloud-Agnostic Resilience

Architectural autonomy is not a binary state but a spectrum that requires a disciplined approach to service selection and abstraction. By adopting containerization via EKS or Kubernetes as the universal runtime layer, organizations can establish a consistent execution environment that remains portable across disparate cloud providers. This methodology allows teams to leverage AWS innovation for immediate speed while ensuring that the underlying application logic isn’t inextricably tied to proprietary compute features. Implementing the “Adapter Pattern” further decouples your core business logic from cloud-native services by creating a standardized interface for external dependencies. When using Infrastructure as Code (IaC), prioritizing tools like Terraform ensures that your environment definitions remain provider-agnostic, allowing for the rapid recreation of infrastructure in alternate ecosystems if strategic priorities shift. Balancing the strategic implications of cloud adoption involves identifying which services provide a competitive advantage and which simply contribute to unnecessary dependency.

Abstraction Layers and Middleware

Service meshes like Istio or Linkerd provide a critical layer of abstraction by moving networking and security concerns away from AWS-specific tools into a platform-independent control plane. This approach is further strengthened by utilizing runtimes like Dapr to decouple code from stateful services such as SQS or DynamoDB, which effectively neutralizes the risk of deep API integration. Engaging in DevOps Consulting allows enterprises to design these exit-ready architectures with precision, ensuring that every component is evaluated for its impact on long-term flexibility. This strategic foresight transforms cloud infrastructure from a potential trap into a versatile engine for growth, providing the stability, scalability, and sovereignty required for modern digital operations.

Database Portability and Data Gravity

Data gravity remains a formidable obstacle when avoiding vendor lock-in with aws, particularly when relying on proprietary engines like Aurora or DynamoDB. While managed NoSQL offers high performance, it creates a rigid data layer that’s difficult to port without significant refactoring. Strategies for data decoupling, such as Change Data Capture (CDC), enable real-time portability by streaming data changes to external repositories, thereby reducing the friction of a potential exit. Planning for “The Big Move” also necessitates a clear understanding of egress timelines. Moving 50TB of data can take considerable time depending on throughput and costs around $4,500 in fees. If you require assistance in mapping your cloud-agnostic roadmap, our specialists can help you evaluate your current architecture to ensure it remains robust and portable.

Automated Testing: The Secret Weapon for Cloud Portability

A sophisticated architecture provides the skeleton of autonomy, but it is through rigorous validation that an enterprise breathes life into its cloud-agnostic vision. While many organizations focus on the initial deployment, avoiding vendor lock-in with aws requires a shift in perspective toward continuous testability. An exit strategy remains a theoretical paper exercise until it’s subjected to a validated test suite that proves an application’s resilience across heterogeneous environments. By implementing contract testing, DevOps teams can ensure that microservices maintain identical behavioral patterns regardless of the underlying cloud provider, thereby neutralizing the subtle risks of proprietary API dependencies. This methodical approach to validation allows leadership to view cloud exit strategies not as a defensive fallback, but as a proactive measure of operational health and strategic flexibility.

Benchmarking serves as a critical component of this validation process, utilizing performance testing to compare AWS metrics against potential alternative providers to ensure that migration does not compromise service levels. Establishing a dedicated Portability Test Bed allows for the simulation of real-world workloads in secondary environments, providing the empirical data necessary to confirm that an application is truly exit-ready. This environment acts as a crucible where architectural choices are tested against the realities of network latency, storage performance, and resource orchestration, ensuring that the enterprise maintains a steady hand in a fast changing technological landscape.

Continuous Portability Validation

Integrating cross-cloud smoke tests into your Software Test Automation Services ensures that portability remains a constant priority rather than an after-thought. While automation provides the speed required for large-scale operations, Manual Testing is essential for uncovering nuanced UI/UX discrepancies that arise from regional latency or platform-specific rendering differences. Automated validation provides the only objective measure of cloud independence, offering the peace of mind that comes from verified, repeatable results.

Digital Assurance and Risk Mitigation

Leveraging Software and Digital Assurance Testing enables a comprehensive audit of vendor-specific dependencies that architectural diagrams might overlook. By simulating catastrophic cloud outages, organizations can test the efficacy of multi-cloud failover strategies and measure the speed of their “Exit Trigger” to see how quickly critical workloads can be moved under pressure. This disciplined approach to risk reduction empowers enterprises to pursue large-scale technological evolution with confidence, knowing their digital sovereignty is protected by a framework of precision, portability, and progress.

Avoiding Vendor Lock-in with AWS: A Strategic Guide for Enterprise Autonomy in 2026

Governance and Managed Services: Maintaining Strategic Leverage

Establishing a robust governance framework is the cornerstone of long-term digital sovereignty, ensuring that architectural choices remain aligned with business objectives. A Cloud Center of Excellence (CCoE) serves as the institutional guardian of this mission, moving beyond mere technical oversight to actively monitor vendor dependency levels across the entire enterprise. By integrating cloud portability audits into the standard ITSM review cycle, leadership can transform avoiding vendor lock-in with aws from a reactive concern into a proactive governance discipline. This strategic oversight includes negotiating AWS contracts with explicit exit clauses and return guarantees for data, specifically leveraging the policy updates from March 2024 where AWS began waiving data transfer fees for customers departing the platform. While these regulatory shifts provide a foundation, true leverage is maintained through the constant evaluation of service alternatives and the enforcement of agnostic standards.

The methodical application of governance ensures that every cloud investment is scrutinized for its impact on future flexibility. This involves a shift from a “cloud-first” to a “cloud-smart” strategy, where the focus remains on organizational progress through the combination of human expertise and technical tools. By maintaining a steady hand in a fast-changing landscape, enterprises can achieve a state of institutional maturity that values stability, precision, and scalable growth above the convenience of proprietary features.

ITSM and Vendor Management

Aligning your cloud strategy with comprehensive IT Service Management Solutions provides the visibility required to manage complex, multi-provider ecosystems with precision. Through ServiceNow Consulting Services, organizations can implement automated discovery tools that track cloud assets and their portability status in real-time. This level of transparency is vital for identifying “Shadow IT” instances where individual departments may have adopted proprietary AWS services without considering the long-term migration risks. By centralizing asset management, enterprises ensure that every technological investment contributes to a versatile and exit-ready infrastructure.

Managed Outsourcing as a Portability Bridge

Managed services act as a strategic buffer, neutralizing the operational debt that often accumulates when internal teams become overly specialized in a single provider’s toolset. By utilizing Managed Outsourcing Services, enterprises can maintain a balanced talent portfolio that bridges the gap between AWS-specific execution and broader industry standards. This approach ensures that your organization retains the “Exit-as-a-Service” capability, where external partners provide the diverse skills necessary to facilitate a platform transition if market conditions change. Embracing this model is a critical component of avoiding vendor lock-in with aws, as it ensures your human capital remains as portable as your code. If you are ready to fortify your governance framework and reclaim strategic control over your digital assets, consult with our cloud governance experts today to build a roadmap for enduring autonomy.

The Test Triangle Framework: Ensuring Cloud Sovereignty

The Test Triangle Framework represents a sophisticated synthesis of technical precision and strategic foresight, specifically engineered to empower global enterprises in avoiding vendor lock-in with aws. By combining DevOps rigor with comprehensive Digital Assurance, we enable organizations to build systems that are inherently exit-ready from the moment of inception. Our structured 12-month roadmap facilitates a methodical transition from deep, proprietary AWS-native dependency to a resilient, cloud-agnostic architecture. This journey is grounded in a “Validation First” philosophy, which asserts that an infrastructure’s portability is only as real as the automated test suites that verify it. We don’t just design for autonomy; we implement the rigorous testing protocols necessary to prove that your applications can thrive in any environment.

Central to this framework is our 2026 approach to Atlassian Implementation, which serves as the collaborative engine for cross-functional cloud governance. By integrating Jira and Confluence directly into your cloud strategy, we create a transparent ecosystem where portability risks are documented, tracked, and mitigated in real-time. This level of visibility ensures that both technical managers and executive leadership maintain a clear understanding of the organization’s digital sovereignty. It’s about creating a culture of accountability where technical execution is always aligned with long-term business stability and operational agility.

Partnering for Long-Term Success

Test Triangle acts as a steady hand, providing the reliability and expertise required to navigate the complexities of large-scale technological evolution. We recently collaborated with a global financial firm to reduce their cloud dependency through automated verification protocols, demonstrating the peace of mind that stems from systemic risk reduction. This partnership approach ensures that your organization isn’t just surviving a migration, but is actively evolving into a more versatile and disciplined entity. If you’re ready to secure your autonomy and evaluate your current infrastructure, contact Test Triangle today for a comprehensive Cloud Portability Audit.

A Holistic View of Digital Transformation

Integrating cloud autonomy into your broader Digital Transformation Services is essential for maintaining a competitive edge in a fast-changing landscape. The synergy between Atlassian, ServiceNow, and AWS creates a unified operational layer that supports stability, precision, and scalable growth. By treating your cloud infrastructure as a modular asset rather than a permanent fixture, you empower your enterprise to pivot as market conditions dictate. Ultimately, vendor lock-in is a choice made through accumulated technical debt and administrative inertia, but with a reliable long-term collaborator, it’s never an inevitability. We remain deeply invested in your success, providing the tools and human expertise needed to ensure your digital future remains entirely in your own hands.

Mastering Enterprise Autonomy and Strategic Flexibility

Achieving true operational independence requires a disciplined transition from proprietary dependency to a validated, cloud-agnostic architecture. By prioritizing architectural abstraction and rigorous automated testing, your organization can successfully navigate the complexities of avoiding vendor lock-in with aws while maintaining the high pace of innovation your business demands. This strategic shift ensures that your digital infrastructure remains a versatile asset rather than a permanent constraint, allowing you to negotiate from a position of strength and pivot with precision as market conditions evolve.

Test Triangle serves as a reliable long-term collaborator for global enterprises across Europe, North America, and Asia, providing the human expertise and technical tools necessary to manage these complex transitions. With strategic partnerships spanning AWS, Atlassian, and ServiceNow, we bring institutional maturity and deep experience in highly regulated sectors like Pharma and Finance to every engagement. Secure Your Cloud Autonomy with Test Triangle’s Strategic Consulting today to begin building an exit-ready future. Your journey toward digital sovereignty is a path we are ready to walk together, ensuring your organization remains a steady hand in a fast-changing technological landscape.

Frequently Asked Questions

What is the most common cause of AWS vendor lock-in?

The primary catalyst for lock-in is the deep integration of proprietary APIs and specialized data services into an application’s core logic. When developers utilize high level services like DynamoDB or Aurora without abstraction layers, the resulting “sticky” architecture requires extensive code rewrites to migrate. This technical dependency is often compounded by financial commitments that prioritize immediate cost savings over long term architectural flexibility.

How does multi-cloud strategy help in avoiding vendor lock-in?

A multi-cloud posture facilitates autonomy by forcing teams to adopt standardized deployment patterns and provider agnostic tooling. By maintaining workloads across different ecosystems, enterprises naturally move toward avoiding vendor lock-in with aws through the use of universal runtimes like Kubernetes. This approach prevents any single provider from becoming a point of failure or a barrier to strategic negotiation during contract renewals.

Can I use AWS Lambda without getting locked in?

Yes, you can leverage serverless innovation without sacrificing portability by decoupling your business logic from the specific cloud trigger. Utilizing frameworks like the Serverless Framework or wrapping your logic in standard containers allows you to move functions between providers with minimal friction. The key is to treat the cloud specific event as a simple input that passes data to a platform independent execution layer.

What are the hidden costs of cloud migration and exit strategies?

Beyond the obvious egress fees, enterprises often overlook “hidden” networking charges such as NAT Gateway processing fees at $0.045 per GB and public IPv4 address hourly rates. There is also a significant “skills gap” cost associated with retraining a specialized workforce to manage a new platform’s unique operational nuances. These operational and financial frictions can often exceed the direct costs of data transfer during a platform transition.

How does Infrastructure as Code (IaC) improve cloud portability?

Infrastructure as Code allows for the creation of repeatable, documented environment definitions that can be redeployed across different regions or providers with high precision. Tools like Terraform enable a provider agnostic approach to resource provisioning, ensuring that your infrastructure remains a modular asset rather than a manual configuration trap. This methodology accelerates the “Exit Trigger” by allowing teams to recreate complex environments in hours rather than months.

Is it possible to achieve 100% cloud-agnostic architecture?

While theoretically possible, achieving total agnosticism often introduces a “portability tax” in the form of increased complexity and reduced access to provider specific innovations. Most successful organizations in 2026 pursue “strategic agnosticism,” focusing their portability efforts on high risk data layers while accepting managed services for non critical functions. This balanced approach ensures operational efficiency while maintaining the ability to pivot when business needs dictate.

What role does data egress play in vendor lock-in?

Data egress acts as a formidable financial barrier, with rates reaching $0.09 per GB after the initial 100GB monthly allowance. For a media company serving 50TB of content, these fees can quickly scale to $4,500 per month, creating a gravity effect that makes avoiding vendor lock-in with aws a significant budgetary challenge. Organizations must implement data decoupling strategies, such as Change Data Capture, to mitigate these costs before they become prohibitive.

How often should an enterprise test its cloud exit strategy?

Enterprises should validate their exit strategy at least annually or whenever a major architectural change is implemented. Integrating these tests into your standard ITSM review cycle ensures that portability remains a live capability rather than a theoretical document. Regular validation through automated smoke tests and performance benchmarking provides the empirical data required to maintain a steady hand in a fast changing technological landscape.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.
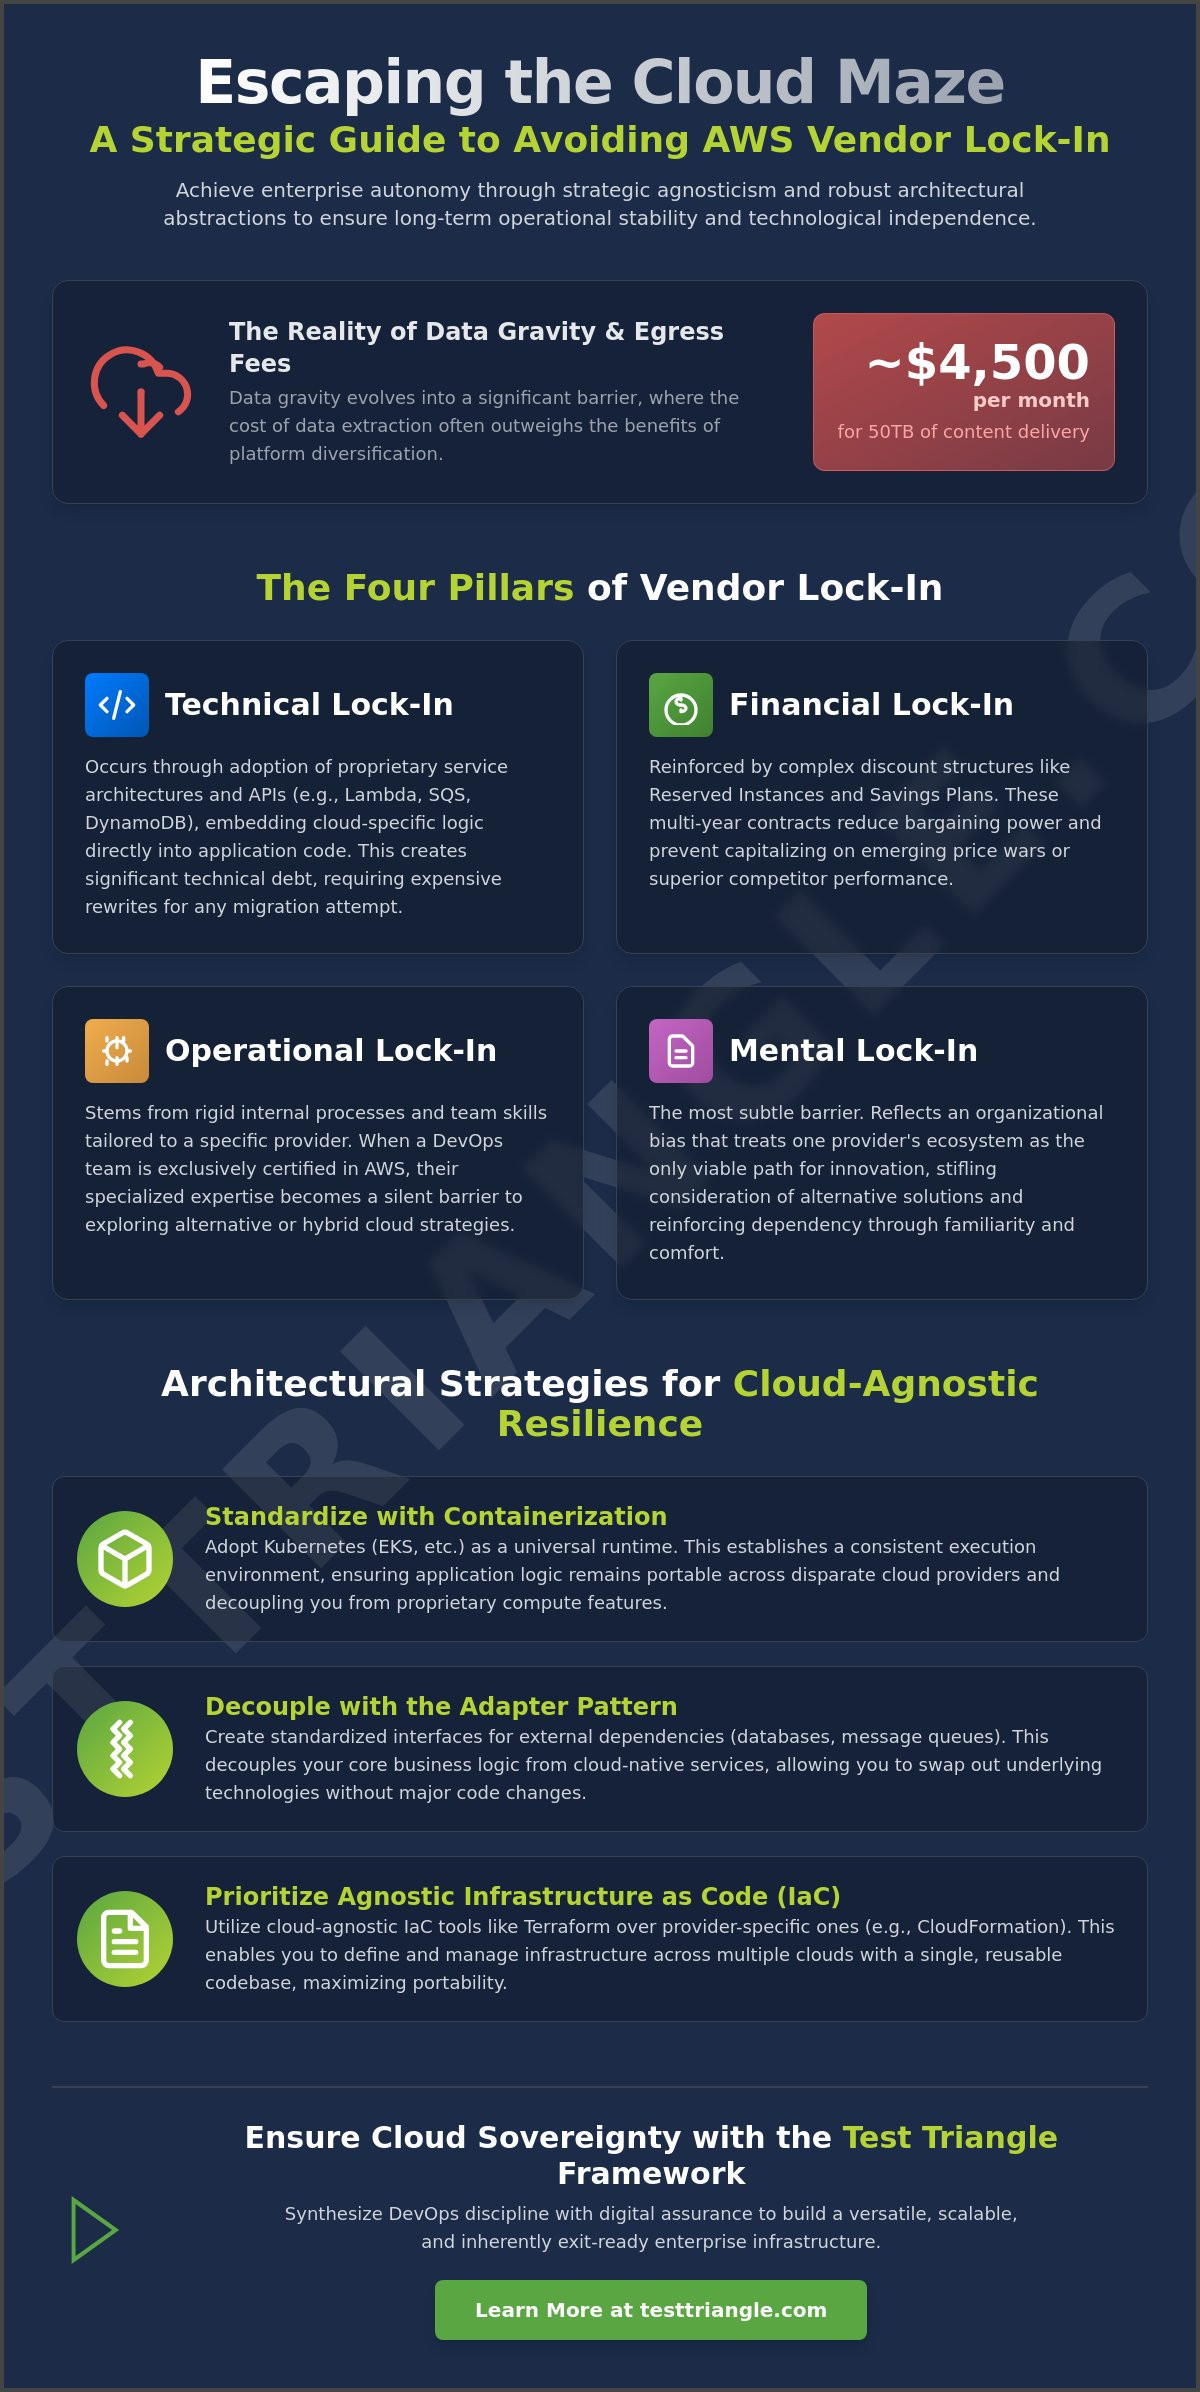

With cloud-specific roles currently expanding four times faster than traditional IT positions, global enterprises face a critical shortage of the specialized expertise required to maintain stability during massive infrastructure shifts. You’ve likely seen how the financial burden of maintaining parallel environments can swiftly drain your migration ROI, leaving leadership questioning the initial business case. Successfully de-risking a large scale aws cloud migration demands more than just basic tooling; it requires a disciplined integration of Cloud Financial Management, automated validation, and strategic talent alignment. By shifting from a simple lift-and-shift mindset toward a modernized, AI-enhanced framework, your organization can transform a volatile transition into a foundation for sustainable, scalable growth.

This article outlines a comprehensive methodology for mitigating the technical, financial, and operational hazards inherent in enterprise-level AWS transitions. We’ll examine how to utilize the latest 2026 updates, such as Kubernetes 1.36 support and enhanced DataSync protocols, to ensure your cutover is seamless and secure. You’ll discover a structured approach to validate data integrity, reduce operational downtime, and eliminate the fear of security breaches. Our goal is to provide the precision, predictability, and partnership necessary to help your team master the cloud landscape with absolute confidence and institutional maturity.

Key Takeaways

  • Integrate Cloud Financial Management (CFM) principles early in the assessment phase to maximize ROI and leverage the AWS Migration Acceleration Program to offset initial infrastructure investments.
  • Establish automated validation and feature management as your primary defense against data loss, allowing for gradual traffic migration and immediate rollback capabilities during complex cutovers.
  • Implement a robust, multi-layered framework for de-risking a large scale aws cloud migration that prioritizes application modernization over the inherent limitations of traditional lift-and-shift strategies.
  • Address the critical AWS talent shortage by aligning internal training with specialized IT staffing services to ensure your migration remains on schedule and within budget.
  • Leverage global DevOps consulting and ServiceNow expertise to synchronize your technical execution with broader business outcomes for a secure, high-performance digital evolution.

Large-scale migration risk in 2026 has evolved from simple data transfer challenges into a multi-dimensional puzzle of architectural compatibility and operational readiness. As global enterprises attempt to modernize, they often find that foundational cloud computing concepts must be re-evaluated to accommodate AI-driven discovery and automated landing zones. Successfully de-risking a large scale aws cloud migration requires a departure from the legacy ‘lift and shift’ mentality, which frequently results in ‘lift and stall’ scenarios where unvalidated technical debt is simply moved to a more expensive environment. Without a rigorous strategy that prioritizes modernization over mere relocation, organizations risk inheriting unmanaged legacy architectures that fail to deliver the promised 20-40% reduction in infrastructure costs.

Our methodology centers on a disciplined triad: Assess, Align, and Accelerate. This framework ensures that technical managers and executive leadership are unified in their objectives before the first workload is moved. By establishing a baseline for risk early in the process, we help organizations identify which of the ‘6Rs’ (Rehost, Replatform, Refactor, Repurchase, Retire, Retain) best serves their long-term stability and growth. It’s a process that demands institutional maturity and a steady hand to manage the fast-changing technological landscape.

Identifying Common Failure Points in Enterprise Migrations

Inadequate readiness assessments across the six dimensions of the AWS Cloud Adoption Framework (CAF) remain a primary cause of project failure. When organizations overlook the governance or people perspectives, they create friction that slows technical execution. The impact of fragmented data silos on migration predictability is equally severe. When disparate data sets are moved without a unified governance model, they create security vulnerabilities that often emerge during the critical transition phase. This lack of visibility leads to unvalidated legacy architectures that compromise the target environment and introduce unnecessary risk.

The Cost of Stalled Migrations and ROI Erosion

Maintaining parallel environments is one of the most significant drains on a migration business case. For every month a migration stalls, the enterprise pays twice for the same infrastructure, rapidly eroding the projected return on investment. Speed without validation is the primary driver of budget overruns, as unplanned downtime during cutover can cause catastrophic disruptions to global service delivery. Organizations don’t just face technical hurdles; they face financial ones that can derail digital transformation. Quantifying the business impact of these delays reveals that de-risking a large scale aws cloud migration is not merely a technical requirement but a financial imperative for the modern enterprise that values software and digital assurance testing as a cornerstone of its strategy.

Implementing a Cloud Financial Management (CFM) Framework

A successful migration isn’t just a technical achievement; it’s a financial one. Successfully de-risking a large scale aws cloud migration requires a rigorous Cloud Financial Management (CFM) framework established during the initial Assess phase. By integrating financial oversight early, organizations can prevent the budget creep that often follows unmanaged resource sprawl. This proactive stance allows technical managers to justify infrastructure spend by directly linking it to operational stability and performance gains.

Utilizing the AWS Migration Acceleration Program (MAP) provides a structured mechanism to offset initial investment costs through credits and incentives across the Assess, Mobilize, and Migrate phases. This strategic alignment is essential for de-risking data and cloud migrations, ensuring that the transition remains economically viable while maintaining high standards of data consistency. By leveraging the AWS Pricing Calculator during the Mobilize phase, teams can generate high-fidelity estimates that anchor the project in financial reality and organizational progress.

To prevent ‘bill shock’, enterprises should deploy automated cost-monitoring tools, such as the AWS Cost and Usage Report 2.0, which now includes granular details for services like Amazon Athena and Redshift. Establishing clear financial milestones allows leadership to track migration health against the original business case. This methodical approach transforms cloud spending from an unpredictable variable into a manageable asset that supports scalable growth. If you need assistance auditing your current cloud spend or planning a cost-effective transition, our team is ready to discuss your migration strategy.

Avoiding Parallel Environment Cost Traps

The financial burden of maintaining legacy on-premises hardware alongside new cloud instances can quickly erode ROI. Rapid decommissioning strategies are vital. Organizations should prioritize optimizing resource allocation to prevent over-provisioning, which often occurs when teams replicate on-premises capacity in the cloud without right-sizing. Leveraging Reserved Instances and Savings Plans early in the roadmap provides a predictable cost structure, securing long-term stability and reducing the risk of ballooning operational expenses.

Aligning Business Drivers with Technical Execution

Technical milestones must translate into tangible business outcomes. If a database migration is complete, the associated cost savings from retiring the old license should be immediately visible in transparent financial reporting. This transparency secures executive buy-in and reinforces the image of IT as a value-generating partner. Cloud Financial Management functions as a strategic discipline that aligns cloud consumption with overarching corporate objectives rather than acting as a mere tactical accounting exercise.

De-Risking a Large Scale AWS Cloud Migration: A Strategic Framework for 2026

De-Risking Through Continuous Testing and Feature Management

While the financial frameworks discussed previously provide the economic foundation for a transition, automated testing serves as the primary technical mechanism for de-risking a large scale aws cloud migration. In the 2026 enterprise landscape, where application dependencies are increasingly intricate, treating quality assurance as a post-migration afterthought is no longer viable. Instead, a strategic approach integrates continuous validation into every phase of the migration lifecycle, ensuring that each architectural shift is backed by empirical data rather than assumptions. This methodical verification process allows organizations to maintain operational stability while accelerating their modernization efforts.

Performance testing plays a critical role in validating cloud-native scalability before high-traffic workloads are transitioned. By simulating real-world demand within the AWS environment, teams can identify bottlenecks in Amazon EKS clusters or RDS configurations before they impact the end-user experience. This level of rigor ensures that the target infrastructure doesn’t just host applications but optimizes them for the superior performance standards expected of modern digital platforms. It’s about achieving precision, stability, and growth through disciplined technical execution.

Automated Validation for Large-Scale Data Integrity

Validating massive datasets without disrupting production environments requires a sophisticated blend of automation and strategy. Organizations must ensure schema consistency and data accuracy across complex hybrid environments, where legacy on-premises databases must remain synchronized with cloud-native targets. By implementing comprehensive data migration testing, teams can detect anomalies in real-time, preventing the data loss or corruption that often derails large-scale cutovers. Utilizing specialized software test automation services allows for the creation of accelerated feedback loops, providing the peace of mind that comes from knowing every record is accounted for and secure.

Feature Management: The Safety Net for Cloud Cutover

Feature management acts as a vital safety net during the final stages of a migration, allowing teams to decouple deployment from release for risk-free testing in live environments. By implementing feature toggles, organizations can execute gradual traffic migrations, moving small percentages of users to the new infrastructure while monitoring system health. This approach significantly reduces the blast radius of potential errors. If an issue is detected, the ability to trigger an instant rollback ensures that service remains uninterrupted.

  • Canary Releases: Monitor performance on a subset of users before a full-scale rollout.
  • Decoupled Deployment: Test code in production without exposing it to the entire user base.
  • Instant Rollbacks: Mitigate technical hazards with a single toggle, preserving the customer experience.

This level of control empowers enterprises to evolve their digital infrastructure with a sense of security and institutional maturity, turning a complex cutover into a predictable, non-event. By synchronizing technical methodology with these advanced release strategies, global organizations can manage their complex digital infrastructures with unparalleled expertise and reliability.

Bridging the Specialized AWS Skills Gap

The most sophisticated technical roadmap remains vulnerable without the specific human capital required for its execution. Since cloud-specific roles are expanding four times faster than traditional IT positions, the resulting scarcity of qualified architects has become a primary bottleneck for the modern enterprise. Successfully de-risking a large scale aws cloud migration depends on securing these specialized skills at the precise moment they are needed. Relying solely on internal upskilling often leads to project delays, as the learning curve for complex AI services and automated landing zones can be steep and unpredictable.

Leveraging remote offshore resources provides a strategic advantage by enabling 24/7 migration cycles. This continuous execution model accelerates timelines and ensures that critical workflows are managed with constant vigilance. For organizations operating in highly regulated sectors, the need for precision is non-negotiable. Utilizing specialized pharma IT staffing ensures that your migration team understands the nuances of the HIPAA Security Rule updates finalized in May 2026 and the upcoming EU AI Act enforcement in August. This level of industry-specific expertise is a cornerstone of our identity as a reliable long-term collaborator.

Strategic IT Staffing Models for Global Enterprises

Balancing permanent talent with flexible contract resources allows organizations to maintain a lean core team while scaling up for high-intensity migration phases. Our staffing solutions provide immediate access to vetted AWS experts who possess the institutional maturity to operate within diverse, complex environments. By integrating specialized recruiters into your planning process, you significantly reduce the time-to-hire for niche roles such as Cloud Security Architects. This agility ensures that your migration velocity remains consistent, even as technical requirements evolve. To secure the specific talent your project demands, contact our staffing specialists today.

Maintaining Operational Stability During Talent Transitions

Knowledge transfer protocols are essential to prevent ‘brain drain’ once the primary migration phase concludes. By utilizing managed services to bridge the gap during internal upskilling, enterprises ensure that their new cloud infrastructure remains optimized and secure. This human-centric approach is vital for de-risking a large scale aws cloud migration, as it ensures that technical debt is not replaced by talent debt. Expert-led DevOps engineering is an absolute necessity for achieving the long-term stability and scalable growth promised by a modernized AWS environment. This steady hand in a fast-changing technological landscape allows your organization to focus on innovation while we manage the complexities of the underlying infrastructure through precision, predictability, and partnership.

Test Triangle: Your Strategic Partner for Secure AWS Evolution

As global enterprises move toward the 2026 digital horizon, the intersection of infrastructure and platform management becomes the ultimate risk frontier. Successfully de-risking a large scale aws cloud migration requires a partner who understands that the cloud isn’t just a destination, but an evolving ecosystem that must be managed with institutional maturity. Test Triangle brings specialized expertise in DevOps consulting to ensure that your CI/CD pipelines and deployment strategies are optimized for the high standards of the AWS environment. By maintaining Atlassian ecosystem stability during these complex transitions, we help your development teams remain productive and focused on innovation rather than infrastructure discrepancies.

Our methodology extends beyond the initial cutover to provide the peace of mind found in long-term operational stability. Through managed outsourcing services, we deliver post-migration optimization that ensures your cloud environment continues to evolve alongside your business needs. This adaptable approach allows your organization to leverage the full power of AWS while we manage the technical rigor required for sustained performance. We don’t just facilitate a move; we engineer a foundation for stability, scalability, and success.

Integrating ServiceNow and AWS for Seamless ITSM

De-risking critical workflows involves more than just server migration; it requires the synchronization of your IT Service Management (ITSM) with your new cloud-native reality. Through strategic ServiceNow implementation on AWS, we optimize IT workflows to handle incident management with the speed and precision that cloud environments demand. Maintaining CMDB accuracy during massive infrastructure shifts is a common failure point that we address through rigorous validation and automated discovery. By utilizing our IT service management solutions, your organization can reduce operational friction and ensure that governance remains intact throughout the digital transformation process.

Sustaining Excellence with Long-Term Collaboration

The transition from migration to modernization is where true value is realized. Test Triangle’s commitment to reliability, precision, and growth ensures that your AWS environment remains a high-performance asset long after the final server is decommissioned. We position ourselves as a steady hand in a fast-changing technological landscape, helping you navigate complex regulatory updates and technical shifts with confidence. Our goal is to empower your leadership through risk reduction and strategic clarity. To ensure your transition is backed by global expertise, contact Test Triangle for a strategic AWS migration audit and begin your journey toward a secure, modernized future. De-risking a large scale aws cloud migration is a complex endeavor, but with the right collaborator, it becomes a predictable path to organizational progress.

Securing Your Future in the Cloud Ecosystem

Transitioning to a cloud-native state requires a disciplined synthesis of financial transparency, technical validation, and specialized talent acquisition. By establishing a robust Cloud Financial Management framework and integrating continuous automated testing, global enterprises can transform a high-stakes transition into a predictable engine for growth. De-risking a large scale aws cloud migration is ultimately about achieving institutional maturity through the careful alignment of technical execution with long-term business objectives. This methodical approach ensures that your infrastructure doesn’t just function; it excels under the rigorous demands of a modern digital economy.

Test Triangle stands as a reliable long-term collaborator with a global presence across Europe, North America, and Asia, offering specialized expertise in highly regulated sectors like Pharma and Finance. Our strategic partnerships with AWS, Atlassian, and ServiceNow allow us to manage your complex digital infrastructure with the precision, predictability, and partnership your organization demands. We invite you to secure your digital transformation with Test Triangle’s AWS migration expertise and ensure your evolution is managed by a steady hand. Together, we can turn technological complexity into a sustainable competitive advantage.

Frequently Asked Questions

What are the primary risks associated with a large-scale AWS cloud migration?

The primary risks include the accumulation of technical debt, security vulnerabilities during the cutover phase, and financial erosion caused by unmanaged parallel environments. In the 2026 landscape, AI-driven discovery failures can also lead to misaligned landing zones and architectural instability. Successfully de-risking a large scale aws cloud migration requires identifying these failure points early to ensure that modernization takes precedence over simple relocation.

How can we manage parallel environment costs during a long-term migration?

Managing parallel environment costs requires the disciplined integration of Cloud Financial Management (CFM) and rapid decommissioning schedules for on-premises hardware. Organizations should utilize tools like the AWS Pricing Calculator to generate high-fidelity estimates and prevent the over-provisioning that often drains ROI. By right-sizing instances and leveraging Savings Plans early in the roadmap, enterprises can protect their business case throughout the transition.

What role does automated testing play in de-risking a cloud transition?

Automated testing serves as the primary technical mechanism for validating system behavior and data accuracy in the new environment. It allows teams to execute comprehensive regression suites and performance benchmarks without manual intervention, which significantly accelerates feedback loops. This rigorous validation ensures that complex application dependencies are preserved and that the target infrastructure meets the high standards of security required for enterprise stability.

Is it better to retrain existing staff or hire AWS specialists for a migration?

A hybrid approach that combines internal upskilling with specialized IT staffing services is often the most effective strategy for maintaining migration velocity. While retraining builds long-term institutional knowledge, hiring AWS specialists provides the immediate expertise needed to navigate complex architectural shifts. This balance ensures that your project doesn’t stall due to the steep learning curve associated with advanced cloud-native services and automated landing zones.

How can we ensure data integrity when moving massive enterprise datasets to AWS?

Ensuring data integrity involves implementing schema consistency checks and utilizing high-performance tools like AWS DataSync. As of June 2026, DataSync Enhanced mode offers a cost-effective way to manage large transfers at $0.015 per gigabyte in the US East (Ohio) region. Rigorous validation testing must be performed to confirm that every record is accurately moved, preventing the data corruption that can derail global service delivery.

What is the AWS Migration Acceleration Program (MAP) and how does it reduce risk?

The AWS Migration Acceleration Program (MAP) is a comprehensive three-phase methodology that provides financial incentives and technical best practices to reduce migration risk. It offers credits and support across the Assess, Mobilize, and Migrate phases to offset the initial infrastructure investment. This structured framework ensures that organizations follow proven pathways, leading to a more predictable and cost-effective transition to a modernized cloud environment.

How do we maintain uptime for critical tools like ServiceNow during migration?

Maintaining uptime for ServiceNow requires a strategic integration of ITSM workflows with AWS native monitoring tools like CloudWatch. Organizations must ensure CMDB accuracy during infrastructure shifts to prevent service disruptions and fragmented data silos. By implementing strategic IT service management solutions, teams can synchronize incident management and governance, ensuring that critical business tools remain operational and optimized throughout the migration lifecycle.

How long does a typical large-scale enterprise AWS migration take to de-risk?

The duration of a large-scale migration varies based on architectural complexity, but the de-risking process typically begins with a 3-6 month mobilization phase. For technical reference, the AWS Application Migration Service (MGN) provides a 90-day free period for each source server, which often serves as a window for initial validation. A full-scale enterprise evolution toward modernization can take 12-24 months to achieve complete operational stability and ROI.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.

What if the premium your organization pays for digital stability is actually subsidizing a provider’s internal inefficiencies rather than fueling your own technological evolution? Many enterprise leaders feel the weight of opaque Managed Service Provider Subscription Fees that continue to climb even as service levels stagnate or critical resources remain underutilized. It’s a common frustration to find your budget tied up in “shelfware” or rigid retainers that prioritize ticket volume over the strategic health of your ServiceNow or Atlassian ecosystems.

This 2026 guide is designed to help you master the complexities of modern pricing structures, allowing you to align your investment with specific business outcomes and long-term operational stability. You’ll discover a clear framework for comparing complex quotes and learn how to shift the conversation from basic maintenance to high-impact platform optimization. We will explore current industry benchmarks for per-user and co-managed models, identify the hidden costs in low-tier plans, and provide the methodology needed to secure a partnership that prioritizes your ROI through disciplined DevOps and ITSM integration.

Key Takeaways

  • Understand why traditional break-fix models have been superseded by recurring structures. These frameworks prioritize continuous digital transformation and operational stability.
  • Master the nuances of Managed Service Provider Subscription Fees by comparing per-user and per-device models. This ensures your IT spend remains predictable in a remote-first environment.
  • Identify hidden value drivers and setup costs to prevent paying for underutilized “shelfware” or services that don’t scale.
  • Establish a rigorous evaluation framework for reviewing SLAs and RFP responses. Your service levels must effectively support business-critical platforms like ServiceNow.
  • Learn how to bridge the gap between technical execution and strategic success. Integrating specialized Atlassian implementation expertise into your managed support model is a critical differentiator.

Defining Managed Service Provider Subscription Fees in 2026 requires a perspective that views technology as a driver of institutional maturity rather than a simple cost center. In the current market, the reactive “break-fix” hourly model has been almost entirely marginalized in favor of recurring subscriptions that guarantee operational continuity and risk mitigation. Leaders must understand what a managed service provider is in this new era: a long-term collaborator that manages complex digital infrastructures through systemic improvement rather than mere incident response. This shift reflects a broader economic reality where global volatility demands predictable, outcome-linked expenditure that aligns with long-term strategic goals.

The transition from “Monitoring-Only” to “Outcome-Based” pricing represents the most significant change in how enterprises evaluate their IT investments. While legacy providers focused on uptime and ticket volume, the modern framework prioritizes the acceleration of specific business objectives. Global economic shifts, including talent scarcity in specialized technical fields and the rising costs of cybersecurity insurance, have naturally influenced MSP margin expectations and base rates. However, the move toward transparent, value-driven models ensures that organizations can justify these costs by measuring the direct impact on their digital transformation journey.

The Evolution of Value-Based IT Support

The industry has reached a tipping point where uptime metrics alone no longer justify high-level retainers. Modern enterprises are prioritizing business-aligned performance indicators, shifting the focus of Managed Service Provider Subscription Fees toward Precision, Progress, Performance. By integrating advanced automation and cognitive computing into their internal workflows, providers are effectively reducing the overhead of commoditized tasks. This allows them to redirect human capital toward high-level strategic architecture. Consequently, organizations are now prioritizing platform-specific expertise over generalist support, recognizing that specialized knowledge is required to optimize complex environments.

Subscription Fees vs. Professional Service Fees

Maintaining a clear distinction between recurring maintenance and project-based consulting is essential for transparent budgeting and margin management. While subscription fees cover the ongoing health, security, and incremental updates of your IT service management ecosystem, one-time initiatives usually fall under professional service fees. For instance, a full-scale Atlassian implementation or a major ServiceNow migration requires a time-and-materials approach due to its unique scope. Identifying which IT needs fit a subscription model depends on the frequency and predictability of the requirement. A robust Service Level Agreement (SLA) acts as the definitive boundary, ensuring that both parties agree on what constitutes “business as usual” versus a specialized transformation project.

Selecting the appropriate framework for Managed Service Provider Subscription Fees is a critical decision that influences both operational agility and budgetary precision. In a remote-first work environment, the debate between “Per-User” and “Per-Device” models has largely settled in favor of user-centric billing. This shift reflects the reality that modern professionals often operate across multiple endpoints, making device-based tracking an administrative burden. While approximately 13% of providers still rely on per-device pricing as their primary model, around 26% have transitioned to a hybrid approach that combines elements of both to better reflect the complexity of modern enterprise infrastructures.

For organizations managing high-stakes environments, the “All-You-Can-Eat” model often provides the most robust ROI. This comprehensive structure decouples support from ticket volume, encouraging a proactive partnership where the provider is incentivized to eliminate root-cause issues rather than billing for repetitive fixes. When evaluating these models, it’s vital to align the chosen tier with your actual needs. Many enterprises find themselves overpaying for “Gold” tier packages that include redundant compliance features, when a “Silver” tier combined with targeted ServiceNow consulting services would offer a more precise fit for their operational requirements.

The Per-User Pricing Model: The 2026 Standard

Per-user billing has emerged as the industry standard because it simplifies scalability during periods of rapid organizational growth. This model aligns the provider’s incentives with the client’s success; fewer technical disruptions lead to lower operational costs for the MSP, fostering a culture of Stability, Security, Success. To prevent overbilling, enterprises must implement rigorous audits of “active user” counts within their directory services. Ensuring that subscription fees are only applied to current, authorized personnel is a fundamental step in maintaining a lean and efficient IT budget. If you’re looking to optimize your resource allocation, you might consider how tailored staffing strategies can complement your existing support structure.

Tiered and À La Carte Options

Tiered structures allow organizations to construct a custom service stack that matches specific platform needs without the risks associated with pure Ă  la carte pricing. While Ă  la carte models offer initial flexibility, they often lead to “nickel and diming” for essential security patches or routine maintenance tasks. A more strategic approach involves evaluating tiered packages against your internal DevOps and QA capabilities. For instance, an organization with a strong internal testing team may only require a subscription that covers specialized Atlassian implementation support and high-level architectural guidance, rather than a full-service helpdesk retainer.

Managed Service Provider Subscription Fees: The 2026 Enterprise Buying Guide

Beyond the Monthly Retainer: Identifying Hidden Costs and Value Drivers

While the monthly retainer is the most visible element of Managed Service Provider Subscription Fees, the true total cost of ownership is often dictated by variables that sit just below the surface. Strategic procurement requires a granular understanding of how onboarding fees, platform licensing, and integrated personnel models impact the long-term budget. A common pitfall for enterprises is failing to account for “out-of-scope” triggers. These are specific events or requests that fall outside the standard agreement, leading to unexpected billing spikes that can disrupt even the most disciplined financial planning. By identifying these triggers during the negotiation phase, you can ensure your expenditure remains predictable and aligned with your ROI targets.

Platform licensing for ecosystems like Atlassian and ServiceNow also plays a significant role in your overall spend. Whether your provider manages these licenses on your behalf or you maintain them internally, the complexity of these environments often necessitates specialized oversight. Integrating staffing solutions directly into your managed service framework allows for more sophisticated margin management. This approach enables you to fill specific skill gaps, such as specialized manual or automation testing, without the need to upgrade your entire service tier for the entire organization.

Onboarding and Implementation Charges

A professional system audit and environment baseline are the core components of a legitimate onboarding fee. This initial phase is not merely a setup cost; it’s a rigorous process that ensures your provider understands the nuances of your digital infrastructure. When negotiating multi-year managed service contracts, it’s often possible to amortize these setup fees or tie them to specific implementation milestones. You must ensure that comprehensive knowledge transfer is explicitly included in this phase. This prevents vendor lock-in and guarantees that your internal teams remain empowered and informed throughout the partnership.

The Role of Specialized Talent in MSP Fees

The integration of managed outsourcing services can significantly lower your subscription overhead by optimizing the delivery model. By balancing high-level local strategic consulting with cost-effective technical execution teams, providers can offer a more versatile and globally-minded support structure. This model provides “fractional” access to elite DevOps and QA experts who might be too expensive to hire as full-time internal resources. This hybrid approach delivers Precision, Proximity, Productivity, ensuring that your technical managers have the specific expertise they need exactly when they need it, without inflating the base subscription rate.

The Strategic Buyer’s Framework for Evaluating MSP Proposals

Evaluating Managed Service Provider Subscription Fees through the lens of a Request for Proposal (RFP) demands a rigorous methodology that transcends basic cost comparisons. A strategic buyer doesn’t merely look for the lowest monthly retainer; instead, they seek to understand the correlation between the fee structure and the provider’s ability to deliver operational resilience. This evaluation process should involve five critical questions designed to expose the depth of a provider’s strategic commitment. These include inquiries into their methodology for license optimization, their internal security protocols, and how they define “value” beyond basic ticket resolution. By forcing providers to articulate their impact on your long-term digital health, you can distinguish between a simple vendor and a high-level corporate partner.

When assessing an SLA for business-critical environments such as ServiceNow, it’s essential to look for guarantees that protect against systemic failure rather than just slow response times. Cheaper bids often indicate a lack of platform-specific expertise, which can be disastrous during complex Atlassian Cloud migrations or infrastructure overhauls. Using the “Cost of Downtime” as a benchmark allows technical leaders to justify higher-tier managed service subscriptions to executive stakeholders. If an hour of system unavailability costs the enterprise significantly more than the annual premium for expert support, the decision to prioritize quality becomes a matter of risk management rather than just procurement. High-level support delivers Stability, Scalability, Security, protecting your most valuable digital assets from preventable disruptions.

Auditing Vendor Expertise and Certifications

Authorized partnership status, such as being an Atlassian Platinum partner, should significantly influence your fee tolerance. These endorsements serve as official benchmarks of a provider’s technical depth and their direct line to platform-level support. Industry-specific experience is equally vital, particularly in highly regulated sectors like Pharma or Finance where compliance is non-negotiable. You must verify the MSP’s internal security protocols and their history of managing diverse, complex digital infrastructures. A partner’s ability to operate across these rigid regulatory frameworks ensures that your organizational progress isn’t hindered by compliance gaps.

Negotiating for Scalability and Flexibility

Building “ramp-up/ramp-down” clauses into your agreement ensures that Managed Service Provider Subscription Fees reflect the actual usage of your cloud-based tools. As your organization evolves, your support needs will fluctuate; your contract should be versatile enough to accommodate these shifts without punitive penalties. It’s also critical to review the exit strategy early in the relationship. Offboarding and data migration costs should be transparently defined to prevent financial friction at the end of the collaboration. If you are ready to move beyond generic support and secure a partner who understands the complexities of your digital ecosystem, reach out to our team today for a strategic consultation.

Test Triangle: Aligning Managed Service Fees with Enterprise Excellence

Test Triangle operates as a strategic visionary for global enterprises, ensuring that Managed Service Provider Subscription Fees are never viewed as a static overhead but as a catalyst for systemic improvement. Our philosophy centers on transparent, outcome-linked models that prioritize the long-term health of your digital infrastructure. We recognize that a one-size-fits-all approach fails to address the nuances of complex environments. Therefore, we customize our fee structures to align precisely with your specific digital transformation roadmap, ensuring every dollar spent contributes to measurable operational progress and institutional maturity.

The “Test Triangle Advantage” lies in our unique ability to bridge the gap between technical execution and business outcomes. By combining deep technical expertise in manual and automation testing with strategic IT service management solutions, we offer a comprehensive support framework that generalist providers cannot match. We seamlessly integrate specialized Atlassian implementation expertise into our ongoing managed support, ensuring that your platforms are not only maintained but continuously optimized for peak performance. This integrated approach delivers Precision, Proactivity, Partnership, positioning us as a reliable collaborator deeply invested in your stability.

Strategic Platform Optimisation

Our managed services move beyond the limitations of ticket-based metrics to focus on holistic system health and efficiency. We believe that true value is found in preventing disruptions before they occur, which is why our methodology emphasizes proactive monitoring and architectural refinement. As highlighted in our strategic guide to Atlassian consulting, organizations that prioritize strategic oversight over basic maintenance often see a significant reduction in long-term operational spend. By leveraging a global presence, we provide extended availability across diverse time zones, delivering high-level expertise without the premium price tag typically associated with localized, around-the-clock coverage.

Your Partner in Long-Term Operational Stability

We act as a disciplined extension of your internal IT and DevOps teams, fostering a spirit of partnership that is deeply invested in your long-term success. Our commitment to transparent billing ensures that your Managed Service Provider Subscription Fees remain predictable, with regular Strategic Business Reviews (SBRs) providing clear visibility into performance and ROI. We prioritize organizational stability through a combination of human expertise and industry-leading technical tools, ensuring a steady hand in a fast-changing landscape. To define a managed service model that fits your 2026 goals and empowers your technological evolution, contact our team for a detailed consultation.

Securing Your Digital Future Through Strategic Partnership

Mastering the nuances of Managed Service Provider Subscription Fees is no longer just a procurement task; it’s a strategic imperative for organizations aiming for long-term operational stability. By shifting from reactive, ticket-based expenditure to outcome-linked models, enterprises can transform their IT budget into a powerful engine for digital evolution. This guide has detailed the importance of auditing platform-specific expertise and identifying hidden value drivers to ensure your investment delivers Precision, Progress, Performance. As technical landscapes grow more complex, the ability to align recurring costs with tangible business milestones becomes the definitive marker of a mature digital strategy.

As an Atlassian Platinum Partner and ServiceNow Specialist Partner, Test Triangle provides the institutional maturity required to manage your most complex digital infrastructures with confidence. Our global delivery model ensures you receive expert support across all time zones, allowing your internal teams to focus on high-level innovation rather than routine maintenance. We remain committed to transparent, disciplined collaboration that prioritizes your strategic success and operational resilience. Optimise your IT spend with a strategic Managed Service consultation from Test Triangle and take the first step toward a more predictable, value-driven technological landscape. We look forward to supporting your journey toward enterprise excellence.

Frequently Asked Questions

What is the average monthly cost for a Managed Service Provider subscription?

In the 2026 US market, Managed Service Provider Subscription Fees typically range from $110 to $400 per user per month. These rates vary based on the depth of the service catalog, including whether the package incorporates advanced security monitoring, compliance oversight, or specialized platform management. Organizations opting for co-managed models, where they retain an internal IT lead, often see lower per-user rates compared to those requiring full-service outsourcing.

Do MSP subscription fees usually include software licenses like Atlassian or ServiceNow?

Subscription fees generally cover the management and optimization of the platform rather than the underlying software licenses themselves. Licensing for enterprise ecosystems like ServiceNow or Atlassian is usually treated as a separate pass-through cost or managed directly by the client. However, working with a partner who can provide Atlassian Licenses as part of a consolidated agreement often simplifies the procurement process and ensures that seat counts are audited for maximum efficiency.

How often should an MSP review and adjust their subscription fees?

Subscription fees should be reviewed annually or during scheduled Strategic Business Reviews (SBRs) to ensure they remain aligned with your actual resource consumption. These reviews allow both parties to adjust for changes in headcount, infrastructure complexity, or new regulatory requirements. A transparent review process prevents budgetary drift and guarantees that your expenditure continues to reflect the strategic value delivered to the enterprise.

What is the difference between an MSP subscription and a traditional IT support contract?

A modern MSP subscription is a proactive, outcome-based model that prioritizes systemic health through a predictable recurring fee. In contrast, traditional IT support often follows a reactive “break-fix” approach where costs are tied to ticket volume or hourly rates. The subscription model aligns the provider’s incentives with your success; they are motivated to eliminate root-cause issues to reduce their own operational overhead while maintaining your stability.

Are there hidden costs in MSP onboarding that I should look out for?

Hidden costs often emerge in the form of system auditing, environment baselining, and complex data migration tasks that fall outside the initial quote. You should also verify if knowledge transfer sessions and the integration of legacy tools are included in the setup fee. Ensuring these activities are clearly defined in the Service Level Agreement prevents unexpected billing spikes and ensures a steady hand during the transition period.

Can I negotiate a lower subscription fee by using offshore technical resources?

Utilizing a global delivery model that incorporates remote offshore resources can significantly optimize your Managed Service Provider Subscription Fees without sacrificing technical rigor. This hybrid approach allows you to access specialized talent for execution-heavy tasks like automation testing while maintaining local strategic oversight. It provides a versatile, globally-minded support structure that delivers high-level expertise at a more sustainable price point for large-scale digital infrastructures.

How do I calculate the ROI of my Managed Service Provider subscription fees?

ROI is calculated by measuring the reduction in system downtime, the speed of digital transformation initiatives, and the cost-efficiency gained by reallocating internal staff to strategic projects. You must also account for the risk mitigation provided by expert platform oversight, which prevents costly configuration errors and security gaps. A successful subscription delivers Stability, Scalability, Security, providing value that transcends simple maintenance to drive organizational progress.

What happens to my subscription fees if my company scales rapidly?

Per-user pricing models are designed to scale automatically, ensuring that your costs stay aligned with your headcount as you grow. To maintain financial precision, it’s essential to build “ramp-up/ramp-down” clauses into your agreement to accommodate rapid changes without punitive penalties. This flexibility ensures that your managed service model remains an adaptable collaborator that supports your growth rather than a rigid financial burden during periods of expansion.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.
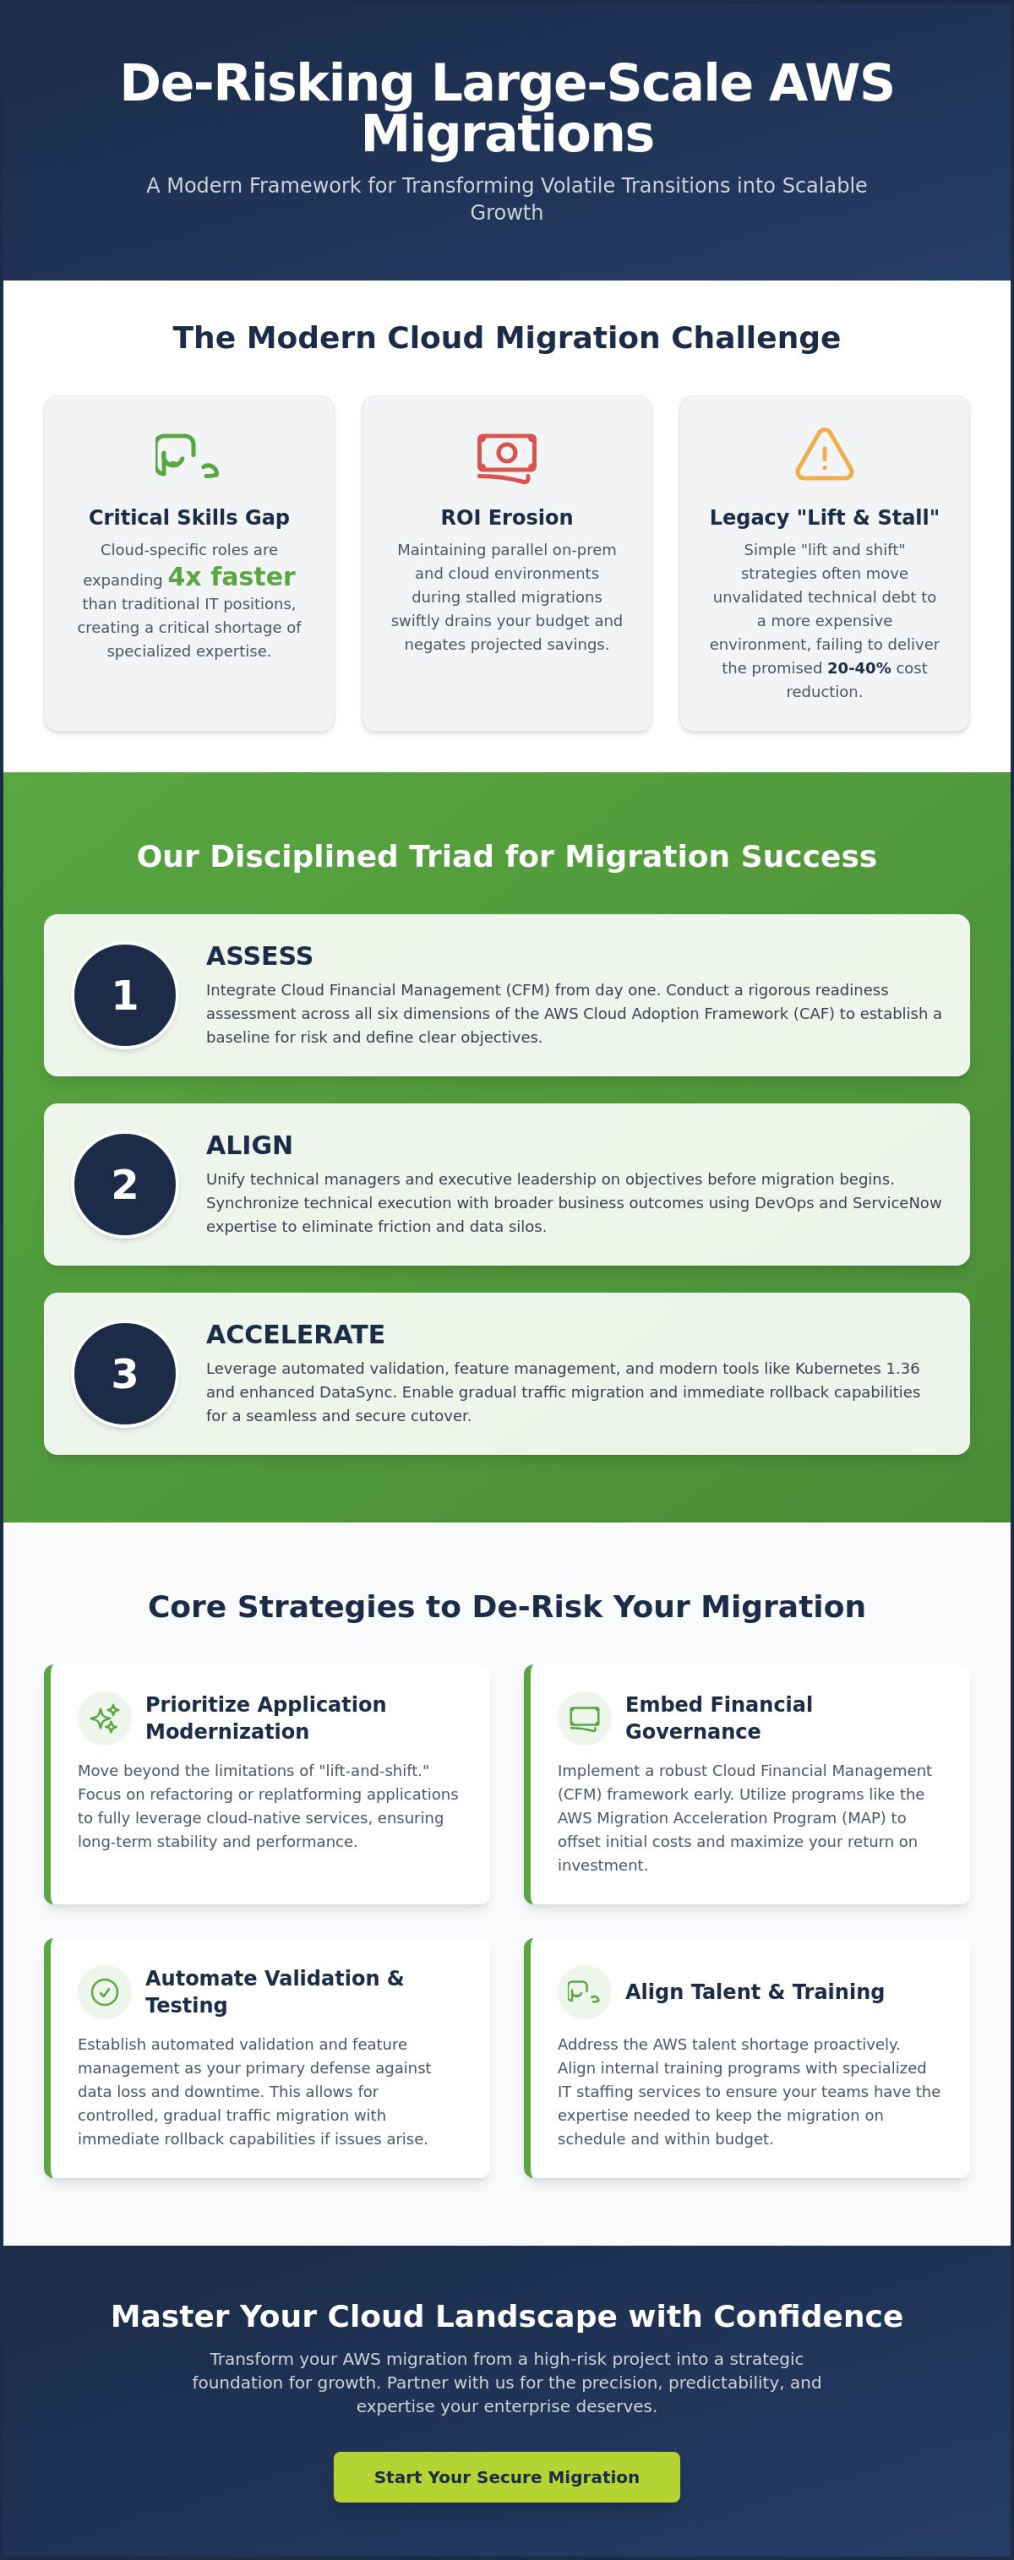

Did you know that while 94% of enterprises have integrated at least one cloud service by 2026, 38% of these migrations still exceed their original budget? This fiscal friction often stems from parallel running costs or unforeseen complexities in data sovereignty. For global leadership, the prospect of an AWS Cloud Migration shouldn’t feel like a gamble with your operational stability or a test of your team’s existing skill gaps. It’s natural to feel uneasy about potential business downtime or the tightening grip of regulations like India’s DPDPA 2025 updates and Canada’s 2026 sovereign cloud policies.

You deserve a transition that prioritizes precision over guesswork. We’ve designed this strategic guide to help you master the complexities of enterprise evolution; providing a professional roadmap that ensures security, scalable growth, and a significant reduction in technical debt. By exploring the 7 Rs of migration and the latest AI-driven discovery tools, we’ll outline a clear path to improved system performance that aligns with your 2026 digital transformation goals. This approach ensures your organization achieves precision, partnership, and progress throughout the entire lifecycle.

Key Takeaways

  • Identify how the “7 Rs” framework provides a disciplined methodology for categorizing workloads, ensuring each application follows the most efficient path toward modernization.
  • Learn to navigate a structured AWS Cloud Migration roadmap that moves from initial portfolio assessment to the establishment of a secure, compliant landing zone.
  • Address the critical human element of technological change by bridging internal skill gaps and overcoming cultural resistance within highly regulated enterprise environments.
  • Discover how to maximize post-migration ROI by optimizing ServiceNow and Atlassian ecosystems through specialized DevOps consulting and managed support.
  • Shift your operational focus from simple relocation to systemic evolution, utilizing agentic AI to accelerate modernization timelines and improve long-term system performance.

The Strategic Imperative: Why AWS Cloud Migration Defines Enterprise Success in 2026

In 2026, the concept of cloud migration has moved far beyond simple data transfer. It’s now a fundamental catalyst for systemic enterprise evolution and digital maturity. An effective AWS Cloud Migration represents a shift from static infrastructure to a dynamic, machine-speed environment where agentic AI and predictive analytics define the pace of business. Modern organizations don’t view this transition as a one-time technical task. Instead, they recognize it as a strategic opportunity to rebuild their operational core for a future that demands constant adaptation. It’s about building a foundation that supports continuous improvement, operational stability, and long-term resilience.

By moving from rigid capital expenditure (CapEx) models to a performance-driven operational (OpEx) framework, enterprises gain the agility to respond to market shifts in real-time. This isn’t just about reducing costs; it’s about optimizing value across the entire digital ecosystem. We approach every migration through a specific “Test Triangle” perspective: Strategy, Security, and Scalability. This trifecta ensures that your technological evolution is grounded in practical business outcomes. When you align your high-level mission with technical execution, you create a steady hand in a fast-changing landscape.

Beyond Cost Savings: The Modern Drivers of Migration

Modern migration is fueled by a need for operational resilience. In a volatile global market, the ability to maintain business continuity through AWS’s distributed infrastructure is a competitive necessity. Innovation velocity has also become a primary driver. The cloud allows for rapid prototyping and the deployment of AI-driven applications that would be impossible in legacy environments. Additionally, AWS’s carbon-efficient infrastructure helps organizations meet increasingly strict corporate sustainability mandates. This turns technical decisions into environmental, social, and governance (ESG) victories by utilizing real-time carbon footprint reporting.

The Risks of Inertia: What Happens When You Delay?

Delaying your cloud journey creates a compounding burden of technical debt. Aging on-premises data centers become increasingly expensive to maintain and lack the modern cloud-native protections required to thwart sophisticated security threats. There is also a significant human cost. The widening talent gap means that top IT professionals actively seek out cloud-native environments. If you aren’t evolving, you’ll struggle to attract the experts needed to run your business. Our staffing solutions can help bridge this gap, but the underlying infrastructure must be modern to sustain a high-performing team.

Selecting Your Path: The 7 Rs of AWS Migration Strategy

Successful cloud evolution requires more than just moving data; it demands a disciplined methodology to categorize every workload within your enterprise portfolio. The “7 Rs” framework serves as this strategic compass, allowing leadership to balance speed, cost, and long-term digital maturity. By assigning a specific migration path to each application, you avoid the “complexity trap” that often stalls large-scale transitions. Whether your goal is immediate data center exit or a complete overhaul for AI readiness, selecting the right path is the most critical decision in your AWS Cloud Migration journey. It’s about matching technical execution to specific business outcomes, ensuring that every move contributes to operational stability and scalable growth.

Tactical Execution: Rehost, Relocate, and Repurchase

For organizations prioritizing speed and risk reduction, tactical strategies offer the path of least resistance. Rehosting, or “lift-and-shift,” remains the most common approach, accounting for 38.3% of migrations according to 2026 industry data. It allows you to move applications to the cloud without modifying the core code, making it ideal for large-scale legacy environments. Relocating leverages VMware Cloud on AWS to move hundreds of instances simultaneously at the hypervisor level, maintaining operational consistency. Meanwhile, repurchasing involves shifting from perpetual licenses to modern SaaS models. This is an excellent opportunity to transition legacy service desks to a modern ServiceNow implementation or move project management to the cloud with expert Atlassian consulting.

Strategic Transformation: Replatform and Refactor

When the objective is systemic improvement rather than simple relocation, strategic transformation becomes the priority. Replatforming involves making targeted optimizations, such as migrating to managed database services, to boost performance without a full architectural rewrite. Refactoring, however, is the gold standard for 2026. This approach re-architects applications to be cloud-native, enabling full integration with agentic AI and serverless computing. While it requires more upfront investment, refactoring delivers the highest levels of scalability and long-term ROI. If you’re unsure which path aligns with your fiscal year goals, our team can help you evaluate your portfolio architecture to find the optimal balance.

Finally, a robust AWS Cloud Migration strategy must include portfolio hygiene through Retaining and Retiring. Retaining involves keeping specific workloads on-premises to meet strict sovereign cloud procurement policies, such as Canada’s 2026 data residency requirements. Retiring focuses on decommissioning redundant or obsolete systems, which can significantly reduce technical debt and streamline your security perimeter. By rigorously applying these seven categories, you transform a chaotic move into a structured, predictable evolution that empowers your entire organization.

AWS Cloud Migration: A Strategic Step-by-Step Guide for Enterprise Evolution in 2026

A Step-by-Step Roadmap to a Seamless AWS Transition

Transitioning to a cloud-native ecosystem requires a methodical, phase-gated approach that prioritizes operational stability over sheer speed. A successful AWS Cloud Migration isn’t a single event but a journey that demands technical precision, organizational readiness, and expert partnership. By following a structured roadmap, enterprises can navigate the complexities of 2026’s digital landscape while mitigating the risks of business downtime and regulatory non-compliance. This process moves logically from broad portfolio assessment to specific service optimization, ensuring that your technological evolution is both intentional and well-organized.

Phase 1 & 2: Preparation and Foundation

The journey begins with a Comprehensive Portfolio Assessment and Business Case Validation. During this stage, conducting an Optimization and Licensing Assessment (OLA) is essential to right-size your cloud footprint, preventing the over-provisioning that often leads to budget overruns. Establishing a Cloud Center of Excellence (CCoE) ensures cross-functional alignment, bringing together leadership from IT, finance, and security to drive a unified vision. We then move into the Mobilisation Stage, where we build your AWS Landing Zone. This involves designing a multi-account structure that enforces strict security guardrails and compliance foundations, providing a steady hand for your complex digital infrastructure.

Phase 3 & 4: Migration and Quality Assurance

In the Execution phase, we implement automated waves of workload transfers. In 2026, we utilize tools like AWS Migration Hub, which now incorporates predictive analytics to map application dependencies. This intelligence can reduce the discovery phase by months, allowing for a more efficient and disciplined move. However, the migration is only complete once it passes through rigorous validation. Data Migration Testing plays a critical role here, ensuring that data integrity is maintained and that no business logic errors are introduced during the transition. By focusing on precision and human expertise, we confirm that all performance benchmarks are met before the final cutover.

To minimize operational impact, final cutover strategies often employ blue-green deployments or canary releases. These methodologies allow for a seamless transition by running the new environment alongside the old, providing the peace of mind that comes from risk reduction. After the cutover, we shift our focus to post-migration validation, where we continuously monitor system performance and scalability. This methodical rhythm ensures that your organization doesn’t just reach the cloud but thrives within it, achieving the operational efficiency and scalable growth promised at the start of the journey.

Overcoming Enterprise Migration Challenges: People, Process, and Security

While technical frameworks provide the architecture, the primary friction points of an AWS Cloud Migration frequently reside within organizational culture and human capital. Addressing the internal skills gap while managing cultural resistance to change is a prerequisite for leadership teams pursuing long-term operational stability. In highly regulated sectors such as Finance and Pharmaceuticals, organizations often fall into a “complexity trap” where legacy processes conflict with cloud-native agility. Navigating these hurdles requires a composed, solution-oriented approach that prioritizes precision, partnership, and progress. By treating the transition as a human-centric evolution rather than a mere server move, you ensure that your digital infrastructure remains resilient and your workforce remains empowered.

The Human Element: Staffing and Training

Executing a large-scale evolution requires a specialized workforce, including Cloud Architects, DevOps engineering professionals, and Security Specialists. Many organizations find that their existing IT teams possess deep institutional knowledge but lack the specific cloud-native expertise required for a seamless transition. To bridge these immediate project needs, savvy enterprises leverage professional IT Staffing Services to inject high-level expertise into their migration waves. Additionally, integrating remote offshore resources allows for continuous delivery cycles and significant cost-efficiency without compromising technical rigor. This dual approach empowers your organization to maintain momentum while simultaneously upskilling your internal workforce for the new operational reality.

Security and Compliance in the Cloud

Security isn’t a peripheral concern; it’s a foundational pillar of the “Test Triangle” methodology. Implementing Zero Trust architectures within your AWS environment from day one ensures that every access request is verified, regardless of its origin. In highly regulated industries, automating compliance monitoring is the only way to consistently meet evolving standards like GDPR, HIPAA, or GxP. Staying current with OWASP Top 10 2025 news is equally critical, as emerging vulnerability categories directly inform the security guardrails you must enforce within your cloud environment. The AWS Shared Responsibility Model defines cloud security as a collaborative effort where AWS manages the security of the cloud, while the customer remains responsible for security in the cloud. By clearly defining these boundaries, you achieve the peace of mind that comes from comprehensive risk reduction and systemic protection.

If your internal teams are facing a skills bottleneck that threatens your timeline, contact us to discuss strategic staffing solutions that align with your migration goals. This collaboration ensures your transition remains on track while building the institutional maturity needed for long-term success.

Maximizing Post-Migration ROI: Modernization and Managed Support

The successful completion of an AWS Cloud Migration is not the final destination; it’s the foundation for systemic enterprise evolution. While many organizations focus purely on the technical cutover, the most successful global players shift their focus toward modernization to unlock the full potential of their cloud environment. This evolution involves moving beyond simple workload management to embracing cloud-native architectures that support agentic AI and predictive analytics. By partnering with a reliable Managed Service Provider, leadership teams can maintain system health while exercising rigorous cost control. Utilizing tools like AWS Cost Explorer on a monthly basis ensures that your cloud spend remains optimized, preventing the budget creep that historically affects nearly 38% of enterprise migrations.

Integrating Your Enterprise Ecosystem

Integrating your established enterprise tools into the AWS ecosystem creates a “single pane of glass” view for your IT Service Management (ITSM) across complex hybrid environments. Enhancing your Atlassian implementation with cloud-native scalability allows your development teams to operate with greater agility and precision. Similarly, by integrating ServiceNow consulting services with AWS data lakes, you can streamline workflows and derive deeper insights from your operational data. This synergy ensures that your infrastructure remains manageable, secure, and fully aligned with your high-level business outcomes; providing the peace of mind that comes from a well-organized digital estate.

The Path to DevOps Maturity

A successful AWS Cloud Migration serves as the critical starting line for advanced DevOps consulting initiatives that drive long-term digital maturity. Implementing Infrastructure as Code (IaC) allows for repeatable, error-free environment provisioning, which is essential for maintaining stability as your organization scales. This methodical approach to automation reduces technical debt and empowers your workforce to focus on high-value innovation rather than routine maintenance. Ultimately, your cloud journey is a process of constant refinement where human expertise and technical tools combine to drive organizational progress. Understanding the evolving landscape of DevOps engineering in 2026 can help enterprise leaders avoid common misconceptions that stall automation efforts and prevent technical investments from translating into measurable business outcomes. Migration is never a static destination; it is the catalyst for continuous digital innovation and sustainable growth in a fast-changing technological landscape.

Secure Your Digital Future Through Strategic Evolution

Transitioning to the cloud in 2026 is no longer a matter of simple technical feasibility; it’s a strategic necessity for enterprises aiming to lead in an increasingly machine-speed economy. We’ve explored how a disciplined approach to modernization empowers organizations to shed technical debt while embracing agentic AI and cloud-native scalability. By aligning your application portfolio with the 7 Rs framework and prioritizing human-centric staffing, you transform potential operational risks into clear competitive advantages. This journey requires a steady hand and a commitment to long-term digital maturity.

As an AWS Consulting Partner with specialized expertise in highly regulated sectors like Pharma and Finance, Test Triangle acts as a reliable long-term collaborator for your digital journey. Our global delivery model and 24/7 managed support ensure your infrastructure remains resilient, secure, and optimized long after the initial cutover. Partner with Test Triangle for your strategic AWS Cloud Migration roadmap today to achieve the precision, stability, and growth your enterprise deserves. Your path to a modernized, high-performance future starts here.

Frequently Asked Questions

What is the average timeline for an enterprise AWS cloud migration?

The average timeline for an enterprise AWS Cloud Migration typically ranges from six to twenty-four months, depending on the complexity of your application portfolio and the chosen strategy. While small-scale proof-of-concept projects can be executed in weeks, large-scale systemic evolution requires a methodical approach that accounts for discovery, foundation building, and validation. Factors like data volume, regulatory requirements, and internal team readiness significantly influence the overall duration.

How much does AWS cloud migration cost for a mid-sized organization?

Costs for a mid-sized organization vary based on the scale of the workloads and the selected 7 Rs strategy. Major expenses often include parallel running costs, where organizations maintain both on-premise and cloud environments for three to eighteen months. Additionally, data transfer fees and underlying infrastructure provisioned during replication contribute to the total investment. Utilizing a professional roadmap helps identify these hidden expenses early, ensuring fiscal transparency and long-term ROI.

Can I migrate legacy applications to AWS without rewriting the code?

You can certainly migrate legacy applications without rewriting code by utilizing the Rehosting or “Lift-and-Shift” strategy. This approach is the most common path for data center exits, as it moves applications directly to AWS infrastructure with minimal modification. While this provides a rapid transition, it won’t immediately unlock cloud-native benefits like auto-scaling or AI integration. It serves as a practical first step before pursuing deeper modernization in subsequent phases.

What are the most common risks associated with AWS cloud migration?

The most common risks associated with an AWS Cloud Migration include unexpected business downtime, internal skill gaps, and complex regulatory compliance hurdles. Without a disciplined transition plan, organizations may face data integrity issues or security vulnerabilities in their new environment. Mitigating these risks requires a combination of robust testing methodologies and strategic staffing to ensure that technical execution aligns with operational stability and security benchmarks.

How does AWS migration impact my existing Atlassian or ServiceNow licences?

Migration offers a strategic opportunity to optimize your existing Atlassian or ServiceNow ecosystem by transitioning from perpetual licenses to modern SaaS models. While the underlying business logic remains consistent, moving these platforms to the cloud often requires a licensing assessment to ensure compliance and cost-efficiency. Our experts help align these tools with your new AWS environment, providing a single pane of glass view for your IT service management operations.

Is AWS cloud migration secure for highly regulated industries like healthcare?

AWS migration is highly secure for regulated sectors like healthcare, provided organizations implement a Zero Trust architecture and follow the Shared Responsibility Model. AWS provides specialized services and infrastructure that comply with global standards such as HIPAA, GDPR, and GxP. By automating compliance monitoring and enforcing strict data residency guardrails, enterprises can achieve a level of security that often surpasses traditional on-premise data centers.

What is the difference between cloud migration and cloud modernization?

Cloud migration focuses on moving workloads from on-premise infrastructure to the cloud, whereas modernization involves re-architecting applications to utilize cloud-native features. Migration is the initial step that establishes the foundation, while modernization unlocks advanced capabilities like serverless computing and agentic AI integration. Both are essential components of a digital transformation journey, but modernization is what ultimately drives maximum scalability and long-term performance improvements.

How do I choose between a Lift-and-Shift and a Refactoring strategy?

Choosing between Lift-and-Shift and Refactoring depends on your application’s criticality and your digital maturity goals. Lift-and-Shift is ideal for organizations needing a fast data center exit with low risk and minimal upfront investment. In contrast, Refactoring is the preferred choice for core applications that require maximum scalability or AI integration. A balanced approach often involves rehosting non-critical systems while refactoring high-value workloads to ensure optimal ROI.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.


With 99% of organizations reporting API security incidents in the past year, the bridge between technical connectivity and business stability has never been more fragile. You’ve likely felt the strain of fragmented system integrations causing unexpected downtime; perhaps you’ve even struggled to scale manual testing for complex microservices that demand constant updates. By leveraging professional api testing services, enterprises can finally bridge this gap between rapid deployment and absolute reliability. We understand that maintaining a seamless third-party ecosystem while mitigating risks like Broken Object Level Authorization (BOLA) is a daunting challenge for any IT leader.

This guide explores how a strategic approach to API quality ensures zero-defect data migrations and accelerates your CI/CD pipelines through advanced automation. By combining technical expertise with adaptable delivery models, Test Triangle helps businesses eliminate the 55 minutes of weekly productivity lost to API failures. We’ll examine the latest 2026 standards, including NIST SP 800-228-upd1 and the integration of Java 21 for modern frameworks, to provide a roadmap for your digital transformation journey.

Key Takeaways

  • Learn why validating logic at the message layer provides a more robust and faster feedback loop than traditional UI-based testing methods.
  • Discover how professional api testing services leverage service virtualization and schema mapping to ensure scalable, risk-free environment configurations.
  • Identify strategies to mitigate injection attacks and unauthorized access by aligning your security protocols with the OWASP API Security Top 10.
  • Understand the methodology for integrating continuous quality assurance within Jira and ServiceNow environments to accelerate your DevOps release cycles.
  • Explore how the “Technology. Talent. Transformation.” framework empowers enterprises to navigate complex digital migrations with precision and stability.

The Strategic Role of API Testing Services in Enterprise Architecture

In 2026, APIs have evolved into the indispensable connective tissue of global IT infrastructure, facilitating nearly all high-value data exchanges between disparate systems. Professional api testing services act as a strategic safeguard within this ecosystem, validating complex business logic, security protocols, and performance metrics at the message layer. Unlike traditional testing that focuses on the surface level, these services dive into the “headless” architecture to ensure that every request and response meets rigorous enterprise standards. By adopting a “Shift-Left” philosophy, organizations can identify critical flaws during the design and development phases rather than after deployment. This proactive approach significantly reduces the cost of software defects, which often escalate by 10x to 100x when discovered in production environments. Utilizing established API testing methodologies ensures that your technical execution aligns perfectly with long-term business stability.

Why Headless Testing Outperforms UI-Based Validation

Speed is the primary differentiator in modern QA cycles. While UI automation scripts often require several minutes to navigate through visual elements, API tests execute in mere seconds, providing near-instantaneous feedback to development teams. This efficiency is paired with superior stability; API contracts and schemas remain consistent even when user interfaces undergo frequent aesthetic updates. To bridge the gap between legacy UI testing and modern headless requirements, many enterprises leverage managed outsourcing services to access specialized talent that can build and maintain these high-speed automation suites.

Business Continuity and the Cost of API Failure

Broken integrations represent more than just technical glitches; they’re catastrophic events that lead to data corruption, operational paralysis, and rapid customer churn. API downtime is a direct threat to revenue-generating digital workflows. When a single endpoint fails in a microservices architecture, the ripple effect can bring down an entire enterprise platform, resulting in an average loss of 55 minutes of weekly productivity per employee. Establishing robust api testing services is no longer optional but a prerequisite for successful digital transformation services. By securing the data exchange layer, Test Triangle helps organizations maintain the “flawless” operational continuity required to thrive in a hyper-connected economy.

Core Methodologies: Implementing a Scalable API Testing Strategy

Establishing a scalable framework for api testing services requires a methodical transition from mapping endpoints to continuous monitoring. By analyzing requirements first, architects define the expected data schemas and request-response pairs that drive the entire integration. Following this, environment configuration utilizes service virtualization to simulate external dependencies, which avoids the risks associated with using live production data. Aligning these environments with NIST security strategies ensures that the testing infrastructure itself remains resilient against modern threats. Once the environment is stable, engineers design test suites that cover functional paths, negative scenarios, and complex edge cases. These tests are then integrated into the CI/CD pipeline for automated execution, while real-time dashboards provide the quality insights necessary for informed decision-making.

Functional vs. Non-Functional API Testing

Validating the accuracy of status codes and payload structures constitutes the core of functional testing. This ensures that the business logic remains sound across every transaction. Conversely, non-functional testing assesses how the system behaves under extreme stress or high load, maintaining availability when traffic spikes. Complementing your API quality strategy with dedicated performance testing services ensures that your infrastructure can sustain enterprise-grade scalability under real-world conditions. Maintaining data integrity during these backend shifts is critical, as detailed in our guide on data migration testing. If you’re looking to refine your current QA framework, our team can help you evaluate your technical architecture to ensure long-term stability.

The Rise of AI-Augmented API Automation

The integration of artificial intelligence services has revolutionized how we approach scale. AI tools now analyze historical traffic patterns to predict potential failure points before they manifest in code. These systems generate synthetic test data at a scale previously impossible for manual teams to manage. While AI handles the repetitive heavy lifting, the Strategic Architect remains essential. Human expertise is still required to validate the complex logic and creative edge cases that autonomous tools might overlook. This synergy between “Talent” and “Technology” ensures that your api testing services remain both efficient and deeply insightful, providing a superior level of precision that pure automation cannot achieve alone.

API Testing Services: A Strategic Guide to Enterprise Connectivity and Quality in 2026

Security and Compliance: Mitigating Risks in Regulated Industries

By treating security as a foundational architectural layer rather than a post-development afterthought, enterprises can effectively neutralize the threat of unauthorized data access and injection attacks. In an era where over 90% of web-based attacks target APIs, professional api testing services provide the rigorous validation necessary to protect sensitive corporate assets. Adhering to the OWASP API Security Top 10 ensures that your defense strategy addresses critical vulnerabilities like Broken Object Level Authorization (BOLA) and Broken Authentication. By implementing automated test case generation for RESTful architectures, Test Triangle empowers organizations to conduct deep, white-box probing that uncovers hidden logic flaws before they can be exploited. This methodical approach transforms security from a reactive burden into a strategic advantage, ensuring that every endpoint remains resilient against the sophisticated threats of 2026.

Validation of encryption and authentication protocols, including OAuth and JWT, must occur at every individual endpoint to prevent cascading failures. In highly regulated sectors such as Finance, new standards like PSD3 and eIDAS have raised the baseline for Strong Customer Authentication (SCA). By integrating these compliance requirements directly into the testing lifecycle, we help global enterprises avoid the catastrophic costs associated with data breaches. Strategic architects prioritize the validation of these protocols to ensure that data exchange remains both secure and efficient across multi-cloud environments. This level of precision is what differentiates a “Trusted Partner” from a standard vendor, providing the institutional maturity required to manage complex digital infrastructures.

API Security Testing for Global Compliance

Navigating the intricate requirements of GDPR, HIPAA, and GxP requires a sophisticated blend of technical rigor and industry-specific knowledge. Our specialized Pharma IT staffing solutions provide the domain expertise needed to maintain rigorous audit trails and compliant testing environments. In 2026, an insecure API is a legal liability, not just a technical bug. By leveraging talent that understands the nuances of life sciences and banking, we ensure that your api testing services meet the highest global standards for regulatory adherence.

Data Integrity and Privacy Validation

Protecting Personally Identifiable Information (PII) is a paramount concern as data flows through increasingly complex microservices. We validate that PII is never exposed in API responses by enforcing strict data masking and anonymization protocols at the message layer. Validating end-to-end encryption within multi-cloud architectures ensures that data remains protected during transit and at rest. This focus on “flawless” data integrity helps organizations maintain customer trust while mitigating the risk of regulatory fines and reputational damage.

Integrating API Quality into the DevOps Pipeline

By embedding continuous quality assurance directly into the DevOps pipeline, enterprises transform their api testing services from a bottleneck into a catalyst for speed. Moving away from periodic, end-of-cycle validation allows teams to operate within a unified ecosystem where Jira and ServiceNow serve as the primary conduits for quality data. When developers receive instant feedback on their code commits, the entire release cycle accelerates, reducing the average enterprise’s weekly productivity loss of 55 minutes caused by API failures. Leveraging a strategic Atlassian implementation ensures that every API defect is tracked alongside development tasks, creating a transparent workflow that prioritizes resolution before code reaches production.

The role of mock services and service virtualization cannot be overstated in parallel development workflows. These technologies allow front-end teams to build against stable API definitions while back-end services are still under construction, effectively eliminating the “waiting for deployment” phase. This synchronization ensures that integration issues are caught in the design phase, long before they can impact the end-user experience or business continuity.

Continuous Integration and the API Feedback Loop

Automating regression suites to run with every code commit is the only way to maintain stability in a microservices architecture. This approach identifies contract breaks immediately, preventing the accumulation of technical debt that often consumes 60-80% of testing time in maintenance alone. Whether your stack utilizes Postman 12.9.7, SoapUI, or custom frameworks, the focus remains on ensuring that “headless” validation occurs as early as possible. Identifying these flaws early reduces the cost of remediation and keeps the digital transformation journey on schedule.

Optimising Workflows with ServiceNow and Atlassian

By integrating QA results into IT service management solutions, Test Triangle provides stakeholders with a “single pane of glass” view of software quality. This visibility is essential for IT managers who need to see the direct correlation between technical health and business outcomes. Using ServiceNow to manage the API lifecycle and incident response allows organizations to automate the transition from a detected production failure to a documented resolution task. This synergy between talent and technology empowers your team to drive digital transformation without sacrificing operational stability. If you’re ready to modernize your deployment pipeline, contact our consultants today to build a custom automation strategy.

Test Triangle: Your Trusted Partner for API Transformation

By aligning advanced technological frameworks with elite human expertise, Test Triangle serves as a high-level corporate partner for global enterprises navigating the complexities of modern connectivity. We don’t just provide api testing services; we architect resilient digital foundations that withstand the pressures of a hyper-connected economy. Our approach leverages the robust ecosystems of AWS, Atlassian, and ServiceNow to ensure that your connectivity is both scalable and secure. By combining this technical rigor with an adaptable delivery model, we help businesses optimize their workflows and reduce the operational costs associated with integration failures. This synergy allows us to move beyond simple bug-finding, driving strategic architectural improvements that empower long-term stability and growth through our core philosophy: Technology. Talent. Transformation.

Finding the right expertise to manage complex microservices is often the primary hurdle for modern IT leaders in 2026. We bridge this talent gap by providing access to a global pool of specialized QA engineers and pharma-compliant experts who understand the nuances of regulated sectors. Whether you require a fully managed service or targeted staffing solutions for a specific project, our flexible engagement models adapt to your unique operational requirements. This versatility ensures that you have the right talent in place to navigate the 60-80% of API testing time typically lost to manual maintenance. Our talent isn’t just skilled in code; they’re experts in the industry-leading platforms that drive your business forward.

The Strategic Architect Persona

The personality of Test Triangle is that of a Strategic Architect, a steady hand in a fast-changing technological landscape. We maintain a proven track record across Banking, Healthcare, and Retail, where precision isn’t just a goal but a baseline requirement for survival. Our commitment to mitigating risks through disciplined execution allows your team to focus on core innovation while we manage the intricate details of your digital transformation. We’ve assisted global enterprises in achieving zero-defect data migrations by applying a rigorous, methodical approach to every endpoint and integration layer, ensuring that your api testing services translate into tangible business value.

Get Started with a Comprehensive API Audit

Elevating your quality standards begins with a clear, objective understanding of your current maturity level. Our tailored consulting services identify immediate security and performance gaps that could threaten your revenue-generating workflows or lead to regulatory non-compliance. By conducting a comprehensive API audit, we provide the strategic roadmap necessary for a flawless digital journey. We’ll help you evaluate your technical architecture against the latest 2026 standards, ensuring your systems are robust, secure, and future-ready. Contact our experts today to elevate your API quality standards.

Secure Your Digital Future Through Strategic API Excellence

The evolution of enterprise architecture in 2026 demands more than just basic connectivity; it requires a flawless integration layer that can withstand the rigors of global data exchange. By prioritizing a “Shift-Left” approach and integrating security protocols like the OWASP API Security Top 10, organizations can neutralize risks before they escalate into costly production failures. Professional api testing services provide the strategic bridge needed to align technical execution with long-term business stability. Whether you’re navigating the complexities of PSD3 in finance or GxP requirements in life sciences, having a steady hand to guide your digital transformation is essential for maintaining a competitive edge.

Test Triangle stands as your Trusted Partner for Global Enterprises, offering specialized expertise in Pharma and Financial IT compliance to ensure your infrastructure remains robust and secure. By leveraging our core philosophy of Technology. Talent. Transformation., we help you accelerate release cycles and optimize your DevOps pipeline within Jira and ServiceNow environments. It’s time to move beyond reactive bug-fixing and embrace a visionary approach to quality that drives scalable growth. Partner with Test Triangle to secure and optimise your API infrastructure. Contact us today. We look forward to helping you achieve operational perfection.

Frequently Asked Questions

What are the main benefits of outsourcing API testing services?

Outsourcing allows enterprises to leverage specialized talent and flexible engagement models to scale their quality assurance efforts without the overhead of internal hiring. By partnering with a Strategic Architect, businesses gain access to established frameworks that reduce the 60-80% of time typically spent on test maintenance. This approach ensures that your digital transformation remains on schedule while mitigating the risks associated with internal skill gaps.

How does API testing differ from unit testing and integration testing?

API testing validates the logic, security, and performance at the message layer, whereas unit testing focuses on isolated code snippets and integration testing examines the interaction between multiple modules. By targeting the “headless” layer, api testing services identify defects that unit tests might miss due to their narrow scope. This strategic focus ensures that the connective tissue of your enterprise architecture remains robust under real-world conditions.

Can API testing be fully automated in a DevOps environment?

Full automation is achievable by integrating regression suites directly into the CI/CD pipeline using tools like Jira and ServiceNow. Automating these workflows provides instant feedback to developers with every code commit; this effectively eliminates manual bottlenecks in the release cycle. By combining technical expertise with adaptable delivery models, Test Triangle helps organizations achieve a “single pane of glass” view of quality through automated end-to-end workflows.

What tools are most commonly used for enterprise API testing in 2026?

Enterprise teams in 2026 primarily utilize Postman 12.9.7 for collaboration and Karate v2 for its Java 21+ compatibility and BDD capabilities. Other essential tools include REST Assured 5.5.7 and AI-native platforms that autonomously generate synthetic test data at scale. Integrating these tools within an Atlassian ecosystem ensures that technical execution remains aligned with global industry standards and enterprise-grade security requirements.

How much does it cost to implement professional API testing services?

While total project costs vary based on complexity, industry data from March 2026 indicates that API security protection typically ranges between $200 and $600 per API monthly. A dedicated API penetration testing assessment generally costs between $3,000 and $10,000 per engagement. Investing in professional api testing services helps avoid the catastrophic financial impact of data breaches, which affected 57% of organizations in the last two years.

Is API testing necessary if we already have comprehensive manual testing?

Manual testing is insufficient for modern microservices architectures because it cannot validate the thousands of request-response pairs generated by complex integrations. API testing provides a level of precision and speed that manual efforts simply can’t match, particularly when identifying Broken Object Level Authorization (BOLA) risks. Shifting to an automated API strategy allows your team to focus on high-level architectural improvements rather than repetitive, error-prone manual checks.

How does API testing impact the speed of software delivery?

API testing significantly accelerates software delivery by providing a faster feedback loop than traditional UI-based validation. Since API tests execute in seconds rather than minutes, they allow for more frequent deployments without sacrificing stability or security. This efficiency is a core component of “Transformation” through “Technology,” helping enterprises stay ahead in a fast-changing technological landscape by reducing time-to-market for new features.

What are the most common security vulnerabilities found during API testing?

The most common vulnerabilities identified during testing align with the OWASP API Security Top 10 (2023 Revision), which remains the active standard in 2026. These include Broken Object Level Authorization (BOLA), Broken Authentication, and Broken Object Property Level Authorization. Validating these risks at every endpoint ensures that PII remains protected and that your organization adheres to global regulations like PSD3 and GDPR.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.

By 2026, industry analysts project that 83% of enterprise migrations will fail to meet their original timelines or budget targets due to inadequate validation strategies. You likely recognize that mapping legacy schemas to modern cloud platforms is a high-stakes endeavor where a single corrupted record can trigger regulatory fines or halt production in sensitive sectors like Pharma and Finance. It’s natural to fear the downtime and “surprises” that often plague post-go-live environments when critical data integrity is left to chance.

By leveraging a robust, automated approach to data migration testing, Test Triangle empowers your organization to achieve a flawless transition while maintaining strict compliance standards. This guide provides a strategic framework to optimize your validation protocols, ensuring every byte is accounted for and audit-ready. We’ll explore the practical steps to build a repeatable testing engine that delivers digital transformation through our signature commitment to Technology. Talent. Transformation. As your trusted partner, we’ll help you eliminate migration risks and drive long-term operational stability by following a methodical, disciplined roadmap to success.

Key Takeaways

  • Navigate the evolution from simple storage moves to complex cloud-to-cloud transformations by implementing a structured 5-phase validation roadmap.
  • Establish a robust ROI for your migration projects by leveraging strategic risk mitigation frameworks tailored for high-compliance sectors like Finance and Pharmaceuticals.
  • Optimize validation accuracy by transitioning from manual spot-checks to full-coverage automated ETL testing and AI-driven anomaly detection.
  • Master the strategic framework of data migration testing to guarantee data integrity and eliminate business disruptions during complex system transitions.
  • Accelerate your digital evolution by aligning Technology, Talent, and Transformation to deliver flawless migrations within the Atlassian and ServiceNow ecosystems.

What is Data Migration Testing and Why is it Critical in 2026?

By establishing a rigorous validation framework, enterprises ensure that their most valuable digital assets transition between environments without compromise. In the 2026 technological landscape, data migration testing has evolved from simple storage transfers into complex, multi-layered cloud-to-cloud transformations. Understanding What is Data Migration? remains the foundation for any project; however, modern testing must now account for the intricate ETL (Extract, Transform, Load) processes that define today’s hybrid-cloud ecosystems. Failure to validate these transitions can result in a 25% increase in operational downtime and severe compliance penalties under evolving global data protection regulations.

As a Strategic Architect in the quality assurance space, Test Triangle recognizes that data integrity is the heartbeat of the modern enterprise. By leveraging advanced automation and strategic oversight, we help businesses mitigate the risks of data loss and corruption. Positioning ourselves as a Trusted Partner, we focus on the intersection of Technology, Talent, and Transformation to deliver flawless results in high-stakes environments like Banking and Life Sciences. The cost of failure in 2026 is no longer just a technical glitch; it represents lost revenue, regulatory fines, and permanent brand damage.

The Core Objectives of Migration Validation

By prioritizing accuracy and completeness, validation teams prevent data corruption during the critical ETL cycle. This process ensures that every record aligns with the target schema while maintaining functional business logic in the new environment. Beyond simple accuracy, teams must validate performance and scalability under real-world data volumes. In 2025, industry reports indicated that 60% of migration failures stemmed from poor performance testing, making high-volume stress testing a non-negotiable requirement for 2026 enterprise projects. Ensuring your infrastructure can handle peak loads after a migration requires dedicated performance testing services that validate system resilience before and after the cutover.

Data Migration vs. Standard Software Testing

While functional software testing is often stateless, data migration testing is inherently stateful and data-centric. Standard testing focuses on how a feature behaves; migration testing focuses on how data lives and changes across complex schemas. This requires a specialized strategic approach to preserve metadata and historical records. By analyzing schema complexity early in the lifecycle, Test Triangle ensures that historical context is never lost, maintaining the continuity required for regulatory audits and long-term business intelligence. This distinction is vital for maintaining operational stability during digital transformation.

A 5-Phase How-to Guide for Effective Data Migration Testing

By aligning technical rigor with strategic business objectives, enterprises ensure that data migration testing acts as a catalyst for growth rather than a bottleneck. Test Triangle focuses heavily on the “Transformation” pillar of our core triad, ensuring that legacy data evolves into a high-value asset during the transition. Establishing a structured roadmap from pre-migration audits to post-migration sign-off mitigates the risks inherent in complex digital infrastructures.

Phase 1 & 2: Pre-Migration Audit and Schema Mapping

Identifying “dirty data” early prevents downstream failures that compromise system integrity. A 2024 industry report indicated that poor data quality costs organizations an average of $12.9 million annually in operational inefficiencies. Conducting a source system data quality assessment allows teams to clean records before they enter the new environment. Creating a comprehensive Source-to-Target Mapping (STM) document is a critical step in this process. This document must detail every field, data type, and transformation logic while verifying mandatory fields and valid value lists. Utilizing the Modernization and Migration Management (M3) Playbook provides a structured framework for these early-stage audits, ensuring that the schema aligns with global standards before the move begins.

Phase 3 & 4: Execution and Automated Validation

Moving from staging environments to production cutover requires precision and real-time visibility. Running the migration tool with active error logging allows the team to capture schema mismatches or timeout issues as they occur. We leverage automated scripts to compare record counts and checksums across systems, ensuring that no data is lost or corrupted during transit. Parallel Testing is a method for comparing old and new system outputs simultaneously to ensure functional parity. By automating these repetitive validation tasks, enterprises accelerate their delivery timelines while maintaining superior accuracy. This phase bridges the gap between technical execution and business outcomes, providing the reliability that global enterprises demand.

Phase 5: Post-Migration and User Acceptance Testing (UAT)

Securing stakeholder sign-off depends on transparent reporting and verifiable audit trails. Performing end-to-end business process testing with the migrated data set confirms that the new system handles real-world scenarios as expected. It’s vital to have a “rollback” strategy ready to execute within a 60-minute window in case of critical production failures. This level of preparation protects operational stability and reinforces the role of a Strategic Architect in the migration process. Organizations that engage with a trusted testing partner typically see a 35% reduction in post-go-live defects. Through disciplined execution and talent-driven strategies, we help businesses navigate these transitions with total confidence.

Data Migration Testing: The 2026 Enterprise Guide to Flawless Transitions

Strategic Risk Mitigation in High-Compliance Industries

Enterprise leaders often view data migration testing as a sunk cost, yet this perspective ignores the staggering ROI of risk avoidance. A 2023 IBM report indicates the average cost of a data breach reached $4.45 million, a figure that pales in comparison to the potential fines for regulatory non-compliance in the Pharmaceutical or Financial sectors. For these industries, data validation isn’t a choice; it’s a legal mandate. By shifting the focus from “cost” to “capital preservation,” organizations protect their market standing and operational continuity.

In the Pharmaceutical realm, GxP standards dictate that every record must remain legible, original, and accurate throughout its lifecycle. Any discrepancy during a move can invalidate years of clinical research. This case study on data migration in healthcare illustrates how rigorous validation protocols prevent the catastrophic loss of patient data integrity. By leveraging Test Triangle’s 15+ years of experience in Pharma IT staffing, we provide the specialized talent required to navigate these complex regulatory waters. Our experts ensure that GDPR and GxP documentation is audit-ready, transforming testing from a hurdle into a strategic advantage. Technology. Talent. Transformation. This triad ensures that your migration meets the highest global standards of precision.

Ensuring Data Sovereignty and Security

Security isn’t a final layer; it’s the foundation of the entire migration process. We prioritize testing for AES-256 encryption at rest and TLS 1.3 for data in transit to prevent interception. Our teams meticulously validate that Role-Based Access Controls (RBAC) map perfectly from legacy environments to the new architecture. This prevents the “privilege creep” that often occurs during transitions. For global enterprises, we strictly enforce data residency requirements, ensuring that localized data stays within its legal jurisdiction to satisfy regional sovereignty laws.

Handling Large-Scale Data Volumes

Managing migrations involving 50 million+ records requires a tiered approach to data migration testing to avoid project stagnation. We utilize “Full Population” testing for critical financial fields while applying “Statistical Data Sampling” for non-critical metadata to accelerate timelines. Beyond accuracy, we performance test the target system under peak load. This confirms that the new infrastructure won’t buckle under the weight of the migrated data. Our flexible engagement models allow us to scale testing resources dynamically, ensuring that high volumes don’t translate into high delays. Complementing this with enterprise-grade performance testing services ensures your target environment can sustain the demands of petabyte-scale workloads long after the migration is complete.

Leveraging Automation and AI in Modern Data Validation

The era of manual spot-checks is over. By 2026, the sheer volume of enterprise information makes traditional sampling techniques a liability rather than a strategy. Modern data migration testing now demands full-coverage automated ETL (Extract, Transform, Load) validation to ensure every record survives the transition without loss or corruption. High-performing IT departments have shifted toward 100% data verification, utilizing automated scripts that compare source and target environments in real-time. This transition reduces the risk of post-migration defects by 92%, allowing teams to focus on strategic optimization instead of manual error correction.

AI-Driven Schema Mapping and Anomaly Detection

AI has fundamentally changed how we handle structural differences between systems. By leveraging machine learning to suggest mappings between disparate legacy and modern schemas, organizations reduce manual mapping effort by 40%. These AI models analyze historical metadata to predict the most accurate destination for complex data points. Automated data profiling tools now identify outliers and potential corruption points that traditional scripts often miss. The next evolution in this space is “Agentic AI,” where autonomous agents generate and execute test cases dynamically as metadata changes during the migration lifecycle. This proactive approach ensures that data migration testing remains robust even when source structures are fluid.

Integrating Testing into the DevOps Pipeline

Treating “Data as Code” is a core requirement for a modern CI/CD environment. By integrating automated regression tests directly into the DevOps pipeline, enterprises ensure that migrating a specific dataset doesn’t break existing application integrations or downstream analytics. This continuous validation cycle provides immediate feedback to engineers, preventing small errors from cascading into system-wide failures. In the context of a 2026 data cutover, Smoke Testing is the automated, high-velocity validation of core schema integrity and critical data pathways executed within minutes of the load to authorize the final transition to production.

Selecting the right migration testing tools requires a structured framework focused on long-term scalability. Consider these four pillars during your evaluation:

  • Scalability: The tool must handle petabyte-scale loads without performance degradation.
  • Interoperability: It should support a diverse ecosystem, including Snowflake, Databricks, and legacy SQL systems.
  • Compliance: Built-in features for GDPR and CCPA masking are essential for maintaining security.
  • Integration: Seamless connectivity with Jira Service Management allows for automated incident tracking and resolution.

By combining technical expertise with adaptable delivery models, Test Triangle helps global enterprises navigate these technological shifts. We act as a Strategic Architect to ensure your infrastructure remains stable throughout the transformation process. To elevate your next project, explore how our Automation Testing services can drive a flawless transition for your business. Ensuring that application integrations remain intact after a migration also depends on robust api testing services that validate every connectivity layer between your migrated systems and third-party ecosystems.

The Test Triangle Approach: Technology, Talent, and Transformation

By aligning technical precision with strategic foresight, Test Triangle functions as a Strategic Architect for the world’s most complex enterprise transitions. We recognize that moving legacy systems to modern environments is a high-stakes endeavor where data integrity is the only acceptable baseline. Our methodology centers on the powerful triad of Technology, Talent, and Transformation. This approach ensures that data migration testing becomes a value-driving phase rather than a bottleneck, allowing organizations to leverage their information assets with total confidence.

Specialized Ecosystem Expertise

Migrating to Atlassian Cloud presents unique challenges that standard testing protocols often miss. Beyond simple record transfers, organizations must account for app compatibility and custom API configurations that can break during the shift. As a verified partner for both Atlassian and AWS, Test Triangle builds bespoke validation frameworks for Jira and Confluence migrations. We focus on the intricate dependencies between data sets and third-party plugins. For ServiceNow implementations, our strategy involves validating business workflows alongside the raw data. We ensure that 100% of automated logic remains functional post-migration, protecting the critical service desk operations that keep your business running.

Flexible Staffing for Migration Projects

The talent gap remains a primary hurdle for IT leaders in 2026. Test Triangle bridges this void by offering adaptable delivery models that cater to the specific demands of a project. By utilizing specialized contract staff for short-term migration bursts, enterprises can increase their testing throughput by up to 40% without the long-term burden of permanent hires. We combine the high-level strategic consulting found in our Dublin and London offices with the cost-efficiency of offshore centers. This hybrid model provides a continuous testing cycle that accelerates go-live dates while maintaining a robust security posture.

Our clients consistently see a reduction in project risk through this “Trusted Partner” engagement style. It’s about having the right experts in place at the right time to prevent data loss and system downtime. Consult with our migration experts today to secure your project’s success and ensure your infrastructure is ready for the next decade of growth.

The path to a flawless digital transformation requires more than just tools; it demands a partner who understands the architectural nuances of your technical stack. Test Triangle provides the steady hand needed to navigate these shifts, ensuring your move to the cloud or a new ERP is seamless, secure, and strategically sound. By optimizing your data migration testing phase, we help you turn a complex technical requirement into a competitive advantage for the future.

Securing Your Digital Legacy Through Strategic Validation

Navigating the complexities of 2026’s digital landscape requires more than basic data transfer; it demands a rigorous 5-phase validation framework that eliminates architectural debt. By integrating AI-driven automation and modern risk mitigation strategies, global enterprises can ensure 100% data integrity while meeting the strict compliance standards of the Banking and Life Sciences sectors. Successful data migration testing isn’t just a technical checkbox. It’s a strategic imperative that safeguards your operational stability during large-scale transformations.

As a Strategic Partner for Atlassian and ServiceNow, Test Triangle brings a proven track record of excellence across four global regions, including Ireland, the UK, USA, and India. We leverage our signature framework of Technology, Talent, and Transformation to deliver robust, scalable results for the world’s most demanding infrastructures. Our flexible engagement models ensure that your specific business outcomes remain the priority throughout the entire migration lifecycle. You don’t have to face these technical hurdles alone when you have a seasoned architect by your side.

Elevate your infrastructure today. Partner with Test Triangle for a Flawless Data Migration Strategy and accelerate your journey toward a secure, optimized digital future.

Frequently Asked Questions

What is the difference between data migration testing and data reconciliation?

Data migration testing encompasses the entire validation lifecycle, while data reconciliation specifically focuses on verifying that the record counts and financial totals match between source and target systems. By executing automated reconciliation scripts, teams ensure that 100% of the datasets are accounted for during the transfer. This granular verification acts as a subset of the broader testing strategy, which also includes schema validation and performance benchmarking.

How much of my data should I test during a migration?

Enterprises should aim for 100% data reconciliation of all records while utilizing a 10% to 15% stratified sampling size for complex functional validation. By leveraging a risk-based approach, you prioritize high-value business entities such as customer profiles or financial ledgers. This strategy ensures that critical data paths are 100% accurate without the prohibitive costs of manual verification for every non-essential field.

Can data migration testing be fully automated in 2026?

Full automation of data migration testing is achievable for 95% of standard ETL processes in 2026, though human oversight remains vital for final architectural sign-off. By integrating AI-driven validation tools with Jira Service Management, teams can automate schema mapping and anomaly detection. This reduces manual effort by 80% and accelerates the transition timeline for global enterprises managing petabyte-scale migrations.

What are the most common challenges in enterprise data migration testing?

The primary challenges include mapping 20-year-old legacy schemas to modern cloud structures and managing the latency of moving 500+ terabytes across hybrid environments. By identifying these bottlenecks early, Test Triangle helps organizations prevent the 40% project delay typically caused by poor source data quality. Success requires a robust strategy that addresses inconsistent naming conventions and missing metadata before the first record moves.

How does data migration testing impact business downtime?

Rigorous testing reduces planned downtime by 60% by enabling a dry run methodology that identifies performance chokepoints before the actual cutover. By simulating the migration in a mirrored environment, technical teams can refine the execution window to fit within a standard 48-hour weekend block. This precision ensures that global operations resume on Monday morning without the risk of extended system outages.

What role does UAT play in the data migration lifecycle?

User Acceptance Testing (UAT) serves as the final gate where business stakeholders verify that the migrated data supports 100% of their daily operational workflows. By involving end-users from the finance and sales departments, you ensure that the target system’s front-end displays data correctly. This phase is critical because it catches logic errors that automated technical scripts might overlook during the initial data migration testing phase.

Why is a rollback strategy essential for migration testing?

A rollback strategy is essential because it provides a 100% guaranteed recovery path if the production cutover encounters a catastrophic failure. By establishing clear Point of No Return milestones, project managers can revert to the legacy system within a 4-hour window. This safety net protects the organization’s reputation and ensures that data integrity is maintained even if the primary migration attempt fails.

How do GxP regulations affect testing for pharmaceutical companies?

GxP regulations require pharmaceutical companies to maintain a 100% documented audit trail and validated state throughout the migration process as mandated by EudraLex Volume 4 Annex 11. By implementing rigorous ALCOA+ principles, firms ensure that data remains attributable and legible. Failure to comply with these 21 CFR Part 11 standards can result in significant regulatory fines or the suspension of manufacturing licenses.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.