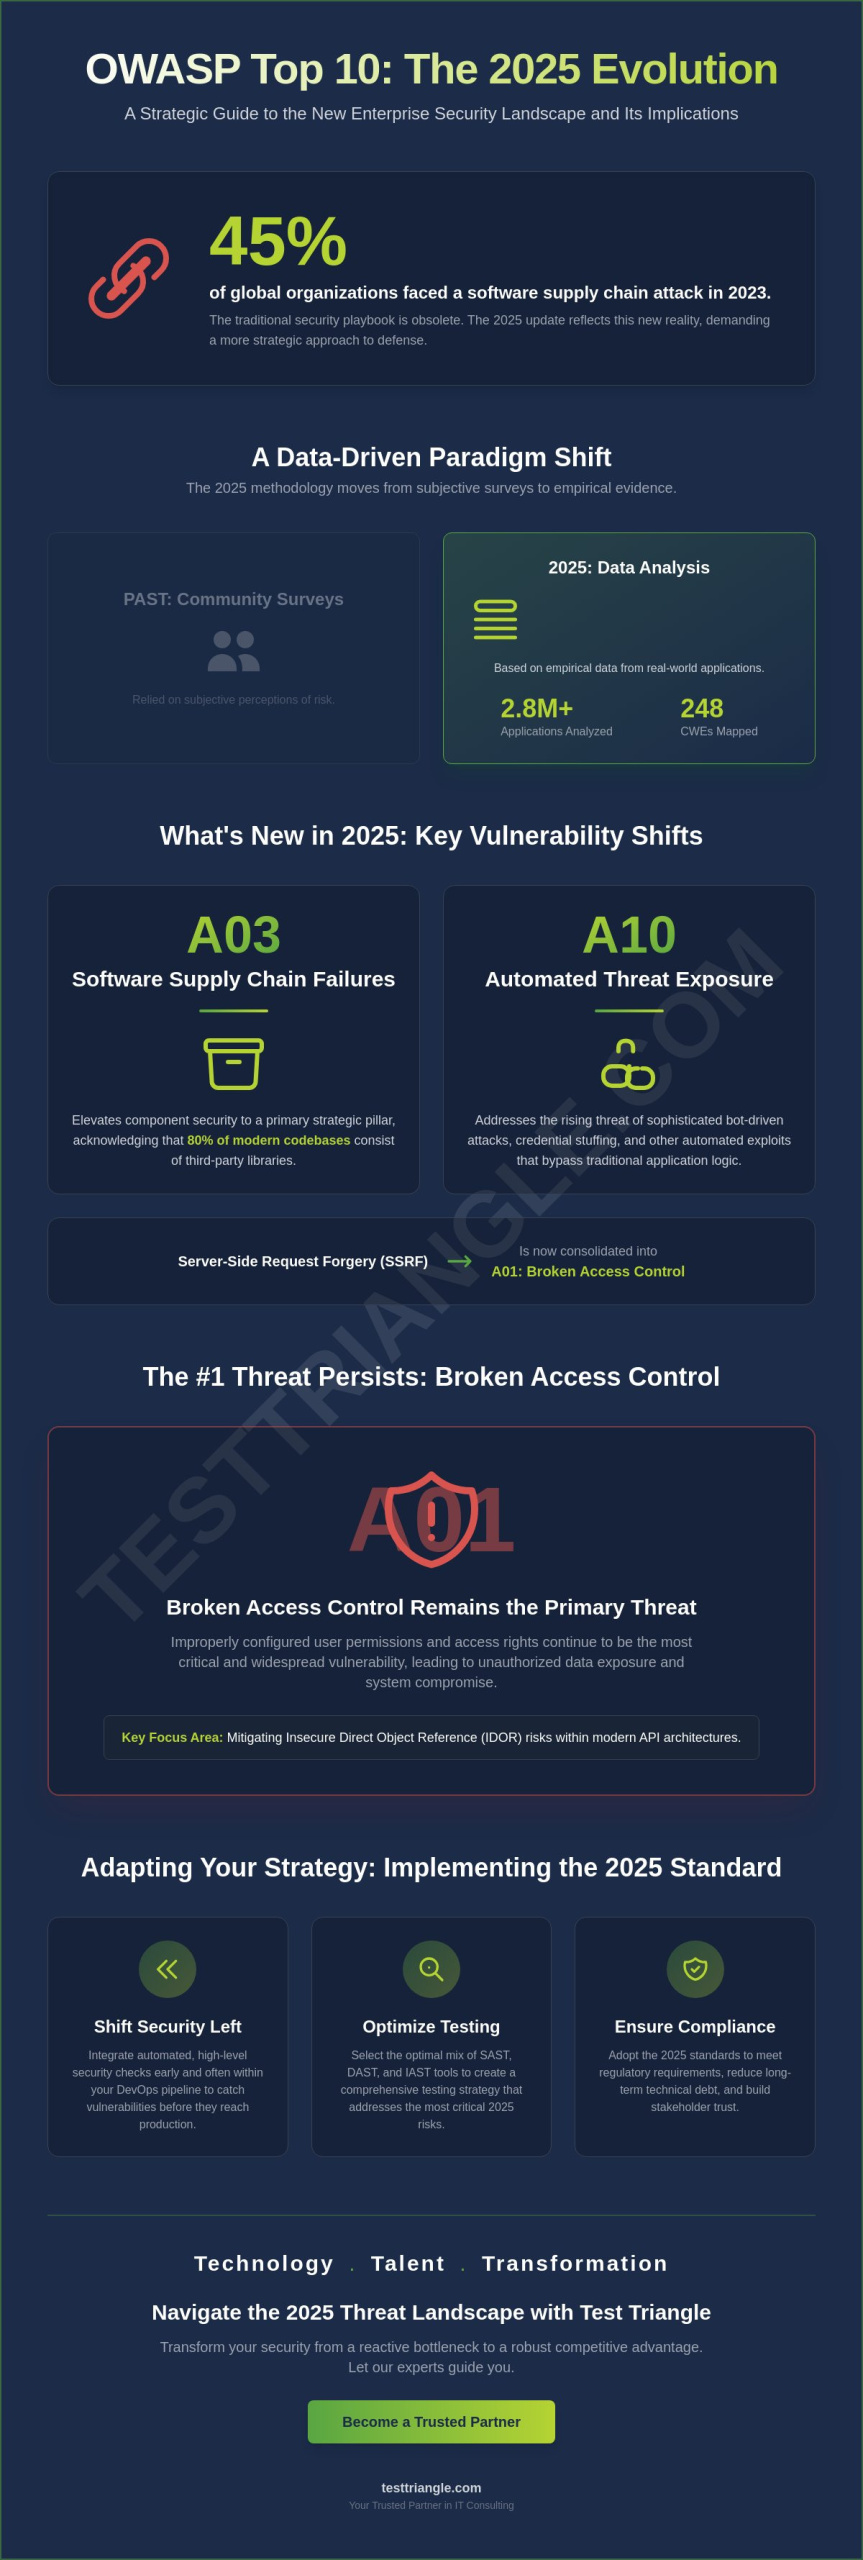
In a landscape where 45% of global organizations reported a software supply chain attack in 2023, the traditional security playbook is rapidly becoming obsolete. You’ve likely felt the mounting pressure of integrating complex security protocols into high-velocity DevOps pipelines while managing an increasingly volatile risk surface. It’s difficult to maintain a flawless defense when vulnerability categories evolve faster than your internal documentation can keep pace. Staying ahead of the owasp top 10 2025 news is no longer just a compliance checkbox; it’s a strategic requirement for any enterprise committed to long-term operational stability.

By aligning technical rigor with strategic foresight, Test Triangle helps global businesses transform their security posture from a reactive bottleneck into a robust competitive advantage. In this article, you’ll discover the critical updates in the 2025 framework and learn how to leverage these insights to optimize your testing strategy. We’ll provide a clear understanding of emerging risks and actionable steps for compliance. Our goal is to empower your team to drive digital transformation through our core philosophy: Technology. Talent. Transformation. As your Trusted Partner, we’ll ensure your security roadmap is both visionary and deeply practical.

Key Takeaways

  • By analyzing data from millions of applications, you will understand how the latest owasp top 10 2025 news reshapes the global standard for enterprise application security and risk awareness.
  • Identify the two entirely new vulnerability categories introduced this year and learn why the consolidation of SSRF into Access Control requires a strategic update to your defense protocols.
  • Gain actionable insights into why Broken Access Control remains the primary threat to digital stability and how to effectively mitigate IDOR risks within modern API architectures.
  • Elevate your DevOps pipeline by integrating high-level security checks and selecting the optimal mix of SAST, DAST, and IAST tools to address the most critical 2025 risks.
  • Leverage our “Technology, Talent, and Transformation” framework to transition from a reactive security posture to a robust, architected defense led by a trusted strategic partner.

The Evolution of Web Security: Understanding the OWASP Top 10 2025

The OWASP Top 10 remains the definitive global benchmark for application security awareness, providing a critical lens through which enterprises view digital risk. As organizations prepare for the 2026 fiscal year, the latest owasp top 10 2025 news signals a fundamental change in the security paradigm. By moving beyond a simple list of technical flaws, the OWASP organization now provides a strategic roadmap for systemic resilience. This update isn’t just a routine refresh. It’s a call to action for enterprises to shift their focus from identifying symptoms to addressing the root-cause vulnerabilities that lead to catastrophic breaches.

Strategic security requires a steady hand and a clear vision. By aligning with these updated standards, Test Triangle helps global enterprises leverage technology to protect their most valuable assets. This evolution is critical for any firm navigating digital transformation, as it establishes a foundation of trust and operational stability. Security is no longer a peripheral concern; it’s the core of business continuity and enterprise growth.

The Methodology Behind the 2025 Update

The 2025 update utilizes a rigorous, data-driven approach that analyzes 2.8 million applications across diverse industries. This methodology marks a departure from the community-survey models used in previous years, which often relied on subjective perceptions of risk. By mapping findings to 248 specific Common Weakness Enumerations (CWEs), the framework provides an empirical basis for security investment. This granular detail allows IT leaders to:

  • Identify high-frequency vulnerabilities across complex application portfolios.
  • Optimize resource allocation by targeting systemic weaknesses rather than isolated bugs.
  • Drive measurable improvements in code quality and deployment safety.

This evidence-based strategy ensures that the latest owasp top 10 2025 news reflects the actual threats facing modern digital infrastructures. It allows for a more disciplined approach to risk management that prioritizes actual data over industry trends.

Why Compliance with 2025 Standards Matters

Adhering to the 2025 standards is essential for maintaining regulatory compliance in highly scrutinized sectors like finance and healthcare. By adopting these benchmarks, organizations demonstrate a commitment to superior security that satisfies both auditors and stakeholders. Implementing these standards early reduces the long-term maintenance costs and technical debt that typically follow a security breach. It’s a proactive investment in the brand’s reputation and operational integrity. As a Trusted Partner, Test Triangle emphasizes that security isn’t a hurdle to innovation but an accelerant for growth. Through the synergy of Technology, Talent, and Transformation, businesses can achieve a robust security posture that supports long-term success and global scalability.

What’s New in 2025? Key Shifts in the Vulnerability Landscape

By analyzing the strategic updates within the official OWASP Top 10 2025, global enterprises can identify a decisive pivot toward systemic architectural integrity. The latest owasp top 10 2025 news reveals that security is no longer confined to isolated code quality; it now encompasses the entire digital ecosystem. This shift reflects a landscape where 80% of modern application codebases consist of third-party libraries, necessitating a broader defensive perimeter.

The 2025 update introduces two entirely new categories that address the complexities of modern automation and artificial intelligence. First, A03:2025 – Software Supply Chain Failures elevates component security from a sub-task to a primary strategic pillar. Second, A10:2025 – Automated Threat Exposure addresses the rise of sophisticated bot-driven attacks and credential stuffing that bypass traditional logic. By integrating these categories, the OWASP Foundation acknowledges that cloud-native environments and configuration-driven apps require more than just “patching”; they require a robust, zero-trust architecture.

The consolidation of Server-Side Request Forgery (SSRF) into Access Control highlights a logical evolution in risk management. Security architects now recognize that SSRF is fundamentally a failure to enforce authorization at the network or service boundary. By grouping these risks, the 2025 framework helps organizations streamline their remediation efforts through a unified policy engine.

A03:2025 – Software Supply Chain Failures

The elevation of supply chain security to a standalone priority stems from a 45% increase in attacks targeting CI/CD pipelines and developer environments since 2022. Modern risks aren’t just limited to “old” code; they involve unverified APIs, compromised build tools, and malicious dependencies hidden in deep package trees. Software Supply Chain Failures represent the risk of unverified components. By leveraging strategic security testing, businesses can validate every link in their delivery chain to ensure that third-party integrations don’t become Trojan horses for enterprise data.

Consolidation and Re-ranking: The 2021 vs 2025 View

The hierarchy of risk has shifted significantly to reflect the reality of cloud-heavy infrastructures. Security Misconfiguration has climbed to the #2 spot, driven by the fact that 65% of cloud breaches now originate from preventable configuration errors rather than complex exploits.

  • A01: Broken Access Control (Remains #1 due to its persistent impact on data privacy)
  • A02: Security Misconfiguration (Moved up from #4 in 2021)
  • A03: Software Supply Chain Failures (New standalone category for 2025)
  • A04: Cryptographic Failures (Shifted down slightly as encryption standards mature)
  • A05: Injection (Now includes broader AI-driven injection patterns)

Merging standalone categories into broader umbrellas allows the OWASP Top 10 2025 news to focus on the root causes of failure rather than specific symptoms. This approach empowers a Trusted Partner to help clients build more resilient systems through Technology. Talent. Transformation.
OWASP Top 10 2026 News: Strategic Implications for Enterprise Security

Dominant Risks: Why Broken Access Control and Misconfigurations Still Lead

The OWASP Top 10 2025 reinforces a critical reality for enterprise leaders: Broken Access Control remains the most pervasive threat to digital integrity. Data from the OWASP Foundation indicates that 94% of applications tested exhibited some form of broken access control, with a mean incidence rate of 3.81%. This persistence is driven by the proliferation of modern APIs, where Insecure Direct Object References (IDOR) allow unauthorized users to manipulate parameters to access sensitive data. By failing to implement rigorous server-side validation, developers inadvertently leave doors open for catastrophic data exfiltration.

Recent owasp top 10 2025 news highlights that modern software engineering relies too heavily on vulnerable default configurations. While automated security testing identifies approximately 60% of common vulnerabilities, it often misses the nuanced logic flaws that lead to these breaches. By combining automated scans with strategic oversight, Test Triangle helps organizations identify these flaws early in the lifecycle, preventing costly post-deployment remediation.

The Complexity of Access Control in Distributed Systems

Managing permissions becomes exponentially harder as enterprises scale their microservices and Atlassian ecosystems. In a distributed architecture, a single user request might traverse 12 or more distinct services, increasing the surface area for privilege escalation. By adopting a “Least Privilege” architectural principle, organizations ensure that every module operates with the minimum necessary permissions. This strategic approach prevents lateral movement during a breach. Our teams leverage deep expertise in Jira and ServiceNow to optimize identity and access management (IAM) protocols, ensuring that your Technology. Talent. Transformation. strategy remains secure.

Mitigating Security Misconfigurations

Security misconfigurations frequently occur in cloud environments where 65% of breaches originate from human error in setting up container orchestration. By implementing “Security as Code,” enterprises automate the deployment of hardened configurations, preventing the drift that occurs during rapid release cycles. While automated scans catch open ports or default passwords, they cannot fully grasp complex business logic. Integrating Manual Testing alongside automated tools provides a robust defense against sophisticated exploits.

As a Trusted Partner, Test Triangle delivers a superior level of security by combining technical precision with strategic oversight. We ensure that every configuration aligns with global compliance standards, protecting your digital assets from the evolving threats identified in the owasp top 10 2025 news

Implementing the 2025 Standard: Shifting Security Left in your DevOps Pipeline

By embedding rigorous security protocols directly into the CI/CD pipeline, global enterprises can identify and neutralize vulnerabilities before they ever reach a production environment. The latest owasp top 10 2025 news confirms that reactive security models are failing to keep pace with rapid deployment cycles. To maintain a robust defense, organizations must leverage a strategic mix of Static Application Security Testing (SAST), Dynamic Application Security Testing (DAST), and Interactive Application Security Testing (IAST). This multi-layered toolset allows teams to scan source code, analyze running applications, and monitor execution flows simultaneously.

Building a “Security Culture” is the foundation of this transformation. When developers take direct ownership of code safety, the burden on security teams decreases and software quality improves. It’s a shift that requires more than just tools; it demands a fundamental change in how teams perceive their roles. By empowering engineers with the right training, enterprises ensure that security is a shared responsibility rather than an isolated checkpoint.

Automation vs. Manual Expertise

Automated tools excel at identifying 85% of common vulnerabilities, such as injection flaws or broken access controls, at incredible speeds. They provide the technical backbone of a modern security strategy. Human expertise remains indispensable for addressing A04:2025 – Insecure Design. This category focuses on architectural flaws that require a deep understanding of business logic which software can’t yet replicate.

To scale these efforts effectively, many organizations utilize QA Outsourcing to gain access to specialized talent. These experts interpret complex data and provide the human insight needed to solve nuanced problems. By blending automation with manual penetration testing, businesses achieve a level of precision that tools alone can’t provide. The owasp top 10 2025 news updates suggest that shifting security left is no longer optional for competitive enterprises.

Securing the Atlassian and ServiceNow Environments

Applying OWASP 2025 principles to enterprise platforms like Jira Service Management and ServiceNow is critical for maintaining operational integrity. Custom plugins and third-party integrations often serve as overlooked entry points for attackers. During a complex AWS cloud migration, security must be integrated into the architecture from the very first day. This proactive stance prevents the accumulation of technical debt and ensures that digital transformation services deliver long-term value.

By prioritizing security during platform upgrades and cloud transitions, enterprises protect their most sensitive data assets. Test Triangle acts as a Strategic Architect in these scenarios, ensuring your ecosystem is both agile and resilient. Partner with Test Triangle to secure your enterprise DevOps pipeline today.

Test Triangle serves as a Strategic Architect for global enterprises, ensuring that security isn’t just a reactive measure but a foundational pillar of operational stability. By aligning our custom security testing services with the latest owasp top 10 2025 news, we empower organizations to mitigate risks before they manifest as costly breaches. Our methodology centers on a proven triad: Technology, Talent, and Transformation. This framework allows us to provide a steady hand in a fast-changing landscape, helping firms in sectors like Banking and Life Sciences maintain flawless digital infrastructures. We’ve built our reputation on being a Trusted Partner that’s deeply invested in the long-term success of our clients.

By combining technical expertise with adaptable delivery models, Test Triangle helps businesses reduce costs while elevating their security posture. We don’t just provide a service; we deliver a comprehensive roadmap that addresses the unique challenges of the 2025 threat environment. Our global presence ensures that we can support complex infrastructures across multiple time zones, providing the reliability that modern enterprises demand.

Technology: Advanced Tooling and Integration

By leveraging our expertise in industry-leading security platforms, we help businesses optimize their existing stacks for maximum visibility. Our consultants refine DevOps pipelines to incorporate real-time vulnerability feedback, ensuring that security is a continuous process rather than a final gate. This proactive integration reduces the time to remediation by approximately 40% in high-velocity development environments. We’ve mastered the art of technical integration, specifically by embedding automated OWASP 2025 security checks into Atlassian workflows to ensure that Jira Service Management becomes a central hub for risk remediation. This approach ensures that developers receive actionable security data without leaving their primary work environment.

Talent and Transformation: Long-term Strategic Partnership

Addressing the sophisticated risks highlighted in the owasp top 10 2025 news requires more than software; it demands specialized human intelligence. We bridge the global skills gap by providing the elite talent needed to manage complex security environments, from penetration testers to DevSecOps engineers. Our flexible engagement models allow us to act as a Strategic Architect, driving digital transformation that’s secure by design rather than by accident. By embedding security into the very fabric of the development culture, we’ve helped clients ensure that 90% of new features meet rigorous security standards before they ever reach production. This cultural shift is essential for maintaining a robust defense in an era of automated attacks.

Our commitment to excellence is reflected in our ability to scale security teams rapidly to meet emerging threats. Whether you’re navigating a migration or securing a new AI-driven application, our consultants provide the precision and discipline required for success. Consult with our experts on your OWASP 2025 security roadmap to begin your journey toward a more robust and resilient digital future.

Fortifying Your Enterprise Against the 2025 Vulnerability Landscape

Adapting to the latest owasp top 10 2025 news requires more than a reactive posture; it demands a strategic overhaul of your development lifecycle. By prioritizing the mitigation of Broken Access Control and addressing persistent misconfigurations, global enterprises can reduce their attack surface before code ever reaches production. Organizations operating within high-compliance sectors like Pharmaceuticals and Finance must align their DevOps pipelines with these updated 2025 standards to maintain operational integrity. Shifting security left ensures that vulnerabilities are identified early, helping organizations avoid the $4.45 million average cost of a data breach reported by IBM in 2023.

As an Authorized Atlassian and ServiceNow Strategic Partner, Test Triangle provides the specialized expertise needed to navigate these complex shifts. Our global delivery model is built on the pillars of Technology, Talent, and Transformation, ensuring your digital infrastructure remains robust against emerging threats. By choosing a Trusted Partner with a proven track record in rigorous regulatory environments, you’re investing in a secure and scalable future. We’re ready to help you optimize your security strategy and drive long-term resilience.

Contact Test Triangle for a Comprehensive OWASP 2025 Security Audit

Frequently Asked Questions

What is the most significant change in the OWASP Top 10 2025?

The elevation of Software Supply Chain Failures to a primary risk category is the most critical update in the 2025 list. This shift responds to a 40% increase in supply chain attacks documented in the 2024 ENISA Threat Landscape report. By prioritizing this category, OWASP encourages global enterprises to move beyond internal code audits and scrutinize third-party dependencies. This strategic focus ensures that your security posture remains robust against complex, multi-stage digital intrusions.

How does A03:2025 Software Supply Chain Failures differ from previous versions?

A03:2025 expands its scope by focusing explicitly on the provenance and security of external components. While the 2021 version touched on integrity, the 2025 update demands rigorous verification of the 80% of modern application code that typically originates from open-source libraries. This change requires organizations to implement automated Software Bill of Materials (SBOM) management. By adopting these measures, your team can effectively mitigate risks associated with unverified third-party scripts and plugins.

Is SSRF still a standalone category in the 2025 OWASP list?

Server-Side Request Forgery (SSRF) remains a distinct category, though its ranking has shifted based on 2024 exploit frequency data. Organizations must still treat SSRF as a high-priority threat because it allows attackers to bypass firewalls and access internal microservices. This persistence in the owasp top 10 2025 news highlights the ongoing vulnerability of cloud-native architectures where metadata services are frequently targeted. You shouldn’t overlook this risk just because other categories have gained more visibility.

Why did Security Misconfiguration move up to the second position in 2025?

Security Misconfiguration rose to the number two spot because it accounts for 35% of successful cloud breaches identified in 2024 industry data. As enterprises accelerate their digital transformation, the complexity of managing permissions across thousands of containers often leads to human error. By addressing this early, your team can prevent the unauthorized access that stems from default credentials and overly permissive cloud buckets. It’s a vital area where automated configuration audits can deliver immediate security improvements.

How can my organization transition from the 2021 to the 2025 OWASP standards?

Transitioning requires an immediate gap analysis to map your current 2021 controls against the updated 2025 risk definitions. You should update your DevSecOps pipelines by January 2026 to include specific checks for supply chain integrity and advanced configuration validation. Through the synergy of Technology, Talent, and Transformation, Test Triangle acts as a Strategic Architect during this process. We help you leverage automated tools to align your security roadmap with these evolving global standards flawlessly.

What tools are best for testing against the OWASP Top 10 2025?

Effective testing requires a combination of Static Analysis Security Testing (SAST) and Dynamic Analysis Security Testing (DAST) tools like Checkmarx or Burp Suite Professional. To address the latest owasp top 10 2025 news, you must also integrate Software Composition Analysis (SCA) tools such as Snyk to monitor third-party vulnerabilities. These platforms provide the technical rigor needed to identify complex flaws like insecure direct object references. Using integrated tools within Jira Service Management ensures that your remediation workflows remain efficient.

Does OWASP Top 10 2025 apply to mobile applications or just web apps?

The OWASP Top 10 2025 focuses primarily on web application risks, though many of its principles apply to the backend APIs used by mobile apps. For mobile-specific threats, organizations should refer to the OWASP Mobile Top 10, which was last updated in late 2023. By combining both standards, enterprises ensure a flawless security layer across their entire digital ecosystem. This approach protects both browser-based interfaces and native mobile applications from common vulnerabilities like broken access control and data leaks.

How often does OWASP update its Top 10 list?

OWASP typically updates the Top 10 list every three to four years, with previous iterations released in 2017, 2021, and now 2025. These updates rely on data contributed by over 500 security organizations and hundreds of thousands of vulnerability reports. This structured cadence allows your business to plan long-term security investments while staying informed about the most prevalent threats. As a Trusted Partner, we monitor these cycles to ensure your defensive strategies evolve alongside the changing technological landscape.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.
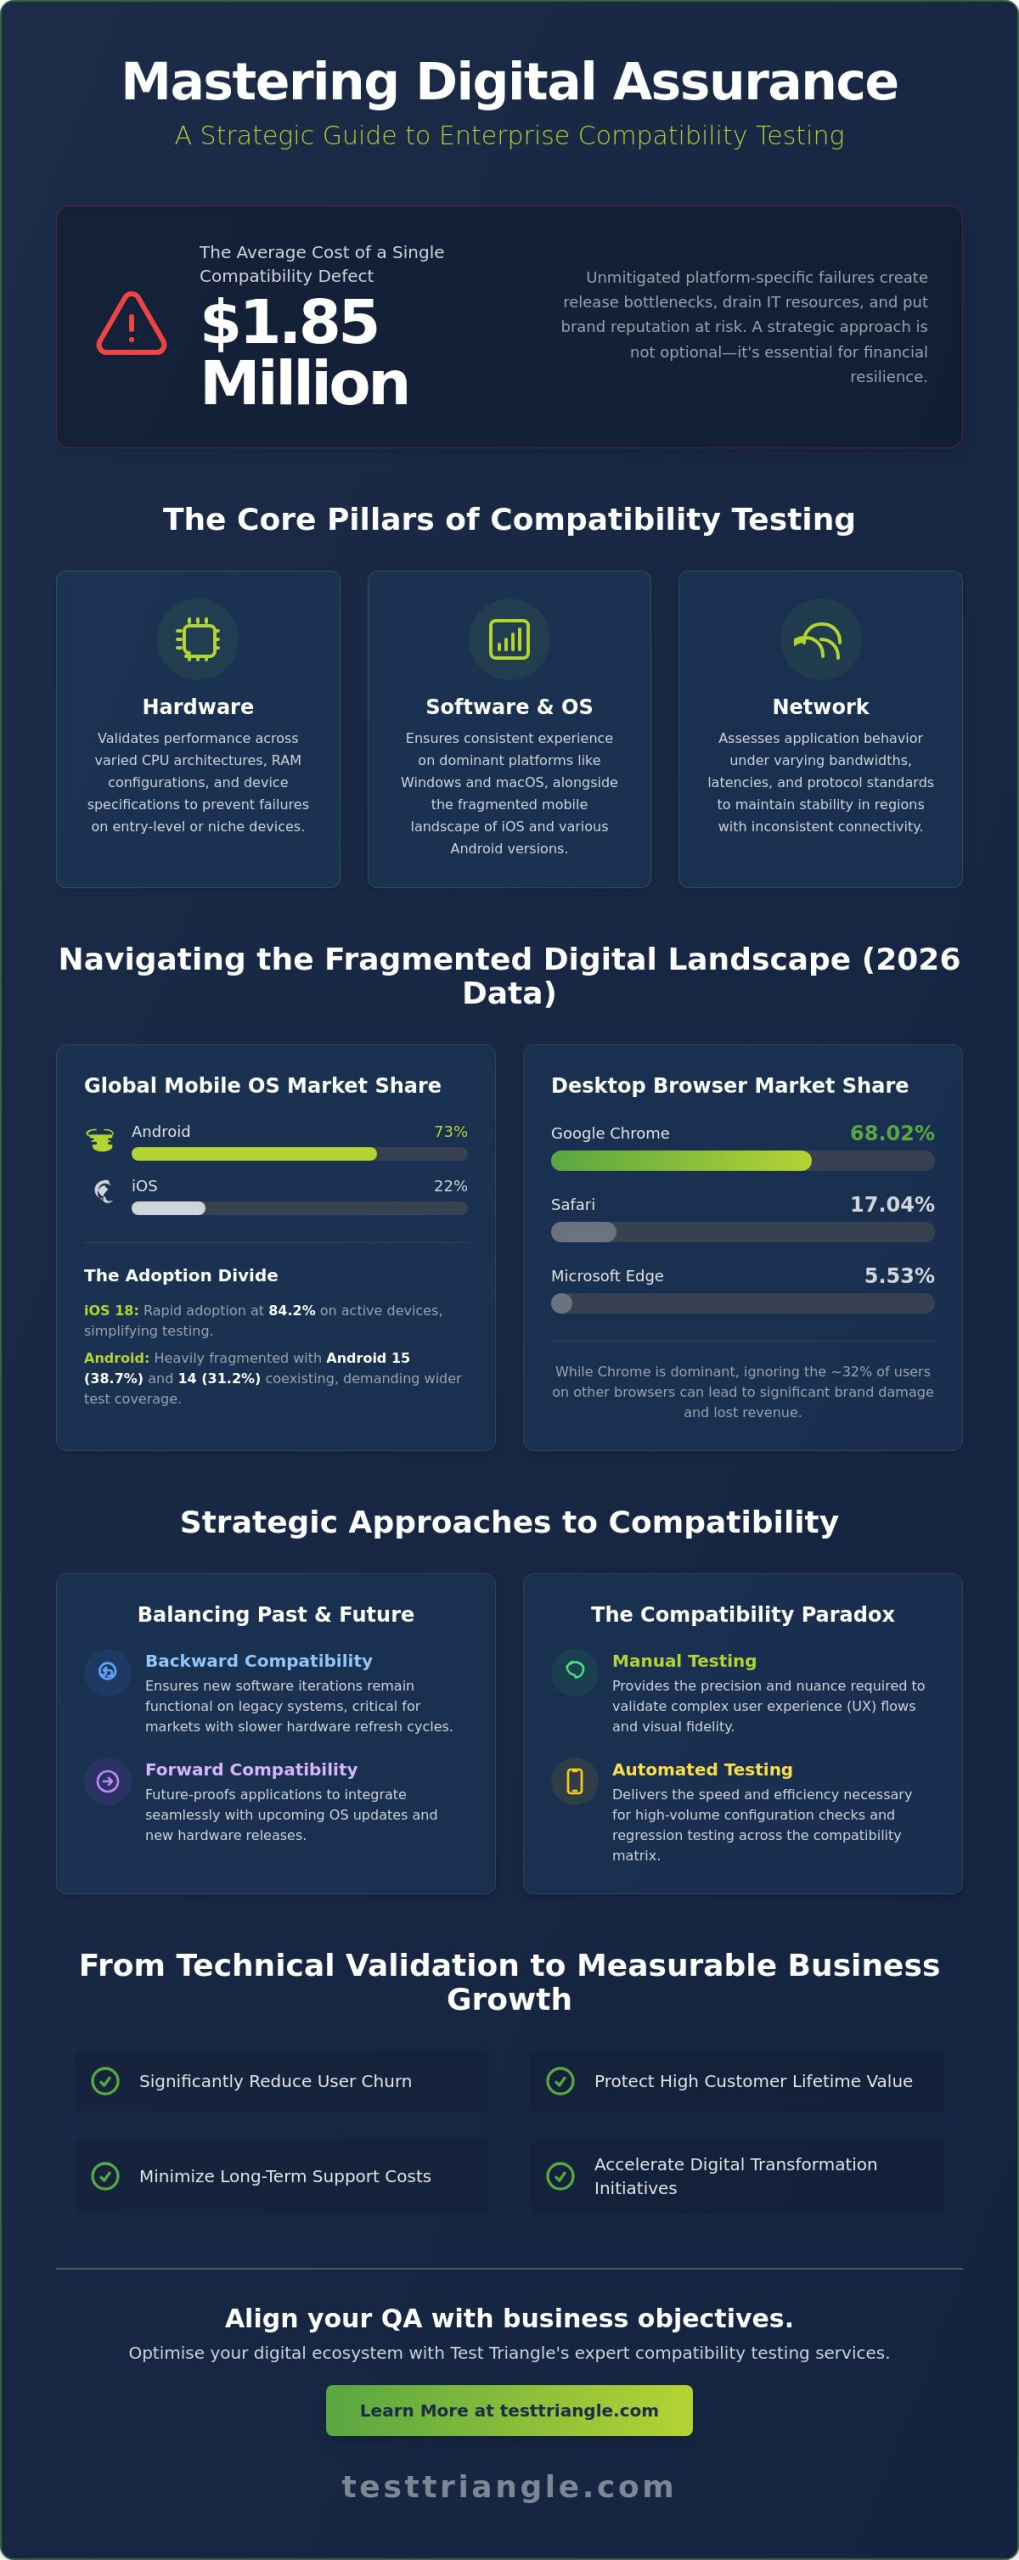
When a single compatibility-related defect can cost an enterprise an average of $1.85 million per incident, the implementation of comprehensive compatibility testing services becomes a vital pillar of financial and operational resilience. You likely find that the escalating costs of maintaining internal device labs, coupled with the pressure of fragmented platform adoption, create a persistent bottleneck in your release cycles. This friction often results in a reactive stance toward quality; brand reputation is left vulnerable to platform-specific failures that could have been mitigated through a more disciplined, strategic approach.

This guide offers a strategic blueprint for mastering digital assurance in 2026, moving beyond simple bug-hunting to establish a foundation for long-term user adoption. You’ll learn how to leverage a clear framework for platform prioritization and integrate automation testing to reduce post-release defects effectively. We will detail the path toward aligning your QA methodology with executive objectives, ensuring your digital infrastructure remains a reliable vehicle for global growth and systemic stability.

Key Takeaways

  • Understand how elite compatibility testing services transition from simple bug detection to a strategic pillar of enterprise digital assurance and risk mitigation.
  • Navigate the “Compatibility Paradox” by balancing the precision of manual testing for user experience with the efficiency of automation for high-volume configurations.
  • Establish a data-driven Compatibility Matrix that prioritizes platform testing based on real-world user analytics and organizational risk profiles.
  • Learn to align quality assurance with broader business objectives through the strategic integration of industry-leading platforms like ServiceNow and Atlassian.

Defining Compatibility Testing Services in the Multi-Platform Era

The modern enterprise ecosystem is defined by its inherent volatility, requiring a rigorous approach to software validation that transcends basic functional checks. As a specialized non-functional testing type, Compatibility testing serves as the primary mechanism for ensuring interoperability across disparate technical environments. Strategic compatibility testing services evaluate how an application performs within diverse hardware configurations, operating system versions, and network protocols, ensuring that the user experience remains consistent regardless of the access point. This methodology is central to digital assurance, protecting brand integrity by preventing the platform-specific glitches that lead to user frustration and immediate churn.

A sophisticated strategy must address two distinct temporal dimensions: backward and forward compatibility. Backward compatibility ensures that new software iterations remain functional on legacy systems, a critical requirement for enterprises serving markets with slower hardware refresh cycles. Conversely, forward compatibility involves future-proofing the application to ensure it integrates seamlessly with upcoming OS updates or hardware releases. By balancing these priorities, organizations maintain a stable, reliable presence across the global device landscape, where Android currently holds a 73% market share and iOS maintains a 22% share as of early 2026.

The Core Pillars of Compatibility

Precision, performance, and peace-of-mind are achieved through a three-pronged focus on the underlying technology stack. Hardware compatibility testing validates performance across varied CPU architectures and RAM configurations, ensuring that resource-intensive applications don’t fail on entry-level devices. Software and OS compatibility involves rigorous validation against dominant platforms like Windows and macOS, alongside the fragmented mobile landscape where iOS 18 and multiple Android versions coexist. Finally, network compatibility testing assesses application behavior under varying bandwidths, latencies, and protocol standards, which is essential for maintaining operational stability in regions with inconsistent connectivity.

Why Compatibility is a Strategic Business Driver

Beyond technical validation, compatibility testing services act as a catalyst for organizational growth and cost efficiency. By eliminating platform-specific friction points, enterprises can significantly reduce user churn and protect the high lifetime value of their customer base. A proactive approach also minimizes long-term support costs; it prevents the drain on IT resources caused by troubleshooting defects in niche or legacy environments. These services are indispensable for successful Digital Transformation Services, ensuring that as new enterprise tools are introduced, they integrate flawlessly with existing stacks and maintain the steady hand of institutional maturity. This strategic alignment ensures that every technical deployment translates directly into measurable business outcomes and scalable growth.

The Strategic Scope of Software Compatibility: Beyond Browsers

While many stakeholders view compatibility as a simple front-end validation, enterprise-grade compatibility testing services must address the entire technological stack to ensure seamless digital assurance. This multidimensional approach moves from the user interface down to the backend architecture, where minor discrepancies in data handling or API responses can trigger systemic failures. By adopting standards recognized by the National Institute of Standards and Technology (NIST), organizations can situate their testing protocols within a broader framework of software quality and institutional reliability. True compatibility is not just about visual fidelity; it’s about the precision of data exchange between your application and the global digital infrastructure.

In the current web landscape, Google Chrome maintains a dominant 68.02% market share as of April 2026. However, the remaining fragmentation across Safari at 17.04% and Microsoft Edge at 5.53% necessitates precise cross-browser validation to prevent brand damage. Mobile environments present an even greater challenge due to diverging adoption rates. While iOS 18 enjoys a rapid 84.2% adoption rate on active iPhones, the Android ecosystem remains heavily divided, with Android 15 at 38.7% and Android 14 at 31.2%. Strategic compatibility testing services bridge this gap, ensuring that your software remains performant across these varied version cycles without sacrificing speed or security.

Server and Database Compatibility

Validating application behavior across cloud environments like AWS and Azure, or within complex on-premise configurations, is essential for maintaining consistent uptime. Database interoperability is equally vital; ensuring data integrity remains intact across SQL and NoSQL variants prevents the corruption of critical business intelligence. For organizations focused on complex connectivity, our API Testing Services provide the deep-dive technical context needed to secure your third-party integrations and internal microservices.

Peripheral and External Integration

Modern enterprise compatibility extends to the physical world, requiring rigorous testing with external hardware such as printers, scanners, or IoT sensors that power industrial workflows. Human-centric compatibility is also a regulatory necessity. With the U.S. Department of Justice adopting WCAG 2.1 Level AA for ADA Title II compliance, many public entities must meet these standards by April 2026 to avoid legal risk. Aligning these technical requirements with IT Service Management Solutions ensures enterprise-wide consistency and operational reliability across every touchpoint. If you’re ready to stabilize your digital ecosystem, consult with our strategic QA experts to begin your transformation.

Compatibility Testing Services: A Strategic Guide to Enterprise Digital Assurance in 2026

Strategic Selection: Manual vs. Automated Compatibility Testing

Enterprises often grapple with the “Compatibility Paradox,” a strategic challenge where the exponential growth of the global device landscape outpaces manual testing capacity while remaining too nuanced for total automation. To resolve this, elite compatibility testing services utilize a disciplined 80/20 prioritization framework, focusing resources on the configurations that represent the vast majority of user traffic. By balancing human intuition with machine speed, organizations can orchestrate a testing lifecycle that is both comprehensive and cost-effective, ensuring that digital products remain resilient across every critical touchpoint. This methodology allows for a steady hand in a fast-changing technological landscape, emphasizing organizational progress through a combination of human expertise and technical precision.

When to Prioritise Manual Compatibility Testing

Manual validation remains indispensable for capturing the subtle UI/UX discrepancies that automated scripts often overlook. This human-centric approach is vital for exploratory testing on flagship devices, where the visual “look and feel” of an application directly influences brand perception. By focusing on high-value user journeys, testers can identify visual regressions and layout shifts across varied display resolutions that might otherwise compromise the user experience. For a deeper analysis of these methodologies, our Manual Testing Pillar provides a clear framework for integrating human expertise into your digital assurance strategy, ensuring that your software resonates with users on a qualitative level.

Scaling with Automated Cross-Platform Tools

To achieve the stability, scale, and speed required for modern release cycles, organizations must leverage Software Test Automation Services for high-volume regression. Utilizing cloud-based device farms allows for the parallel execution of test suites across hundreds of configurations simultaneously, providing a level of coverage that manual efforts cannot replicate. This approach is particularly effective for validating stable, repetitive paths across the most common user environments, such as the dominant Chrome and iOS 18 versions identified in our earlier market share analysis. Integrating these automated compatibility testing checks directly into the CI/CD pipeline ensures that interoperability is maintained continuously, significantly reducing the risk of post-release defects while accelerating your overall time-to-market.

Building an Enterprise Compatibility Strategy for 2026

Developing a robust enterprise strategy for 2026 requires a shift from exhaustive, unprioritized testing toward a model of data-driven precision. By leveraging sophisticated user analytics, organizations can identify the exact configurations that drive the highest engagement and revenue, allowing them to focus their compatibility testing services where they matter most. This approach involves the creation of a Compatibility Matrix that aligns technical coverage with business risk and current market share. It ensures that your most critical digital assets remain stable across the volatile platform updates that define the modern ecosystem, providing the peace of mind that comes from proactive risk reduction.

We must address the practical reality that testing every possible device combination is a mathematical impossibility. Instead, sophisticated enterprises should define a “Minimum Viable Compatibility” (MVC) tier. This tier guarantees a flawless experience on the top 90% of user environments while establishing a functional baseline for secondary platforms. Achieving this requires a balanced QA budget that utilizes virtualization for rapid, cost-effective regression and real device testing for final, high-fidelity assurance. This hybrid model avoids the high cost of maintaining massive device labs without sacrificing the qualitative insights necessary for global brand integrity.

Pharma and Regulated Industry Considerations

In highly regulated sectors like Life Sciences, compatibility testing takes on a critical legal dimension. Strategic compatibility testing services in these environments must ensure validated testing environments that meet strict GxP compliance standards. Maintaining comprehensive audit trails and documentation is a requirement for operational stability and regulatory approval. To navigate these complex landscapes, partnering with specialized IT Staffing Agencies for Pharmaceutical Industry ensures that your team possesses the domain expertise needed to maintain compliance alongside technical rigor.

Performance and Data Integrity during Transitions

Compatibility must also remain a priority during large-scale system migrations or digital shifts. Ensuring that data remains consistent and accessible across varied platforms is the primary goal of Data Migration Testing. Simultaneously, leadership should monitor Performance Testing Services metrics to identify how hardware acceleration or different GPU vendors affect application speed on varied device tiers. These technical nuances ensure that performance isn’t sacrificed for the sake of broad compatibility. Ready to refine your digital assurance roadmap? Speak with our strategic consultants today to build a customized compatibility matrix for your enterprise.

Optimising Digital Ecosystems with Test Triangle

In a global marketplace where digital stability directly correlates with revenue retention, Test Triangle provides a strategic partnership that bridges the gap between technical quality assurance and high-level business outcomes. By moving beyond the role of a traditional vendor, we position ourselves as a reliable, long-term collaborator dedicated to your operational stability and scalable growth. Our comprehensive compatibility testing services are designed to address the multifaceted challenges of the 2026 digital landscape, ensuring that your enterprise applications remain resilient across every hardware, software, and network configuration. This disciplined approach provides the peace of mind that comes from systemic risk reduction and the empowerment found in large-scale technological evolution.

Efficiency, expertise, and evolution define our commitment to digital assurance. Our deep technical proficiency in complex enterprise ecosystems, including Atlassian Implementation and ServiceNow, ensures that compatibility validation is never performed in a vacuum. We integrate testing protocols directly into your core operational platforms, facilitating a seamless flow of data and functionality across your entire infrastructure. To support these efforts, we offer highly adaptable engagement models, from managed outsourcing to specialized IT staffing, underpinned by a global delivery model that ensures continuous digital assurance and rapid market readiness for your software portfolio.

Strategic Partnership and Long-Term Value

Our methodology focuses on delivering long-term value through official partnerships with industry leaders like AWS and ServiceNow, allowing for infrastructure-aware testing that accounts for cloud-specific nuances. By leveraging these alliances, we provide customized technology roadmapping to future-proof your application’s compatibility against upcoming platform shifts. This strategic foresight prevents the costly rework associated with reactive testing, anchoring your digital strategy in recognized global benchmarks and institutional maturity. Our goal is to serve as a steady hand, guiding your organization through the complexities of digital transformation with precision and technical rigor.

Next Steps for Enterprise Digital Assurance

Initiating a comprehensive compatibility audit of your current software portfolio is the first step toward achieving a stabilized digital ecosystem. This audit identifies critical fragmentation risks and establishes the baseline for a data-driven Compatibility Matrix. Integrating these rigorous compatibility checks into your DevOps Consulting framework ensures that quality is built into the development lifecycle rather than added as an afterthought. By aligning your QA methodology with executive goals, you transform testing from a cost center into a strategic asset. To begin your journey toward flawless digital transitions, contact Test Triangle for a Strategic QA Consultation and discover how our expertise can secure your competitive advantage.

Mastering Digital Resilience in an Evolving Ecosystem

The transition toward a unified digital assurance model requires more than technical execution; it demands a strategic alignment between quality engineering and overarching business goals. By implementing a data-driven Compatibility Matrix and balancing the “Compatibility Paradox” through a disciplined mix of manual and automated validation, your organization can effectively mitigate the financial risks associated with platform fragmentation. This approach ensures that your software remains performant across the 2026 device landscape, protecting your brand integrity and user experience in every global market.

Test Triangle stands as your reliable long-term collaborator, offering compatibility testing services that are deeply integrated with the ecosystems of our strategic partners, including Atlassian, ServiceNow, and AWS. Our global delivery model, which maintains a robust presence in Europe, North America, and Asia, provides the specialized expertise necessary for success in highly regulated industries like Life Sciences. It’s time to move beyond reactive QA and embrace a proactive roadmap for stability, precision, and growth. You can secure your digital ecosystem with Test Triangle’s strategic compatibility testing services and lead your enterprise toward a future of enduring operational excellence.

Frequently Asked Questions

What is the difference between compatibility testing and interoperability testing?

Compatibility testing ensures your application functions correctly across diverse environments like varied operating systems, browsers, or hardware configurations. Interoperability testing, by contrast, validates the seamless exchange of data between your software and external systems or third-party APIs. While compatibility focuses on environment-specific performance, interoperability is about systemic communication and integration within a broader digital infrastructure.

How do we decide which devices and browsers to include in our compatibility testing services?

Strategic selection begins with a rigorous analysis of your specific user analytics to identify the platforms driving the highest engagement and revenue. You should align these insights with global market share data, such as Google Chrome’s 68.02% dominance or the high adoption rates of iOS 18. This data-driven approach allows you to build a Compatibility Matrix that prioritizes high-value configurations while establishing a functional baseline for secondary environments.

Can compatibility testing be fully automated in 2026?

Full automation remains unattainable in 2026 because automated scripts cannot replicate the nuanced human perception required to identify subtle UI/UX discrepancies. While automation testing is essential for high-volume regression and parallel execution on cloud-based device farms, manual intervention is still necessary for exploratory testing on flagship devices. A balanced strategy leverages automation for speed and manual testing for qualitative brand assurance.

What are the risks of ignoring backward compatibility for enterprise software?

Ignoring backward compatibility risks alienating users on legacy systems, which often leads to immediate churn and increased long-term support costs. For global enterprises, failing to support older OS versions can result in significant brand damage and the loss of market share in regions with slower hardware refresh cycles. Proactive compatibility testing services mitigate these risks by ensuring a stable experience across both modern and legacy environments.

How does compatibility testing impact the overall cost of software development?

While comprehensive compatibility testing requires an initial investment, it significantly reduces the overall cost of software development by preventing expensive post-release defects. Industry estimates from 2025 suggest that compatibility-related failures cost enterprises an average of $1.85 million per incident. By identifying environment-specific glitches early in the lifecycle, organizations avoid the high costs of emergency patches and reactive troubleshooting.

Is it necessary to test on real devices, or are emulators sufficient for digital assurance?

Emulators are sufficient for early-stage development and basic functional checks, but real device testing is essential for final digital assurance. Real devices provide accurate data on hardware acceleration, battery consumption, and network latency that emulators often fail to replicate. A disciplined QA strategy utilizes virtualization for cost-effective scaling and real devices for validating high-priority user journeys on flagship hardware.

How often should we perform compatibility testing for a SaaS application?

Compatibility testing should be an ongoing component of your CI/CD pipeline, performed with every major release or significant environment update. For SaaS applications, it’s also vital to monitor external platform cycles, such as browser version updates or mobile OS refreshes, to ensure continued stability. This continuous approach to quality engineering prevents the accumulation of technical debt and maintains a reliable presence in a fast-changing landscape.

What role does compatibility testing play in regulatory compliance for the pharmaceutical industry?

In the pharmaceutical industry, compatibility testing is a core requirement for GxP compliance and maintaining validated testing environments. It ensures that critical software remains functional and accurate across all approved hardware configurations, which is vital for patient safety and data integrity. Rigorous documentation and audit trails during this process provide the necessary proof of compliance for regulatory bodies in highly regulated sectors.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.
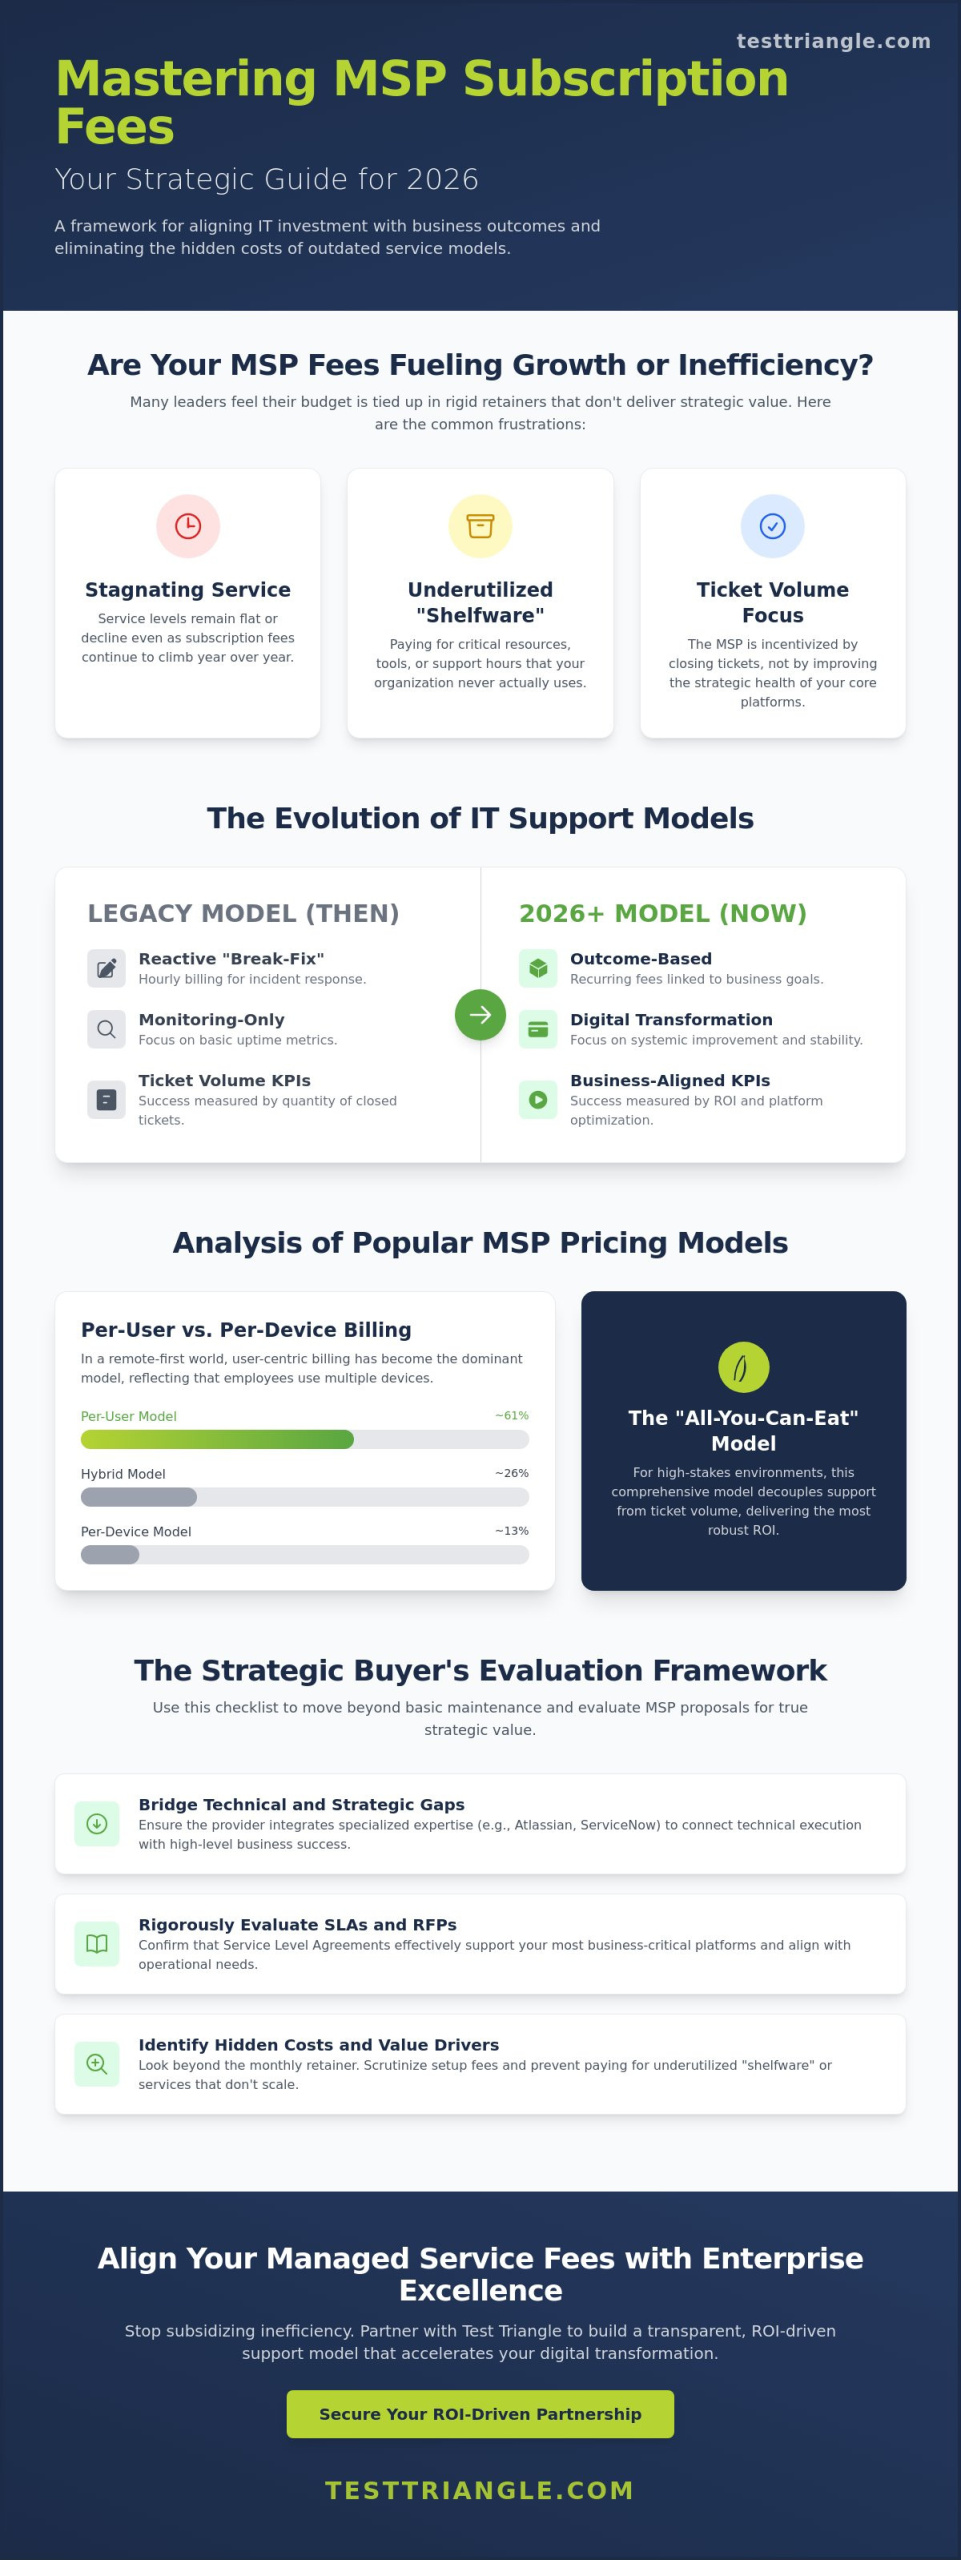

What if the premium your organization pays for digital stability is actually subsidizing a provider’s internal inefficiencies rather than fueling your own technological evolution? Many enterprise leaders feel the weight of opaque Managed Service Provider Subscription Fees that continue to climb even as service levels stagnate or critical resources remain underutilized. It’s a common frustration to find your budget tied up in “shelfware” or rigid retainers that prioritize ticket volume over the strategic health of your ServiceNow or Atlassian ecosystems.

This 2026 guide is designed to help you master the complexities of modern pricing structures, allowing you to align your investment with specific business outcomes and long-term operational stability. You’ll discover a clear framework for comparing complex quotes and learn how to shift the conversation from basic maintenance to high-impact platform optimization. We will explore current industry benchmarks for per-user and co-managed models, identify the hidden costs in low-tier plans, and provide the methodology needed to secure a partnership that prioritizes your ROI through disciplined DevOps and ITSM integration.

Key Takeaways

  • Understand why traditional break-fix models have been superseded by recurring structures. These frameworks prioritize continuous digital transformation and operational stability.
  • Master the nuances of Managed Service Provider Subscription Fees by comparing per-user and per-device models. This ensures your IT spend remains predictable in a remote-first environment.
  • Identify hidden value drivers and setup costs to prevent paying for underutilized “shelfware” or services that don’t scale.
  • Establish a rigorous evaluation framework for reviewing SLAs and RFP responses. Your service levels must effectively support business-critical platforms like ServiceNow.
  • Learn how to bridge the gap between technical execution and strategic success. Integrating specialized Atlassian implementation expertise into your managed support model is a critical differentiator.

Defining Managed Service Provider Subscription Fees in 2026 requires a perspective that views technology as a driver of institutional maturity rather than a simple cost center. In the current market, the reactive “break-fix” hourly model has been almost entirely marginalized in favor of recurring subscriptions that guarantee operational continuity and risk mitigation. Leaders must understand what a managed service provider is in this new era: a long-term collaborator that manages complex digital infrastructures through systemic improvement rather than mere incident response. This shift reflects a broader economic reality where global volatility demands predictable, outcome-linked expenditure that aligns with long-term strategic goals.

The transition from “Monitoring-Only” to “Outcome-Based” pricing represents the most significant change in how enterprises evaluate their IT investments. While legacy providers focused on uptime and ticket volume, the modern framework prioritizes the acceleration of specific business objectives. Global economic shifts, including talent scarcity in specialized technical fields and the rising costs of cybersecurity insurance, have naturally influenced MSP margin expectations and base rates. However, the move toward transparent, value-driven models ensures that organizations can justify these costs by measuring the direct impact on their digital transformation journey.

The Evolution of Value-Based IT Support

The industry has reached a tipping point where uptime metrics alone no longer justify high-level retainers. Modern enterprises are prioritizing business-aligned performance indicators, shifting the focus of Managed Service Provider Subscription Fees toward Precision, Progress, Performance. By integrating advanced automation and cognitive computing into their internal workflows, providers are effectively reducing the overhead of commoditized tasks. This allows them to redirect human capital toward high-level strategic architecture. Consequently, organizations are now prioritizing platform-specific expertise over generalist support, recognizing that specialized knowledge is required to optimize complex environments.

Subscription Fees vs. Professional Service Fees

Maintaining a clear distinction between recurring maintenance and project-based consulting is essential for transparent budgeting and margin management. While subscription fees cover the ongoing health, security, and incremental updates of your IT service management ecosystem, one-time initiatives usually fall under professional service fees. For instance, a full-scale Atlassian implementation or a major ServiceNow migration requires a time-and-materials approach due to its unique scope. Identifying which IT needs fit a subscription model depends on the frequency and predictability of the requirement. A robust Service Level Agreement (SLA) acts as the definitive boundary, ensuring that both parties agree on what constitutes “business as usual” versus a specialized transformation project.

Selecting the appropriate framework for Managed Service Provider Subscription Fees is a critical decision that influences both operational agility and budgetary precision. In a remote-first work environment, the debate between “Per-User” and “Per-Device” models has largely settled in favor of user-centric billing. This shift reflects the reality that modern professionals often operate across multiple endpoints, making device-based tracking an administrative burden. While approximately 13% of providers still rely on per-device pricing as their primary model, around 26% have transitioned to a hybrid approach that combines elements of both to better reflect the complexity of modern enterprise infrastructures.

For organizations managing high-stakes environments, the “All-You-Can-Eat” model often provides the most robust ROI. This comprehensive structure decouples support from ticket volume, encouraging a proactive partnership where the provider is incentivized to eliminate root-cause issues rather than billing for repetitive fixes. When evaluating these models, it’s vital to align the chosen tier with your actual needs. Many enterprises find themselves overpaying for “Gold” tier packages that include redundant compliance features, when a “Silver” tier combined with targeted ServiceNow consulting services would offer a more precise fit for their operational requirements.

The Per-User Pricing Model: The 2026 Standard

Per-user billing has emerged as the industry standard because it simplifies scalability during periods of rapid organizational growth. This model aligns the provider’s incentives with the client’s success; fewer technical disruptions lead to lower operational costs for the MSP, fostering a culture of Stability, Security, Success. To prevent overbilling, enterprises must implement rigorous audits of “active user” counts within their directory services. Ensuring that subscription fees are only applied to current, authorized personnel is a fundamental step in maintaining a lean and efficient IT budget. If you’re looking to optimize your resource allocation, you might consider how tailored staffing strategies can complement your existing support structure.

Tiered and À La Carte Options

Tiered structures allow organizations to construct a custom service stack that matches specific platform needs without the risks associated with pure à la carte pricing. While à la carte models offer initial flexibility, they often lead to “nickel and diming” for essential security patches or routine maintenance tasks. A more strategic approach involves evaluating tiered packages against your internal DevOps and QA capabilities. For instance, an organization with a strong internal testing team may only require a subscription that covers specialized Atlassian implementation support and high-level architectural guidance, rather than a full-service helpdesk retainer.

Managed Service Provider Subscription Fees: The 2026 Enterprise Buying Guide

Beyond the Monthly Retainer: Identifying Hidden Costs and Value Drivers

While the monthly retainer is the most visible element of Managed Service Provider Subscription Fees, the true total cost of ownership is often dictated by variables that sit just below the surface. Strategic procurement requires a granular understanding of how onboarding fees, platform licensing, and integrated personnel models impact the long-term budget. A common pitfall for enterprises is failing to account for “out-of-scope” triggers. These are specific events or requests that fall outside the standard agreement, leading to unexpected billing spikes that can disrupt even the most disciplined financial planning. By identifying these triggers during the negotiation phase, you can ensure your expenditure remains predictable and aligned with your ROI targets.

Platform licensing for ecosystems like Atlassian and ServiceNow also plays a significant role in your overall spend. Whether your provider manages these licenses on your behalf or you maintain them internally, the complexity of these environments often necessitates specialized oversight. Integrating staffing solutions directly into your managed service framework allows for more sophisticated margin management. This approach enables you to fill specific skill gaps, such as specialized manual or automation testing, without the need to upgrade your entire service tier for the entire organization.

Onboarding and Implementation Charges

A professional system audit and environment baseline are the core components of a legitimate onboarding fee. This initial phase is not merely a setup cost; it’s a rigorous process that ensures your provider understands the nuances of your digital infrastructure. When negotiating multi-year managed service contracts, it’s often possible to amortize these setup fees or tie them to specific implementation milestones. You must ensure that comprehensive knowledge transfer is explicitly included in this phase. This prevents vendor lock-in and guarantees that your internal teams remain empowered and informed throughout the partnership.

The Role of Specialized Talent in MSP Fees

The integration of managed outsourcing services can significantly lower your subscription overhead by optimizing the delivery model. By balancing high-level local strategic consulting with cost-effective technical execution teams, providers can offer a more versatile and globally-minded support structure. This model provides “fractional” access to elite DevOps and QA experts who might be too expensive to hire as full-time internal resources. This hybrid approach delivers Precision, Proximity, Productivity, ensuring that your technical managers have the specific expertise they need exactly when they need it, without inflating the base subscription rate.

The Strategic Buyer’s Framework for Evaluating MSP Proposals

Evaluating Managed Service Provider Subscription Fees through the lens of a Request for Proposal (RFP) demands a rigorous methodology that transcends basic cost comparisons. A strategic buyer doesn’t merely look for the lowest monthly retainer; instead, they seek to understand the correlation between the fee structure and the provider’s ability to deliver operational resilience. This evaluation process should involve five critical questions designed to expose the depth of a provider’s strategic commitment. These include inquiries into their methodology for license optimization, their internal security protocols, and how they define “value” beyond basic ticket resolution. By forcing providers to articulate their impact on your long-term digital health, you can distinguish between a simple vendor and a high-level corporate partner.

When assessing an SLA for business-critical environments such as ServiceNow, it’s essential to look for guarantees that protect against systemic failure rather than just slow response times. Cheaper bids often indicate a lack of platform-specific expertise, which can be disastrous during complex Atlassian Cloud migrations or infrastructure overhauls. Using the “Cost of Downtime” as a benchmark allows technical leaders to justify higher-tier managed service subscriptions to executive stakeholders. If an hour of system unavailability costs the enterprise significantly more than the annual premium for expert support, the decision to prioritize quality becomes a matter of risk management rather than just procurement. High-level support delivers Stability, Scalability, Security, protecting your most valuable digital assets from preventable disruptions.

Auditing Vendor Expertise and Certifications

Authorized partnership status, such as being an Atlassian Platinum partner, should significantly influence your fee tolerance. These endorsements serve as official benchmarks of a provider’s technical depth and their direct line to platform-level support. Industry-specific experience is equally vital, particularly in highly regulated sectors like Pharma or Finance where compliance is non-negotiable. You must verify the MSP’s internal security protocols and their history of managing diverse, complex digital infrastructures. A partner’s ability to operate across these rigid regulatory frameworks ensures that your organizational progress isn’t hindered by compliance gaps.

Negotiating for Scalability and Flexibility

Building “ramp-up/ramp-down” clauses into your agreement ensures that Managed Service Provider Subscription Fees reflect the actual usage of your cloud-based tools. As your organization evolves, your support needs will fluctuate; your contract should be versatile enough to accommodate these shifts without punitive penalties. It’s also critical to review the exit strategy early in the relationship. Offboarding and data migration costs should be transparently defined to prevent financial friction at the end of the collaboration. If you are ready to move beyond generic support and secure a partner who understands the complexities of your digital ecosystem, reach out to our team today for a strategic consultation.

Test Triangle: Aligning Managed Service Fees with Enterprise Excellence

Test Triangle operates as a strategic visionary for global enterprises, ensuring that Managed Service Provider Subscription Fees are never viewed as a static overhead but as a catalyst for systemic improvement. Our philosophy centers on transparent, outcome-linked models that prioritize the long-term health of your digital infrastructure. We recognize that a one-size-fits-all approach fails to address the nuances of complex environments. Therefore, we customize our fee structures to align precisely with your specific digital transformation roadmap, ensuring every dollar spent contributes to measurable operational progress and institutional maturity.

The “Test Triangle Advantage” lies in our unique ability to bridge the gap between technical execution and business outcomes. By combining deep technical expertise in manual and automation testing with strategic IT service management solutions, we offer a comprehensive support framework that generalist providers cannot match. We seamlessly integrate specialized Atlassian implementation expertise into our ongoing managed support, ensuring that your platforms are not only maintained but continuously optimized for peak performance. This integrated approach delivers Precision, Proactivity, Partnership, positioning us as a reliable collaborator deeply invested in your stability.

Strategic Platform Optimisation

Our managed services move beyond the limitations of ticket-based metrics to focus on holistic system health and efficiency. We believe that true value is found in preventing disruptions before they occur, which is why our methodology emphasizes proactive monitoring and architectural refinement. As highlighted in our strategic guide to Atlassian consulting, organizations that prioritize strategic oversight over basic maintenance often see a significant reduction in long-term operational spend. By leveraging a global presence, we provide extended availability across diverse time zones, delivering high-level expertise without the premium price tag typically associated with localized, around-the-clock coverage.

Your Partner in Long-Term Operational Stability

We act as a disciplined extension of your internal IT and DevOps teams, fostering a spirit of partnership that is deeply invested in your long-term success. Our commitment to transparent billing ensures that your Managed Service Provider Subscription Fees remain predictable, with regular Strategic Business Reviews (SBRs) providing clear visibility into performance and ROI. We prioritize organizational stability through a combination of human expertise and industry-leading technical tools, ensuring a steady hand in a fast-changing landscape. To define a managed service model that fits your 2026 goals and empowers your technological evolution, contact our team for a detailed consultation.

Securing Your Digital Future Through Strategic Partnership

Mastering the nuances of Managed Service Provider Subscription Fees is no longer just a procurement task; it’s a strategic imperative for organizations aiming for long-term operational stability. By shifting from reactive, ticket-based expenditure to outcome-linked models, enterprises can transform their IT budget into a powerful engine for digital evolution. This guide has detailed the importance of auditing platform-specific expertise and identifying hidden value drivers to ensure your investment delivers Precision, Progress, Performance. As technical landscapes grow more complex, the ability to align recurring costs with tangible business milestones becomes the definitive marker of a mature digital strategy.

As an Atlassian Platinum Partner and ServiceNow Specialist Partner, Test Triangle provides the institutional maturity required to manage your most complex digital infrastructures with confidence. Our global delivery model ensures you receive expert support across all time zones, allowing your internal teams to focus on high-level innovation rather than routine maintenance. We remain committed to transparent, disciplined collaboration that prioritizes your strategic success and operational resilience. Optimise your IT spend with a strategic Managed Service consultation from Test Triangle and take the first step toward a more predictable, value-driven technological landscape. We look forward to supporting your journey toward enterprise excellence.

Frequently Asked Questions

What is the average monthly cost for a Managed Service Provider subscription?

In the 2026 US market, Managed Service Provider Subscription Fees typically range from $110 to $400 per user per month. These rates vary based on the depth of the service catalog, including whether the package incorporates advanced security monitoring, compliance oversight, or specialized platform management. Organizations opting for co-managed models, where they retain an internal IT lead, often see lower per-user rates compared to those requiring full-service outsourcing.

Do MSP subscription fees usually include software licenses like Atlassian or ServiceNow?

Subscription fees generally cover the management and optimization of the platform rather than the underlying software licenses themselves. Licensing for enterprise ecosystems like ServiceNow or Atlassian is usually treated as a separate pass-through cost or managed directly by the client. However, working with a partner who can provide Atlassian Licenses as part of a consolidated agreement often simplifies the procurement process and ensures that seat counts are audited for maximum efficiency.

How often should an MSP review and adjust their subscription fees?

Subscription fees should be reviewed annually or during scheduled Strategic Business Reviews (SBRs) to ensure they remain aligned with your actual resource consumption. These reviews allow both parties to adjust for changes in headcount, infrastructure complexity, or new regulatory requirements. A transparent review process prevents budgetary drift and guarantees that your expenditure continues to reflect the strategic value delivered to the enterprise.

What is the difference between an MSP subscription and a traditional IT support contract?

A modern MSP subscription is a proactive, outcome-based model that prioritizes systemic health through a predictable recurring fee. In contrast, traditional IT support often follows a reactive “break-fix” approach where costs are tied to ticket volume or hourly rates. The subscription model aligns the provider’s incentives with your success; they are motivated to eliminate root-cause issues to reduce their own operational overhead while maintaining your stability.

Are there hidden costs in MSP onboarding that I should look out for?

Hidden costs often emerge in the form of system auditing, environment baselining, and complex data migration tasks that fall outside the initial quote. You should also verify if knowledge transfer sessions and the integration of legacy tools are included in the setup fee. Ensuring these activities are clearly defined in the Service Level Agreement prevents unexpected billing spikes and ensures a steady hand during the transition period.

Can I negotiate a lower subscription fee by using offshore technical resources?

Utilizing a global delivery model that incorporates remote offshore resources can significantly optimize your Managed Service Provider Subscription Fees without sacrificing technical rigor. This hybrid approach allows you to access specialized talent for execution-heavy tasks like automation testing while maintaining local strategic oversight. It provides a versatile, globally-minded support structure that delivers high-level expertise at a more sustainable price point for large-scale digital infrastructures.

How do I calculate the ROI of my Managed Service Provider subscription fees?

ROI is calculated by measuring the reduction in system downtime, the speed of digital transformation initiatives, and the cost-efficiency gained by reallocating internal staff to strategic projects. You must also account for the risk mitigation provided by expert platform oversight, which prevents costly configuration errors and security gaps. A successful subscription delivers Stability, Scalability, Security, providing value that transcends simple maintenance to drive organizational progress.

What happens to my subscription fees if my company scales rapidly?

Per-user pricing models are designed to scale automatically, ensuring that your costs stay aligned with your headcount as you grow. To maintain financial precision, it’s essential to build “ramp-up/ramp-down” clauses into your agreement to accommodate rapid changes without punitive penalties. This flexibility ensures that your managed service model remains an adaptable collaborator that supports your growth rather than a rigid financial burden during periods of expansion.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.

With industry benchmarks now demanding a crash-free user rate of over 98 percent and app load times under two seconds, the margin for technical error in 2026 has effectively vanished. You likely recognize that high uninstallation rates often stem from subtle lag or the failure to replicate unpredictable network conditions during the development cycle. It’s frustrating when performance testing remains a late-stage afterthought rather than a core component of your sprint. This comprehensive mobile app performance testing checklist provides the strategic framework you need to bridge the gap between technical execution and business outcomes.

By adopting a DevOps-aligned approach, you can transform performance from a reactive hurdle into a predictable driver of user retention. We promise to guide you through a repeatable framework designed to eliminate bottlenecks and ensure your applications remain compliant with the latest iOS 26 and Android 17 SDK requirements. This guide previews the essential protocols for testing across diverse hardware, from the flagship iPhone 17 Pro to high-volume budget devices, ensuring your digital infrastructure achieves the operational stability required for long-term global success.

Key Takeaways

  • Quantify the strategic impact of mobile responsiveness by analyzing how millisecond delays directly correlate with enterprise revenue loss within the competitive 2026 landscape.
  • Deploy a rigorous mobile app performance testing checklist that systematically monitors CPU spikes, battery drain, and network resilience to eliminate bottlenecks before deployment.
  • Integrate performance metrics into the DevOps lifecycle to facilitate shift-left testing, ensuring that speed and stability are verified with every automated code commit.
  • Enhance backend scalability by emulating diverse network conditions and optimizing data payloads to maintain high-performance standards across complex global infrastructures.
  • Align technical KPIs with long-term business growth by utilizing expert performance engineering and flexible staffing solutions to drive sustainable digital transformation.

The High Stakes of Mobile Performance in the 2026 Digital Economy

In the digital economy of 2026, the correlation between application speed and enterprise profitability has reached a critical inflection point. Global enterprises now recognize that millisecond delays are no longer mere technical inconveniences; they’re direct catalysts for revenue erosion and brand degradation. While 5G ubiquity promised seamless connectivity, it paradoxically raised the bar for app responsiveness. When users operate on high-speed networks, their psychological threshold for latency drops significantly. If an application fails to load instantly, the user doesn’t blame the network; they blame the brand. By grounding your strategy in the foundational principles of Software performance testing, your organization can move from reactive troubleshooting to proactive engineering.

Adopting a performance-first mindset requires a fundamental shift in how we approach the development lifecycle. It’s about moving beyond the “fix it if it breaks” mentality and embracing a culture of precision, pace, and performance. This strategic evolution is particularly vital for App Store Optimization (ASO). In 2026, both Apple and Google utilize performance vitals as primary ranking factors. Applications that fail to meet the industry benchmark of 98 percent crash-free users or load times under two seconds find themselves buried in search results, regardless of their feature set. Implementing a comprehensive mobile app performance testing checklist ensures that visibility remains high and technical debt remains low.

User Retention and the Cost of Latency

The financial implications of performance bottlenecks are most visible in user retention rates. For subscription-based models, even a minor increase in lag can fuel negative brand sentiment and trigger immediate uninstalls. We see this reflected in current benchmarks where day 1 retention must exceed 25 percent to sustain growth. When performance is treated as an afterthought, the cost of reclaiming a lost user often exceeds the initial acquisition spend. Maintaining stability across diverse hardware, from the flagship iPhone 17 to the widely used Samsung Galaxy A-series, is essential for preserving the user base you’ve worked hard to build.

Performance as a Competitive Differentiator

In saturated markets like finance and retail, “stable” has become the new “fast.” Enterprises that prioritize consistent, reliable user experiences can significantly reduce long-term customer acquisition costs by fostering organic loyalty. Benchmarking your application against industry leaders isn’t just about matching their speed; it’s about exceeding their reliability. Through our specialized performance testing services, we act as a reliable long-term collaborator, helping you transform technical KPIs into tangible business ROI. This disciplined approach to QA ensures that your digital transformation efforts result in scalable growth rather than operational instability. A well-executed mobile app performance testing checklist acts as the blueprint for this competitive advantage, allowing your team to deploy with confidence every time.

The Definitive Mobile App Performance Testing Checklist

Executing a robust mobile app performance testing checklist requires more than just measuring speed; it demands a deep dive into how an application interacts with the host hardware under varying conditions. In 2026, where devices like the iPhone 17 Pro and Samsung Galaxy S26 offer immense processing power, users expect fluid interactions that don’t compromise device health. Monitoring CPU, RAM, and GPU spikes is essential. High resource utilization often results in frame drops or unresponsive UI elements. By aligning your strategy with Apple’s official performance guide, you can ensure that your application utilizes system resources efficiently without triggering thermal throttling.

Battery consumption remains a top reason for app uninstalls. Identifying power-hungry background processes through rigorous analysis prevents your app from being flagged by OS-level energy monitors. Similarly, testing for thermal impact during prolonged heavy usage is vital. Devices that overheat will automatically throttle performance, leading to a degraded user experience that your testing suite must account for. Startup time benchmarks, specifically the ‘First Contentful Paint’, determine the user’s initial perception of quality. If the app doesn’t become interactive within that two-second window, abandonment rates climb. To prevent crashes during extended sessions, memory leak detection must be a non-negotiable part of your QA cycle. Ensuring long-session stability is a hallmark of institutional maturity in software development.

On-Device Performance Metrics

Maintaining a consistent 60 or 120 FPS frame rate is critical for modern displays. Beyond visual smoothness, your checklist should evaluate storage footprint and cache management. Inefficient caching can bloat the app size, leading to storage warnings on budget devices like the Samsung Galaxy A07. Additionally, the impact of sensors such as GPS, Biometrics, and high-resolution cameras must be measured, as these components significantly drain resources when active. For enterprises seeking to refine these processes, our specialized performance testing services provide the technical rigor needed for scalable growth.

Stability and Reliability Under Pressure

Determining the breaking point through stress testing helps you understand the absolute limits of your architecture. Spike testing evaluates how the app recovers after a sudden user influx, while soak testing identifies performance degradation over several hours of continuous use. This methodical approach ensures that your application remains reliable during peak traffic events. If you are looking to optimize your current QA framework or need expert oversight, you can connect with our strategic consultants to discuss a tailored mobile app performance testing checklist for your specific enterprise needs.

Mobile App Performance Testing Checklist: The 2026 Strategic Enterprise Guide

Network Resilience and Backend Scalability Analysis

While on-device metrics establish the baseline for fluid interaction, the true measure of enterprise-grade reliability lies in an application’s ability to navigate the volatile nature of global networks. In the 2026 ecosystem, where 5G ubiquity is high but consistency remains elusive in transit hubs or rural corridors, your mobile app performance testing checklist must prioritize network resilience. By emulating 3G, 4G, and spotty Wi-Fi environments, your engineering team can ensure that the application remains functional even when connectivity is compromised. Leveraging the latest Google I/O 2026 performance tools, such as the updated ProfilingManager, allows developers to gain granular visibility into how varying connection qualities impact real-time data synchronization and user experience.

Identifying backend bottlenecks that masquerade as app lag is a sophisticated exercise in root-cause analysis that requires a holistic view of the technology stack. Data payload optimization is a critical component of this strategy; reducing API response sizes ensures that even users on legacy connections don’t suffer from prolonged wait times. Beyond simple speed, the architecture must support robust offline mode functionality. Ensuring graceful degradation when connectivity is lost prevents the app from hanging or crashing, which is essential for maintaining the high standards of stability that global enterprises demand. By focusing on server-side response times, you can isolate whether a delay originates in the mobile client or the cloud infrastructure, allowing for more precise remediation and improved operational efficiency.

API and Integration Performance

The modern mobile landscape relies heavily on a web of third-party integrations and SDKs, each of which introduces potential latency. Evaluating the speed and reliability of these external services is paramount to preventing a single failed integration from compromising the entire user journey. To maintain peak efficiency, enterprises often utilize specialized API testing services to validate seamless data flow and manage concurrent request handling at the gateway level. This disciplined approach to integration testing ensures that your digital infrastructure remains resilient under heavy load, providing the peace of mind that comes from comprehensive risk reduction.

Global Connectivity Standards

Operating on a global scale requires strict adherence to international connectivity standards and protocol optimization. Your testing suite should compare the performance of HTTP/2 versus HTTP/3 to determine which protocol offers the best multiplexing and header compression for your specific use case. Testing for cross-border latency and CDN efficiency is vital for apps with a distributed user base, as it highlights geographical performance disparities. For real-time communication apps, handling packet loss and jitter is a non-negotiable requirement. Integrating these factors into your mobile app performance testing checklist ensures that your application provides a consistent, high-quality experience regardless of the user’s physical location or network hardware.

Integrating Performance into the DevOps Lifecycle

The structural evolution of enterprise software development necessitates that performance is no longer treated as a concluding validation phase but as an intrinsic element of the continuous delivery pipeline. By adopting a shift-left strategy, organizations can identify latency issues during the earliest development stages, effectively neutralizing technical debt before it compounds. This proactive integration ensures that every line of code is scrutinized for its impact on system resources, transforming your mobile app performance testing checklist from a static document into a dynamic, automated component of your CI/CD environment. Our DevOps Consulting framework emphasizes this cultural shift, aligning engineering efforts with high-level business ROI.

Automated performance regression acts as a critical safeguard, preventing incremental speed degradation with every code commit. To maintain this standard, development teams must establish strict performance budgets, which define acceptable thresholds for resource consumption and response times. When a build exceeds these predefined limits, automated gates within the deployment pipeline trigger immediate alerts, allowing for rapid remediation. This disciplined approach ensures that the final product remains lean and responsive, even as new features are introduced at a rapid cadence. By grounding your methodology in these rigorous standards, you achieve the institutional maturity required to operate within highly regulated, global industries through precision, predictability, and progress.

Automated Testing Frameworks

Selecting the right tools for Software Test Automation Services is paramount for building a resilient performance infrastructure. Your framework should facilitate the creation of scalable load scripts that accurately mimic real-world user journeys across diverse device profiles. Integrating these performance gates into platforms like Jenkins, GitLab, or Azure DevOps ensures that stability is verified at every stage of the lifecycle. This methodical automation reduces the reliance on manual oversight while increasing the precision of your quality assurance efforts through continuous detection, diagnosis, and delivery.

Performance Observability

Transitioning from basic monitoring to deep system observability allows enterprises to analyze log data and predict performance failures before they manifest as user-facing issues. By utilizing APM tools and AI-driven analytics, technical managers can perform sophisticated root cause analysis of lag, identifying the exact microservice or database query responsible for latency. This level of visibility provides the peace of mind that comes from comprehensive risk reduction and operational stability. If your organization is ready to modernize its delivery pipeline, consult with our DevOps experts to integrate a high-performance culture into your existing infrastructure.

Strategic QA Partnership: Elevating Performance with Test Triangle

Managing the intricate requirements of the 2026 digital landscape requires more than just a mobile app performance testing checklist; it demands a synergy between technical rigor and strategic foresight. As a reliable long-term collaborator, Test Triangle provides high-level IT Consulting designed to manage the complex digital infrastructures of global enterprises with expertise and precision. We focus on risk reduction and organizational progress, ensuring that your digital transformation initiatives are supported by a steady hand in a fast-changing technological environment. By aligning technical execution with business outcomes, we empower your leadership to make data-driven decisions that foster sustainable growth and operational stability.

Our commitment to excellence is reflected in our flexible Staffing Solutions, which provide access to specialized performance engineers capable of handling the most demanding QA workflows. Whether you’re optimizing for the latest iOS 26 features or ensuring Android 17 compatibility, our experts integrate seamlessly into your existing teams to deliver measurable results. We believe in an adaptable approach to service delivery, combining human expertise with industry-leading tools to assess, automate, and accelerate your path to market. This disciplined methodology ensures that your application meets the high standards of quality and security expected by today’s sophisticated user base.

Custom QA and Staffing Models

Bridging the talent gap in specialized performance engineering often requires a versatile, globally-minded strategy. Through our Managed Outsourcing Services, enterprises can reduce operational overhead while significantly increasing the quality of their performance assurance protocols. This model allows you to scale your QA team dynamically, providing the agility needed for major product launches without the long-term burden of internal recruitment. Our remote and offshore experts bring institutional maturity to every project, ensuring that your mobile app performance testing checklist is executed with the highest degree of technical discipline.

Enterprise Platform Optimisation

Specialized enterprise ecosystems like Atlassian and ServiceNow require a unique approach to mobile performance that standard QA providers often overlook. Our expertise in Atlassian Implementation ensures that your mobile integrations remain responsive and scalable under heavy enterprise loads. Similarly, we specialize in ServiceNow Consulting Services to ensure that mobile interfaces provide the efficiency required for modern IT service management. If your organization is ready to elevate its performance standards, the next step is to request a comprehensive performance audit to identify and eliminate hidden bottlenecks within your digital infrastructure.

Future-Proofing Enterprise Mobile Excellence

In the rapidly shifting technological landscape of 2026, maintaining a competitive edge requires a disciplined commitment to technical rigor and operational stability. By implementing a DevOps-aligned mobile app performance testing checklist, your organization can move beyond reactive troubleshooting to embrace a culture of precision, pace, and performance. This strategic evolution ensures that your digital infrastructure remains resilient across global networks while consistently meeting the high standards of a sophisticated user base through methodical detection, diagnosis, and delivery.

As an Atlassian Gold Solution Partner and Strategic ServiceNow Implementation Partner, Test Triangle acts as a reliable long-term collaborator for enterprises navigating large-scale digital transformations. Our global presence and specialized QA expertise provide the peace of mind derived from risk reduction and the empowerment found in scalable growth. We invite you to secure your application’s future with Test Triangle’s Performance Testing Services and transform your technical KPIs into tangible business ROI. Your journey toward seamless user experiences and sustained market leadership begins with a partnership built on stability, precision, and trust.

Frequently Asked Questions

What is the most critical metric in a mobile app performance testing checklist?

App load time and crash-free user rates represent the most critical indicators within any mobile app performance testing checklist. Industry benchmarks for 2026 dictate that applications must become interactive within two seconds to avoid immediate user abandonment. Additionally, maintaining a crash-free rate above 98 percent ensures the operational stability required for enterprise-level user retention and long-term brand loyalty across diverse hardware ecosystems.

How often should I perform mobile performance testing in a DevOps cycle?

Performance testing should be integrated continuously into the DevOps cycle through automated regression suites triggered by every code commit. This shift-left approach identifies latency issues during the earliest development stages, preventing technical debt from compounding over time. By establishing automated performance gates in your CI/CD pipeline, you ensure that speed and stability are verified through every iteration of the software lifecycle.

Can I rely on simulators for performance testing, or do I need real devices?

While simulators provide initial utility during early development, real devices are essential for capturing accurate hardware interactions and thermal impacts. Simulators cannot replicate the nuances of GPU throttling, sensor drain, or unpredictable network jitter found on physical handsets like the iPhone 17 or Galaxy S26. Utilizing a diverse real-device cloud ensures your application remains resilient across varying hardware specifications and environmental conditions.

How does battery consumption affect my app’s performance ranking?

Excessive battery consumption negatively impacts your app’s ranking by triggering OS-level energy warnings and increasing uninstallation rates. Both Apple and Google utilize performance vitals as primary ranking factors in 2026; applications that drain resources excessively are deprioritized in search results. Monitoring power-hungry background processes ensures your application remains compliant with the efficiency standards required for high global visibility and user satisfaction.

What is the difference between load testing and stress testing for mobile apps?

Load testing evaluates application behavior under expected user volumes to ensure consistent response times during normal operation. In contrast, stress testing pushes the infrastructure to its absolute breaking point to identify how the system fails and recovers under extreme conditions. Both methodologies are vital components of a comprehensive mobile app performance testing checklist, providing the technical rigor needed for scalable growth during peak traffic events.

How do I test mobile app performance for users with poor network connectivity?

Testing for poor connectivity involves network latency emulation to simulate 3G, 4G, and high-jitter environments. This process ensures that your application implements graceful degradation and robust offline functionality when a stable connection is unavailable. By analyzing data payload sizes and API response times under these constrained conditions, you can optimize the user experience for a globally distributed audience operating on inconsistent infrastructure.

What are performance budgets, and how do they help development teams?

Performance budgets are predefined thresholds for metrics such as bundle size, CPU usage, and load times that development teams must not exceed. These budgets act as a strategic framework for managing technical debt and ensuring that new features don’t compromise system responsiveness. By adhering to these limits, teams maintain the institutional maturity required to deliver lean, high-performance applications that align with technical KPIs and business ROI.

Should I outsource my mobile performance testing or keep it in-house?

The decision to outsource performance testing often depends on the need for specialized expertise and flexible scaling during major product launches. Partnering with an external provider for performance testing or IT staffing services allows enterprises to bridge the talent gap with offshore experts while reducing internal overhead. This strategic collaboration provides the peace of mind that comes from comprehensive risk reduction and expert oversight of complex digital infrastructures.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.
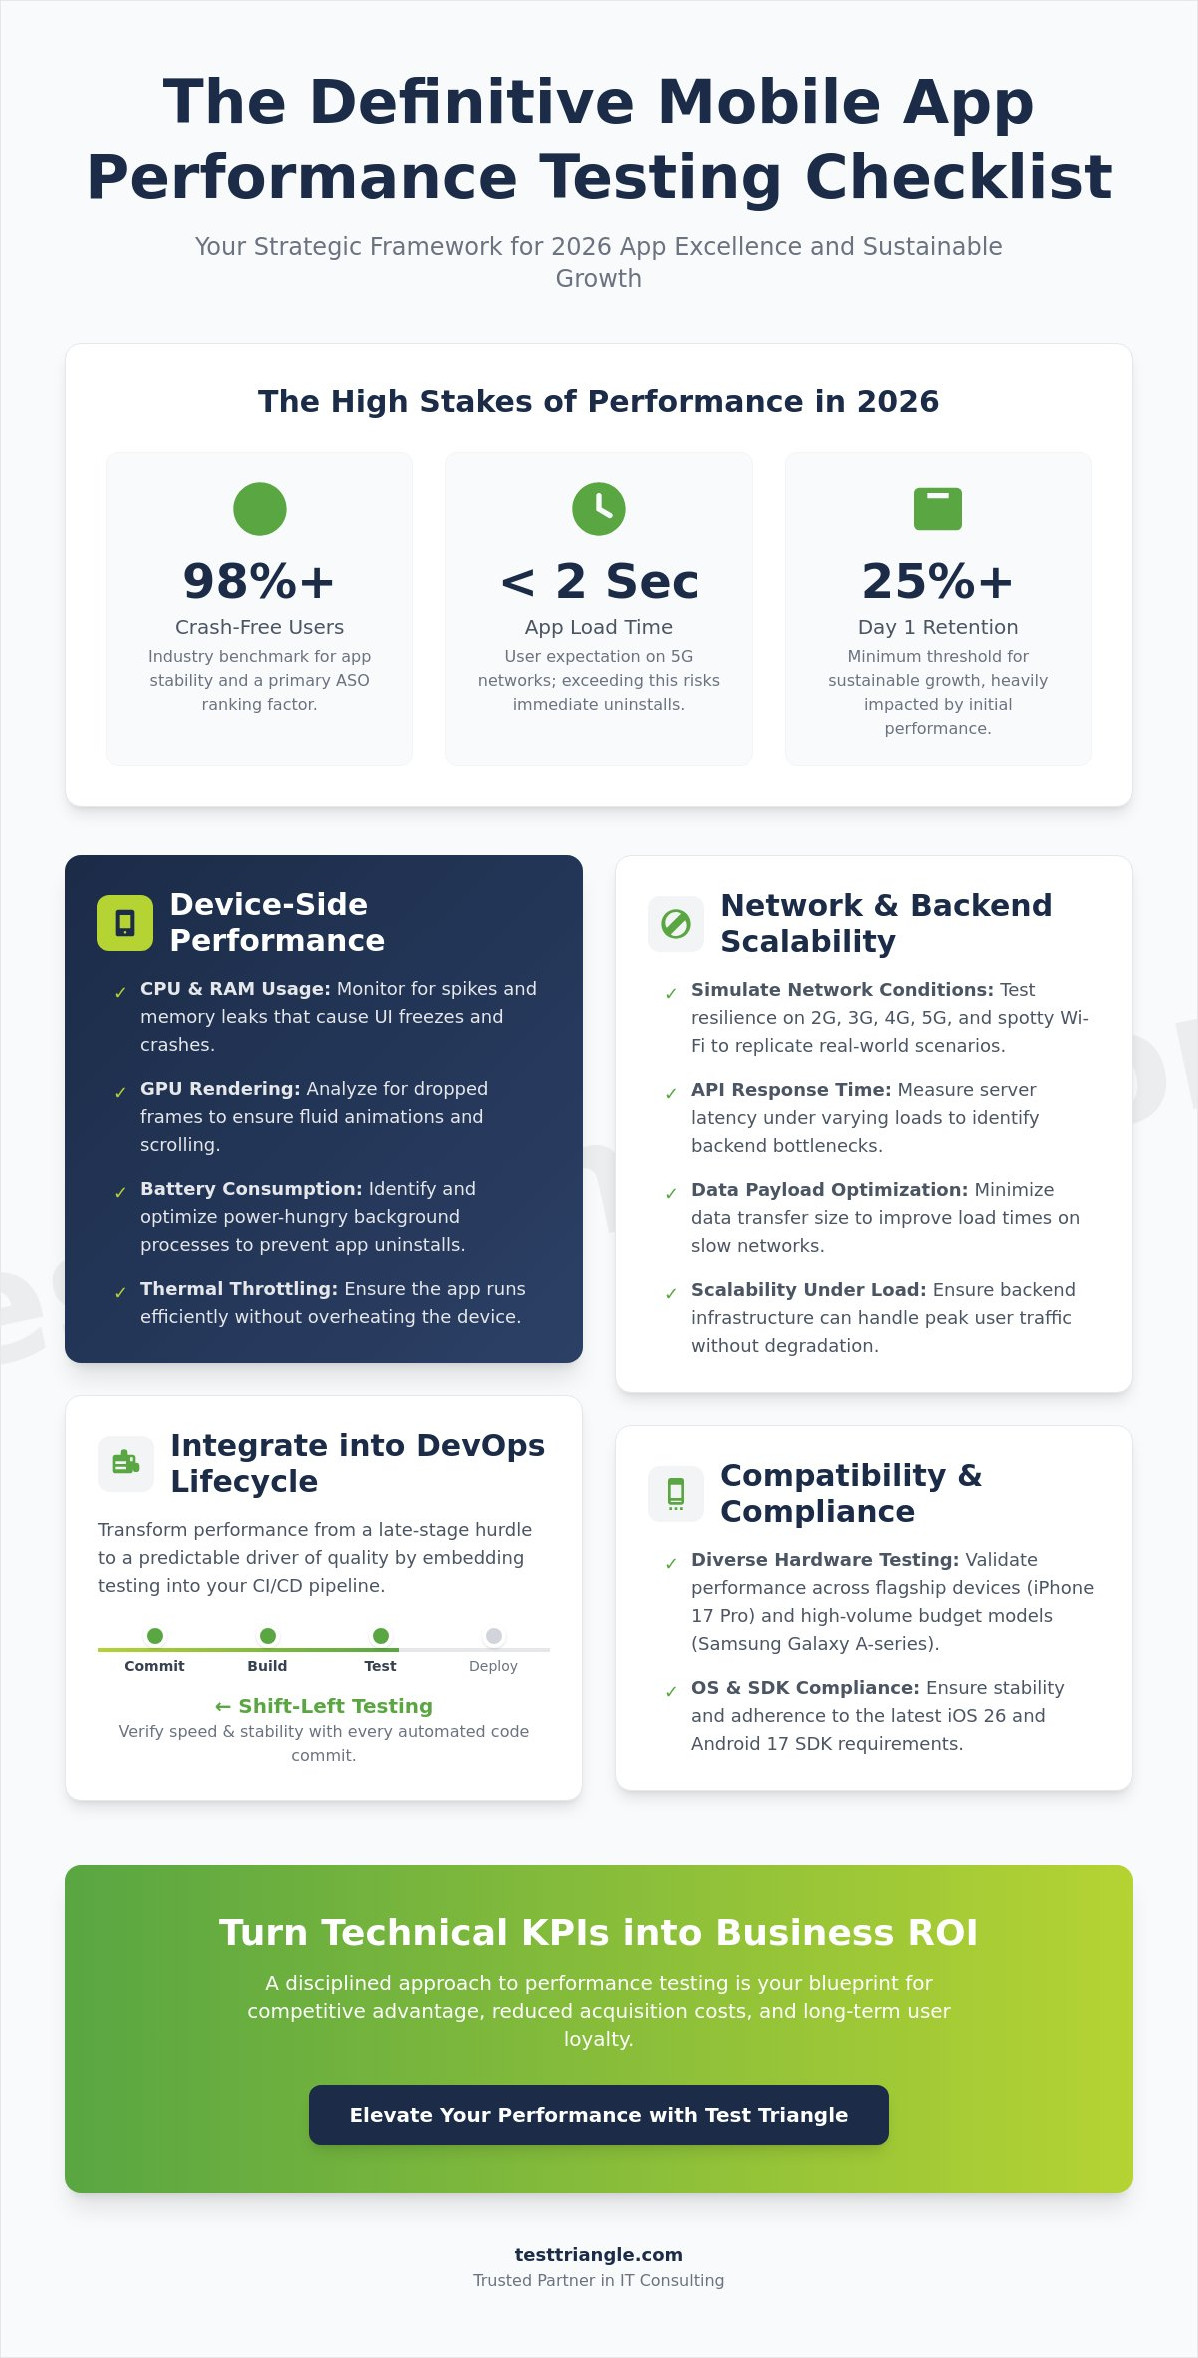

With 43% of websites currently failing the 200ms Interaction to Next Paint (INP) threshold, the technical margin for error has never been thinner for global enterprises. You understand that a mere one-second delay in page load time can trigger a 7% reduction in conversions, potentially costing your organization millions during peak volatility. Implementing rigorous load testing for ecommerce black friday 2026 is no longer a seasonal checkbox; it is a strategic necessity to protect your digital ecosystem from catastrophic system failure and unrecovered revenue loss.

We agree that the fear of third-party API instability and the difficulty of simulating realistic, high-concurrency user behavior are significant hurdles for any digital transformation leader. This guide provides the strategic framework you need to master your infrastructure readiness and ensure your platform remains resilient under the most intense traffic surges. By examining how to identify hidden bottlenecks and validate your infrastructure spend, you will move from reactive troubleshooting to a state of authoritative, crash-free readiness that delivers precision, performance, and peace-of-mind.

Key Takeaways

  • Evaluate the impact of AI-driven personalization engines on server capacity to ensure your infrastructure can withstand the sophisticated demands of the 2026 retail landscape.
  • Navigate the performance testing hierarchy by integrating stress, spike, and soak simulations into your strategy for load testing for ecommerce black friday 2026.
  • Identify invisible system bottlenecks by analyzing the technical debt often hidden within headless architectures and the limitations of automated cloud scaling.
  • Adopt a phased, four-month readiness roadmap that utilizes DevOps Consulting to automate testing protocols and secure long-term operational stability.
  • Mitigate high-stakes risks through managed quality assurance, positioning your organization for a crash-free event via strategic technical partnership.

The Strategic Imperative of Load Testing for Black Friday 2026

Software load testing is the strategic simulation of high-volume traffic designed to expose architectural weaknesses and validate system resilience before they manifest as customer-facing failures. For enterprises orchestrating load testing for ecommerce black friday 2026, this process has evolved from a seasonal checkbox into a fundamental pillar of digital assurance. We define Software load testing as the rigorous evaluation of how a system behaves under specific expected loads, ensuring that every microservice and database query performs optimally when concurrency peaks.

The 2026 retail landscape introduces unprecedented technical pressure. Hyper-personalization engines and AI-driven shopping assistants now generate massive server-side computations for every individual user session. It’s no longer enough to handle a high volume of static requests; your infrastructure must now process complex, intelligence-heavy interactions in real-time. The goal is a frictionless customer experience where the system remains invisible, even under maximum stress, preventing the catastrophic revenue loss associated with site instability.

Quantifying the “Cost of a Second” reveals the high stakes of this preparation. Research indicates that a single second of latency can trigger a 7% reduction in conversions. In an era where Black Friday sales have reached record-breaking heights of $74 billion globally, these milliseconds represent millions in abandoned carts. Comprehensive load testing for ecommerce black friday 2026 ensures that your platform doesn’t just stay online, but remains responsive enough to secure every potential transaction during the most volatile trading window of the year.

The Evolution of Peak Traffic in 2026

The composition of traffic has fundamentally changed, shifting from human-centric browsing to an environment dominated by high-frequency bot interactions and autonomous AI shoppers. These agents interact with your platform at speeds no human could match, placing unique strains on API gateways and inventory management systems. Traditional average load metrics are now obsolete. With 43% of websites currently failing the 200ms threshold for Interaction to Next Paint (INP), international retail brands must prioritize global latency testing to ensure that geographic distance doesn’t degrade the responsiveness modern consumers demand.

Risk Mitigation as a Business Value Driver

Strategic Performance Testing is a vital investment in brand equity and long-term customer loyalty. When a platform fails during a high-budget marketing campaign, the damage extends beyond immediate sales to include significant reputational harm. There are also critical legal implications to consider. With the EU AI Act and updated data privacy laws in states like Indiana and Kentucky now in effect, system instability can lead to compliance failures or data exposure during cascading failures. Validating your infrastructure spend through rigorous testing secures your organizational reputation and maximizes the ROI of your peak season initiatives.

The Performance Testing Hierarchy: Beyond Simple Load Simulation

Executing effective load testing for ecommerce black friday 2026 requires a multi-layered approach that transcends basic traffic volume simulations. While traditional methods focus on whether a site stays online, modern enterprise environments demand a more nuanced understanding of how various types of performance testing interact to secure the entire transaction lifecycle. By implementing a hierarchy of testing protocols, organizations can validate that their software and digital assurance testing efforts cover every conceivable failure point, from specific microservice latency to global system collapse.

Isolation testing serves as a critical diagnostic tool within this hierarchy. It allows technical teams to decouple specific components and identify which microservice or third-party API acts as the weakest link in the chain. For those seeking the highest level of resilience, chaos engineering introduces intentional, controlled failures into the environment. This advanced tier of readiness ensures that your system doesn’t just survive traffic; it possesses the self-healing capabilities required to maintain operations when unforeseen infrastructure issues arise during the peak shopping window.

Load vs. Stress vs. Spike Testing

Understanding the distinction between these methodologies is essential for building a robust load testing for ecommerce black friday 2026 strategy. Each serves a distinct purpose in identifying the difference between a “degradation point,” where performance begins to slow, and the “breaking point,” where the system fails entirely. Spike testing is particularly vital for simulating the sudden, extreme bursts of concurrency seen during flash sales or limited-time offers.

Test TypePrimary PurposeUser Load ProfileExpected Strategic Outcome
Load TestingValidate performance under expected peak traffic.Steady increase to anticipated maximum.Confirmation of baseline operational stability.
Stress TestingIdentify the absolute breaking point of the system.Traffic pushed beyond documented limits.Verified understanding of failure modes and recovery.
Spike TestingSimulate “Limited Time Offer” rushes.Sudden, extreme bursts of concurrency.Validation of auto-scaling and queue management.

The Role of Soak Testing in Peak Season

While spike tests handle the immediate rush, soak testing addresses the endurance required for a multi-day event. By maintaining a high load for 48 to 72 hours, teams can uncover memory leaks and database contention issues that remain hidden during shorter test cycles. This duration is also critical for validating auto-scaling cooldown periods. It ensures that infrastructure doesn’t prematurely scale down while secondary processes are still completing. To ensure your architecture is prepared for these sustained demands, you may wish to consult with a performance specialist regarding your current environment.

Load Testing for Ecommerce Black Friday 2026: A Strategic Readiness Guide

Identifying Invisible Bottlenecks in Modern Ecommerce Architectures

Relying solely on a cloud provider’s auto-scaling capabilities is a common strategic oversight. While horizontal scaling adds compute resources, it cannot resolve underlying architectural inefficiencies. In fact, rapid scaling can often exacerbate database deadlocks or reveal hidden synchronization issues that only manifest under the extreme concurrency of load testing for ecommerce black friday 2026. Modern headless commerce architectures, while offering flexibility, introduce a “headless tax.” Every interaction requires multiple API calls between decoupled layers, placing immense pressure on back-end services that might have been optimized for traditional monolithic structures. Without rigorous validation, these decoupled layers can become silent points of failure.

Database locking remains the primary cause of checkout failures during high-traffic events. When thousands of users attempt to update inventory or finalize payments simultaneously, poorly optimized query patterns lead to deadlocks that halt the entire transaction pipeline. These bottlenecks are often invisible during low-traffic periods but become catastrophic under peak demand. Integrating Performance Testing into your development lifecycle allows for the identification of these contention points long before they impact your revenue. It’s about achieving stability, scalability, and security through proactive technical discipline.

The Third-Party API Trap

Your platform’s performance is intrinsically linked to the stability of your external ecosystem. During peak events, a slow response from a credit card processor or a review widget can block critical threads, leading to abandoned carts. We recommend implementing strategies for “graceful degradation.” This ensures that if a non-essential service like a social media feed or a tracking script fails, the core checkout journey remains intact. Mocking these external responses during your test cycles is essential to isolate your internal system’s true capacity and ensure your site is not held hostage by a third-party vendor’s latency.

Microservices and Cascading Failures

Distributed systems are vulnerable to cascading failures where a single lagging service triggers a domino effect across the entire architecture. The “Circuit Breaker” pattern is a non-negotiable requirement for 2026 readiness. It prevents a failing service from being overwhelmed by continuous requests, allowing it the necessary time to recover. Without this protection, you risk “Retry Storms.” This occurs when automated retries from multiple services simultaneously hit a struggling component, effectively performing a self-inflicted DDoS attack on your own infrastructure. Testing these failover mechanisms is as important as testing the load itself.

A Phased Roadmap for Peak Season Readiness

Achieving operational resilience requires more than a last-minute stress test. For global enterprises, the journey toward successful load testing for ecommerce black friday 2026 must begin at least three to four months in advance. This lead time allows for the deep architectural adjustments identified in previous sections to be implemented without compromising the release cycle. By leveraging DevOps Consulting, organizations can automate these performance validations, moving away from manual, reactive checks toward a sophisticated “Shift-Left” methodology. This approach ensures that performance is validated at the code level before reaching staging, significantly reducing the cost of remediation.

The transition from synthetic testing to real-user monitoring (RUM) marks the final stage of this evolution. While synthetic tests provide a controlled baseline, RUM captures the actual experience of users across diverse geographies and device types. This dual-layered visibility is essential for identifying the “last mile” latencies that impact conversion rates. By integrating these insights into your Atlassian-managed workflows, your technical teams can maintain a unified view of system health and performance debt throughout the preparation phase.

Step 1: Baseline and Goal Setting

Establishing a baseline begins with a granular analysis of historical data from the 2025 peak season to set realistic growth targets for the coming year. Key Performance Indicators (KPIs) such as response time, throughput, and error rates must be defined against these projections. We prioritize the most critical user paths, specifically search functionality, cart additions, and the final checkout sequence, to ensure that high-value interactions remain frictionless even when concurrency reaches its zenith.

Step 2: Environment Mirroring and Scripting

Environment mirroring is a prerequisite for accuracy. Testing in a scaled-down environment often leads to false confidence; it fails to expose the database index issues or network latencies that only surface at production scale. We insist on full data parity, utilizing a production-sized database to identify long-term contention issues. Test scripts must be meticulously developed to include “think time” and varied user journeys, reflecting the non-linear way modern shoppers interact with AI-driven platforms.

Step 3: Execution and Iterative Optimization

The execution phase is an iterative “Test-Fix-Retest” cycle. A single test run is never sufficient to validate complex fixes. Utilizing software test automation services allows teams to run regression performance tests continuously as the infrastructure evolves. The final milestone is a full-scale simulation where the entire stack is tested at 150% of the expected peak load. To begin your architectural audit and secure your platform’s future, connect with our strategic consulting team today.

As global enterprises approach the final validation phase of their peak season roadmap, the transition from internal verification to managed digital assurance becomes a critical pivot point for risk mitigation. Test Triangle serves as a strategic visionary and practical partner, providing the technical rigor required to ensure your platform exceeds the unprecedented demands of the modern retail calendar. Implementing comprehensive load testing for ecommerce black friday 2026 requires more than just high-end tools; it demands the specialized expertise of a seasoned collaborator capable of translating technical metrics into operational certainty and executive peace of mind.

Our managed outsourcing services allow organizations to access specialized peak-season bursts of activity without the overhead of permanent internal expansion. This flexibility is complemented by our staffing solutions, which provide the niche expertise necessary for complex JMeter or Locust deployments. By integrating these resources with your existing Atlassian Implementation, we create a unified ecosystem where performance data flows directly into your development workflows. This synergy ensures that every bottleneck identified during load testing for ecommerce black friday 2026 is tracked, prioritized, and resolved with disciplined precision.

The Value of an Independent QA Partner

Internal development teams often fall victim to “development bias,” where familiarity with the codebase leads to overlooking subtle architectural flaws that only manifest under extreme stress. An independent partner provides an objective perspective, utilizing global testing teams to simulate authentic traffic patterns from diverse geographic regions. These experts don’t just deliver data; they interpret complex load test reports into actionable business intelligence. This process empowers your leadership to make informed decisions regarding infrastructure spend and marketing spend, ensuring that every dollar invested contributes to a stable, high-performing customer journey.

Ensuring Long-Term Stability Post-Black Friday

The value of a rigorous performance strategy extends far beyond the final checkout of the holiday weekend. By analyzing peak season data, we help you optimize your infrastructure costs during “normal” trading periods, ensuring you aren’t over-provisioning resources. The lessons learned during Black Friday are transformed into permanent CI/CD performance gates, preventing future code deployments from introducing regression issues. This commitment to continuous improvement is at the heart of our IT Service Management solutions, which prioritize long-term organizational progress over short-term fixes. To secure your digital future and validate your readiness for the upcoming surge, you should partner with Test Triangle for your 2026 performance strategy today.

Securing Your Competitive Advantage for the 2026 Peak Season

Mastering the complexities of modern retail requires a shift from reactive troubleshooting to a proactive, risk-based methodology. By prioritizing shift-left performance testing and addressing the bottlenecks inherent in decoupled architectures, your organization can transform technical vulnerabilities into a robust foundation for growth. We’ve explored how a phased roadmap ensures your platform remains frictionless even as AI-driven traffic peaks. Implementing rigorous load testing for ecommerce black friday 2026 is the definitive step toward protecting your revenue during the year’s most volatile trading window. Don’t leave your infrastructure’s resilience to chance when the stakes are at their highest.

As an Atlassian Gold Solution Partner with global delivery centers across Europe, North America, and Asia, Test Triangle brings institutional maturity to your digital assurance strategy. Our expertise in high-compliance sectors like Finance and Pharma ensures your infrastructure meets the highest standards of stability and security. We’re ready to act as your reliable long-term collaborator, providing the specialized insights needed to navigate this evolving landscape. Secure Your 2026 Peak Season Performance with Test Triangle and prepare your platform for unprecedented success. Your resilient future starts today.

Frequently Asked Questions

When should I start load testing for Black Friday 2026?

You should initiate your performance testing cycle at least three to four months before the peak event to allow sufficient time for identifying and remediating deep architectural flaws. Starting early ensures that your DevOps teams can integrate performance gates into the CI/CD pipeline, preventing late-stage code deployments from introducing regression issues that could compromise your 2026 readiness. This lead time is essential for conducting multiple iterations of the “Test-Fix-Retest” cycle to achieve optimal stability.

How much traffic should I simulate for a Black Friday load test?

We recommend simulating at least 150% of your anticipated peak traffic to identify the absolute breaking point of your infrastructure and validate your failover mechanisms. By analyzing historical data from the 2025 peak season and projecting growth targets for 2026, you can establish a realistic baseline that accounts for both human shoppers and the increasing volume of autonomous AI shopping agents. Testing beyond the expected peak provides the technical assurance needed to handle unexpected viral surges or aggressive marketing campaigns.

Can cloud auto-scaling replace the need for performance testing?

Cloud auto-scaling cannot replace the need for rigorous performance testing because it only addresses compute capacity rather than architectural efficiency or database health. Automated scaling often masks underlying issues like database deadlocks, poorly optimized API calls, or memory leaks, which can lead to cascading failures even when additional resources are provisioned. Relying on scaling alone without validating your system’s limits often results in unexpected costs and unrecovered revenue during high-concurrency events.

What are the most common bottlenecks found during ecommerce load testing?

The most frequent bottlenecks identified during load testing for ecommerce black friday 2026 include database contention, third-party API latency, and the technical “tax” associated with headless commerce architectures. These invisible points of failure often remain hidden during normal trading periods but become catastrophic under extreme concurrency. Identifying these issues early allows your organization to implement strategies like the “Circuit Breaker” pattern or graceful degradation to maintain a frictionless customer journey when individual services lag.

How do I test third-party payment gateway performance without making real charges?

You can validate payment workflows by utilizing vendor-provided sandbox environments or by mocking third-party responses to simulate various success and failure scenarios under load. This methodology allows your technical teams to isolate internal performance and test how the system handles external timeouts without incurring transaction fees or processing real financial data. It’s a critical step for ensuring that your checkout sequence remains resilient even if an external processor experiences its own peak-season latency.

What is the difference between load testing and stress testing for retail?

Load testing validates system behavior under the expected peak volume to ensure operational stability, while stress testing pushes the system beyond its documented limits to identify its absolute breaking point. While load testing confirms that you can meet your business goals, stress testing reveals how the system fails and how effectively it recovers. Both methodologies are essential components of a comprehensive digital assurance strategy, providing the data needed to manage infrastructure spend and mitigate the risk of catastrophic failure.

How does headless commerce affect my load testing strategy?

Headless commerce increases the complexity of your strategy by requiring the validation of decoupled front-ends and the resulting pressure on back-end APIs. Every user interaction in a headless environment typically triggers multiple API calls across distributed systems, which necessitates a deeper focus on inter-service communication latency and microservice resilience. Your testing scripts must accurately reflect these complex interaction patterns to ensure that your API gateway doesn’t become a single point of failure during high-traffic bursts.

What tools are best for simulating millions of concurrent users in 2026?

For simulating massive concurrency in 2026, industry-standard platforms like Apache JMeter 5.6.3 and Locust 2.44.0 remain the preferred choices for global enterprises due to their scalability and flexibility. These tools allow for the creation of sophisticated, intelligence-heavy interaction models that mimic the behavior of modern shoppers and AI assistants. When integrated with a managed performance testing framework, these tools provide the granular visibility required to validate end-to-end journeys across diverse geographic regions and device types.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.

How can your organization maintain a “Compliance-First, Agile-Always” posture when the deadline for GAMP 5 Second Edition alignment arrives in August 2026? You’ve likely realized that finding professionals who possess both technical agility and deep Computer System Validation (CSV) experience is becoming the industry’s most significant hurdle. It’s frustrating to watch critical digital transformation projects stall because IT talent doesn’t fully grasp the nuances of 21 CFR Part 11 or the impending EU GMP Annex 11 revisions.

For leaders looking to navigate this dual imperative, it is helpful to explore Healthcare & Life Sciences Staffing options that provide access to specialists who understand the rigorous demands of the pharma sector.

This guide demonstrates how to refine your Pharma IT Staffing strategy to secure specialized experts who bridge the gap between life sciences innovation and rigorous regulatory compliance. By aligning your recruitment methodology with high-level business outcomes, you’ll learn how to reduce time-to-hire for specialized roles while ensuring 100% compliance in every technical placement. We’ll examine how a focus on precision, performance, and partnership can optimize your IT infrastructure through the strategic implementation of platforms like Atlassian and ServiceNow.

Key Takeaways

  • Understand the critical transition from generalist support to specialized validation roles that safeguard data integrity within GxP environments.
  • Identify the core technical competencies, including Atlassian and ServiceNow expertise, required to automate complex pharmaceutical workflows while ensuring regulatory alignment.
  • Evaluate the strategic advantages of varied engagement models, such as Recruitment Outsourcing Managed Services, to achieve the optimal balance of operational flexibility and technical rigor.
  • Refine your Pharma IT Staffing process with structured assessment techniques designed to verify a candidate’s mastery of FDA and EMA regulatory frameworks.
  • Discover how a long-term partnership with a strategic visionary can future-proof your digital infrastructure through precision, progress, and partnership.

Understanding the Evolution of Pharma IT Staffing

Pharma IT Staffing is no longer just about filling technical vacancies; it’s the strategic intersection of high-level digital execution and uncompromising regulatory adherence. In the complex field of Pharmacoinformatics, the demand for generalist IT support has been replaced by a need for specialists who understand the scientific and legal context of their work. As we move through 2026, the industry has shifted away from “IT that works” toward IT that is audit-ready, resilient, and fully validated. This evolution requires a disciplined, versatile, and globally-minded approach to talent acquisition.

The current landscape is defined by a dual imperative: accelerating digital transformation while maintaining absolute compliance with GxP and 21 CFR Part 11 standards. It’s not enough to hire a DevOps engineer who can manage a pipeline. You need a professional who understands how automated deployments interact with computerized system validation (CSV) protocols in a highly regulated environment. This ensures stability, scalability, and success across the entire drug development lifecycle.

The Compliance-Technology Gap

Generalist staffing models often falter in the life sciences because they overlook the rigorous documentation required for regulatory approval. By August 2026, organizations are expected to align fully with GAMP 5 Second Edition, which emphasizes a risk-based approach to AI and cloud computing. This regulatory shift means that technical placements must now possess a deep understanding of data integrity and lifecycle management. Without this specialized knowledge, technical implementations risk becoming compliance liabilities rather than operational assets. We focus on bridging this gap by identifying talent that treats compliance as a baseline requirement rather than an afterthought.

Digital Transformation in Life Sciences

The transition toward AI-driven drug discovery and decentralized clinical trials has created an unprecedented demand for data integrity experts and cloud migration specialists. Modernizing legacy laboratory systems is a necessity for survival in a market where R&D costs continue to climb. Through specialized staffing solutions, enterprises can access the talent needed to manage complex infrastructure upgrades while ensuring that every byte of data remains secure. This methodology connects technical expertise to business results, providing the peace of mind that comes from reduced risk and systemic improvement.

Essential Roles and Technical Competencies for 2026

Identifying the right human capital is the most critical factor in achieving technological maturity in a market defined by rapid change and heavy regulation. As 68% of pharmaceutical HR leaders identify talent scarcity as their primary operational risk, the focus of Pharma IT Staffing has shifted toward professionals who can manage the delicate balance of innovation and compliance. It’s no longer sufficient to hire for technical proficiency alone; the modern life sciences enterprise requires individuals who understand the scientific implications of their digital work. With senior IT consultant rates reaching $250 per hour in 2026, the financial stakes of every placement have never been higher.

DevOps engineers with specific life sciences experience are currently the most sought-after assets in the industry. These professionals possess the rare ability to bridge the gap between rapid software deployment and the rigid requirements of GxP environments. Alongside them, the Validation Engineer has emerged as a cornerstone of the modern IT team. This role ensures that every system update is documented, verified, and compliant with 21 CFR Part 11, providing the peace of mind that comes from a resilient and audit-ready infrastructure.

Enterprise Platform Specialists

Integrating Atlassian Consulting into your R&D strategy allows for the seamless management of clinical trial workflows through Jira and Confluence. These tools, when managed by specialists, provide a single source of truth for complex global projects. Similarly, leveraging ServiceNow experts for compliant IT Service Management ensures that internal processes remain transparent and scalable. Research from Kearney suggests that strategic talent in digital transformation is the true differentiator for success, rather than the tools themselves. This methodical approach to platform management reduces operational friction and empowers teams to focus on core pharmaceutical innovation.

Quality Assurance and Validation Experts

The demand for manual and automated testing professionals has surged as companies look to protect their data integrity and intellectual property. In 2026, security testing is not a separate phase but an integrated component of the development lifecycle. Sourcing talent for large-scale data migration projects requires a disciplined eye for detail to prevent data loss during the move to cloud-based systems. A reliable partner can help you discuss your specific talent requirements to ensure your team is equipped for these challenges. Our focus remains on providing the human expertise needed to support organizational progress through every stage of the digital journey.

  • Cloud Architects with GxP experience to manage $45 billion market growth in life sciences software.
  • AI Engineers capable of integrating machine learning into the drug discovery lifecycle.
  • Cybersecurity Architects specializing in protecting decentralized clinical trial data.
  • ITSM Specialists focused on ServiceNow workflow automation and audit-readiness.

Pharma IT Staffing: A Strategic Guide to Life Sciences Talent in 2026

Evaluating Pharma IT Staffing Models: FSP vs. Contract vs. Managed Services

Selecting the appropriate engagement model is a strategic decision that directly impacts an organization’s ability to remain agile while upholding strict regulatory standards. As the pharmaceutical industry moves toward a blended workforce, the choice between permanent, contract, and managed service models must be dictated by the specific technical requirements and the associated regulatory risk. Since 2023, the demand for contingent labor in the life sciences has grown by 41%, reflecting a broader trend toward accessing specialized expertise for project-based needs. This shift allows enterprises to maintain a core team of strategic leaders while utilizing flexible layers for technical execution, ensuring Scalability, Security, and Stability across the digital landscape.

While many organizations utilize the Functional Service Provider (FSP) model for clinical data management, this approach often lacks the technical depth required for complex IT infrastructure projects. For long-term operational stability and systemic improvement, managed outsourcing services offer a more robust framework. This model provides the peace of mind that comes from risk reduction, as the provider takes full accountability for service delivery and compliance. By aligning IT talent with high-level business outcomes, pharmaceutical leaders can focus on innovation rather than the administrative burden of talent acquisition.

Contract and Temporary Staffing

Utilizing temporary contract staff is a highly effective strategy for managing peak project demands, such as large-scale system migrations or the impending August 2026 GAMP 5 alignment deadline. This model offers a 3x faster time-to-fill for open roles compared to traditional permanent hiring, allowing for rapid response to changing market conditions. In 2026, the strategic advantage of remote and offshore IT resources is undeniable, providing access to global talent pools while managing costs through margin-based billing. This flexibility ensures that specialized validation or DevOps projects don’t stall due to local talent scarcity.

Managed Services and Strategic Partnerships

Transitioning from simple staffing to a Managed Service Provider (MSP) model represents a shift toward a long-term collaborative partnership. This approach integrates industry-leading platforms like ServiceNow directly into the service description, ensuring that Service Level Agreements (SLAs) are closely aligned with pharmaceutical quality standards. A strategic partner acts as a steady hand, providing the human expertise and technical tools necessary for sustainable growth. This methodical rhythm of service delivery reduces the internal burden of recruitment and training, allowing your internal leadership to prioritize large-scale technological evolution and long-term success.

Ensuring Compliance and Cultural Fit in Technical Recruitment

Success in Pharma IT Staffing depends on more than just matching a resume to a job description; it requires a disciplined verification of a candidate’s “compliance DNA.” In a sector where a single data integrity failure can jeopardize years of research, the primary objection for hiring managers is often whether a technical expert truly respects the GxP environment. You aren’t just looking for someone who can write code. You’re looking for someone who understands that in a validated system, every change must be documented, tested, and approved. This institutional maturity is what separates a standard IT professional from a life sciences specialist who values stability and precision.

Establishing a “compliance culture” within technical teams ensures that regulatory requirements are viewed as a catalyst for quality rather than a hurdle to speed. When your IT staff operates with this mindset, they provide the peace of mind that comes from risk reduction and systemic improvement. Leveraging specialized recruitment and talent acquisition fees for expert vetting allows enterprises to outsource the heavy lifting of regulatory screening to a partner who understands the complex nuances of pharmaceutical manufacturing.

Vetting for Regulatory Competence

Vetting for regulatory competence involves structured interview techniques that go beyond surface-level definitions. Ask candidates to describe their specific role during a past FDA or EMA audit; their answer should reveal their proficiency in validated software environments and their commitment to data integrity. Background checks and credential verification are non-negotiable in this highly regulated industry. A methodical approach to screening identifies individuals who can maintain 100% compliance while managing complex digital infrastructures. To ensure your next hire possesses these critical traits, consult with our talent acquisition experts for a specialized vetting strategy.

Bridging the Gap Between IT and Science

Bridging the gap between IT and science requires technical staff to understand the pharmaceutical “Molecule to Market” lifecycle. When a DevOps engineer understands how their deployment pipeline affects clinical researcher productivity, they become a strategic collaborator rather than a mere service provider. Onboarding strategies must emphasize this connection, fostering a culture where technical teams feel deeply invested in long-term patient outcomes. This alignment ensures that digital transformation remains a practical tool for organizational progress, allowing your business to operate as a steady hand in a fast-changing technological landscape.

Future-Proofing Your Pharma IT Infrastructure with Test Triangle

Test Triangle stands as a strategic visionary in the life sciences sector, redefining the standards of Pharma IT Staffing by merging human expertise with technical rigor. We don’t just fill roles; we build resilient ecosystems. Our approach moves beyond the transactional nature of traditional recruitment to provide a steady hand in a fast-changing technological landscape. By aligning specialized talent with high-level business objectives, we ensure that your digital infrastructure remains validated, agile, and fully prepared for the regulatory demands of 2026. This commitment to institutional maturity provides the peace of mind derived from risk reduction and long-term operational stability.

A Blended Approach to Talent and Technology

By integrating specialized staffing solutions with high-level DevOps consulting, we empower life sciences enterprises to accelerate their digital transformation journeys without compromising on quality. This methodology connects technical execution to specific business outcomes, ensuring that every professional placed within your organization contributes to systemic improvement. We offer customized training programs for all placed staff, which guarantees immediate ROI and seamless integration into your existing GxP workflows. This synergy between talent and technology allows your internal leadership to focus on large-scale innovation while we manage the complexities of technical execution.

The Test Triangle Advantage

Our proven track record as one of the premier IT staffing agencies for pharmaceutical industry is built on a foundation of precision, progress, and partnership. We leverage our deep-rooted partnerships with industry-leading platforms like Atlassian and ServiceNow to source niche talent that understands both the software and the scientific context. With access to a global pool of pre-vetted, compliance-aware professionals, we provide the versatile human capital necessary to manage complex digital infrastructures across diverse regions. Our global presence ensures that talent scarcity never becomes an operational risk for your R&D or manufacturing projects.

Navigating the complexities of recruitment and talent acquisition in 2026 requires a partner who is deeply invested in your long-term success. We provide strategic guidance that bridges the gap between technical managers and executive leadership, ensuring that every staffing decision supports organizational progress. Our disciplined approach to vetting and placement means your team is always equipped with the specialized skills needed to maintain 100% compliance in an increasingly scrutinised regulatory environment. Partnering with us means choosing a reliable collaborator dedicated to empowering your enterprise through large-scale technological evolution and sustainable growth.

Building a Resilient Digital Foundation for 2026

The transition toward a “Compliance-First, Agile-Always” infrastructure requires a deliberate shift in how your organization approaches human capital. You’ve identified that the intersection of technical proficiency and regulatory awareness is the new baseline for success in a landscape defined by evolving GAMP 5 and Annex 11 requirements. Establishing a long-term partnership with a strategic visionary ensures that your Pharma IT Staffing needs are met with precision, providing the stability required for large-scale technological evolution and systemic improvement.

As an Atlassian Platinum Solution Partner and ServiceNow Premier Partner, we leverage our ISO 9001:2015 certified quality management to deliver pre-vetted experts who understand the scientific implications of their technical work. This disciplined methodology reduces time-to-hire while reinforcing your data integrity protocols across the entire drug development lifecycle. We remain committed to your long-term success by providing a steady hand through every phase of digital transformation, allowing your leadership to focus on core pharmaceutical innovation with total peace of mind.

Secure your specialized Pharma IT talent with Test Triangle today to ensure your team is equipped for the challenges of 2026 and beyond. We look forward to empowering your enterprise through human expertise and technical excellence.

Frequently Asked Questions

What is the difference between general IT staffing and Pharma IT staffing?

Pharma IT staffing differs from general recruitment by requiring a deep understanding of GxP environments and computerized system validation (CSV). While general IT focuses on technical proficiency, life sciences roles demand professionals who can navigate the rigid documentation standards of the FDA and EMA. This ensures that every digital implementation supports data integrity and patient safety from the outset.

How do you ensure IT staff are compliant with FDA 21 CFR Part 11?

Ensuring compliance with FDA 21 CFR Part 11 involves verifying a candidate’s mastery of electronic records and signature protocols through structured technical assessments. We evaluate their ability to implement audit trails and security controls within validated systems. This disciplined vetting process guarantees that every professional understands the legal implications of their technical work.

What are the typical recruitment fees for specialized Pharma IT roles in 2026?

Recruitment fees for specialized roles in 2026 vary based on the complexity of the position and the engagement model chosen. Organizations should evaluate these costs as a strategic investment in risk reduction and long-term operational stability. It’s advisable to consult with a specialized partner to discuss specific talent acquisition structures tailored to your digital transformation goals.

Can I use remote or offshore IT staff for validated pharmaceutical projects?

Remote or offshore IT staff can be effectively utilized for validated projects if they operate within a secure, GxP-compliant framework. The global nature of Pharma IT Staffing in 2026 allows enterprises to access niche talent pools while maintaining strict data governance. Success depends on clear communication protocols and a partner who can manage the logistical complexities of international compliance.

Which IT roles are currently in highest demand within the life sciences sector?

High-demand roles currently include Validation Engineers, DevOps Engineers with life sciences experience, and AI Specialists capable of managing drug discovery data. There’s also a significant need for Cybersecurity Architects who can protect decentralized clinical trial infrastructures. These roles are essential for maintaining a resilient and audit-ready digital ecosystem.

How does a Functional Service Provider (FSP) model differ from traditional staffing?

The Functional Service Provider (FSP) model focuses on outsourcing an entire department or project function rather than individual roles. Unlike traditional staffing, which provides human capital for specific vacancies, the FSP model offers a more integrated approach to technical execution. This allows pharmaceutical companies to scale their operations while maintaining high standards of quality and efficiency.

What technical certifications should I look for in a Pharma IT candidate?

Look for candidates who combine platform-specific certifications, such as Atlassian Certified Professional or ServiceNow System Administrator, with industry-recognized credentials like GAMP 5 training. Technical proficiency must be paired with a demonstrated understanding of quality risk management. This combination ensures the professional can handle both the technical tools and the regulatory context.

How can specialized staffing help with Atlassian or ServiceNow implementation?

Specialized staffing provides access to consultants who understand how to configure Atlassian and ServiceNow platforms specifically for pharmaceutical workflows. These experts ensure that your IT Service Management tools are fully validated and capable of managing complex clinical data. This strategic alignment reduces implementation risks and accelerates the path to digital maturity.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.
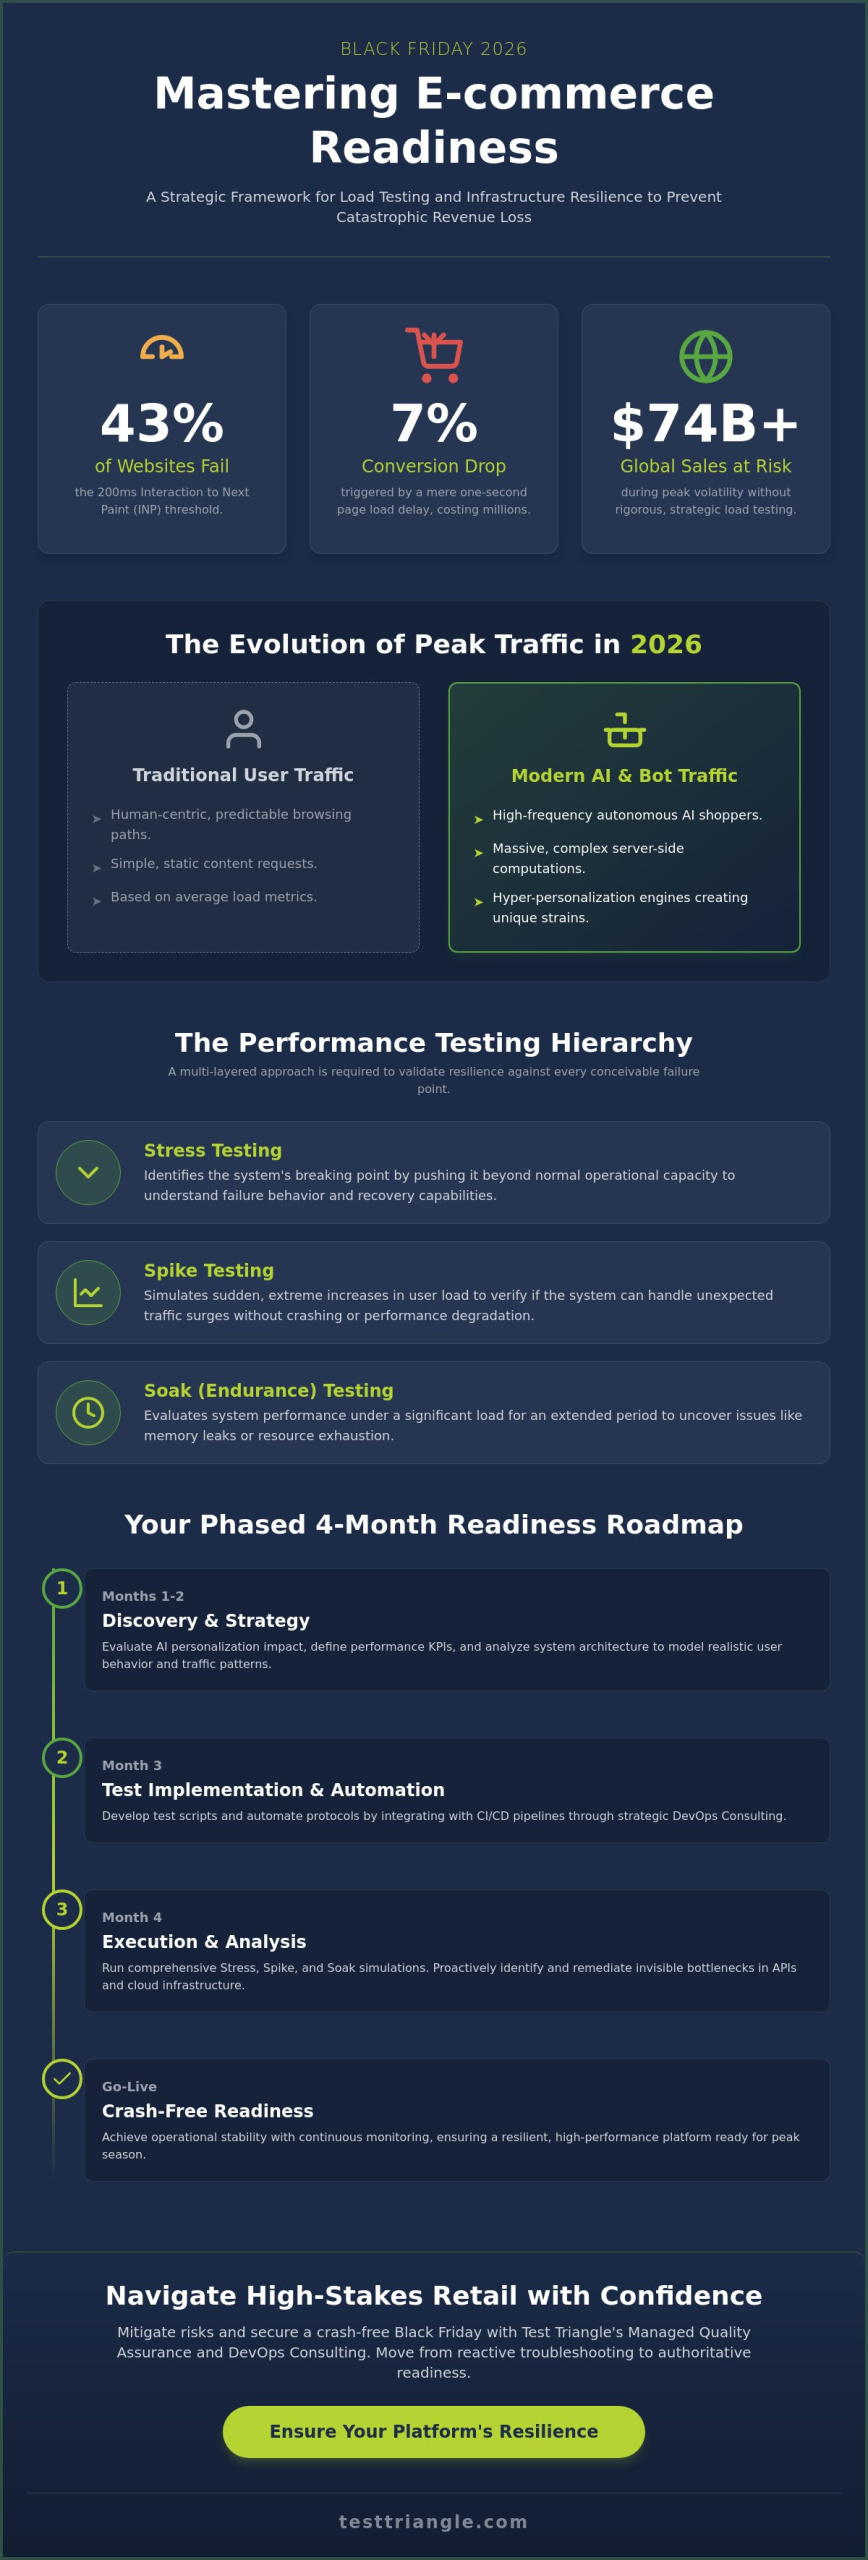

By the end of 2026, Gartner projects that 80% of large software organizations will have established platform engineering teams to manage infrastructure complexity. Despite these structural shifts, many enterprise leaders still struggle with release cycles that lag behind market demands and specialized talent that leaves as quickly as they arrive. You likely hired for DevOps engineering expecting immediate agility, yet you might find your teams caught in a confusing overlap of SRE, SysAdmin, and developer responsibilities. It’s a common frustration to see high-level technical investments fail to translate into measurable business outcomes.

You’re not alone in feeling that the promise of automation hasn’t fully delivered on its potential for reliability and speed. This article serves as your strategic guide to debunking the five critical myths that currently stall digital transformation efforts. We’ll provide a clear framework for defining the DevOps engineering role within a modern enterprise, ensuring your technical roadmap aligns perfectly with long-term operational stability. From understanding the impact of AI-driven SRE tools to optimizing your deployment frequency, you’ll discover how to turn technical friction into a disciplined engine for growth.

Key Takeaways

  • Transition from reactive infrastructure management to a proactive, code-driven methodology that aligns your technical execution with core business objectives.
  • Discover why human-centric scaling and team collaboration are superior to the “lone wolf” specialist model for sustainable DevOps engineering success.
  • Learn to avoid the toolchain trap by prioritizing process refinement and cultural alignment over the mere implementation of high-end automation software.
  • Master the “Day 2 Operations” mindset to ensure your digital transformation remains a continuous cycle of optimization rather than a static, one-time project.

Myth 1: Debunking the Identity Crisis. DevOps Engineering is Just “SysAdmin 2.0”

Many enterprise leaders mistake a title change for a structural evolution. They assume that by rebranding their operations team, they’ve achieved agility. However, DevOps engineering isn’t a simple upgrade of a system administrator’s toolkit; it’s a fundamental shift in how organizations deliver value. While traditional administrators focus on the maintenance of existing servers, engineers in this discipline focus on the architecture of the delivery pipeline itself. By integrating DevOps principles into the core of the business, leaders can dismantle the silos that historically separated development and operations, creating a unified flow that prioritizes systemic efficiency over individual task completion.

This transition is anchored in the “You Build It, You Run It” philosophy popularized by industry leaders like Amazon and Red Hat. In this model, the responsibility for a service doesn’t end when the code is committed. Instead, the engineering team maintains accountability for the service throughout its entire lifecycle. This proactive approach eliminates the “throw it over the wall” mentality, forcing a focus on long-term reliability and code-driven infrastructure. Instead of manual provisioning, which is prone to human error and inconsistency, teams utilize Infrastructure as Code (IaC) to ensure environments are reproducible, scalable, and secure. This shift ensures that infrastructure is managed with the same version control and testing rigor as the application code itself.

The Evolution from Operations to Engineering

Historically, operations teams were the firefighters of the IT world, reacting to outages with manual fixes. Modern DevOps engineering reverses this dynamic by applying software engineering rigor to infrastructure management. The role has matured from “fixing broken things” to “building systems that don’t break” by design. By embedding infrastructure requirements directly into the software development life cycle (SDLC), organizations can automate compliance and performance checks before a single line of code reaches production. DevOps engineering is a discipline that applies software engineering practices to infrastructure to create resilient, self-healing environments.

Core Responsibilities vs. Traditional Roles

The distinction becomes clearest when examining Key Performance Indicators (KPIs). Traditional roles often prioritize “Uptime” above all else, which can lead to a fear of change and slower release cycles. In contrast, DevOps engineers balance Velocity and Reliability, recognizing that speed is only valuable if the system remains stable. This “Software Defined Everything” playground allows for rapid experimentation and automated recovery. For leaders struggling to bridge this gap, DevOps Consulting provides the strategic roadmap necessary to redefine these boundaries and ensure that engineering efforts translate into tangible business value.

Myth 2: The Toolchain Trap—Automation is the Only Metric That Matters

Many enterprise leaders fall into the trap of equating tool acquisition with organizational transformation. They invest heavily in platforms like Jira, Jenkins, or AWS, expecting these tools to solve deep-seated operational friction. However, DevOps engineering is not a product you can purchase off the shelf. If you automate a flawed, fragmented process, you only succeed in accelerating failure. Real progress requires a holistic approach that balances technical implementation with structural change, ensuring that every automated action serves a specific strategic purpose.

The CALMS framework—Culture, Automation, Lean, Measurement, and Sharing—provides the necessary equilibrium for sustainable growth. While automation is a critical pillar, it cannot function in a vacuum. Culture must precede the toolchain because tools are merely force multipliers for the existing organizational mindset. Without a foundation of trust and open communication, even the most sophisticated pipeline becomes a source of technical debt rather than a driver of efficiency. Leaders who prioritize tools over people often find themselves with expensive licenses but no improvement in their actual delivery speed.

Why Automation is a Means, Not an End

Automation serves as a means to an end, not the ultimate objective. There is a persistent danger in creating “Automated Silos,” where departments use disparate tools that fail to communicate, leading to data fragmentation and operational blind spots. Successful application development requires building software architectures that are inherently automatable from the start. High-performing DevOps engineering initiatives focus on strategy, stability, and scalability rather than just writing repetitive scripts. They prioritize the systemic flow of value across the entire organization.

Measuring What Actually Matters

To understand if your investments are delivering results, you must measure what actually impacts the bottom line. The DORA metrics—Deployment Frequency, Lead Time for Changes, Change Failure Rate, and Time to Restore—offer a clear framework for aligning technical efforts with business-level ROI. These indicators move the conversation away from how many scripts were written to how quickly and safely the team delivers value to the customer. Evaluating your toolchain effectiveness should include a simple checklist:

  • Integration: Do your tools communicate seamlessly across the entire development lifecycle?
  • Cognitive Load: Does the automation simplify the developer’s job or add new layers of complexity?
  • Visibility: Are the performance metrics visible and actionable for both technical and executive leadership?

If you find your team’s progress stalled by a complex toolchain, you might benefit from a strategic review of your current processes. Consider how a refined approach can empower your engineering leadership to move beyond the toolchain trap and achieve genuine operational excellence.

DevOps Engineering in 2026: Debunking 5 Critical Myths for Enterprise Leaders

Myth 3: The Lone Wolf Fallacy—One “Rockstar” Engineer Can Fix Your Pipeline

Enterprise leaders often succumb to the allure of the “rockstar” hire, believing that a single specialized expert can unilaterally resolve complex pipeline inefficiencies. This approach typically stems from a desire to minimize costs while seeking high-level technical results. However, relying on a solitary specialist creates a dangerous single point of failure that can paralyze your digital transformation if that individual leaves or becomes overwhelmed. DevOps engineering is a collective capability, not an individual talent. When the weight of an entire organization’s deployment frequency rests on one person, they inevitably become the very bottleneck they were hired to eliminate. Hero culture leads to burnout.

The Problem with “DevOps as a Person”

Designating a specific individual as “the DevOps person” frequently backfires by inadvertently creating a new organizational silo. Instead of fostering collaboration between development and operations, this structure encourages developers to outsource their operational responsibilities. This shift leads to a reactive environment where one person is constantly firefighting while the rest of the team remains disconnected from the production environment. Reliance on individual heroics is unsustainable and detrimental to long-term system stability. To mitigate these risks, many enterprises are turning to Managed Outsourcing Services to provide the breadth of expertise required without the vulnerability of the lone wolf model. This approach ensures that institutional knowledge remains within the organization rather than walking out the door with a single employee.

Integrating Quality and Security

True operational excellence requires that DevOps engineering is deeply integrated with quality assurance and security protocols from the start. The “Shift Left” movement emphasizes that testing and security shouldn’t be final checkboxes but continuous activities throughout the development lifecycle. This level of integration is impossible if your DevOps effort is isolated to a single engineer. Effective collaboration requires robust platforms and methodologies, such as software and digital assurance testing, to ensure that every release meets high standards of reliability. By utilizing collaborative tools like ServiceNow and Atlassian, organizations can bridge the communication gap between Dev, QA, and Security. This transforms DevOps from a lonely job title into a pervasive cultural standard that empowers every team member to contribute to the system’s success.

Myth 4: The Startup Stigma—DevOps Engineering is Only for Tech Giants

A persistent misconception suggests that DevOps engineering is a luxury reserved for hyperscalers like Netflix or Google. This “startup stigma” leads many small-to-medium enterprise (SME) leaders to believe their operations are too modest to justify such technical rigor. In reality, organizations with limited resources stand to benefit the most from these methodologies. While a tech giant can absorb the cost of manual inefficiencies through sheer headcount, a smaller team cannot. Implementing a strategic engineering framework reduces the “Cognitive Load” on your developers, freeing them from the mental tax of complex infrastructure management so they can focus on high-value feature development.

The democratization of technology through major cloud providers has leveled the playing field, making enterprise-grade reliability accessible to businesses of all sizes. You don’t need a massive budget to implement robust security or automated scaling. By adopting a “Minimum Viable DevOps” approach, growing organizations can prioritize the most critical bottlenecks, ensuring that their technical foundation supports rather than hinders rapid expansion. This disciplined approach to growth ensures that your systems remain stable even as your user base and data requirements increase exponentially.

DevOps for the SME: A Practical Roadmap

Transitioning toward a more mature operational model doesn’t require an overnight overhaul. Small teams can achieve significant gains by following a structured progression. First, standardizing the environment through proven AWS Cloud Migration strategies ensures a consistent baseline for all future development. Once the foundation is secure, implementing basic CI/CD pipelines eliminates the risk and delay associated with manual deployments. Finally, fostering a “Blameless Post-Mortem” culture allows your team to treat failures as data points for improvement rather than opportunities for finger-pointing, which is essential for maintaining long-term morale and system integrity.

Resource Management and Staffing

One of the most significant challenges for smaller organizations is balancing the need for specialized talent with the reality of a finite budget. Leaders must decide whether to invest in permanent internal hires or leverage flexible Staffing Solutions to fill specific expertise gaps. Utilizing contract or offshore resources often provides access to high-level specialized skills without the heavy overhead of enterprise-level benefits and long-term commitments. This versatility allows you to scale your engineering capacity in direct response to project demands. Scalability is a mindset, not just a server configuration. If you’re ready to optimize your team’s performance, contact our strategic advisors to discuss a tailored approach for your organization.

Myth 5: The “Set it and Forget it” Fallacy—DevOps Engineering is a One-Time Project

Many enterprise leaders treat digital transformation as a destination with a definitive finish line. They assume that once the initial automation pipelines are established, the work of the engineering team is essentially complete. However, DevOps engineering is a continuous discipline that must evolve in parallel with the software it supports. As your application architecture changes to meet shifting market demands, the underlying infrastructure must be refined to maintain high standards of reliability and performance. Treating this evolution as a one-time project is a strategic error that leads to technical debt and operational stagnation.

This reality introduces the “Day 2 Operations” challenge, which focuses on the long-term maintenance, monitoring, and optimization of systems after the initial deployment. Modern engineering requires a sophisticated approach to observability, where real-time data ingestion allows teams to identify and resolve systemic bottlenecks before they impact the end-user. By fostering a culture of continuous improvement, organizations ensure that their technical foundations remain resilient against the complexities of a scaling environment. It’s a journey of constant refinement where each successful release provides the data necessary for the next phase of optimization.

The Continuous Nature of Modern Infrastructure

Infrastructure is never truly static. It requires periodic, rigorous audits of critical platforms like Atlassian or ServiceNow to ensure that configurations remain aligned with changing team workflows and security requirements. While a successful Atlassian Implementation provides a powerful start to the efficiency journey, it’s the ongoing management of these tools that secures long-term business value. Leaders must prioritize staying current with critical security patches and cloud cost optimization strategies to prevent operational overhead from eroding their digital gains. Regular technical health checks are essential for maintaining the agility promised by modern engineering frameworks.

Partnering for Long-Term Maturity

Achieving institutional maturity in a fast-changing landscape often requires the support of a strategic partner who understands the interplay between specialized talent and advanced tools. By integrating comprehensive IT Service Management Solutions, organizations establish the governance and order needed to scale their operations across diverse, highly regulated industries. This collaborative approach ensures that your engineering efforts are not just technically sound but also deeply aligned with your overarching business objectives. If you’re concerned that your current processes have become stagnant, we encourage a strategic review of your DevOps maturity to identify new opportunities for growth and system reliability.

Mastering the Strategic Evolution of Your Engineering Culture

Dismantling the myths surrounding DevOps engineering requires a fundamental shift from viewing infrastructure as a cost center to recognizing it as a strategic asset. Success depends on prioritizing culture over tool acquisition, fostering collective team accountability, and accepting that optimization is an ongoing journey rather than a static project. By moving away from the “lone wolf” model and embracing a disciplined, code-driven methodology, your organization can achieve the stability and velocity needed to compete on a global scale. This evolution transforms your technical friction into a reliable engine for sustainable growth.

As an Atlassian Gold Solution Partner and ServiceNow Consulting Experts, we provide the institutional maturity and technical rigor required to manage complex digital transformations. Our global presence across Europe, North America, and Asia ensures that we remain a reliable collaborator for enterprises seeking scalable growth and risk reduction. If you’re ready to align your technical execution with long-term business value, explore our DevOps Consulting and Staffing Solutions to begin your next phase of operational excellence. Your path to a resilient and efficient digital future starts with a single strategic decision.

Frequently Asked Questions

What is the difference between a DevOps engineer and a Site Reliability Engineer (SRE)?

Site Reliability Engineering (SRE) acts as a specific implementation of the broader DevOps philosophy, focusing primarily on system availability and performance through software engineering practices. While DevOps engineering aims to bridge the gap between development and operations to improve velocity, SRE provides the prescriptive metrics and error budgets needed to maintain stability. This structured approach ensures that speed doesn’t compromise the integrity of the production environment.

Can a small company afford a DevOps engineer?

Small organizations can absolutely afford to integrate these capabilities by leveraging flexible staffing solutions or managed services rather than hiring a full-time, high-salaried specialist. By utilizing a fractional model, smaller teams gain access to enterprise-grade expertise that reduces manual errors and accelerates time-to-market. This strategic investment prevents the costly technical debt that often accumulates in growing businesses with unoptimized delivery pipelines.

What are the most essential tools for a DevOps engineering team in 2026?

Essential tools for 2026 center on Kubernetes for orchestration, Terraform for infrastructure as code, and AI-enhanced observability platforms like Datadog or New Relic. Security integration through tools like Snyk and automated CI/CD via platforms like Harness or GitHub Actions are now baseline requirements for high-performing teams. These technologies provide the precision, protection, and performance necessary to manage modern, complex digital infrastructures effectively.

Is DevOps engineering more about coding or culture?

DevOps engineering requires a balanced integration of technical coding skills and a collaborative organizational culture to be truly effective. While automation scripts and Infrastructure as Code are the visible outputs, they rely on a cultural foundation of shared responsibility and open communication to deliver value. Without a shift in mindset, even the most advanced code will fail to break down the silos that stall digital transformation.

How do I transition my traditional IT team into a DevOps model?

Transitioning a traditional team begins with identifying a pilot project where you can implement automated testing and continuous integration to demonstrate immediate value. Providing structured training and seeking expert consulting helps bridge the skill gap while gradually introducing a blameless, data-driven operational mindset. This methodical evolution ensures that the team moves from reactive maintenance to proactive system engineering without disrupting core business operations.

What is the ROI of investing in DevOps engineering for a non-tech business?

For non-tech businesses, the ROI of DevOps engineering manifests through improved system reliability, reduced operational overhead, and the ability to respond faster to customer needs. By automating repetitive manual tasks, organizations can redirect human capital toward higher-value strategic initiatives that drive revenue. This shift results in a more resilient infrastructure that supports scalable growth and minimizes the financial impact of potential system downtime.

Do I need to be on the cloud (AWS/Azure) to implement DevOps?

You don’t need to be exclusively on a public cloud like AWS or Azure to implement these principles, though cloud environments offer the native automation tools that simplify the process. On-premise and hybrid infrastructures can also benefit from Infrastructure as Code and automated delivery pipelines to improve consistency. The focus remains on the methodology and the results rather than the specific physical location of the servers.

How does DevOps engineering impact software security?

DevOps engineering significantly enhances software security by integrating automated scanning and compliance checks directly into the early stages of the development lifecycle. This “shift-left” approach ensures that vulnerabilities are identified and remediated long before the code reaches production, reducing the risk of a data breach. By treating security as a continuous, automated process, organizations achieve a higher standard of protection while maintaining vision, velocity, and value. Staying current with evolving vulnerability frameworks, such as the OWASP Top 10 2026 news and its strategic implications for enterprise security, is essential for ensuring your DevOps pipeline remains aligned with the latest threat landscape.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.

Did you know that while 94% of enterprises have integrated at least one cloud service by 2026, 38% of these migrations still exceed their original budget? This fiscal friction often stems from parallel running costs or unforeseen complexities in data sovereignty. For global leadership, the prospect of an AWS Cloud Migration shouldn’t feel like a gamble with your operational stability or a test of your team’s existing skill gaps. It’s natural to feel uneasy about potential business downtime or the tightening grip of regulations like India’s DPDPA 2025 updates and Canada’s 2026 sovereign cloud policies.

You deserve a transition that prioritizes precision over guesswork. We’ve designed this strategic guide to help you master the complexities of enterprise evolution; providing a professional roadmap that ensures security, scalable growth, and a significant reduction in technical debt. By exploring the 7 Rs of migration and the latest AI-driven discovery tools, we’ll outline a clear path to improved system performance that aligns with your 2026 digital transformation goals. This approach ensures your organization achieves precision, partnership, and progress throughout the entire lifecycle.

Key Takeaways

  • Identify how the “7 Rs” framework provides a disciplined methodology for categorizing workloads, ensuring each application follows the most efficient path toward modernization.
  • Learn to navigate a structured AWS Cloud Migration roadmap that moves from initial portfolio assessment to the establishment of a secure, compliant landing zone.
  • Address the critical human element of technological change by bridging internal skill gaps and overcoming cultural resistance within highly regulated enterprise environments.
  • Discover how to maximize post-migration ROI by optimizing ServiceNow and Atlassian ecosystems through specialized DevOps consulting and managed support.
  • Shift your operational focus from simple relocation to systemic evolution, utilizing agentic AI to accelerate modernization timelines and improve long-term system performance.

The Strategic Imperative: Why AWS Cloud Migration Defines Enterprise Success in 2026

In 2026, the concept of cloud migration has moved far beyond simple data transfer. It’s now a fundamental catalyst for systemic enterprise evolution and digital maturity. An effective AWS Cloud Migration represents a shift from static infrastructure to a dynamic, machine-speed environment where agentic AI and predictive analytics define the pace of business. Modern organizations don’t view this transition as a one-time technical task. Instead, they recognize it as a strategic opportunity to rebuild their operational core for a future that demands constant adaptation. It’s about building a foundation that supports continuous improvement, operational stability, and long-term resilience.

By moving from rigid capital expenditure (CapEx) models to a performance-driven operational (OpEx) framework, enterprises gain the agility to respond to market shifts in real-time. This isn’t just about reducing costs; it’s about optimizing value across the entire digital ecosystem. We approach every migration through a specific “Test Triangle” perspective: Strategy, Security, and Scalability. This trifecta ensures that your technological evolution is grounded in practical business outcomes. When you align your high-level mission with technical execution, you create a steady hand in a fast-changing landscape.

Beyond Cost Savings: The Modern Drivers of Migration

Modern migration is fueled by a need for operational resilience. In a volatile global market, the ability to maintain business continuity through AWS’s distributed infrastructure is a competitive necessity. Innovation velocity has also become a primary driver. The cloud allows for rapid prototyping and the deployment of AI-driven applications that would be impossible in legacy environments. Additionally, AWS’s carbon-efficient infrastructure helps organizations meet increasingly strict corporate sustainability mandates. This turns technical decisions into environmental, social, and governance (ESG) victories by utilizing real-time carbon footprint reporting.

The Risks of Inertia: What Happens When You Delay?

Delaying your cloud journey creates a compounding burden of technical debt. Aging on-premises data centers become increasingly expensive to maintain and lack the modern cloud-native protections required to thwart sophisticated security threats. There is also a significant human cost. The widening talent gap means that top IT professionals actively seek out cloud-native environments. If you aren’t evolving, you’ll struggle to attract the experts needed to run your business. Our staffing solutions can help bridge this gap, but the underlying infrastructure must be modern to sustain a high-performing team.

Selecting Your Path: The 7 Rs of AWS Migration Strategy

Successful cloud evolution requires more than just moving data; it demands a disciplined methodology to categorize every workload within your enterprise portfolio. The “7 Rs” framework serves as this strategic compass, allowing leadership to balance speed, cost, and long-term digital maturity. By assigning a specific migration path to each application, you avoid the “complexity trap” that often stalls large-scale transitions. Whether your goal is immediate data center exit or a complete overhaul for AI readiness, selecting the right path is the most critical decision in your AWS Cloud Migration journey. It’s about matching technical execution to specific business outcomes, ensuring that every move contributes to operational stability and scalable growth.

Tactical Execution: Rehost, Relocate, and Repurchase

For organizations prioritizing speed and risk reduction, tactical strategies offer the path of least resistance. Rehosting, or “lift-and-shift,” remains the most common approach, accounting for 38.3% of migrations according to 2026 industry data. It allows you to move applications to the cloud without modifying the core code, making it ideal for large-scale legacy environments. Relocating leverages VMware Cloud on AWS to move hundreds of instances simultaneously at the hypervisor level, maintaining operational consistency. Meanwhile, repurchasing involves shifting from perpetual licenses to modern SaaS models. This is an excellent opportunity to transition legacy service desks to a modern ServiceNow implementation or move project management to the cloud with expert Atlassian consulting.

Strategic Transformation: Replatform and Refactor

When the objective is systemic improvement rather than simple relocation, strategic transformation becomes the priority. Replatforming involves making targeted optimizations, such as migrating to managed database services, to boost performance without a full architectural rewrite. Refactoring, however, is the gold standard for 2026. This approach re-architects applications to be cloud-native, enabling full integration with agentic AI and serverless computing. While it requires more upfront investment, refactoring delivers the highest levels of scalability and long-term ROI. If you’re unsure which path aligns with your fiscal year goals, our team can help you evaluate your portfolio architecture to find the optimal balance.

Finally, a robust AWS Cloud Migration strategy must include portfolio hygiene through Retaining and Retiring. Retaining involves keeping specific workloads on-premises to meet strict sovereign cloud procurement policies, such as Canada’s 2026 data residency requirements. Retiring focuses on decommissioning redundant or obsolete systems, which can significantly reduce technical debt and streamline your security perimeter. By rigorously applying these seven categories, you transform a chaotic move into a structured, predictable evolution that empowers your entire organization.

AWS Cloud Migration: A Strategic Step-by-Step Guide for Enterprise Evolution in 2026

A Step-by-Step Roadmap to a Seamless AWS Transition

Transitioning to a cloud-native ecosystem requires a methodical, phase-gated approach that prioritizes operational stability over sheer speed. A successful AWS Cloud Migration isn’t a single event but a journey that demands technical precision, organizational readiness, and expert partnership. By following a structured roadmap, enterprises can navigate the complexities of 2026’s digital landscape while mitigating the risks of business downtime and regulatory non-compliance. This process moves logically from broad portfolio assessment to specific service optimization, ensuring that your technological evolution is both intentional and well-organized.

Phase 1 & 2: Preparation and Foundation

The journey begins with a Comprehensive Portfolio Assessment and Business Case Validation. During this stage, conducting an Optimization and Licensing Assessment (OLA) is essential to right-size your cloud footprint, preventing the over-provisioning that often leads to budget overruns. Establishing a Cloud Center of Excellence (CCoE) ensures cross-functional alignment, bringing together leadership from IT, finance, and security to drive a unified vision. We then move into the Mobilisation Stage, where we build your AWS Landing Zone. This involves designing a multi-account structure that enforces strict security guardrails and compliance foundations, providing a steady hand for your complex digital infrastructure.

Phase 3 & 4: Migration and Quality Assurance

In the Execution phase, we implement automated waves of workload transfers. In 2026, we utilize tools like AWS Migration Hub, which now incorporates predictive analytics to map application dependencies. This intelligence can reduce the discovery phase by months, allowing for a more efficient and disciplined move. However, the migration is only complete once it passes through rigorous validation. Data Migration Testing plays a critical role here, ensuring that data integrity is maintained and that no business logic errors are introduced during the transition. By focusing on precision and human expertise, we confirm that all performance benchmarks are met before the final cutover.

To minimize operational impact, final cutover strategies often employ blue-green deployments or canary releases. These methodologies allow for a seamless transition by running the new environment alongside the old, providing the peace of mind that comes from risk reduction. After the cutover, we shift our focus to post-migration validation, where we continuously monitor system performance and scalability. This methodical rhythm ensures that your organization doesn’t just reach the cloud but thrives within it, achieving the operational efficiency and scalable growth promised at the start of the journey.

Overcoming Enterprise Migration Challenges: People, Process, and Security

While technical frameworks provide the architecture, the primary friction points of an AWS Cloud Migration frequently reside within organizational culture and human capital. Addressing the internal skills gap while managing cultural resistance to change is a prerequisite for leadership teams pursuing long-term operational stability. In highly regulated sectors such as Finance and Pharmaceuticals, organizations often fall into a “complexity trap” where legacy processes conflict with cloud-native agility. Navigating these hurdles requires a composed, solution-oriented approach that prioritizes precision, partnership, and progress. By treating the transition as a human-centric evolution rather than a mere server move, you ensure that your digital infrastructure remains resilient and your workforce remains empowered.

The Human Element: Staffing and Training

Executing a large-scale evolution requires a specialized workforce, including Cloud Architects, DevOps engineering professionals, and Security Specialists. Many organizations find that their existing IT teams possess deep institutional knowledge but lack the specific cloud-native expertise required for a seamless transition. To bridge these immediate project needs, savvy enterprises leverage professional IT Staffing Services to inject high-level expertise into their migration waves. Additionally, integrating remote offshore resources allows for continuous delivery cycles and significant cost-efficiency without compromising technical rigor. This dual approach empowers your organization to maintain momentum while simultaneously upskilling your internal workforce for the new operational reality.

Security and Compliance in the Cloud

Security isn’t a peripheral concern; it’s a foundational pillar of the “Test Triangle” methodology. Implementing Zero Trust architectures within your AWS environment from day one ensures that every access request is verified, regardless of its origin. In highly regulated industries, automating compliance monitoring is the only way to consistently meet evolving standards like GDPR, HIPAA, or GxP. Staying current with OWASP Top 10 2025 news is equally critical, as emerging vulnerability categories directly inform the security guardrails you must enforce within your cloud environment. The AWS Shared Responsibility Model defines cloud security as a collaborative effort where AWS manages the security of the cloud, while the customer remains responsible for security in the cloud. By clearly defining these boundaries, you achieve the peace of mind that comes from comprehensive risk reduction and systemic protection.

If your internal teams are facing a skills bottleneck that threatens your timeline, contact us to discuss strategic staffing solutions that align with your migration goals. This collaboration ensures your transition remains on track while building the institutional maturity needed for long-term success.

Maximizing Post-Migration ROI: Modernization and Managed Support

The successful completion of an AWS Cloud Migration is not the final destination; it’s the foundation for systemic enterprise evolution. While many organizations focus purely on the technical cutover, the most successful global players shift their focus toward modernization to unlock the full potential of their cloud environment. This evolution involves moving beyond simple workload management to embracing cloud-native architectures that support agentic AI and predictive analytics. By partnering with a reliable Managed Service Provider, leadership teams can maintain system health while exercising rigorous cost control. Utilizing tools like AWS Cost Explorer on a monthly basis ensures that your cloud spend remains optimized, preventing the budget creep that historically affects nearly 38% of enterprise migrations.

Integrating Your Enterprise Ecosystem

Integrating your established enterprise tools into the AWS ecosystem creates a “single pane of glass” view for your IT Service Management (ITSM) across complex hybrid environments. Enhancing your Atlassian implementation with cloud-native scalability allows your development teams to operate with greater agility and precision. Similarly, by integrating ServiceNow consulting services with AWS data lakes, you can streamline workflows and derive deeper insights from your operational data. This synergy ensures that your infrastructure remains manageable, secure, and fully aligned with your high-level business outcomes; providing the peace of mind that comes from a well-organized digital estate.

The Path to DevOps Maturity

A successful AWS Cloud Migration serves as the critical starting line for advanced DevOps consulting initiatives that drive long-term digital maturity. Implementing Infrastructure as Code (IaC) allows for repeatable, error-free environment provisioning, which is essential for maintaining stability as your organization scales. This methodical approach to automation reduces technical debt and empowers your workforce to focus on high-value innovation rather than routine maintenance. Ultimately, your cloud journey is a process of constant refinement where human expertise and technical tools combine to drive organizational progress. Understanding the evolving landscape of DevOps engineering in 2026 can help enterprise leaders avoid common misconceptions that stall automation efforts and prevent technical investments from translating into measurable business outcomes. Migration is never a static destination; it is the catalyst for continuous digital innovation and sustainable growth in a fast-changing technological landscape.

Secure Your Digital Future Through Strategic Evolution

Transitioning to the cloud in 2026 is no longer a matter of simple technical feasibility; it’s a strategic necessity for enterprises aiming to lead in an increasingly machine-speed economy. We’ve explored how a disciplined approach to modernization empowers organizations to shed technical debt while embracing agentic AI and cloud-native scalability. By aligning your application portfolio with the 7 Rs framework and prioritizing human-centric staffing, you transform potential operational risks into clear competitive advantages. This journey requires a steady hand and a commitment to long-term digital maturity.

As an AWS Consulting Partner with specialized expertise in highly regulated sectors like Pharma and Finance, Test Triangle acts as a reliable long-term collaborator for your digital journey. Our global delivery model and 24/7 managed support ensure your infrastructure remains resilient, secure, and optimized long after the initial cutover. Partner with Test Triangle for your strategic AWS Cloud Migration roadmap today to achieve the precision, stability, and growth your enterprise deserves. Your path to a modernized, high-performance future starts here.

Frequently Asked Questions

What is the average timeline for an enterprise AWS cloud migration?

The average timeline for an enterprise AWS Cloud Migration typically ranges from six to twenty-four months, depending on the complexity of your application portfolio and the chosen strategy. While small-scale proof-of-concept projects can be executed in weeks, large-scale systemic evolution requires a methodical approach that accounts for discovery, foundation building, and validation. Factors like data volume, regulatory requirements, and internal team readiness significantly influence the overall duration.

How much does AWS cloud migration cost for a mid-sized organization?

Costs for a mid-sized organization vary based on the scale of the workloads and the selected 7 Rs strategy. Major expenses often include parallel running costs, where organizations maintain both on-premise and cloud environments for three to eighteen months. Additionally, data transfer fees and underlying infrastructure provisioned during replication contribute to the total investment. Utilizing a professional roadmap helps identify these hidden expenses early, ensuring fiscal transparency and long-term ROI.

Can I migrate legacy applications to AWS without rewriting the code?

You can certainly migrate legacy applications without rewriting code by utilizing the Rehosting or “Lift-and-Shift” strategy. This approach is the most common path for data center exits, as it moves applications directly to AWS infrastructure with minimal modification. While this provides a rapid transition, it won’t immediately unlock cloud-native benefits like auto-scaling or AI integration. It serves as a practical first step before pursuing deeper modernization in subsequent phases.

What are the most common risks associated with AWS cloud migration?

The most common risks associated with an AWS Cloud Migration include unexpected business downtime, internal skill gaps, and complex regulatory compliance hurdles. Without a disciplined transition plan, organizations may face data integrity issues or security vulnerabilities in their new environment. Mitigating these risks requires a combination of robust testing methodologies and strategic staffing to ensure that technical execution aligns with operational stability and security benchmarks.

How does AWS migration impact my existing Atlassian or ServiceNow licences?

Migration offers a strategic opportunity to optimize your existing Atlassian or ServiceNow ecosystem by transitioning from perpetual licenses to modern SaaS models. While the underlying business logic remains consistent, moving these platforms to the cloud often requires a licensing assessment to ensure compliance and cost-efficiency. Our experts help align these tools with your new AWS environment, providing a single pane of glass view for your IT service management operations.

Is AWS cloud migration secure for highly regulated industries like healthcare?

AWS migration is highly secure for regulated sectors like healthcare, provided organizations implement a Zero Trust architecture and follow the Shared Responsibility Model. AWS provides specialized services and infrastructure that comply with global standards such as HIPAA, GDPR, and GxP. By automating compliance monitoring and enforcing strict data residency guardrails, enterprises can achieve a level of security that often surpasses traditional on-premise data centers.

What is the difference between cloud migration and cloud modernization?

Cloud migration focuses on moving workloads from on-premise infrastructure to the cloud, whereas modernization involves re-architecting applications to utilize cloud-native features. Migration is the initial step that establishes the foundation, while modernization unlocks advanced capabilities like serverless computing and agentic AI integration. Both are essential components of a digital transformation journey, but modernization is what ultimately drives maximum scalability and long-term performance improvements.

How do I choose between a Lift-and-Shift and a Refactoring strategy?

Choosing between Lift-and-Shift and Refactoring depends on your application’s criticality and your digital maturity goals. Lift-and-Shift is ideal for organizations needing a fast data center exit with low risk and minimal upfront investment. In contrast, Refactoring is the preferred choice for core applications that require maximum scalability or AI integration. A balanced approach often involves rehosting non-critical systems while refactoring high-value workloads to ensure optimal ROI.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.
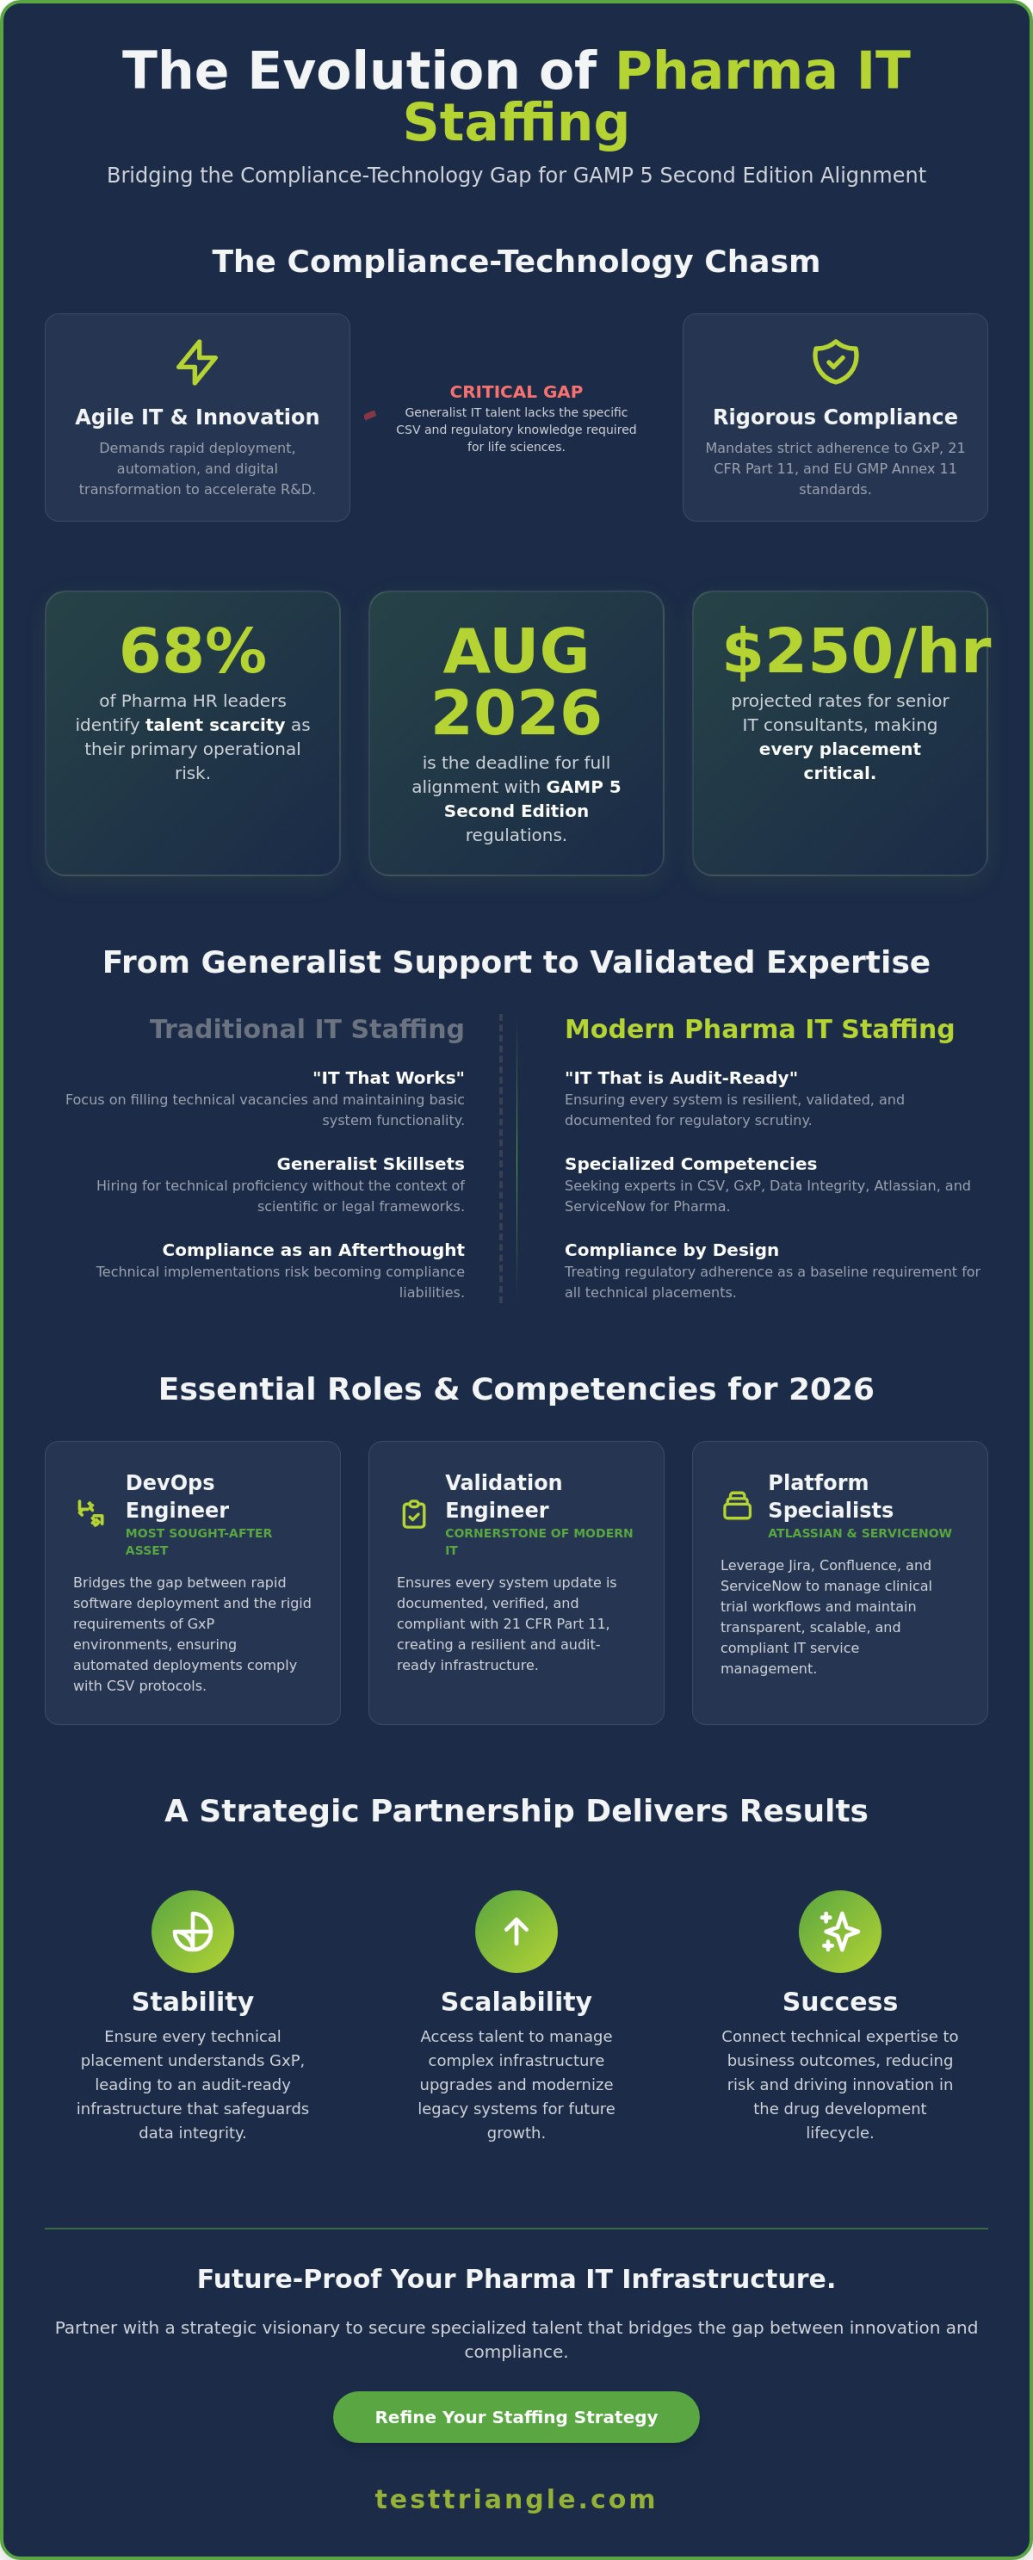

QMetry Migration for Jira Cloud – Zero Data Loss

Test Triangle delivers end-to-end QMetry Test Management migration between Jira Cloud instances – preserving every test case, test cycle, relationship, attachment, and execution history with complete traceability.

QMetry Test Management for Jira Cloud

QMetry is a comprehensive test management solution built to integrate seamlessly with Jira Cloud. It enables QA teams to design, organize, execute, and track test cases directly within Jira – ensuring end-to-end traceability between requirements, test scenarios, and defects.

Designed for agile and DevOps environments, QMetry enhances collaboration, improves test coverage, and provides actionable insights through real-time reporting and analytics.

QMetry Migration Limitations in Jira Cloud

QMetry Cloud has no native cross-instance migration capability. These constraints explain why a specialist solution is essential for safe, complete migration.

  • No Native Cross-Instance Migration

    QMetry Cloud provides no built-in feature to transfer test data between Jira instances. Manual export/import is the only default path, making large-scale migration error-prone and time-consuming.

  • Limited Export Formats (CSV/Excel Only)

    Export is restricted to CSV or Excel – flat formats that cannot capture hierarchical relationships between test cases, test cycles, executions, and Jira requirements.

  • Complex Entity Relationships Not Preserved

    Links between test cases, test cycles, executions, and defects are often broken or lost during standard migration, destroying end-to-end traceability.

  • System-Generated ID Conflicts

    Entity IDs are instance-specific and regenerated in the target Jira environment, breaking all reference-based links and causing data inconsistency.

  • Incomplete Metadata & Asset Migration

    Custom fields, attachments, comments, and execution history are not fully handled via standard export, leading to significant data gaps in the destination environment.

  • Execution History & Audit Trail Loss

    Detailed test step results, execution results, and audit trails are typically lost, making it impossible to faithfully replicate the original QMetry testing setup.

Comprehensive QMetry Migration Solution

Everything migrated. Nothing left behind. Our specialist solution handles every layer of QMetry complexity across Jira Cloud instances.

  • End-to-End Cross-Instance Migration

    Seamless QMetry migration between Jira Cloud instances, eliminating dependency on manual export/import with full automation and data integrity verification.

    Cloud to CloudAutomated
  • Complete Test Asset Migration

    All core QMetry entities migrated – Test Plans, Test Cycles, Test Cases, Test Steps, and Test Executions – with verified data integrity.

    Test PlansTest CasesExecutions
  • Accurate Custom & System Field Mapping

    All custom fields and system fields migrated with proper configuration alignment – no data loss or mapping inconsistencies across Jira instances.

    Custom FieldsSystem Fields
  • Preservation of Complex Entity Relationships

    All critical linkages maintained: Test Cases ↔ Requirements, Cycles ↔ Test Cases, Plans ↔ Cycles, and Defects at step and execution level.

    TraceabilityDefect Links
  • Attachments & Comments Migration

    Fully migrates attachments and comments across Test Plans, Cycles, Cases, Steps, and Executions – no file left behind.

    AttachmentsComments
  • Test Case Versioning Support

    All versions of test cases – including historical versions – migrated to maintain complete audit trails and version control continuity.

    Version HistoryAudit Trail
  • Archived & Active Data Coverage

    Both archived and active QMetry entities are included – ensuring zero data is left behind in the source Jira Cloud instance.

    ArchivedActive
  • Jira Issue Key Preservation

    Original Jira issue keys retained in the destination instance, enabling accurate mapping, traceability, and reporting continuity post-migration.

    Issue KeysContinuity
  • Defect Traceability Maintenance

    End-to-end defect traceability preserved by keeping defect links intact at both step and execution levels throughout the QMetry migration process.

    Step-LevelExecution-Level

Frequently Asked Questions about QMetry Migration

Everything you need to know about migrating QMetry data between Jira Cloud instances.

Can QMetry data be migrated between two separate Jira Cloud instances?

QMetry does not provide any native cross-instance migration capability. However, Test Triangle’s specialist migration solution enables seamless transfer of all QMetry data – test cases, cycles, executions, attachments, and relationships – between any two Jira Cloud instances with full data integrity.

What QMetry data is fully preserved during migration?

Our solution preserves test plans, test cycles, test cases, test steps, test executions, custom fields, system fields, attachments, comments, defect links at step and execution level, all version history, original Jira issue keys, and all entity relationships – ensuring complete data integrity and traceability in the target environment.

Why does QMetry’s native CSV/Excel export fall short for migration?

CSV and Excel exports capture only flat data structures. They cannot represent hierarchical entity relationships, execution history, step-level test results, attachments, or metadata. System-generated IDs are also instance-specific and not portable, causing all cross-references and traceability links to break in the target Jira environment.

Does Test Triangle migrate archived QMetry test data?

Yes. The QMetry migration covers both active and archived entities – nothing is excluded. This ensures complete historical context, audit trail continuity, and full reporting capability in the destination Jira Cloud instance.

Which regions does Test Triangle operate in?

Test Triangle operates globally with teams in Ireland, the United Kingdom, and India, delivering enterprise-grade Atlassian and QMetry migration services to clients across Europe and Asia.

Ready to Migrate QMetry Without the Risk?

Talk to our team and get a tailored QMetry migration plan for your Jira Cloud environment – zero data loss guaranteed.


If your 2026 product roadmap relies on testing cycles that mirror 2023 methodologies, you’re likely accumulating technical debt that will stall your digital transformation by Q4. Most enterprise leaders agree that internal testing bottlenecks now cause nearly 42% of release delays in sensitive sectors like Pharma IT and Banking. By integrating high-quality outsourced qa services into your delivery pipeline, you can mitigate these risks while maintaining the agility required for global competition. At Test Triangle, we believe that the right partnership should act as a force multiplier for your internal teams, rather than a temporary fix for capacity issues.

You deserve a strategy that delivers predictable testing costs and immediate access to specialized expertise in security and performance. This article provides a comprehensive, 5-pillar checklist designed to help you evaluate and select a partner that aligns with your long-term vision. By following this framework, you’ll learn how to achieve faster time-to-market and ensure a seamless Jira or Atlassian integration across your entire ecosystem. We’ll explore how the synergy of Technology, Talent, and Transformation can elevate your operational stability and drive sustainable success through 2026 and beyond.

Key Takeaways

  • Understand the evolution of QA from a cost-focused necessity to a strategic enabler capable of bridging the 2026 specialized talent gap.
  • Identify the optimal engagement framework for your organization by distinguishing between staff augmentation and comprehensive managed testing services.
  • Master the essential technical and regulatory benchmarks required to evaluate high-performing outsourced qa services in sectors like Finance and Pharma.
  • Audit prospective partners using five critical pillars designed to verify advanced automation depth and the security of your intellectual property.
  • Learn how to leverage the “Technology. Talent. Transformation.” triad to integrate a trusted partner that drives long-term digital stability and scalable growth.

The Strategic Shift: Why Enterprises Prioritise Outsourced QA Services in 2026

By repositioning quality assurance from a reactive cost center to a proactive strategic enabler, global enterprises are fundamentally rewriting their digital transformation playbooks. In 2026, the complexity of software ecosystems has reached a tipping point where internal teams often struggle to maintain the pace of innovation while ensuring flawless performance. By leveraging outsourced qa services, organizations gain access to high-level expertise that bridges the gap between technical execution and business outcomes. This shift allows leadership to focus on core product development while a outsourced software testing partner manages the intricate demands of modern quality protocols.

The 2026 talent market presents a significant challenge, as 73% of IT leaders report difficulty in hiring specialized testers for AI-driven systems and advanced cybersecurity protocols. Shifting from a fixed operational overhead to flexible engagement models enables companies to scale their testing capacity based on project demands without the long-term burden of internal headcount. Test Triangle serves as a Trusted Partner in this landscape, providing the necessary agility to navigate market fluctuations. Strategic QA is the intersection of risk mitigation and speed.

Checklist: 5 Signs Your Internal QA Team Has Reached Its Scaling Limit

  • Regression Backlogs: Testing cycles consistently delay production releases by 15% or more.
  • Skill Gaps: Your team lacks certified experts in AI model validation or penetration testing.
  • Infrastructure Costs: Maintaining internal device labs and automation frameworks exceeds your annual budget by 20%.
  • Escaped Defects: Critical bugs are reaching production environments at an increasing rate.
  • Automation Stagnation: Less than 40% of your test suite is automated, leading to manual bottlenecks.

Beyond Cost Savings: The Value of a Fresh Perspective

By introducing independent validation into legacy development cycles, external audits identify critical blind spots that internal teams might overlook due to institutional familiarity. Unbiased validation ensures that production-level defects are minimized before they impact the end-user experience. This objective approach allows outsourced qa services to deliver a superior level of precision. Through our core philosophy of Technology. Talent. Transformation, we help businesses optimize their quality benchmarks while maintaining operational stability.

The 2026 Release Pressure: Speed vs. Quality

CI/CD pipelines frequently fail to deliver on their promise of speed when they lack a robust, outsourced automation strategy to handle the heavy lifting. Implementing a Shift-Left testing methodology has been shown to improve time-to-market metrics by up to 30% by identifying vulnerabilities during the earliest stages of the SDLC. Global delivery centres further accelerate this process by providing 24/7 coverage, ensuring that testing continues across every time zone. This continuous feedback loop drives faster deployments and more resilient software architectures.

Defining Your Model: A Checklist for Choosing Engagement Frameworks

By integrating specialized expertise with adaptable delivery models, enterprises can optimize their outsourced qa services to achieve superior software quality. The shift toward 2026’s decentralized development environments requires a strategic evaluation of how external talent fits into your existing ecosystem. Selecting the right framework isn’t merely a procurement decision; it’s a foundational step in your digital transformation. Many organizations now leverage Cem Kaner’s outsourcing checklist to establish a baseline for vendor technical depth and accountability before committing to a specific model. This rigorous vetting ensures that the chosen partner can provide the necessary Technology, Talent, and Transformation required for long-term stability.

Managed Services: Relieving the Management Burden

Handing over full ownership of the QA process to a Trusted Partner allows internal leadership to focus on high-level product innovation. In this model, the partner manages the entire testing lifecycle, from strategy design to execution. Success is governed by Service Level Agreements (SLAs) that guarantee outcomes rather than just logged hours. For instance, a robust SLA might mandate a 98% test case execution rate or a 24-hour turnaround for critical defect reporting. A dedicated QA Lead acts as the Strategic Architect within this environment, aligning the testing roadmap with your business objectives. This model is ideal for mature organizations looking to drive efficiency through specialized outsourced qa services while maintaining high-level oversight via tools like Jira Service Management.

Staff Augmentation: Plugging Specific Skill Gaps

When specific technical gaps emerge, such as a sudden need for performance testing or security audits in 2026’s complex API ecosystems, staff augmentation provides immediate relief. This model allows for rapid scaling, enabling teams to add specialized talent for short-term projects without the 35% overhead cost typically associated with permanent hires. Achieving seamless integration requires the outsourced resources to adopt your internal culture and technical standards. Recent data from 2025 indicates that 82% of successful staff augmentation projects utilized shared communication protocols to ensure remote resources remained synchronized with in-house developers. It’s a practical way to leverage global talent while maintaining direct control over the daily testing activities.

Selecting the right geographic location for your resources depends on your “Follow the Sun” strategy and communication requirements:

  • Onshore: Essential for projects with strict regulatory compliance or those requiring real-time, same-timezone collaboration with the C-suite.
  • Nearshore: Offers a balance of cost-efficiency and 2 to 4 hour overlap windows, facilitating agile ceremonies and rapid feedback loops.
  • Offshore: Most effective for large-scale regression testing and high-volume execution where significant cost reduction is the primary driver.

Flexible engagement models are no longer a luxury but a necessity for navigating fluctuating project demands. By choosing a partner that offers adaptable frameworks, you ensure your testing capacity can expand or contract alongside your product roadmap. To see how these models function in a real-world environment, you can explore our strategic approach to quality engineering.

The Ultimate Checklist for Evaluating Outsourced QA Services in 2026

Technical and Regulatory Readiness: The Specialized QA Checklist

Generalist providers often fail in high-stakes sectors because they lack the domain-specific rigor required for 2026’s complex regulatory environment. By failing to account for sector-specific nuances in Finance and Pharma, these providers introduce liability rather than mitigating it. A 2025 industry report indicated that 62% of data breaches in regulated sectors stemmed from third-party software vulnerabilities. Selecting outsourced qa services requires a partner who understands that a bug in a clinical trial system isn’t just a technical glitch; it’s a compliance failure. To ensure your organization remains audit-ready, use this essential 2026 certification checklist:

  • ISO 27001:2022: The gold standard for information security management systems.
  • SOC2 Type II: Critical for confirming the operational effectiveness of security controls over time.
  • GxP (GLP, GCP, GMP): Essential for any software touching the life sciences supply chain.
  • PCI DSS 4.0: The mandatory requirement for any provider handling financial transaction data.

By prioritizing these standards, Test Triangle acts as a Strategic Architect, ensuring your digital infrastructure remains robust against evolving threats. Validated Software Testing isn’t an optional add-on for Healthcare; it’s the foundation of patient safety and data privacy. A partner must navigate these regulatory roadmaps with precision, moving beyond simple bug hunting to provide comprehensive risk mitigation.

Life Sciences and Pharma IT Specialization

By integrating Computer System Validation (CSV) protocols directly into the software development lifecycle, Test Triangle ensures that every release meets the stringent requirements of 21 CFR Part 11. Maintaining data integrity throughout the testing lifecycle requires more than just technical skill; it demands a disciplined approach to audit trails and electronic signatures. As of January 2026, 78% of Life Sciences organizations prioritize partners who demonstrate deep CSV expertise. It’s vital to remember that “compliance is not a checkbox but a continuous process” that defines the reliability of your entire IT estate.

Ecosystem Alignment: Atlassian, ServiceNow, and AWS

By aligning testing workflows with your existing toolstack, a sophisticated provider accelerates your digital transformation. Your outsourced qa services partner must be a Strategic Architect who leverages Jira Service Management for seamless defect tracking and real-time visibility. This integration ensures that every identified issue is categorized, prioritized, and resolved within a unified ecosystem. When utilizing AWS cloud-native testing tools, your partner can automate infrastructure provisioning, reducing the testing cycle time by 35% compared to legacy methods. This synergy between technology, talent, and transformation allows your business to scale without compromising on quality or security.

The Vendor Audit: 5 Critical Pillars of a Robust QA Partnership

Selecting outsourced qa services requires a shift from simple vendor selection to strategic architectural alignment. By 2026, 74% of global enterprises will prioritize partners who integrate predictive analytics into their testing lifecycle. This audit ensures your chosen provider isn’t just a resource supplier but a catalyst for digital transformation. By combining technical expertise with adaptable delivery models, a mature partner helps businesses reduce operational friction while maintaining high velocity.

Step 1 involves assessing technical depth. A sophisticated partner moves beyond basic manual scripts to implement AI-driven automation that achieves 90% regression coverage. Step 2 focuses on security; your code represents your primary competitive advantage and requires protection through rigorous protocols. Step 3 establishes communication governance, creating a “heartbeat” through integrated platforms like Jira Service Management. Step 4 evaluates innovation, specifically how the vendor leverages machine learning to predict defect density. Finally, Step 5 examines scalability. A partner must provide access to specialized talent within 48 hours to meet shifting project demands.

Evaluating the “Talent” Pillar

By leveraging rigorous vetting processes, Test Triangle ensures that every engineer possesses both technical certifications and domain-specific expertise. We review recruitment standards to confirm that 95% of the talent bench holds advanced certifications in tools like Selenium, Tricentis Tosca, or Playwright. Continuous training within our partner ecosystems ensures our team masters niche technologies, such as blockchain testing or 5G protocol validation, before they become mainstream requirements. This depth of talent allows us to act as a Trusted Partner in complex environments.

The Security Audit Checklist

Protecting intellectual property is the cornerstone of a professional partnership. A robust audit must verify these specific standards to mitigate risk:

  • Encryption Standards: Implementation of AES-256 for all data at rest and TLS 1.3 for data in transit across all testing environments.
  • Access Controls: Biometric physical security at offshore delivery centres and mandatory multi-factor authentication (MFA) for all logical access to client repositories.
  • Contractual Safeguards: Explicit clauses in the Master Service Agreement (MSA) ensuring 100% client ownership of all test scripts, frameworks, and generated documentation.

By aligning Technology. Talent. Transformation., we help organizations accelerate their release cycles without compromising on precision. Our flexible engagement models allow you to scale resources up or down based on real-time project metrics, ensuring your digital infrastructure remains resilient. This methodical approach to outsourced qa services transforms testing from a bottleneck into a strategic asset.

Ready to elevate your software quality through a strategic partnership? Consult with our QA architects today to secure your digital future.

Technology. Talent. Transformation: Integrating Test Triangle’s QA Expertise

By aligning technical proficiency with strategic business objectives, Test Triangle functions as a Trusted Partner rather than a traditional vendor. Our Dublin-based headquarters provides the high-level governance and strategic oversight required by European enterprises, while our global delivery centers ensure 24/7 operational continuity. We don’t just provide outsourced qa services; we integrate ourselves into your software development lifecycle to drive long-term stability. In a 2024 partnership with a Tier-1 global financial institution, our team overhauled a fragmented testing process. This intervention resulted in a 65% reduction in post-release defects within the first twelve months, proving that strategic alignment outweighs simple staff augmentation.

Our onboarding journey follows a rigorous, four-step methodology designed for clarity and speed:

  • Comprehensive Audit: we evaluate your current QA maturity and identify hidden bottlenecks in your pipeline.
  • Strategic Roadmap: our consultants design a tailored framework specifically aligned with your 2026 delivery goals.
  • Knowledge Transfer: we synchronize our specialized teams with your internal stakeholders to ensure cultural and technical fit.
  • Flawless Execution: we launch automated and manual testing cycles supported by real-time, transparent reporting.

Our Approach to Managed Platform Support

By optimizing Atlassian and ServiceNow environments, we ensure your quality management tools work in harmony with your engineering workflows. We leverage Jira Service Management to provide transparent, data-driven insights into every testing cycle. Combining DevOps engineering with QA allows us to accelerate your digital transformation, ensuring that speed never compromises security. Our flexible delivery models allow growing enterprises to scale their testing capacity up or down based on project demands. It’s a model that provides the agility needed in a volatile market while maintaining a robust quality gate.

Next Steps for Your QA Strategy

Establishing a modern testing framework requires a shift from reactive bug-fixing to proactive quality engineering. You can initiate this shift by scheduling a QA maturity assessment with our senior consultants. We specialize in transitioning organizations from slow, manual legacy testing to high-velocity, automated frameworks that support continuous integration. Our expertise in outsourced qa services ensures your transition is seamless, data-backed, and risk-mitigated. For a deeper exploration of how quality assurance outsourcing is evolving in 2026, including the integration of AI-augmented testing models and Rovo agents into Jira workflows, our strategic guide provides a comprehensive roadmap for enterprises navigating this shift. We’re ready to help you build a resilient digital infrastructure that scales.

Future-Proofing Your Enterprise through Strategic Quality Excellence

Navigating the software landscape of 2026 requires more than a simple checklist; it demands a synergy of technical rigor and operational agility. By aligning specialized engagement models with strict regulatory demands, global enterprises can transform quality assurance from a functional necessity into a strategic asset. Selecting the right outsourced qa services ensures that your digital infrastructure remains resilient against evolving security threats and rapid market shifts.

Test Triangle serves as a Strategic Architect for your testing needs. As an Atlassian Gold Solution Partner and a recognized Enterprise Ireland client, we provide the institutional maturity required for complex digital transformations. Our global delivery centres in Dublin, London, and Hyderabad offer the 24/7 technical expertise necessary to maintain a flawless user experience across all platforms. We bridge the gap between technical execution and business outcomes through our core pillars: Technology. Talent. Transformation.

It’s time to elevate your quality standards and drive scalable growth with a trusted partner who understands your long-term vision. Partner with Test Triangle for Strategic QA Transformation and secure your path toward operational stability today.

Frequently Asked Questions

What are the main benefits of outsourced QA services for enterprises?

Enterprises leverage outsourced qa services to accelerate release cycles by 30% and reduce operational overhead. By accessing global talent pools, companies secure specialized skills like AI-driven automation without the 40% higher cost of internal hiring. This strategic shift allows internal teams to focus on core innovation while external experts ensure a flawless user experience across all digital touchpoints.

How do I ensure data security when working with an offshore QA team?

We ensure data integrity by implementing ISO 27001 and SOC 2 Type II compliant frameworks for every offshore engagement. By utilizing secure VPN tunnels and multi-factor authentication, our teams maintain a zero-trust architecture that protects sensitive intellectual property. Our protocols align with GDPR and CCPA standards, ensuring that 100% of data handling remains transparent and audited by our security lead.

Can outsourced QA services integrate with our existing Jira and DevOps tools?

Our outsourced qa services integrate directly into your existing CI/CD pipelines via Jira Service Management and the wider Atlassian toolset. By aligning with your DevOps workflows, we automate bug reporting and tracking to ensure real-time visibility into the testing lifecycle. This synchronization eliminates communication silos and accelerates the feedback loop between developers and testers, resulting in a 25% increase in sprint velocity.

What is the difference between QA staff augmentation and managed testing services?

QA staff augmentation provides individual experts to work under your internal management, whereas managed testing services offer a fully autonomous team responsible for end-to-end delivery. In a staff augmentation model, you retain 100% control over daily tasks; however, managed services shift the accountability for KPIs and outcomes to the partner. This distinction allows you to choose between tactical support and strategic, results-driven transformation.

Why is specialized QA important for the pharmaceutical and life sciences industries?

Specialized QA is critical for pharmaceutical sectors because it ensures compliance with GxP and FDA 21 CFR Part 11 regulations. By applying rigorous validation protocols, we mitigate the risk of non-compliance which can lead to significant regulatory fines. Our approach integrates automated compliance checks into the software lifecycle, protecting patient safety and data accuracy in these highly regulated environments.

How do we measure the ROI of outsourcing our quality assurance?

You measure ROI by tracking metrics such as defect leakage rates and the reduction in cost-per-test hour. Organizations typically see a 15% reduction in post-release defects within the first 12 months of a strategic partnership. By calculating the difference between internal overhead and the output of a flexible engagement model, you can quantify the total value delivered to your bottom line.

What should be included in a QA outsourcing Service Level Agreement (SLA)?

A robust SLA must include specific targets for defect turnaround times, test coverage percentages, and resource availability. We define clear benchmarks, such as a 24-hour resolution window for critical bugs, to ensure accountability and performance stability. These documented standards act as a roadmap for our partnership, ensuring that Technology, Talent, and Transformation remain aligned with your business objectives.

How quickly can an outsourced QA team be onboarded into our project?

Our team can typically be fully onboarded and integrated into your project within 10 to 14 business days. By following a structured knowledge transfer framework, we minimize downtime and begin delivering actionable insights during the very first sprint. This rapid deployment model allows your organization to scale testing capacity instantly without the 60-day lead time common in traditional recruitment cycles.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.