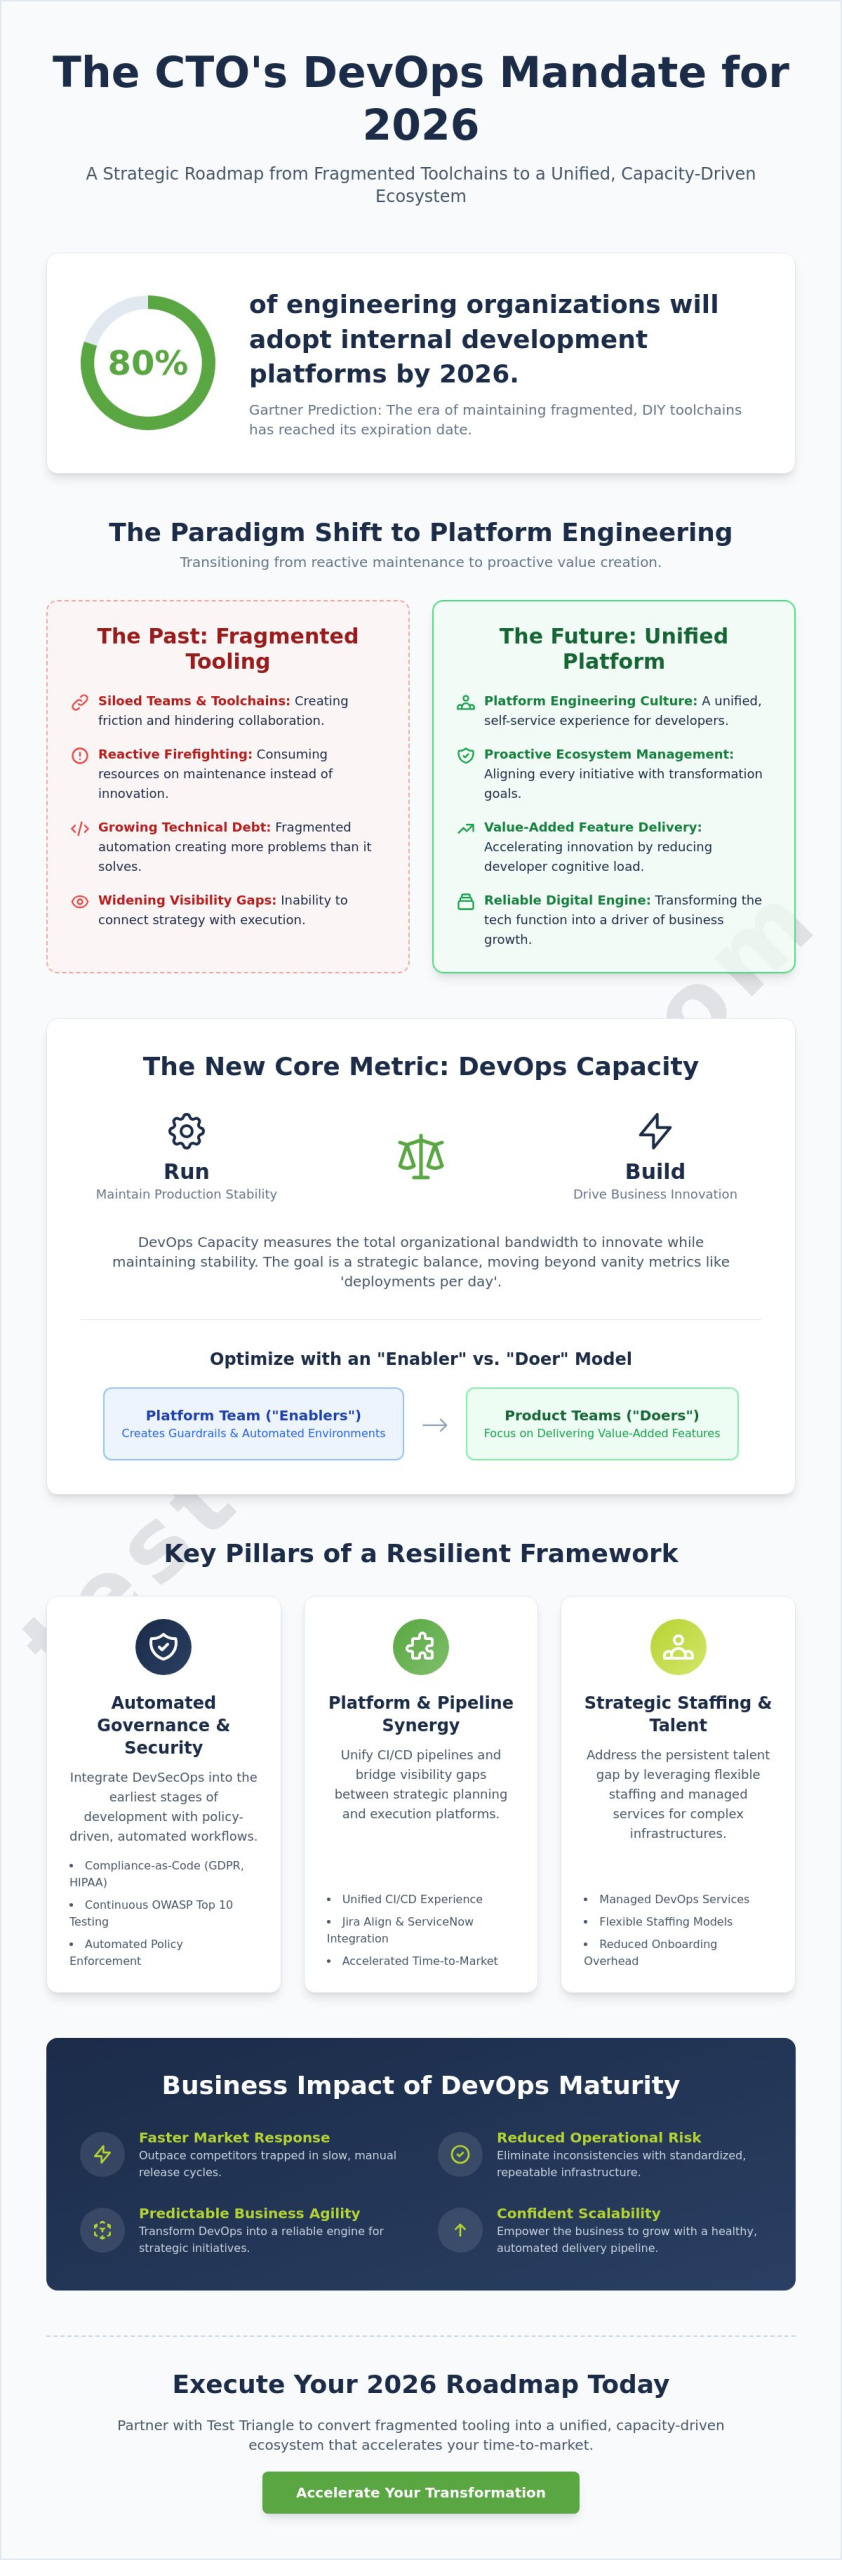
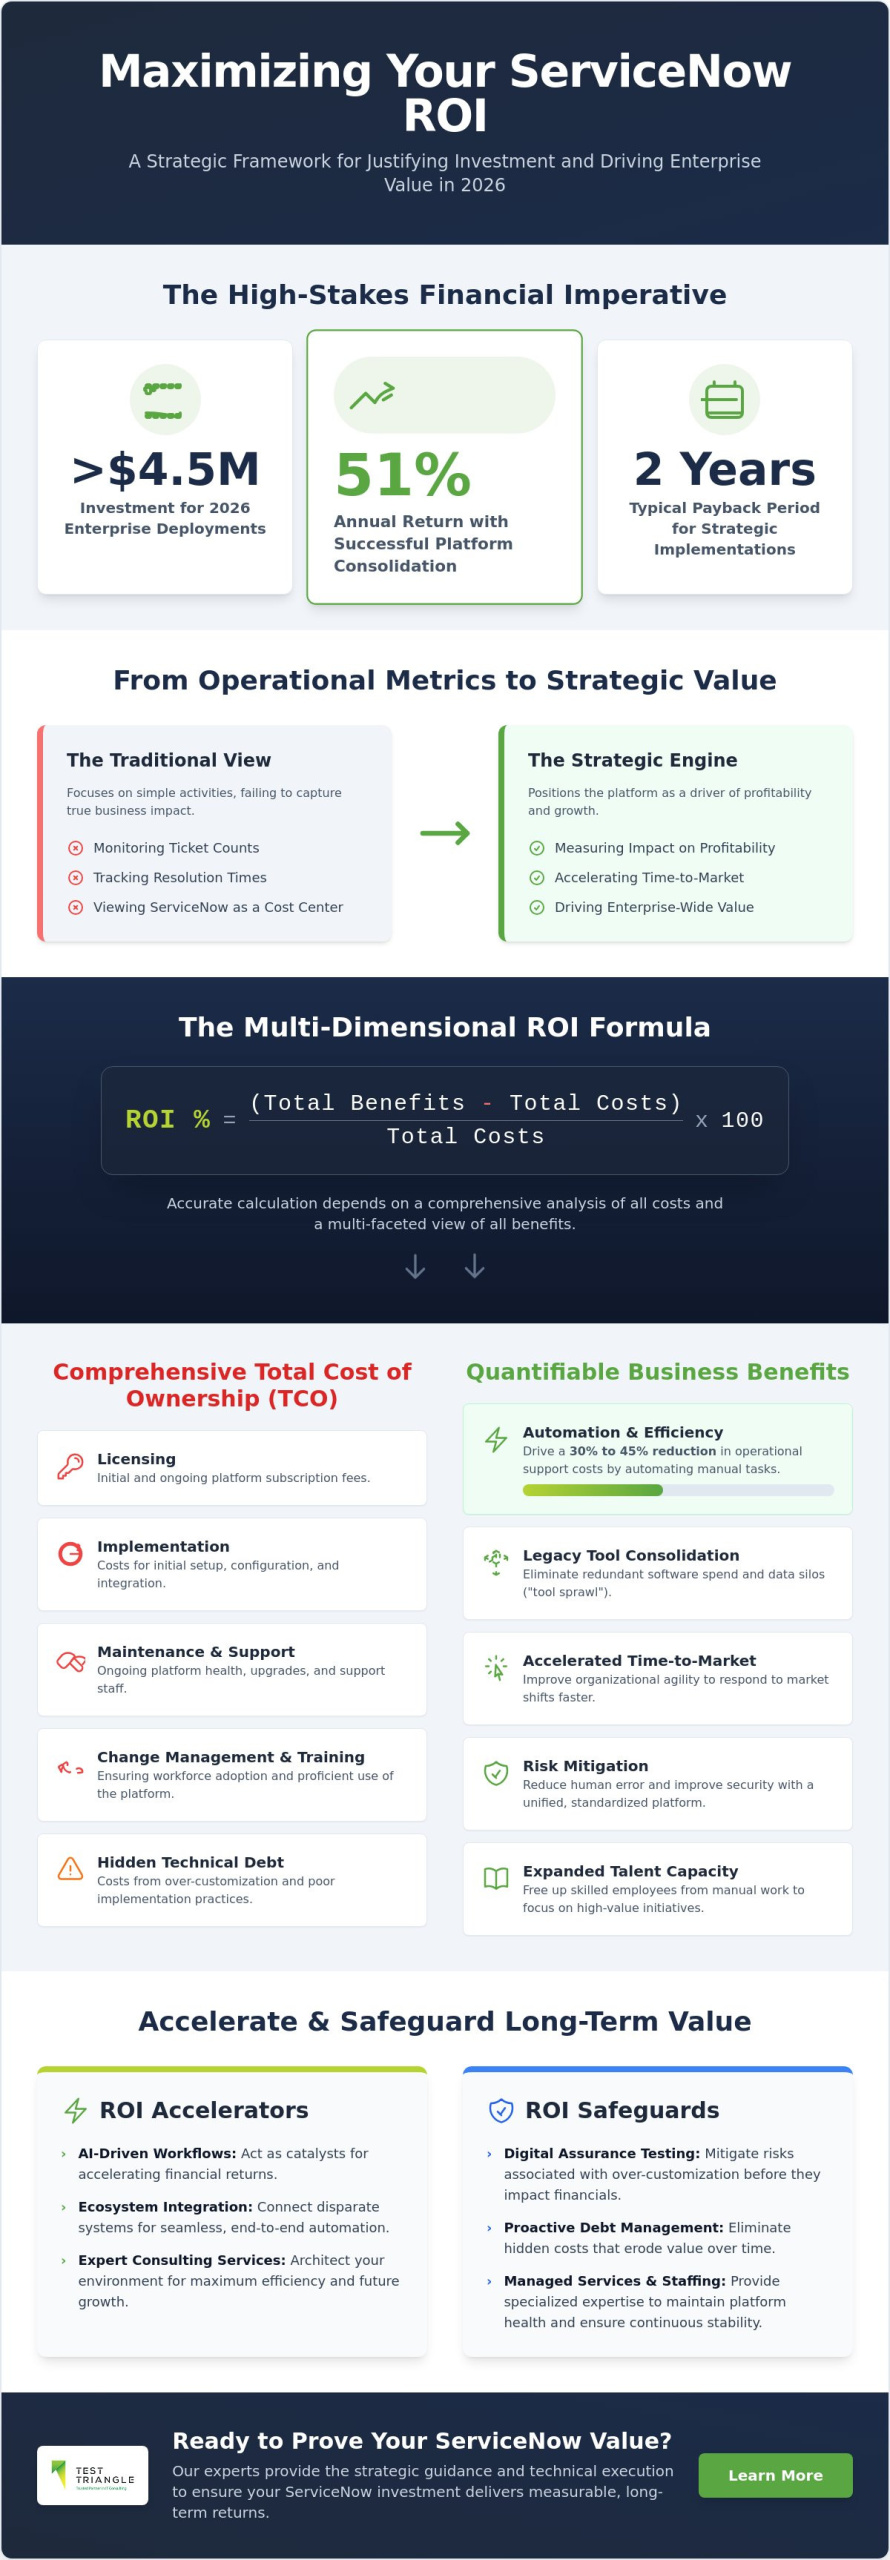
While enterprise deployments in 2026 can require investments exceeding $4.5 million, organizations that successfully execute platform consolidation are realizing an annual return of 51% and a two year payback period. It’s a significant figure that highlights the platform’s potential, yet many leaders still struggle with calculating ServiceNow implementation roi because traditional metrics often fail to capture the nuances of digital transformation. You likely recognize that ServiceNow is more than a ticketing tool; it’s a strategic engine for growth. However, the constant pressure to justify escalating licensing fees while managing the hidden costs of technical debt can make financial validation feel like a moving target.

We’ve designed this framework to bridge the gap between technical execution and executive accountability by providing a clear reporting structure for your investment. You’ll learn how to quantify soft benefits such as user experience improvements, identify the automation areas that drive a 30% to 45% reduction in operational support costs, and validate the consolidation of redundant legacy tools. This guide moves beyond static spreadsheets to offer a dynamic methodology, ensuring you can secure long term operational stability and prove that your ServiceNow roadmap is a disciplined driver of enterprise value.

Key Takeaways

  • Transition from monitoring basic operational activities to measuring strategic business value to ensure your platform investment aligns with 2026 enterprise objectives.
  • Master a multi-dimensional framework for calculating servicenow implementation roi that accurately accounts for both direct cost reductions and indirect productivity enhancements.
  • Identify how AI-driven workflows and broader digital transformation services act as catalysts for accelerating financial returns and expanding organizational talent capacity.
  • Safeguard your long-term financial outcomes by implementing rigorous digital assurance testing to mitigate the risks associated with over-customization and technical debt.
  • Explore how managed services and strategic IT staffing provide the specialized expertise required to maintain platform health and drive continuous operational stability.

The Strategic Imperative of Quantifying ServiceNow Business Value

In the high-stakes corporate environment of 2026, a standard Return on Investment (ROI) calculation is no longer sufficient to justify the scale of enterprise software commitments. Leaders must define ServiceNow ROI as the measurable impact of digitized workflows on overall enterprise profitability. This shift is essential because current market dynamics demand a transition from monitoring simple operational activities to identifying strategic value drivers that empower global growth. By moving beyond the narrow scope of ticket counts, organizations can position ServiceNow as a steady hand that guides the enterprise through technological volatility while ensuring long-term operational stability.

Establishing a baseline for calculating ServiceNow implementation roi requires a clear distinction between activity and value. While resolving a high volume of tickets suggests a productive service desk, it doesn’t necessarily correlate with financial gain if those tickets represent avoidable friction or redundant manual work. True value is realized when automation reduces the cost per transaction and mitigates the risks associated with human error. This approach transforms the platform from a back-office expense into a disciplined engine for strategy, execution, and success.

Shifting from Operational Metrics to Strategic Outcomes

While ticket resolution time remains a common KPI, it’s a surface-level metric that fails to capture the needs of modern enterprises. For global organizations, the more critical metric is the connection between workflow speed and the time-to-market for new business services. When you leverage ServiceNow consulting services to architect your environment, you aren’t just fixing IT issues; you’re accelerating the entire organization’s ability to respond to market shifts. Platform consolidation plays a vital role here by eliminating the redundant software spend and data silos that often plague large-scale digital infrastructures. Reducing this “tool sprawl” provides the peace of mind that comes from a unified, secure, and highly efficient digital ecosystem.

The Total Cost of Ownership (TCO) Equation

A comprehensive approach to calculating ServiceNow implementation roi must account for the full Total Cost of Ownership, which extends far beyond initial licensing. You’ve got to factor in the implementation phase, ongoing platform maintenance, and the inevitable costs of organizational change management. Many enterprises find that the balance between internal staffing and external expertise significantly impacts the TCO baseline. Utilizing managed outsourcing services often proves more cost-effective than maintaining a massive internal team, as it provides access to specialized skills without the overhead of full-time recruitment. Furthermore, don’t overlook the cost of training; ensuring your workforce is empowered to use the platform’s advanced automation is the only way to safeguard your investment and drive the precision, performance, and peace of mind your stakeholders expect.

A Multi-Dimensional Formula for Calculating Implementation ROI

To move beyond anecdotal evidence of success, organizations must adopt a rigorous mathematical approach to financial validation. The standard formula for calculating ServiceNow implementation roi is expressed as: (Total Benefits – Total Costs) / Total Costs x 100. While the equation appears straightforward, its accuracy depends on a comprehensive Total Cost of Ownership (TCO) calculation that accounts for licensing, implementation, and the organizational change management required for adoption. In the context of 2026 enterprise deployments, ServiceNow ROI acts as a longitudinal measure of platform maturity and cost recovery, reflecting an organization’s ability to extract continuous value from digitized workflows over time.

Time to Value (TTV) is a critical component of this framework, particularly for large scale deployments that may span 9 to 12 months. Shortening the TTV ensures that the organization begins realizing cost offsets earlier in the lifecycle, which is vital for maintaining stakeholder confidence. If you’re looking to refine your specific financial model, you might consider how our ServiceNow consulting services can help align these metrics with your broader corporate objectives.

Quantifying Direct Cost Savings

Direct savings provide the most immediate evidence of fiscal discipline. By automating incident management and request fulfillment, organizations can achieve a 35% to 50% reduction in IT labor hours, allowing staff to pivot toward innovation. Furthermore, properly architected deployments typically see a 30% to 50% decrease in Mean Time to Repair (MTTR) within the first six months, which significantly reduces the financial impact of system downtime. Platform consolidation further strengthens the balance sheet; by eliminating the maintenance fees of redundant legacy tools, CIOs can realize an annual ROI of approximately 51%. This systematic approach ensures stability, scalability, and success across the digital infrastructure.

Measuring Indirect Productivity Gains

Indirect gains often represent the largest portion of long term value, though they require more nuanced tracking. Improved employee self-service adoption is a primary driver here; when mature knowledge management and AI assisted workflows are in place, First Contact Resolution (FCR) rates should exceed 70%. This shift reduces administrative friction by allowing cross-departmental workflows to trigger automatically, bypassing manual bottlenecks. We also recommend quantifying the “Experience Factor,” which measures the productivity boost derived from high quality internal and customer interactions. When employees spend less time navigating complex legacy processes, they’re empowered to focus on strategic growth. To explore how these metrics apply to your unique environment, you can reach out to our strategic team for a detailed assessment.

Accelerating Returns through Ecosystem Integration and AI

ServiceNow serves as a powerful catalyst for broader Digital Transformation Services, acting as the connective tissue between disparate enterprise systems. When you integrate ServiceNow with ecosystems like AWS and Atlassian, you create a multiplier effect that significantly enhances the value of each individual platform. This interconnectedness is a pivotal factor when calculating ServiceNow implementation roi, as the returns are no longer confined to IT service management but extend across the entire software development lifecycle. By leveraging DevOps Consulting to align these tools, organizations can accelerate release cycles and ensure that technical execution directly supports business agility.

One of the most profound, yet frequently overlooked, benefits is the ROI of Talent Capacity. By automating the mundane, repetitive tasks that consume your workforce’s time, you empower your existing staff to focus on high-value innovation. This transition from “keeping the lights on” to driving strategic growth provides a sense of empowerment and institutional maturity. It’s about more than just saving hours; it’s about repurposing human expertise to solve complex challenges that a machine cannot, thereby securing your company’s long-term competitive advantage through stability, precision, and scalable growth.

The ROI of Platform Integration

The value of seamless data synchronization between ServiceNow and DevOps tools cannot be overstated. When information flows freely between platforms, you effectively eliminate the data silos that lead to miscommunication and project delays. This integration reduces “swivel-chair management,” where employees manually copy data from one system to another; this process is both inefficient and prone to error. By automating these handoffs, enterprises see a marked improvement in operational precision. This level of coordination ensures that every stakeholder operates from a single source of truth, fostering a culture of reliability and trust.

AI and Machine Learning Returns

The adoption of AI and Machine Learning within the ServiceNow platform offers some of the most quantifiable returns in 2026. Virtual Agents and Predictive Intelligence are no longer experimental; they’re essential tools for handling high-volume requests without human intervention. Mature enterprises report up to a 99.2% reduction in event noise through AIOps, which allows IT teams to ignore the clutter and focus on genuine threats. This AI-driven root cause analysis can cut Mean Time to Resolution (MTTR) by as much as 50%, directly impacting system stability and user satisfaction. Additionally, the role of GenAI in reducing the time required for documentation and knowledge base creation further accelerates the recovery of your initial investment, making the process of calculating ServiceNow implementation roi a clear demonstration of technological evolution.

Safeguarding ROI: Eliminating Technical Debt and Implementation Pitfalls

The mathematical model for calculating ServiceNow implementation roi is only as resilient as the platform’s underlying architecture. While the initial business case often focuses on immediate automation gains, long term financial success is frequently compromised by the silent accumulation of technical debt. Over-customization stands as the primary driver of this value erosion; when organizations deviate too far from standard features to satisfy niche departmental requests, they inadvertently create a rigid environment that is expensive to maintain and difficult to evolve. This complexity often leads to “shadow IT” workarounds, where frustrated users return to manual spreadsheets, effectively nullifying the productivity gains promised during the planning phase.

It’s a common misconception to view ServiceNow implementation as a one-and-done capital expense. In reality, the platform requires a disciplined, evergreen approach to ensure that the cost of recovery doesn’t eventually exceed the value of the digitized workflows. Organizations that fail to account for the ongoing necessity of platform health checks often see their ROI drop by 40% to 60% due to scope creep and technical inefficiencies. To ensure your investment remains a strategic asset rather than a legacy burden, you can consult with our architectural experts for a comprehensive platform audit.

The High Cost of Technical Debt

Custom code acts as a heavy anchor during the twice yearly ServiceNow upgrade cycle, significantly increasing the labor hours required for testing and remediation. To maintain a high “Upgradeability Score,” strategic leaders are increasingly prioritizing a return to Out-of-the-Box (OOTB) functionality. This methodology ensures that the enterprise can immediately leverage new features, such as advanced AI capabilities, without being held back by bespoke scripts that break during version transitions. By treating OOTB as a mandatory standard, you protect the platform’s institutional maturity and ensure that your TCO remains predictable and manageable.

Assurance and Testing as ROI Safeguards

The cost of poor quality is a direct hit to your bottom line, making Software and Digital Assurance Testing an essential protector of your investment. Automated regression testing is particularly vital for every new release, as it provides the peace of mind that existing workflows remain intact while new features are deployed. While automation handles the repetitive checks, Manual Testing remains indispensable for validating complex user journeys and ensuring that the human experience matches technical expectations. This rigorous QA approach prevents production defects that would otherwise result in costly system downtime and lost employee productivity, effectively safeguarding the precision and performance of your digital infrastructure.
Calculating ServiceNow Implementation ROI: A Strategic Framework for 2026

Optimising Long-Term ROI with Managed Services and Flexible Staffing

Achieving a sustainable return requires more than just a successful initial deployment; it demands a resource strategy that balances technical rigor with fiscal agility. While the mathematical framework for calculating ServiceNow implementation roi accounts for licensing and technical debt, the long term trajectory of that value is often determined by the quality of ongoing support. By positioning ServiceNow Consulting Services as the bridge between operational costs and business value, enterprises can ensure that their digital infrastructure remains aligned with evolving corporate objectives. This disciplined approach provides the peace of mind that comes from knowing your platform is managed by experts who prioritize resilience, reliability, and return.

Managed Services vs. In-House Maintenance

Transitioning to a fixed-fee model through Managed Outsourcing Services offers a predictable cost structure that is often superior to the variable expenses of internal hiring. When you maintain a large in-house team, you’re responsible for recruitment, training, and retention in a highly competitive market for ServiceNow specialists. Conversely, a managed service provider grants you immediate access to global expertise, including remote and offshore resources that can provide round-the-clock support without the overhead of permanent headcount. This continuous optimisation prevents platform stagnation, ensuring that your environment is always leveraging the latest automation capabilities to drive cost recovery.

Scaling with Flexible Staffing Models

Specific industries require specialized knowledge to maintain compliance and quality standards. For instance, highly regulated sectors often turn to IT staffing agencies for pharmaceutical industry requirements to find vetted professionals who understand the nuances of GxP compliance within ServiceNow. Utilizing Staffing Solutions allows you to scale your team with “just-in-time” talent for specific implementation phases or complex upgrades. This flexibility is a vital component when calculating ServiceNow implementation roi, as it reduces placement fees and allows you to pay only for the specialized skills you need, when you need them.

Ultimately, the path to long term success is paved through partnership. By choosing a reliable long-term collaborator, you move beyond the role of a service consumer and become a strategic partner in your own technological evolution. This collaborative spirit ensures that your ServiceNow investment continues to deliver operational stability and measurable profitability through a combination of human expertise and technical precision. We remain committed to your long term growth, providing the steady hand needed to navigate a fast changing technological landscape with strategy, support, and success.

Driving Sustained Enterprise Value Through Strategic Platform Governance

When organizations navigate the complexities of the 2026 digital landscape, calculating ServiceNow implementation roi must evolve from a one-time audit into a continuous discipline of value realization. By prioritizing out-of-the-box functionality to mitigate technical debt and integrating AI-driven workflows to enhance talent capacity, enterprise leaders can transform their digital infrastructure into a resilient engine for profitability. Achieving this level of institutional maturity requires a steady hand and a reliable long-term collaborator who understands the intricate requirements of highly regulated industries like Pharma and Finance.

As an Authorized ServiceNow and Atlassian Partner, we provide a global delivery model that leverages offshore cost advantages to deliver precision, performance, and peace of mind. Our approach ensures that your technological evolution is managed with the specialized expertise necessary to safeguard your investment and drive scalable growth. Maximize your platform value with our ServiceNow Consulting Services and secure the operational stability your enterprise deserves. We look forward to supporting your journey toward digital excellence and long-term success.

Frequently Asked Questions

How long does it typically take to see a positive ROI from ServiceNow?

Most global enterprises realize a full return on their investment within a 24 month period. While initial operational improvements such as labor hour recovery often manifest within the first six months, the break-even point typically occurs once the organization has successfully executed platform consolidation and moved into a state of continuous optimization. This timeline ensures that the stabilization phase is complete and the compounding benefits of automated governance are fully realized.

What are the most important KPIs for measuring ServiceNow implementation success?

Success is measured through a sophisticated blend of financial and operational indicators, specifically Mean Time to Resolution (MTTR), labor hour recovery, and the total reduction in legacy tool licensing fees. Strategic leaders also prioritize tracking First Contact Resolution (FCR) rates and self-service adoption levels. These metrics provide a comprehensive view of how digitized workflows are reducing administrative friction and empowering the workforce to focus on high-value innovation.

Does over-customising ServiceNow really decrease its long-term ROI?

Extensive customization significantly erodes long term value by increasing the technical debt and labor costs associated with bi-annual platform upgrades. By deviating from out-of-the-box functionality, organizations create a rigid environment that requires manual remediation during every version transition, which eventually inflates the Total Cost of Ownership. Maintaining architectural discipline ensures the platform remains agile and capable of adopting new features, such as advanced AI, without costly bespoke re-engineering.

How can I calculate the ROI of ServiceNow AI and automation features?

Evaluating the impact of AI involves measuring ticket deflection rates through virtual agents and the reduction in event noise provided by AIOps. When calculating ServiceNow implementation roi for these advanced modules, it’s essential to quantify the talent capacity gained by your technical staff. Shifting human expertise from routine alert management to strategic growth projects represents a substantial gain in organizational productivity and institutional maturity.

Is it better to use an MSP or in-house staff for ServiceNow maintenance to maximize ROI?

Utilizing a Managed Service Provider (MSP) often delivers a more predictable return by replacing variable internal recruitment and training costs with a disciplined, fixed-fee model. This strategic approach provides immediate access to a global pool of certified specialists, ensuring that platform maintenance is handled with precision and reliability. While in-house teams offer internal proximity, the MSP model typically fosters greater operational stability through continuous, expert-led optimization and risk reduction.

What is the role of testing and QA in protecting ServiceNow investment value?

Rigorous digital assurance acts as a critical safeguard that prevents production defects from compromising system availability and user trust. Automated regression testing ensures that new releases don’t disrupt established workflows, while manual validation protects the integrity of complex user journeys. By preventing unplanned downtime and the associated loss of employee productivity, a disciplined testing strategy directly protects the financial integrity of your large-scale technological evolution.

How do I justify the recurring licensing costs of ServiceNow to my CFO?

Justifying recurring fees requires framing ServiceNow as a unified platform that drives cost recovery through the consolidation of redundant legacy software. You should highlight the potential for a 51% annual ROI and the 30% to 45% reduction in operational support costs achieved through mature ITSM automation. Demonstrating how the platform acts as a steady hand that reduces enterprise risk allows executive leadership to view licensing as a strategic investment in long-term success.

Can ServiceNow ROI be measured across non-IT departments like HR or Legal?

Measuring calculating ServiceNow implementation roi across non-IT functions is highly effective when focusing on metrics such as onboarding speed and case resolution efficiency. Organizations utilizing HR Service Delivery frequently report a 60% to 75% improvement in new hire onboarding time, which significantly reduces administrative bottlenecks. These cross-departmental efficiencies ensure that the benefits of digitized workflows are felt across the entire enterprise, providing a consistent and empowered experience for all employees.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.
Why do most enterprise leaders find their ServiceNow budgets ballooning by nearly double the initial estimate within the first eighteen months? It’s because the hidden costs of servicenow implementation aren’t just minor oversights; they’re the predictable consequences of treating a massive architectural shift as a simple software purchase. You likely already understand that the Now Platform is a cornerstone of digital evolution, yet the reality of opaque licensing and complex legacy integrations often creates a significant gap between expected value and actual spend.

We’re here to bridge that gap by uncovering the invisible financial traps and operational overheads that frequently derail even the most ambitious digital transformations. This guide delivers a transparent TCO framework designed to stabilize your budget and ensure your 2026 deployment remains strategically aligned with your broader business goals. We’ll explore how a disciplined approach to data management and training can transform potential overhead into predictable progress, securing the high ROI your organization demands while avoiding the common integration failures that stall momentum. By focusing on stability, precision, and growth, you can move from the “Zurich” release through the upcoming “Australia” update with total financial confidence.

Key Takeaways

  • Identify the structural drivers behind the 40-60% budget overruns common in enterprise deployments by navigating the complex ServiceNow “Custom Quote Maze.”
  • Mitigate the hidden costs of servicenow implementation by avoiding excessive architectural debt and the subsequent “upgrade tax” that restricts access to new platform features.
  • Calculate the true operational impact of internal opportunity costs, ensuring that the diversion of your subject matter experts does not compromise core business stability.
  • Implement a rigorous quality assurance framework and pre-implementation audit to identify technical hurdles before they escalate into expensive post-launch fixes.
  • Adopt a phased rollout methodology that balances out-of-the-box functionality with essential business customization to ensure a predictable and scalable total cost of ownership.

The ServiceNow Implementation Mirage: Why Initial Quotes Are Just the Tip of the Iceberg

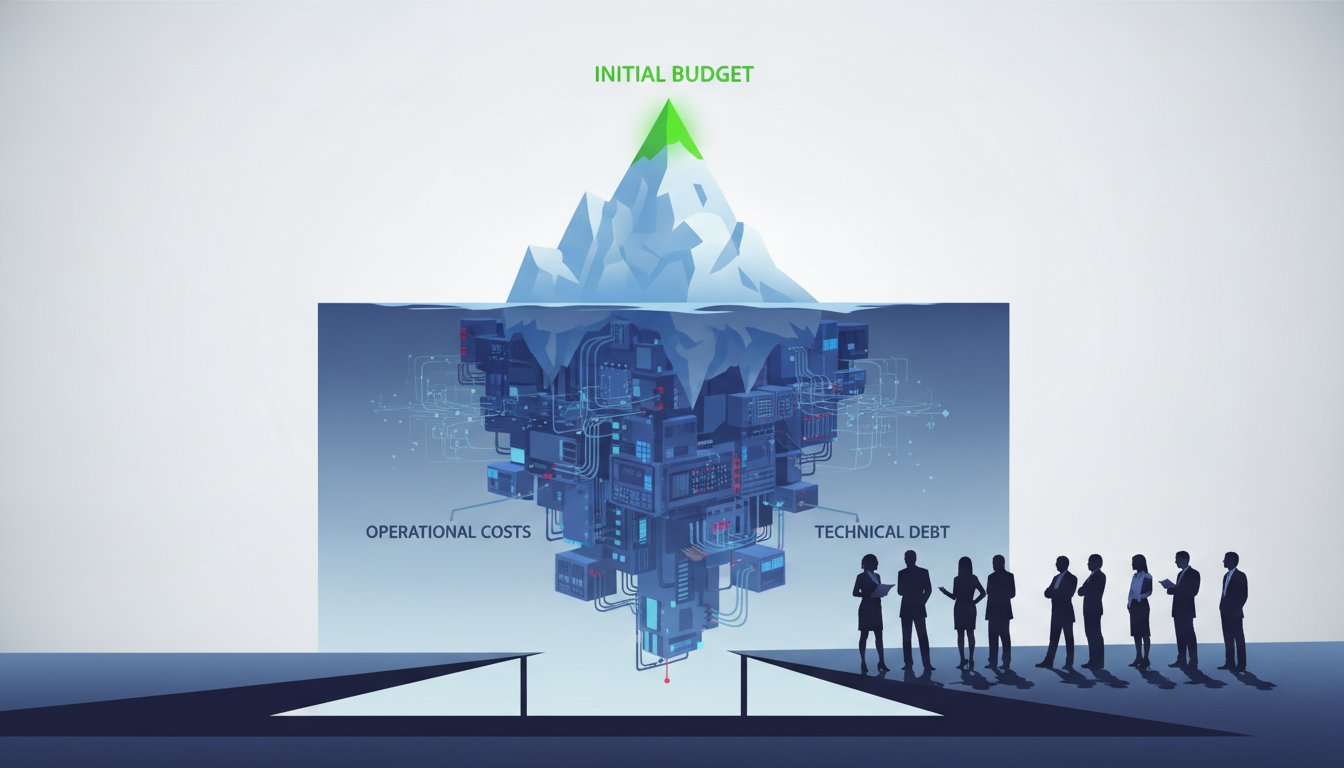
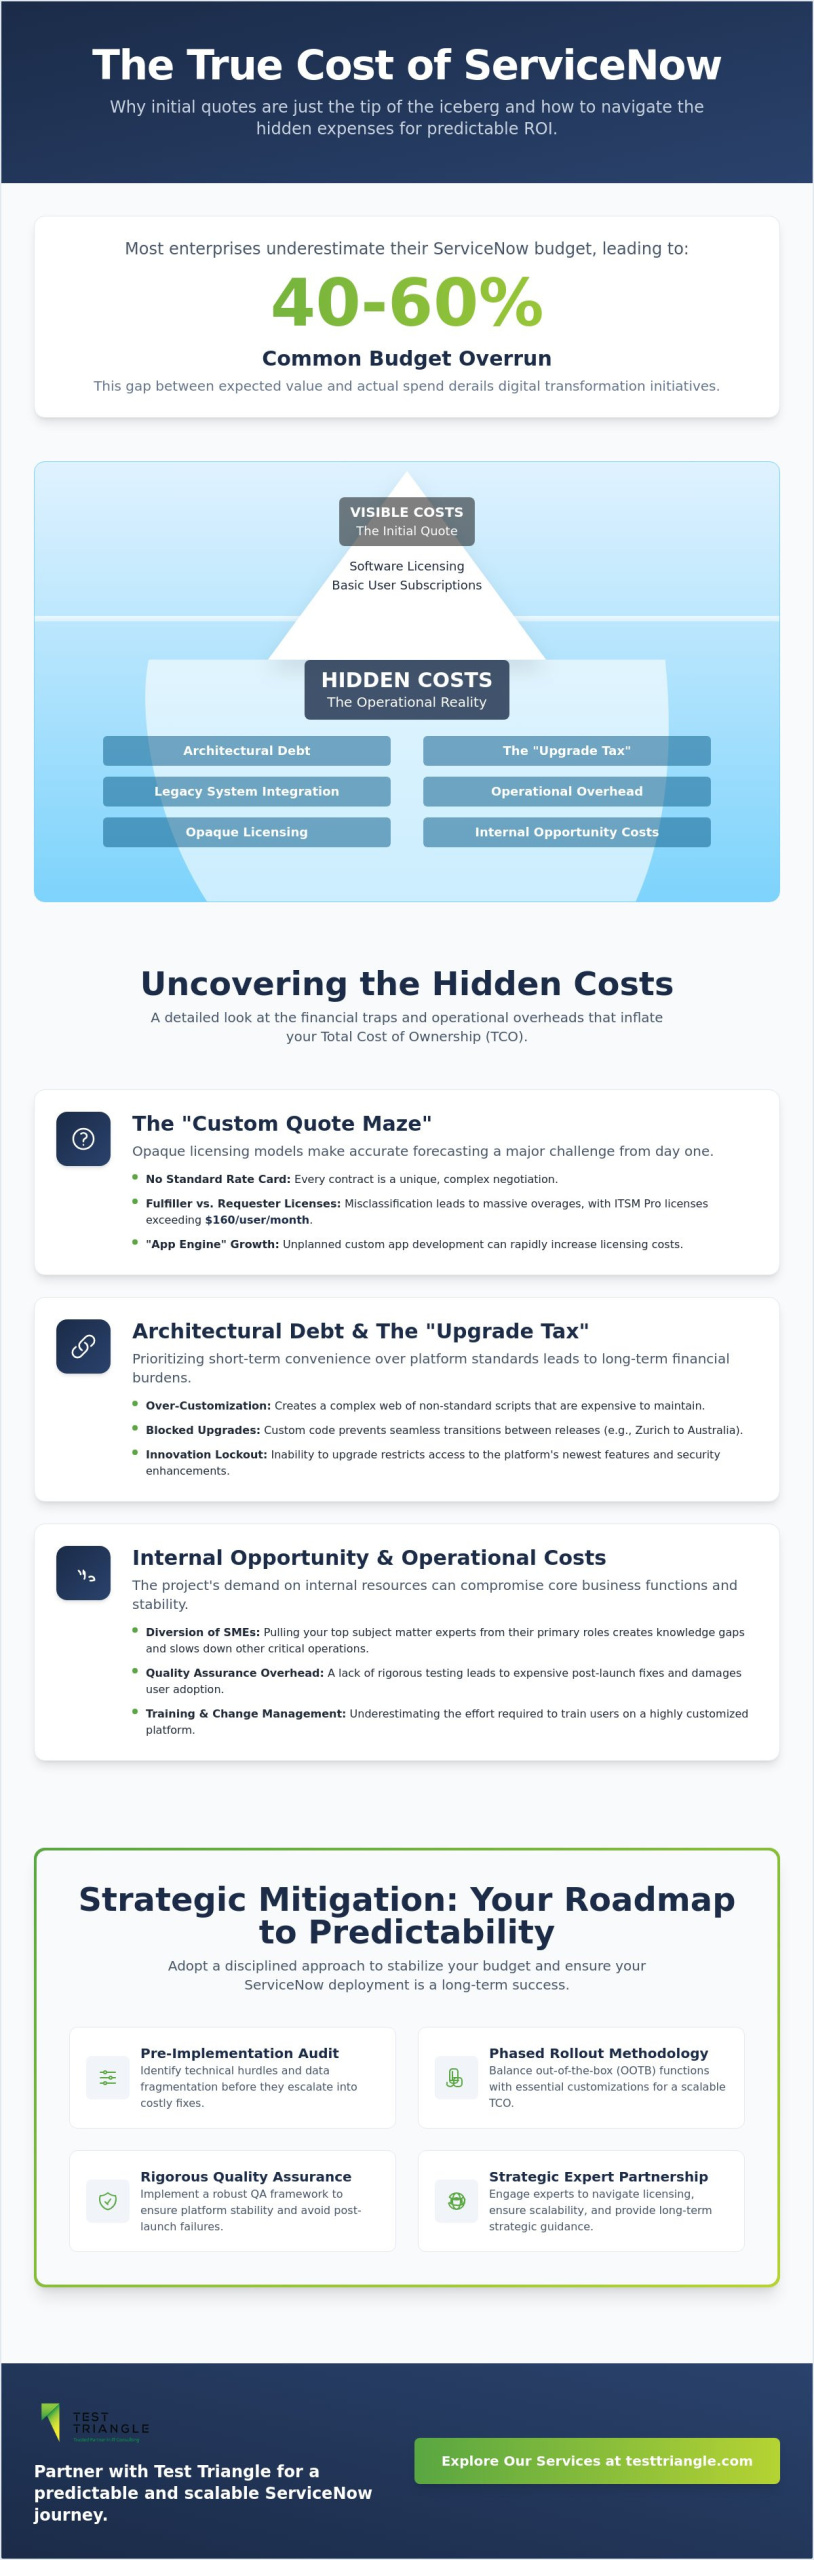
The initial engagement with the ServiceNow platform often begins with a sense of optimism that’s quickly tempered by the reality of the “Custom Quote Maze.” Since the company doesn’t publish a standard rate card, every enterprise enters a highly negotiated environment where the final contract reflects a unique combination of user count, selected modules, and organizational scale. This lack of transparency often masks the hidden costs of servicenow implementation, leading many executives to mistake the licensing fee for the total investment. It’s a strategic oversight that can compromise long-term operational stability.

Industry data suggests that most enterprises underestimate their initial budget by 40% to 60%. This discrepancy occurs because the quote focuses on software acquisition, failing to account for the structural remediation required to make the platform functional. Think of it as the “Renovation Analogy.” Just as a contractor can’t know the state of a building’s internal wiring until the walls are opened, an implementation partner can’t fully assess the complexity of your legacy data until the project begins. If your IT foundation is fragmented, the effort to align it with ServiceNow’s architecture can easily double your projected timelines. Precision, predictability, and performance require looking far beyond the initial sales proposal.

The Gap Between Licensing and Functional Reality

A common pitfall is viewing a ServiceNow license as a finished solution rather than a sophisticated entry ticket. While the “Out-of-the-Box” (OOTB) promise is a powerful marketing narrative, it’s often a financial trap for organizations with unique regulatory requirements or complex workflows. Turning on a module is a technical task; configuring it to mirror your specific business logic requires deep strategic alignment. Without this alignment, the hidden costs of servicenow implementation surface through endless “fix-it” cycles that occur after the initial launch. True platform readiness involves bridging the gap between what the software can do and what your specific business needs it to do.

The 2026 Pricing Landscape: Fulfillers vs. Requesters

Within the 2026 fiscal environment, the distinction between Fulfiller and Requester licenses has become a critical focal point for budget stability. Fulfiller licenses, particularly for ITSM Professional with AI capabilities, carry a premium that can exceed $160 per user per month. Misclassifying users or failing to account for the growth of your “App Engine” footprint can lead to massive annual overages. To ensure a predictable roadmap, organizations must partner with experts who provide ServiceNow consulting services tailored to long-term scalability. This approach ensures that user-type classification remains accurate as your digital infrastructure evolves, providing the peace of mind that comes from financial precision and systemic improvement.

Architectural Debt: The Long-Term Cost of Over-Customization

While the initial deployment of the ServiceNow platform often focuses on immediate functional gains, the long-term financial burden of “architectural debt” represents one of the most significant hidden costs of servicenow implementation. This debt accumulates when organizations prioritize short-term convenience over platform standards, leading to a complex web of custom scripts and modified workflows. According to research on IT projects, large-scale software initiatives often exceed budgets not because of the initial build, but due to the unforeseen complexity of maintaining non-standard environments. In the ServiceNow ecosystem, this manifests as the “Upgrade Tax,” where custom code prevents your organization from seamlessly transitioning between releases like Zurich and Australia, effectively locking you out of the very innovation you’re paying for.

Integration complexity adds another layer to this financial iceberg. Connecting ServiceNow to high-scale environments like AWS or legacy ERP systems requires a disciplined approach to data throughput and API management. If your team builds custom point-to-point integrations instead of utilizing the native IntegrationHub, you aren’t just paying for the initial development. You’re committing to a permanent maintenance cycle where every third-party update risks breaking your connection. Furthermore, the cost of migrating “dirty data” into a clean ServiceNow instance is a major budget driver. Industry benchmarks suggest that organizations should allocate 20% to 30% of their total implementation budget purely for data migration and cleansing activities to avoid expensive post-launch remediation.

The High Price of Deviating from the OOTB Path

Every line of specialized script represents a future maintenance liability. To protect your return on investment, technical debt must be treated as a transparent line item in your initial budget rather than an afterthought. Strategic leaders prioritize stability, precision, and progress by enforcing a “standard-first” policy that minimizes deviations from out-of-the-box (OOTB) functionality. When customization is unavoidable, it must be documented with the same rigor applied to core business logic to ensure that future upgrades don’t become multi-month rescue missions. If you’re concerned about how your current customizations might impact future scalability, you may want to consult with a strategic partner to audit your roadmap.

Integration Hub and Third-Party API Costs

Modern ServiceNow deployments increasingly rely on automated workflows that connect to external clouds. However, many executives are surprised by transaction-based costs associated with IntegrationHub spokes and automated “pro” features. When scaling AWS Cloud Migration initiatives, the financial impact of API rate limits and data throughput charges can escalate quickly. Managing these costs requires a sophisticated understanding of how data flows between platforms. By balancing the use of IntegrationHub with a clear strategy for high-volume data exchanges, you can avoid the throughput charges that often quietly double the operational overhead of a connected enterprise.

The Operational Iceberg: Personnel, Training, and Quality Assurance

Beyond the technical architecture and licensing fees, the human element represents a massive portion of the hidden costs of servicenow implementation. Executives often overlook the “invisible” salary spend associated with their subject matter experts (SMEs). When you divert your top process owners from their core responsibilities to guide a deployment, the resulting productivity dip is a direct, yet unrecorded, expense. This internal opportunity cost is compounded by a specialized talent gap; industry professionals report that hiring dedicated ServiceNow developers often requires a 30% premium over standard IT roles due to the platform’s unique niche and the high demand for certified expertise.

The “QA Deficit” is another significant financial trap that emerges when organizations treat testing as a perfunctory final step rather than a strategic safeguard. Skipping rigorous validation leads to “post-launch shock,” where remediating a bug in a live environment can cost five to ten times more than fixing it during the development phase. Effective change management is equally vital; without it, employee resistance leads to platform underutilization. You don’t want to pay for a high-performance engine only to have your team use it like a basic spreadsheet. Success requires a disciplined focus on order, oversight, and optimization.

The Critical Role of Software and Digital Assurance

Rigorous quality assurance is the most effective way to protect your digital investment from unforeseen operational overhead. While automated tools are powerful, Manual Testing remains essential for validating complex ServiceNow workflows that involve nuanced human decision-making. By leveraging Software Test Automation Services, your organization can create a repeatable regression suite that reduces long-term maintenance spend. This “Shift Left” approach ensures that quality is baked into the methodology, preventing the architectural flaws that often derail 2026 deployment timelines.

Training and Platform Governance

Continuous learning is a mandatory operational expense, not a one-time workshop. As ServiceNow moves from the Zurich release toward Australia, your team must stay updated on new AI-driven decision intelligence and agentic capabilities to maintain peak efficiency. Establishing a Center of Excellence (CoE) is a proven strategy for preventing platform sprawl and the accumulation of “Zombie Modules”—those expensive, licensed features that sit idle because no one knows how to govern them. Strategic alignment between platform capabilities and business goals ensures that every dollar spent on training translates into tangible, scalable growth.

The Hidden Costs of ServiceNow Implementation: A Strategic Executive Guide for 2026

Strategic Mitigation: Auditing Your 2026 Implementation Roadmap

Mitigating financial risk requires a disciplined transition from reactive troubleshooting to proactive platform governance. A comprehensive pre-implementation audit serves as the diagnostic foundation, identifying the hidden costs of servicenow implementation before they manifest as significant budget overruns. This audit should scrutinize your existing data architecture and process maturity to determine whether a “Phased Rollout” or a “Big Bang” approach better suits your organizational risk profile. While a Big Bang deployment promises immediate consolidation, it frequently results in higher post-launch remediation costs. Conversely, a phased approach provides the flexibility to refine workflows based on real-world usage, ensuring that each milestone delivers stability, precision, and performance.

As we move through 2026, new financial variables have entered the landscape, specifically regarding AI compute credits and ESG reporting modules. The “Zurich” and upcoming “Australia” releases emphasize agentic AI and autonomous service management, which rely on a credit-based consumption model rather than traditional flat-fee licensing. Failing to forecast the volume of AI-driven transactions can lead to unexpected mid-quarter invoices. Furthermore, the rising demand for Environmental, Social, and Governance (ESG) transparency means that organizations must budget for specialized modules that track sustainability metrics across the digital supply chain. These emerging drivers represent the next frontier of total cost of ownership (TCO) management.

The Value of Managed Outsourcing

Comparing the expense of internal hiring against Managed Outsourcing Services is a critical step in stabilizing your post-implementation burn rate. Maintaining a full-time, in-house team of ServiceNow architects is often 30% more expensive than standard IT staffing, making a structured support model more financially viable for many global enterprises. By utilizing predictable Managed Service Provider Subscription Fees, you can eliminate the “emergency consulting” fees that occur when internal resources are overwhelmed by platform upgrades or complex integration failures. This approach positions your partner as a reliable long-term collaborator invested in your operational stability.

Forecasting for 2026 and Beyond

Strategic budget planning must account for ServiceNow’s biannual upgrade cycles, which require dedicated windows for testing and validation. The integration of Generative AI, specifically through “Now Assist,” into existing workflows necessitates a clear understanding of data throughput and compute requirements. As your ServiceNow footprint expands into multi-cloud governance, the complexity of managing cross-platform security and compliance will grow. Developing a three-year roadmap that anticipates these shifts ensures that your platform remains a driver of systemic improvement rather than a source of financial friction. To ensure your 2026 roadmap is optimized for both performance and cost, you should schedule a strategic implementation audit with our expert team.

Partnering for Predictability: The Test Triangle Approach

Achieving a successful deployment requires more than technical proficiency; it demands a disciplined methodology that prioritizes long-term financial predictability. At Test Triangle, we eliminate the anxiety associated with the hidden costs of servicenow implementation by integrating a strategic roadmapping phase that aligns platform capabilities with your specific business outcomes. Our “Testing-First” philosophy ensures that digital assurance isn’t a final hurdle but a continuous process, reducing the total cost of ownership by identifying architectural flaws before they escalate into expensive operational overhead. By balancing out-of-the-box functionality with essential, high-value customization, we protect your ability to scale without the burden of excessive technical debt.

The transition from a high-intensity implementation phase to a state of sustainable, managed growth is where many organizations struggle to maintain budget discipline. Our approach focuses on creating a seamless evolution, moving your enterprise from the initial “go-live” toward a model of continuous improvement and systemic progress. By anchoring our expertise in recognized global benchmarks, we provide the peace of mind that your complex digital infrastructure is managed with professional rigor. This methodology doesn’t just launch a platform; it establishes a foundation for stability, precision, and performance that lasts through every subsequent ServiceNow release cycle.

Comprehensive ServiceNow Consulting

To navigate the complexities of the 2026 release cycle, organizations need a partner that offers more than just technical execution. Our ServiceNow Consulting Services provide the strategic oversight necessary to ensure that every module deployment translates into tangible business value. We recognize that specialized talent is a major cost driver, which is why our IT Staffing Services are designed to fill critical niche gaps in your project team with certified experts who understand the nuances of the Now Platform. In a recent enterprise engagement, we successfully reduced implementation overruns by 25% by implementing an automated QA framework that caught integration errors in real-time, proving that rigorous validation is the ultimate cost-saving tool.

Ensuring Long-Term Operational Stability

We view our clients not as transactional accounts but as partners in a journey toward digital maturity. Transitioning from initial implementation to sustainable growth requires a reliable long-term collaborator who can provide the institutional maturity needed to operate across diverse, highly regulated industries. Our global delivery model ensures that your complex digital infrastructure receives 24/7 support, providing the empowerment found in large-scale technological evolution without the risk of downtime. This commitment to operational excellence allows your internal teams to focus on innovation while we handle the technical rigor of platform maintenance and governance. Consult with our ServiceNow experts to audit your implementation roadmap and secure your organization’s technological future.

Securing Your Digital Future through Strategic Platform Governance

Managing the total cost of ownership for a high-scale platform requires a shift from tactical software acquisition to a permanent architectural commitment. By identifying the hidden costs of servicenow implementation during the planning phase, your organization can avoid the structural debt and personnel gaps that frequently stall digital evolution. We’ve explored how a disciplined methodology rooted in quality assurance and proactive governance transforms potential financial traps into a predictable roadmap for systemic improvement. Achieving peak performance in 2026 depends on your ability to balance out-of-the-box efficiency with the essential customizations that drive unique business value.

As a seasoned expert in the global technological landscape, Test Triangle leverages its strategic partnerships with ServiceNow and AWS to provide the institutional maturity your enterprise requires. Our global presence across Europe, North America, and Asia, combined with specialized expertise in Software and Digital Assurance, ensures that your infrastructure remains resilient against the complexities of upcoming release cycles. We invite you to Download our ServiceNow TCO Framework or Book a Strategic Audit to align your platform capabilities with your long-term business goals. We’re ready to help you achieve lasting stability, scalability, and success.

Frequently Asked Questions

What is the average cost of a ServiceNow implementation in 2026?

Implementation costs typically range from three to five times the annual software licensing fees. For enterprise organizations, complex deployments often range from $100,000 to over $500,000. Professional services and implementation can account for approximately 75% of the total first year investment, with licensing making up the remaining 25%.

Why does ServiceNow customization increase long-term costs?

Excessive customization creates architectural debt that complicates the biannual upgrade cycle. When you deviate from out of the box functionality, you incur an “upgrade tax” because custom scripts must be manually remediated for every new release, such as the upcoming Australia update. This adds recurring maintenance overhead that restricts your ability to access new platform features quickly.

How much should we budget for ServiceNow training and change management?

Organizations should allocate between $50 and $150 per user specifically for role based training. This investment is crucial for preventing platform underutilization and the accumulation of licensed features that stay idle because the team lacks the expertise to govern them. Continuous learning ensures that your staff can manage the evolving AI capabilities found in the latest releases.

What are the most common “hidden” integration costs with ServiceNow?

Hidden costs often stem from data migration activities and transaction based fees within the IntegrationHub. It’s recommended to budget 20% to 30% of the total implementation cost purely for data migration to ensure a clean transition. Additionally, automated workflows and third party spokes can trigger consumption based charges that aren’t always apparent in the initial licensing quote.

Can I implement ServiceNow without a partner to save costs?

While an internal approach is possible, it often leads to higher hidden costs of servicenow implementation due to a lack of specialized platform expertise. Experienced partners reduce implementation timelines and prevent expensive post launch fixes. Furthermore, hiring dedicated internal ServiceNow architects is frequently 30% more expensive than standard IT staffing, making a partner model more cost effective for long term stability.

How do ServiceNow licensing updates in 2026 affect my budget?

The shift toward AI driven capabilities in the Zurich and Australia releases introduces credit based consumption models that require precise forecasting. ITSM Professional Edition with AI now costs $160 or more per user per month. Organizations must carefully classify users as fulfillers or requesters to avoid significant annual overages as their digital footprint expands.

What is the role of QA in reducing ServiceNow implementation costs?

Rigorous quality assurance acts as a financial safeguard by identifying technical hurdles before they reach the production environment. Catching a bug during the development phase is significantly cheaper than post launch remediation, which can cost five to ten times more in a live environment. A testing first philosophy ensures that the platform remains stable and performs as intended from day one.

Is ServiceNow ROI achievable within the first 12 months?

Yes, Forrester TEI studies have demonstrated a 264% ROI with a 6 month payback period for the Now Platform. Achieving this rapid return requires strategic alignment and a disciplined approach to the hidden costs of servicenow implementation. By managing architectural debt and focusing on out of the box functionality, organizations can secure their technological future while staying within budget.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.
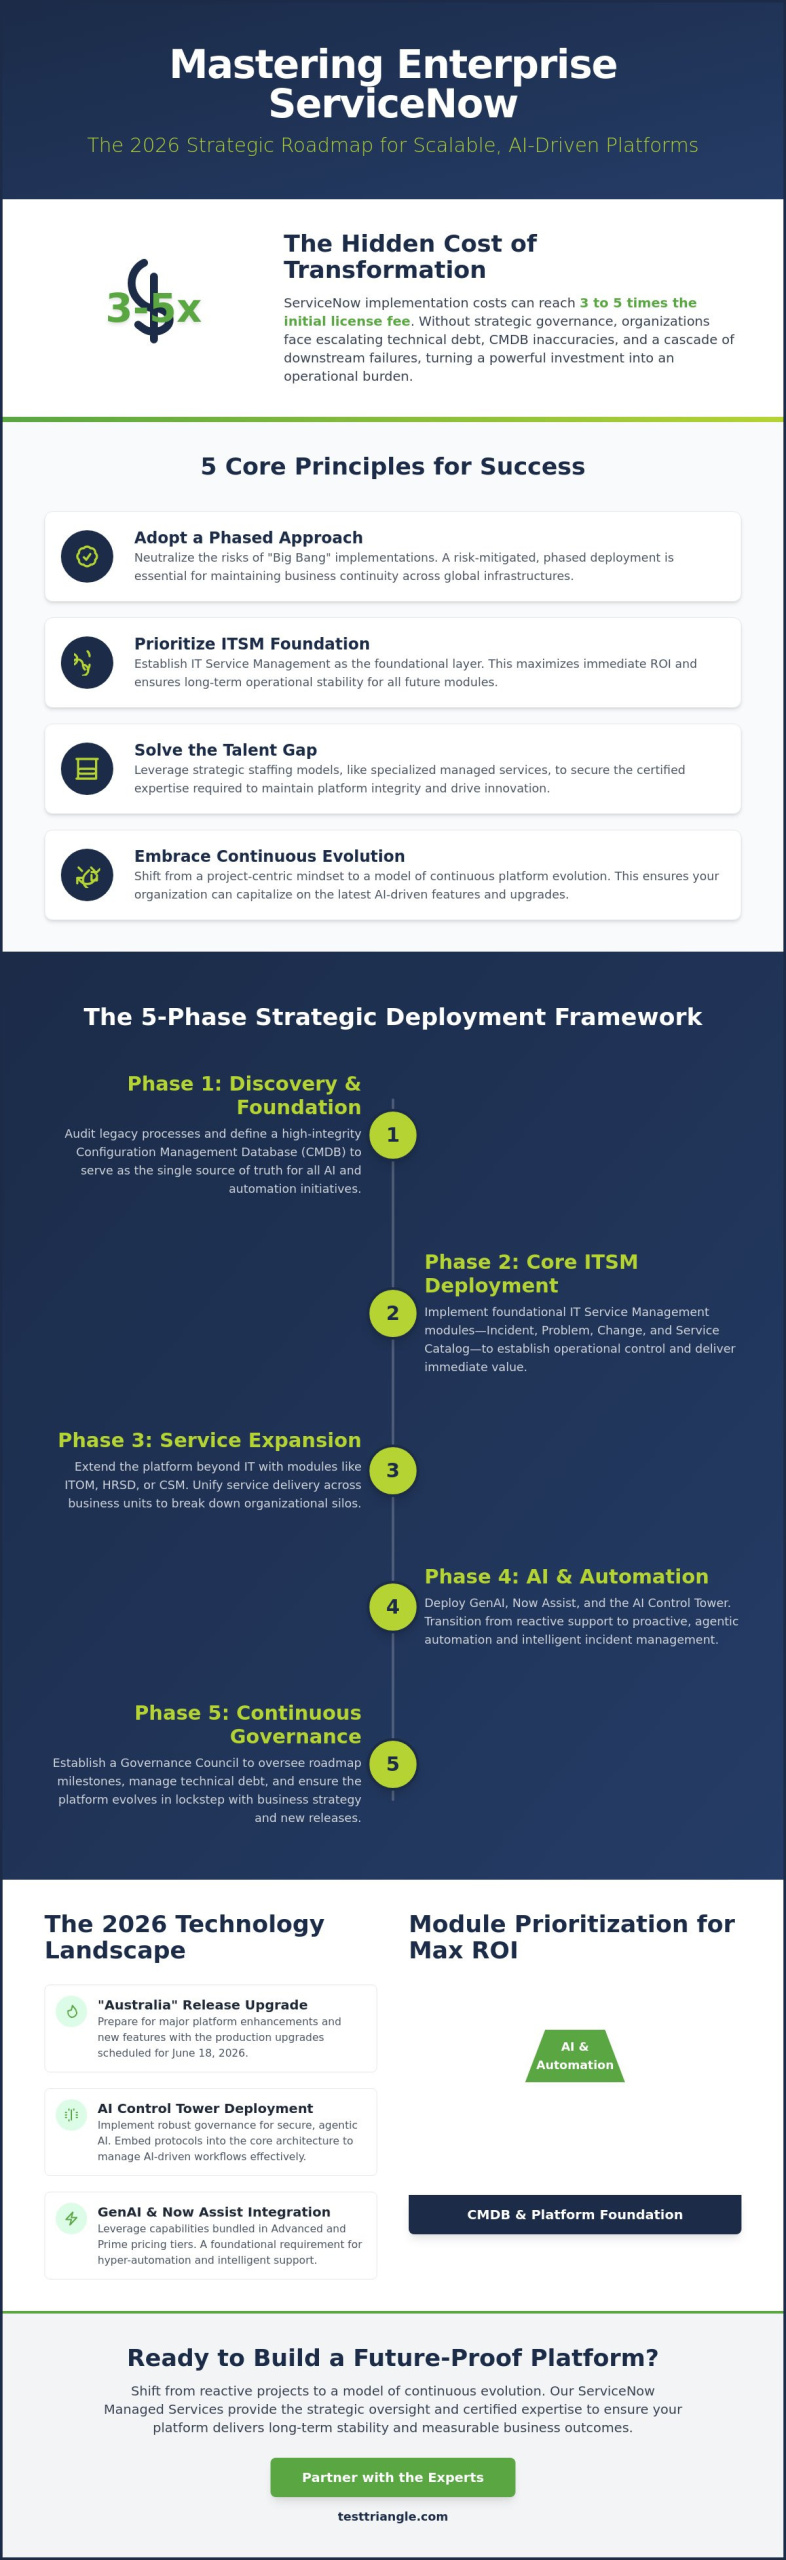

With ServiceNow implementation costs typically reaching three to five times the initial license fee, the strategic challenge for global organizations isn’t just the initial purchase; it’s the persistent governance of a rapidly evolving digital ecosystem. You’ve likely seen how unmanaged technical debt and CMDB inaccuracies can turn a transformative vision into a series of downstream failures. To solve this, sophisticated servicenow managed services for enterprises provide the technical rigor, strategic oversight, and specialized talent required to maintain platform integrity. We focus on delivering precision, performance, and progress through a methodology that connects architectural health to measurable business outcomes.

This guide offers a comprehensive 2026 roadmap designed to help you master the complexities of enterprise-scale deployments with a structured, risk-mitigated approach. You’ll learn how to align IT workflows with your broader corporate objectives while ensuring your platform remains scalable as you grow. We’ll preview the critical phases of the “Australia” release upgrade, the integration of the new Prime pricing tier capabilities, and the deployment of the AI Control Tower for secure, agentic automation. By the end of this article, you’ll have a clear path to achieve long-term operational stability and a platform that evolves alongside your enterprise.

Key Takeaways

  • Learn why a phased, risk-mitigated approach to deployment is essential for maintaining business continuity across global infrastructures, effectively neutralizing the risks associated with high-stakes “Big Bang” implementations.
  • Leverage specialized servicenow managed services for enterprises to navigate the 2026 strategic roadmap, ensuring that technical configurations remain precisely aligned with high-level corporate objectives and systemic growth.
  • Identify the optimal order of operations for module integration, prioritizing IT Service Management as the foundational layer to maximize immediate return on investment and long-term operational stability.
  • Solve the persistent talent gap by evaluating strategic staffing models that secure the certified expertise required to maintain platform integrity amidst a rapidly changing technological landscape.
  • Shift from a project-centric mindset to a model of continuous platform evolution, ensuring your organization is positioned to capitalize on the latest AI-driven features and version upgrades.

The Architecture of Success: Defining the ServiceNow Implementation Roadmap

The architecture of success in modern digital infrastructure isn’t built on static project plans; it’s forged through a living strategic document that synchronizes complex IT workflows with overarching corporate goals. For global organizations, the “Big Bang” deployment model often results in catastrophic operational friction, making a phased transition the superior choice for maintaining business continuity while scaling technical capabilities. Establishing a robust, multi-year roadmap serves as a definitive risk-mitigation tool for large-scale digital transformation. In 2026, the “Assess, Align, Accelerate” framework has become the industry benchmark, particularly as firms prepare for the “Australia” release production upgrades scheduled for June 18. By utilizing servicenow managed services for enterprises, leadership teams can ensure this framework isn’t just theoretical but translates into tangible platform stability, precision, and progress.

Strategic Alignment and Executive Buy-in

Successful platform adoption requires a shift from purely technical metrics to specific corporate KPIs. By mapping platform capabilities directly to business outcomes, such as reducing mean time to resolution or improving employee retention through seamless service delivery, IT leaders can secure sustained funding. We recommend establishing a Governance Council to oversee roadmap milestones, ensuring that every configuration choice supports the enterprise’s long-term vision. Identifying “Quick Wins” during the initial ninety days is essential to demonstrate immediate value to stakeholders, effectively justifying the implementation costs which typically range from three to five times the first-year license fee.

The 2026 Landscape: AI and Hyper-automation

Since its inception, ServiceNow has evolved from a ticketing tool into a comprehensive workflow engine that now prioritizes agentic AI. The 2026 roadmap must integrate GenAI and Now Assist into early phases, especially as these capabilities are now bundled within the Advanced and Prime pricing tiers. Preparing data structures for AI-driven incident management is no longer optional; it’s a foundational requirement for hyper-automation. Strategic servicenow managed services for enterprises focus on future-proofing the platform against evolving regulatory requirements, such as the June 2026 Chemical Regulatory framework, by ensuring that data governance and AI Control Tower protocols are embedded into the core architecture from day one. This proactive approach leads to a scalable, secure, and sophisticated digital environment that empowers the global workforce.

The 5-Phase Strategic Framework for Enterprise Deployment

Executing a global deployment requires more than just technical configuration; it demands a methodical progression that balances speed with architectural integrity. By adopting a five-phase framework, organizations can transform their digital infrastructure from a collection of siloed tools into a unified engine for growth. High-tier servicenow managed services for enterprises provide the necessary guardrails during this transition, ensuring that each phase builds upon a stable foundation rather than compounding technical debt. This disciplined approach allows leadership to maintain visibility while the platform scales across diverse business units.

Phase 1 focuses on Discovery and Foundation, where teams audit legacy processes to define the core Configuration Management Database (CMDB). This stage is critical because ServiceNow’s AI-driven strategy relies heavily on high-quality data to fuel automation and agentic AI. Phase 2 moves into Core ITSM Deployment, establishing incident, problem, and change management workflows that standardize service delivery. Once these essentials are in place, Phase 3 introduces IT Operations Management (ITOM) for full-stack observability. Phase 4 extends the platform’s reach into HR Service Delivery (HRSD) or Strategic Portfolio Management (SPM), aligning technical output with business value. Finally, Phase 5 centers on Continuous Optimization, where the platform is refined to meet shifting enterprise needs.

Phase 1: The Criticality of a Clean CMDB

The CMDB acts as the single source of truth for the entire roadmap. If the data within this database is fragmented or outdated, every downstream process, from automated ticket routing to AI-driven insights, will fail. Enterprises must decide between automated discovery tools and manual data entry, though automation is almost always preferred for maintaining accuracy at scale. Avoiding the “garbage in, garbage out” trap requires a disciplined approach to data governance that starts on day one. It’s the difference between a platform that provides clarity and one that creates confusion.

Scaling Through Managed Services

As the deployment matures, the focus shifts from initial setup to long-term operational health. Transitioning to professional Managed Service Provider (MSP) support through servicenow managed services for enterprises allows internal IT teams to focus on innovation while experts handle the complexities of platform maintenance. This model ensures stability through recurring optimization audits and dedicated helpdesk support that scales with your needs. To ensure your platform remains a high-performance asset, it’s vital to discuss your specific operational requirements with a strategic partner. This partnership provides the institutional maturity needed to manage the “Australia” release and future platform evolutions with precision.

Order of Operations: Prioritising Modules for Maximum ROI

Determining the precise sequence of module activation is a high-stakes decision that dictates the speed of realized value across the organization. While the platform’s versatility is vast, establishing IT Service Management (ITSM) as the foundational layer remains the strategic standard for 90% of enterprises. This preference isn’t merely traditional; it’s a structural necessity because ITSM provides the essential data taxonomies and service schemas required to support more advanced automation. By utilizing servicenow managed services for enterprises, leadership teams can navigate these priorities with a steady hand, ensuring that each new capability rests on a stable, high-performance base that supports systemic growth.

When comparing early ITOM (IT Operations Management) versus HRSD (HR Service Delivery) integration, the choice typically hinges on the organization’s most pressing operational friction. If the enterprise suffers from frequent service outages or lacks visibility into complex cloud infrastructures, ITOM offers the immediate benefit of full-stack observability. Conversely, if the primary goal is to centralize and automate employee requests across global offices, HRSD provides a more visible impact on internal productivity. A common objection arises regarding whether industry-specific modules should be implemented first to address niche requirements. While these modules offer deep functionality, deploying them before the core ITSM engine often creates architectural silos that are difficult to reconcile during later stages of the roadmap.

For organizations focused on technical agility, integrating ServiceNow with Atlassian ecosystems is a critical milestone for achieving DevOps synergy. This connection creates a seamless bridge between the service desk and the development pipeline, allowing for automated ticket synchronization and improved visibility. By aligning these industry-leading platforms, enterprises can achieve a level of speed, security, and scalability that traditional siloed approaches cannot match.

The ITSM-First Approach

Standardizing service desks through an ITSM-first strategy is the most effective way to reduce operational friction and create a unified user experience. By mapping incident management directly to business impact levels, IT teams can prioritize resources based on actual financial or operational risk. The minimum viable platform for a successful enterprise launch consists of a governed CMDB core, a functional incident management workflow, and a standardized service portal. This foundational setup allows the enterprise to capture clean data from day one, which is essential for fueling the AI-driven insights promised in the 2026 roadmap.

Expanding to ITOM and Beyond

Once the foundation is secure, leveraging AIOps within the ITOM module allows organizations to transition from reactive firefighting to proactive maintenance. This evolution is particularly powerful when integrating ServiceNow with AWS cloud environments, where automated discovery and event management can significantly reduce mean time to resolution. Linking your ServiceNow Implementation to broader DevOps Consulting goals ensures that your platform doesn’t just manage services but actively accelerates digital transformation. This strategic expansion transforms the platform into a versatile engine for enterprise-wide innovation and long-term stability.

ServiceNow Managed Services for Enterprises: The 2026 Strategic Roadmap

Overcoming the Talent Gap: Staffing Your Roadmap

The primary bottleneck for global organizations executing a 2026 roadmap isn’t the platform’s architecture; it’s the acute shortage of certified ServiceNow architects and developers. This talent gap often halts progress between the discovery and deployment phases, as enterprises struggle to secure specialists who understand the nuances of the “Australia” release and its bundled AI capabilities. The “Build vs. Buy” dilemma is a constant pressure for IT leadership. While training internal staff is a valuable long-term objective, the immediate requirements of a high-stakes rollout often demand the technical rigor and institutional maturity that only servicenow managed services for enterprises can provide. Specialized recruiters play a vital role here, sourcing hard-to-find talent that bridges the gap between technical execution and business strategy.

To maintain momentum without inflating permanent headcount, many organizations utilize IT Staffing Services to fill tactical gaps during the most labor-intensive milestones. This approach allows for a versatile staffing model that adjusts to the project’s pulse, ensuring that your roadmap doesn’t stall due to a lack of specialized human capital. If your organization is facing a critical expertise shortage, it is time to consult with our staffing experts to secure the certified talent necessary for a seamless deployment.

Hybrid Staffing Models for Global Rollouts

Balancing permanent on-site leadership with remote offshore resources is a proven strategy for maintaining 24/7 development cycles. Using contract specialists for high-intensity Phase 2 and 3 milestones allows enterprises to scale their technical capacity rapidly without the long-term burden of high overhead. This model frequently utilizes margin-based billing for temporary tech staff, providing a cost-effective way to access elite skills during critical transition periods. It’s a disciplined approach that prioritizes operational speed while maintaining strict budget control.

Quality Assurance and Testing Roles

Manual and Automation Testing are non-negotiable requirements for any enterprise roadmap. Integrating QA engineers early in the deployment process prevents the accumulation of technical debt that can cripple a platform’s performance over time. System Integration Testing (SIT) is particularly crucial in multi-platform environments where ServiceNow must communicate flawlessly with AWS, Atlassian, or legacy ERP systems. Following a structured testing guide ensures that every configuration is validated against rigorous security and performance standards before reaching production, safeguarding the integrity of your digital ecosystem.

The Final Milestone: Partnership and Long-Term Evolution

The final milestone in a successful enterprise deployment is the fundamental shift from a project-centric view to a platform-centric philosophy. While the initial go-live represents a significant achievement, the true value of servicenow managed services for enterprises is realized through continuous, incremental evolution. This “platform mindset” ensures that your digital infrastructure remains responsive to shifting market conditions rather than becoming a legacy burden. Precision drives progress. To maintain this momentum, regular version upgrades are essential. With the “Australia” release production upgrades scheduled for June 18, 2026, organizations must stay current to access critical innovations like the AI Control Tower or the bundled Now Assist capabilities now included in the Prime pricing tier. Neglecting these updates doesn’t just stall innovation; it increases security risks and technical debt.

As a seasoned expert in the field, Test Triangle acts as a steady hand in this fast-changing landscape, positioning itself as the strategic collaborator for your IT Service Management solutions. We focus on the peace of mind derived from risk reduction and the empowerment found in large-scale technological evolution. Stability requires constant motion. Transitioning to a managed model allows your internal leadership to focus on high-level strategy while we manage the technical rigor of platform health, ensuring your investment continues to deliver measurable ROI long after the initial implementation.

Measuring Roadmap Maturity

Determining the success of your deployment requires tracking key performance indicators (KPIs) that reflect real business impact. We recommend focusing on metrics such as the reduction in mean time to resolution (MTTR), the accuracy of CMDB data, and overall user adoption rates across different modules. Annual “Health Checks” are a non-negotiable part of this process. These audits identify system bloat and misconfigurations before they cause downstream failures. By leveraging the strategic trinity of Atlassian, ServiceNow, and AWS, organizations can achieve a level of enterprise-wide agility that ensures every workflow is optimized for speed and security.

Ready to Accelerate Your Transformation?

Our “Assess, Align, Accelerate” value proposition is designed to lead your organization from a general need for improvement to a specific, high-performance technical solution. This methodical approach ensures that your ServiceNow environment remains a scalable asset that grows alongside your enterprise. We invite you to explore Test Triangle’s comprehensive IT services to see how our versatile staffing and implementation models can support your long-term goals. Reviewing your strategic roadmap with a consultant today is the best way to ensure your digital infrastructure is prepared for the complexities of the 2026 landscape. Your roadmap is the bridge between technology and business outcome.

Mastering the Evolution of Enterprise Workflows

Achieving operational excellence at scale requires a transition from reactive maintenance to a disciplined, phased strategy that prioritizes architectural health and specialized expertise. By following a structured roadmap, organizations can ensure their digital infrastructure remains resilient while capitalizing on agentic AI and automated governance. Utilizing servicenow managed services for enterprises provides the institutional maturity needed to navigate complex version upgrades and talent shortages with confidence. We focus on delivering precision, performance, and progress through a methodology that transforms technical debt into a scalable engine for growth.

As a ServiceNow Authorized Partner with a global presence across Europe, North America, and Asia, Test Triangle is uniquely positioned to support high-compliance sectors like Finance and Pharma. We act as a reliable long-term collaborator, ensuring your platform aligns with both technical benchmarks and overarching business goals. It’s time to secure your digital future and eliminate the friction of unmanaged systems. Book a Strategic ServiceNow Roadmap Consultation with Test Triangle to refine your deployment strategy. Your journey toward a more efficient and empowered enterprise begins with a single, strategic step.

Frequently Asked Questions

What is the typical timeline for a ServiceNow enterprise implementation?

A standard enterprise-scale deployment typically spans six to twelve months, though the exact duration depends on the complexity of legacy integrations and the scope of the initial modules. While smaller organizations might achieve a go-live in a shorter window, global firms require a more methodical pace to ensure data integrity and user adoption across multiple business units. This timeline includes the critical discovery phase and the subsequent iterative testing cycles necessary for a risk-mitigated launch.

Should we start with ITSM or ITOM in our roadmap?

Enterprises should almost always prioritize IT Service Management (ITSM) as the foundational layer of their roadmap. Because ITSM establishes the core service taxonomies and incident workflows, it provides the essential data structure required for IT Operations Management (ITOM) to function effectively. Starting with ITSM allows teams to standardize the user experience before introducing the advanced observability and AIOps capabilities offered by ITOM.

How much does a ServiceNow implementation usually cost for a global firm?

Total investment for a global firm is determined by a combination of licensing tiers, implementation complexity, and ongoing support requirements. Since ServiceNow operates on a custom-quote basis, organizations must account for the fulfiller base size and the number of integrated business units when budgeting. Utilizing servicenow managed services for enterprises helps manage these costs by providing a predictable expenditure model for long-term maintenance and platform evolution.

What are the most common reasons for ServiceNow roadmap failure?

Roadmap failures most frequently stem from poor governance, inadequate data quality in the CMDB, and a lack of specialized technical talent. When organizations treat the platform as a one-time project rather than a living ecosystem, they often accumulate technical debt that hinders future upgrades. Success requires a disciplined approach that aligns technical configuration with high-level business objectives while maintaining a steady hand through continuous platform evolution.

How do we handle data migration from legacy systems to ServiceNow?

Handling data migration requires a rigorous “clean as you go” strategy to avoid transferring legacy inaccuracies into the new environment. Teams should utilize automated discovery tools to validate existing assets while manually auditing critical service relationships to ensure the CMDB remains a single source of truth. This process often involves a phased migration where data is mapped, transformed, and validated in a staging environment before the final production cutover.

What is the role of a ServiceNow Implementation Specialist versus a Generalist?

A ServiceNow Implementation Specialist possesses deep, certified expertise in specific modules like HRSD or ITOM, ensuring that complex configurations follow industry best practices. In contrast, a Generalist provides broader oversight of the platform’s daily operations and basic maintenance tasks. For global organizations, the strategic visionary role of a Specialist is essential during the high-intensity deployment phases to prevent architectural silos and ensure long-term scalability.

Can ServiceNow be integrated with Atlassian Jira for DevOps?

Integrating ServiceNow with Atlassian Jira is a standard practice for organizations seeking to achieve seamless ticket synchronization between service desks and development teams. This connection allows developers to remain within their preferred environment while IT managers maintain visibility and governance within the ServiceNow platform. By aligning these industry-leading tools, enterprises can accelerate delivery cycles while maintaining strict compliance and security standards.

How often should we update our ServiceNow roadmap?

Roadmaps should be reviewed and updated at least quarterly to account for platform release cycles and shifting business priorities. This methodical rhythm allows leadership to adjust the order of operations based on realized ROI and emerging operational needs. Regular updates ensure that your organization is prepared to leverage the latest innovations and bundled AI capabilities, keeping the platform aligned with your broader digital transformation goals.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.

With 81% of organizations admitting they shipped code with known vulnerabilities into production last year, the margin for error in software delivery has effectively vanished. You’ve likely felt the mounting tension between the demand for rapid release cycles and the critical need to protect an infrastructure where global breach costs now average $4.44 million. Adopting sophisticated ci/cd pipeline security best practices is the only way to resolve this conflict, transforming your delivery chain from a potential liability into a resilient, strategic asset. This guide promises to equip you with a comprehensive framework to master modern delivery complexities, ensuring your organization stays ahead of the sophisticated threats emerging in 2026.

We’ll provide a methodical checklist that bridges the gap between high-level security policy and practical, automated execution. By examining the latest NIST DevSecOps practices and OWASP standards, we’ll show you how to eliminate secrets exposure and verify supply chain integrity without sacrificing momentum. You’ll discover how a disciplined approach to pipeline hardening results in both reduced risk and enhanced operational stability, positioning your enterprise as a leader in secure digital transformation.

Key Takeaways

  • Analyze the evolution of the 2026 threat landscape to transition from reactive patching toward a sophisticated, “Security-by-Design” architecture that protects against complex supply chain poisoning.
  • Establish a resilient foundation for your delivery infrastructure by centralizing identity management and implementing ci/cd pipeline security best practices that eliminate high-risk orphaned credentials.
  • Ensure continuous compliance and artifact integrity by integrating automated Software Bill of Materials (SBOM) generation and real-time dependency scanning into your existing workflows.
  • Execute a comprehensive hardening strategy using a tactical checklist that prioritizes mandatory peer reviews, signed commits, and the seamless integration of SAST and DAST tools.
  • Align your technical delivery with long-term business objectives by leveraging expert DevOps consulting to architect a secure, scalable framework that meets global security benchmarks.

Securing the Software Supply Chain: The 2026 CI/CD Threat Landscape

The digital perimeter has effectively dissolved, placing the software delivery engine at the center of the enterprise risk profile. In 2026, the sophistication of adversaries has reached a critical juncture where the integrity of the delivery process is as vital as the code itself. The evolution from simple code injection to complex supply chain poisoning reflects a maturation of cyber-adversaries who now target the build server and orchestration layers rather than just the application. Implementing robust ci/cd pipeline security best practices is no longer a tactical option but a strategic imperative for any organization aiming to maintain operational stability and customer trust.

Adopting a “Security-by-Design” approach is essential to counter these threats, moving beyond the era of reactive patching which often leaves systems exposed for critical windows. A 2025 survey revealed that 81% of organizations admitted to shipping code with known vulnerabilities, a statistic that underscores the failure of traditional perimeter-based defenses. By integrating security protocols directly into the continuous integration (CI) and continuous delivery (CD) workflow, enterprises can validate every artifact before it reaches production, thereby neutralizing threats at the source. This proactive posture is particularly vital as AI-generated code increases the volume and velocity of vulnerabilities, requiring automated, intelligent oversight to maintain a secure posture.

Identifying Vulnerabilities in Modern Pipelines

Modern delivery environments are often compromised by third-party plugins and automated integrations that lack rigorous security vetting. These tools, while enhancing productivity, frequently introduce unmanaged risks that bypass traditional firewalls. The rise of “Shadow DevOps”—where teams spin up unmanaged pipeline environments outside of official corporate governance—creates significant blind spots that attackers are eager to exploit. In 2026, a Supply Chain Attack is defined as a strategic compromise of third-party components or delivery infrastructure designed to inject malicious payloads into trusted downstream environments. Data from 2025 indicates that 1.6% of organizations using npm have already encountered at least one malicious dependency, proving that trust must be verified, not assumed.

The Shift from DevOps to DevSecOps

Transitioning from DevOps to DevSecOps requires a fundamental cultural and technical shift that prioritizes security, stability, and scalability. This evolution moves security from a final checkpoint to a continuous thread woven through the entire development lifecycle. Security automation is the primary driver of this change, as it reduces the friction between developers and security teams by providing real-time feedback within existing workflows. When security is automated, it becomes a facilitator of speed rather than a bottleneck. A unified, security-first delivery culture empowers teams to own the security of their code, ensuring that every release is backed by a strategic framework of automated controls and expert human oversight. This alignment provides the peace of mind necessary for large-scale technological evolution in a volatile threat environment.

Hardening the Pipeline: Identity and Secrets Management

Centralizing identity and access management (IAM) within the orchestration layer serves as the most effective method for eliminating orphaned credentials that frequently persist after organizational shifts. By integrating these identities with enterprise-wide directories, security teams maintain a single source of truth, ensuring that access is revoked instantly across all environments. Role-Based Access Control (RBAC) complements this by defining precise boundaries for what each user or service account can execute, which prevents unauthorized modifications to pipeline configurations. These ci/cd pipeline security best practices focus on reducing the blast radius of any potential compromise by ensuring that no single identity possesses excessive reach.

For high-risk deployment stages, strategic implementation of Just-in-Time (JIT) access provides a sophisticated layer of protection by granting elevated permissions only for the duration of a specific task. This approach, combined with the use of enterprise-grade secrets vaults rather than insecure environment variables, ensures that sensitive data like API keys and certificates are encrypted at rest and in transit. Unlike static environment variables, modern vaults offer dynamic secret generation and comprehensive audit logs, providing the transparency required for rigorous regulatory compliance. Organizations looking to integrate these rigorous controls into their existing workflows often find that consulting with strategic experts is the most efficient path to long-term operational stability.

Implementing Zero Trust and Least Privilege

A zero-trust architecture dictates that every service, runner, and user must be verified before interacting with the delivery pipeline. This methodology aligns with the NSA and CISA CI/CD Security Guidelines, which advocate for the continuous rotation of access keys and the strict limitation of runner permissions. By auditing these interactions in real-time, organizations can identify anomalous behavior before it escalates into a breach. Reducing the attack surface requires a disciplined commitment to the principle of least privilege, ensuring that pipeline runners only access the specific resources necessary for their immediate build tasks.

Eliminating Hardcoded Secrets and Credential Leaks

Despite the availability of advanced tools, credential leaks remain a primary vulnerability, with 2025 data showing that 32% of all scanner-detected repository secrets were tied directly to CI/CD systems. Implementing automated pre-commit hooks is a vital first step, as it prevents sensitive data from ever entering the version control system. Continuous scanning must extend beyond the code itself to include build logs and artifact metadata, where secrets often hide in plain sight. In 2026, a single leaked API key isn’t just a technical oversight; it’s a multi-million dollar invitation for automated adversaries to dismantle your entire digital infrastructure in seconds.

Integrity Assurance: Validating Code and Dependencies

Maintaining the absolute integrity of software components has become a primary challenge for the modern enterprise, particularly as the complexity of the dependency graph continues to expand. In an environment where 1.6% of organizations using npm have encountered at least one malicious dependency, verifying the provenance of every library is a non-negotiable pillar of ci/cd pipeline security best practices. Establishing a “Trusted Registry” for all container images and build artifacts ensures that only vetted, internal resources are utilized during the orchestration process, effectively neutralizing the risk of public repository poisoning. This strategic isolation allows organizations to solidify, secure, and scale their delivery pipelines with the confidence that their foundational components remain untainted by external adversaries.

Automating Software Composition Analysis (SCA) to identify known vulnerabilities (CVEs) in real-time provides a critical layer of defense that operates at the speed of modern development. By integrating these scans directly into the build cycle, teams can detect and remediate security flaws before they are baked into the final artifact. This proactive validation is further reinforced by implementing cryptographic code signing, which ensures artifact integrity from the moment of creation to the point of deployment. By enforcing signature verification at the production gate, enterprises can guarantee that the code running in their environments is exactly what was approved during the build phase, providing total transparency and operational stability.

Software Bill of Materials (SBOM) and Third-Party Risk

In 2026, the Software Bill of Materials (SBOM) has evolved from a static compliance requirement into a dynamic, real-time inventory that is essential for proactive risk management. Generating a comprehensive SBOM for every build cycle allows security teams to maintain a transparent view of all direct and transitive dependencies. This level of visibility is a cornerstone of Software and Digital Assurance Testing, ensuring that third-party risks are identified and mitigated with surgical precision. Linking SBOM analysis with global vulnerability databases enables a rapid response to emerging threats, transforming a complex supply chain into a manageable, secure asset.

Code Signing and Immutable Build Artifacts

Digital signatures serve as the definitive mechanism for verifying the origin and state of code, acting as a cryptographic seal that prevents unauthorized tampering. The use of immutable build artifacts is essential in this framework; once an artifact is signed and stored, it must never be modified, ensuring that what was tested is exactly what is deployed. Organizations should reference the OWASP CI/CD Security Cheat Sheet to refine their signature verification protocols and ensure that no unsigned or unverified code can bypass the final deployment gate. This disciplined approach to artifact management provides the precision, protection, and peace of mind required to navigate the volatile 2026 threat landscape.

The Enterprise CI/CD Security Best Practices Checklist

Transitioning from theoretical frameworks to operational excellence requires a disciplined application of technical controls across every stage of the delivery lifecycle. To achieve a resilient posture, organizations must move beyond generic security advice and implement a granular, multi-layered defense strategy. This checklist serves as a strategic roadmap for hardening your infrastructure, ensuring that ci/cd pipeline security best practices are embedded into the very fabric of your organizational workflows. By prioritizing these controls, enterprises can achieve a state of continuous compliance while maintaining the high-velocity delivery required by modern market demands.

A comprehensive security posture begins with these foundational pillars:

  • Secure Source Control: Enforce strict branch protection rules that mandate peer reviews for all changes and require cryptographically signed commits to verify author identity.
  • Automated Security Scanning: Integrate Static Application Security Testing (SAST), Dynamic Application Security Testing (DAST), and Software Composition Analysis (SCA) into every pipeline execution to identify vulnerabilities in real-time.
  • Environment Isolation: Utilize ephemeral build runners that are destroyed after each task and operate within isolated network segments to prevent lateral movement by adversaries.
  • Deployment Gates: Establish automated approval workflows that block deployments if security scan results exceed predefined risk thresholds.
  • Audit and Logging: Maintain immutable, centralized logs of all pipeline activities to provide a definitive trail for forensic analysis and regulatory reporting.

Pre-Build and Source Control Hardening

Securing the entry point of your pipeline is critical for preventing the injection of malicious code or unauthorized configuration changes. Mandating Multi-Factor Authentication (MFA) for all repository access is a baseline requirement that significantly reduces the risk of credential-based attacks. Enterprises must also restrict the use of unverified third-party GitHub Actions or GitLab runners, as these external components often bypass internal security vetting. Configuring real-time webhooks for alerting on suspicious configuration changes allows your security team to detect, defend, and decouple potential threats before they propagate through the build cycle.

Build and Test Stage Security Controls

Maintaining developer velocity while enforcing rigorous security standards requires a sophisticated approach to test execution. Running security scans in parallel with traditional functional tests ensures that identifying vulnerabilities doesn’t become a bottleneck for release cycles. Organizations should implement strict ‘fail-build’ thresholds for critical and high-severity issues, ensuring that no known high-risk code reaches production. Leveraging Software Test Automation Services allows for the seamless integration of these security checks into a broader quality assurance framework. For organizations ready to architect a more resilient delivery engine, speaking with a strategic consultant can provide the clarity needed to navigate these technical complexities.

CI/CD Pipeline Security Best Practices: The 2026 Strategic Enterprise Checklist

Strategic Implementation: Scaling Security with Expert Consulting

Scaling security across a fragmented enterprise infrastructure requires a departure from siloed tool implementation toward a unified, strategic technology roadmap. For global organizations, the challenge isn’t just identifying vulnerabilities but maintaining a consistent security posture across thousands of concurrent pipelines. Engaging in high-level DevOps Consulting allows enterprises to architect secure delivery pipelines that are resilient by design and compliant by default. This strategic oversight ensures that ci/cd pipeline security best practices are not merely local optimizations but are standardized across the entire digital estate, providing the institutional maturity necessary for long-term stability.

Managed services play a pivotal role in this evolution by providing continuous monitoring and governance that internal teams may struggle to maintain amidst rapid scaling. Bridging the persistent DevSecOps talent gap is another critical hurdle; for instance, Square Skills provides accredited IT training to help internal teams stay current, while specialized IT staffing services provide the human expertise required to implement complex security controls without slowing down the development engine. By combining expert consulting with dedicated technical talent, organizations can transform their delivery systems into secure, scalable, and sophisticated assets. This holistic approach ensures that your technological evolution is backed by both a practical framework and the specialized skills needed for execution.

Atlassian and ServiceNow Integration for Security Governance

True governance is achieved when security incidents are tracked and remediated with the same rigor as production bugs. Leveraging industry-standard platforms like Jira and ServiceNow for automated incident tracking ensures that every vulnerability identified in the pipeline is assigned, audited, and resolved within established SLAs. Optimizing these environments through expert Atlassian Implementation allows teams to create a unified dashboard for security compliance. This integration provides executive leadership with real-time visibility into the organization’s risk profile, bridging the gap between technical execution and business outcomes. When security data is centralized, it becomes a powerful tool for informed decision-making and operational efficiency.

Custom Security Roadmapping for Global Enterprises

Standardized security controls often fail to account for the unique regulatory pressures of industries such as finance or pharmaceuticals. A tailored security roadmap addresses these specific requirements by aligning technical delivery with global benchmarks and industry-specific mandates. Establishing a long-term strategic partnership ensures that your security posture evolves alongside the threat landscape, moving from basic hardening to advanced, predictive defense. Test Triangle serves as a steady, strategic, and secure partner, empowering enterprises to navigate the complexities of digital transformation with absolute confidence. This collaborative approach provides the peace of mind that comes from knowing your infrastructure is managed by a reliable long-term collaborator dedicated to your operational success.

Architecting Resilience in the 2026 Delivery Landscape

Mastering the complexities of modern software delivery requires a shift from fragmented toolsets to a unified, strategic framework of automated controls and expert oversight. By prioritizing the ci/cd pipeline security best practices outlined in this guide, including the rigorous validation of SBOMs and the centralization of identity management, your organization can effectively neutralize emerging supply chain threats. These technical measures provide the essential foundation for maintaining operational stability while accelerating the pace of digital innovation. Achieving this level of maturity demands a partner with a global presence and deep expertise in navigating highly regulated industries.

As an Atlassian Platinum Partner with a proven track record in complex digital transformations, Test Triangle acts as a reliable long-term collaborator for enterprises seeking to harden their infrastructure. Our approach ensures that security assurance is woven into every stage of the development lifecycle, providing the peace of mind necessary for large-scale technological evolution. We invite you to Secure Your Pipeline with Strategic DevOps Consulting and begin your journey toward a more stable, precise, and scalable future. Your organization’s progress is our primary objective, and we’re ready to help you build a delivery engine that is truly steady, strategic, and secure.

Frequently Asked Questions

What is the most critical stage to secure in a CI/CD pipeline?

The source control repository is the most critical stage to secure because it acts as the primary root of trust for the entire delivery ecosystem. If an adversary compromises the entry point through unauthorized code injection or credential theft, every subsequent stage of the pipeline becomes a vehicle for malicious propagation. Ensuring robust branch protections and mandatory peer reviews at this stage prevents vulnerabilities from entering the build cycle, which fundamentally protects the integrity of the downstream environment.

How can I integrate security without slowing down my deployment frequency?

Integrating security without sacrificing velocity requires the strategic parallelization of automated scanning tools within the orchestration layer. By running SAST and SCA scans alongside functional tests, teams identify critical flaws in real-time without blocking the main delivery path. This approach ensures that ci/cd pipeline security best practices become a facilitator of speed, as catching vulnerabilities early reduces the time-consuming remediation cycles typically required just before a production release.

Is it better to use open-source or commercial security scanning tools?

Enterprise environments generally benefit more from commercial security tools due to their advanced integration capabilities, comprehensive support, and alignment with global compliance standards. While open-source tools provide valuable baseline scanning, commercial platforms offer the sophisticated reporting and centralized governance required by large-scale organizations. Selecting a toolset that bridges the gap between technical execution and executive visibility ensures that security remains a manageable, strategic asset rather than a fragmented collection of scripts.

How does Zero Trust apply specifically to CI/CD workflows?

Zero Trust in CI/CD workflows dictates that every user, build runner, and service account must be explicitly verified before accessing pipeline resources. This methodology eliminates the concept of an “internal” trusted network, requiring continuous authentication and the strict application of the principle of least privilege. By ensuring that runners are ephemeral and have no persistent access to production environments, organizations significantly reduce the potential blast radius of a compromised identity or tool.

What are the most common mistakes in CI/CD secrets management?

The most frequent failures in secrets management include hardcoding credentials in version control and using static environment variables for sensitive data. Many organizations also struggle with long-lived API keys that lack automated rotation, creating a persistent attack surface for adversaries. Transitioning to dynamic secrets generated by enterprise-grade vaults ensures that credentials are short-lived and encrypted, providing the technical rigor necessary to prevent catastrophic data breaches in volatile environments.

How often should pipeline security configurations be audited?

Pipeline security configurations should be monitored in real-time through automated webhooks and audited formally at least once per quarter. Continuous monitoring allows security teams to detect and remediate drift in configuration settings before they can be exploited. These periodic deep dives ensure that your ci/cd pipeline security best practices remain aligned with evolving industry standards and internal compliance requirements, providing the institutional maturity needed for long-term operational stability.

Can automated security testing completely replace manual security reviews?

Automated security testing cannot completely replace manual reviews; instead, the two should function as complementary components of a comprehensive assurance strategy. Automation excels at identifying known vulnerabilities and pattern-based flaws at high velocity, while manual reviews are essential for uncovering complex logic errors and architectural weaknesses. A balanced approach leverages human expertise to interpret automated results, ensuring that the most critical risks are addressed with strategic precision and technical depth.

What role does an SBOM play in pipeline security?

A Software Bill of Materials (SBOM) acts as a definitive, transparent inventory of every component and dependency within a build artifact. In the context of 2026 security standards, the SBOM is vital for identifying transitive risks and ensuring compliance with third-party licensing requirements. By integrating dynamic SBOM generation into each build cycle, enterprises maintain the visibility required to respond instantly when new vulnerabilities are discovered in common libraries or upstream packages.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.
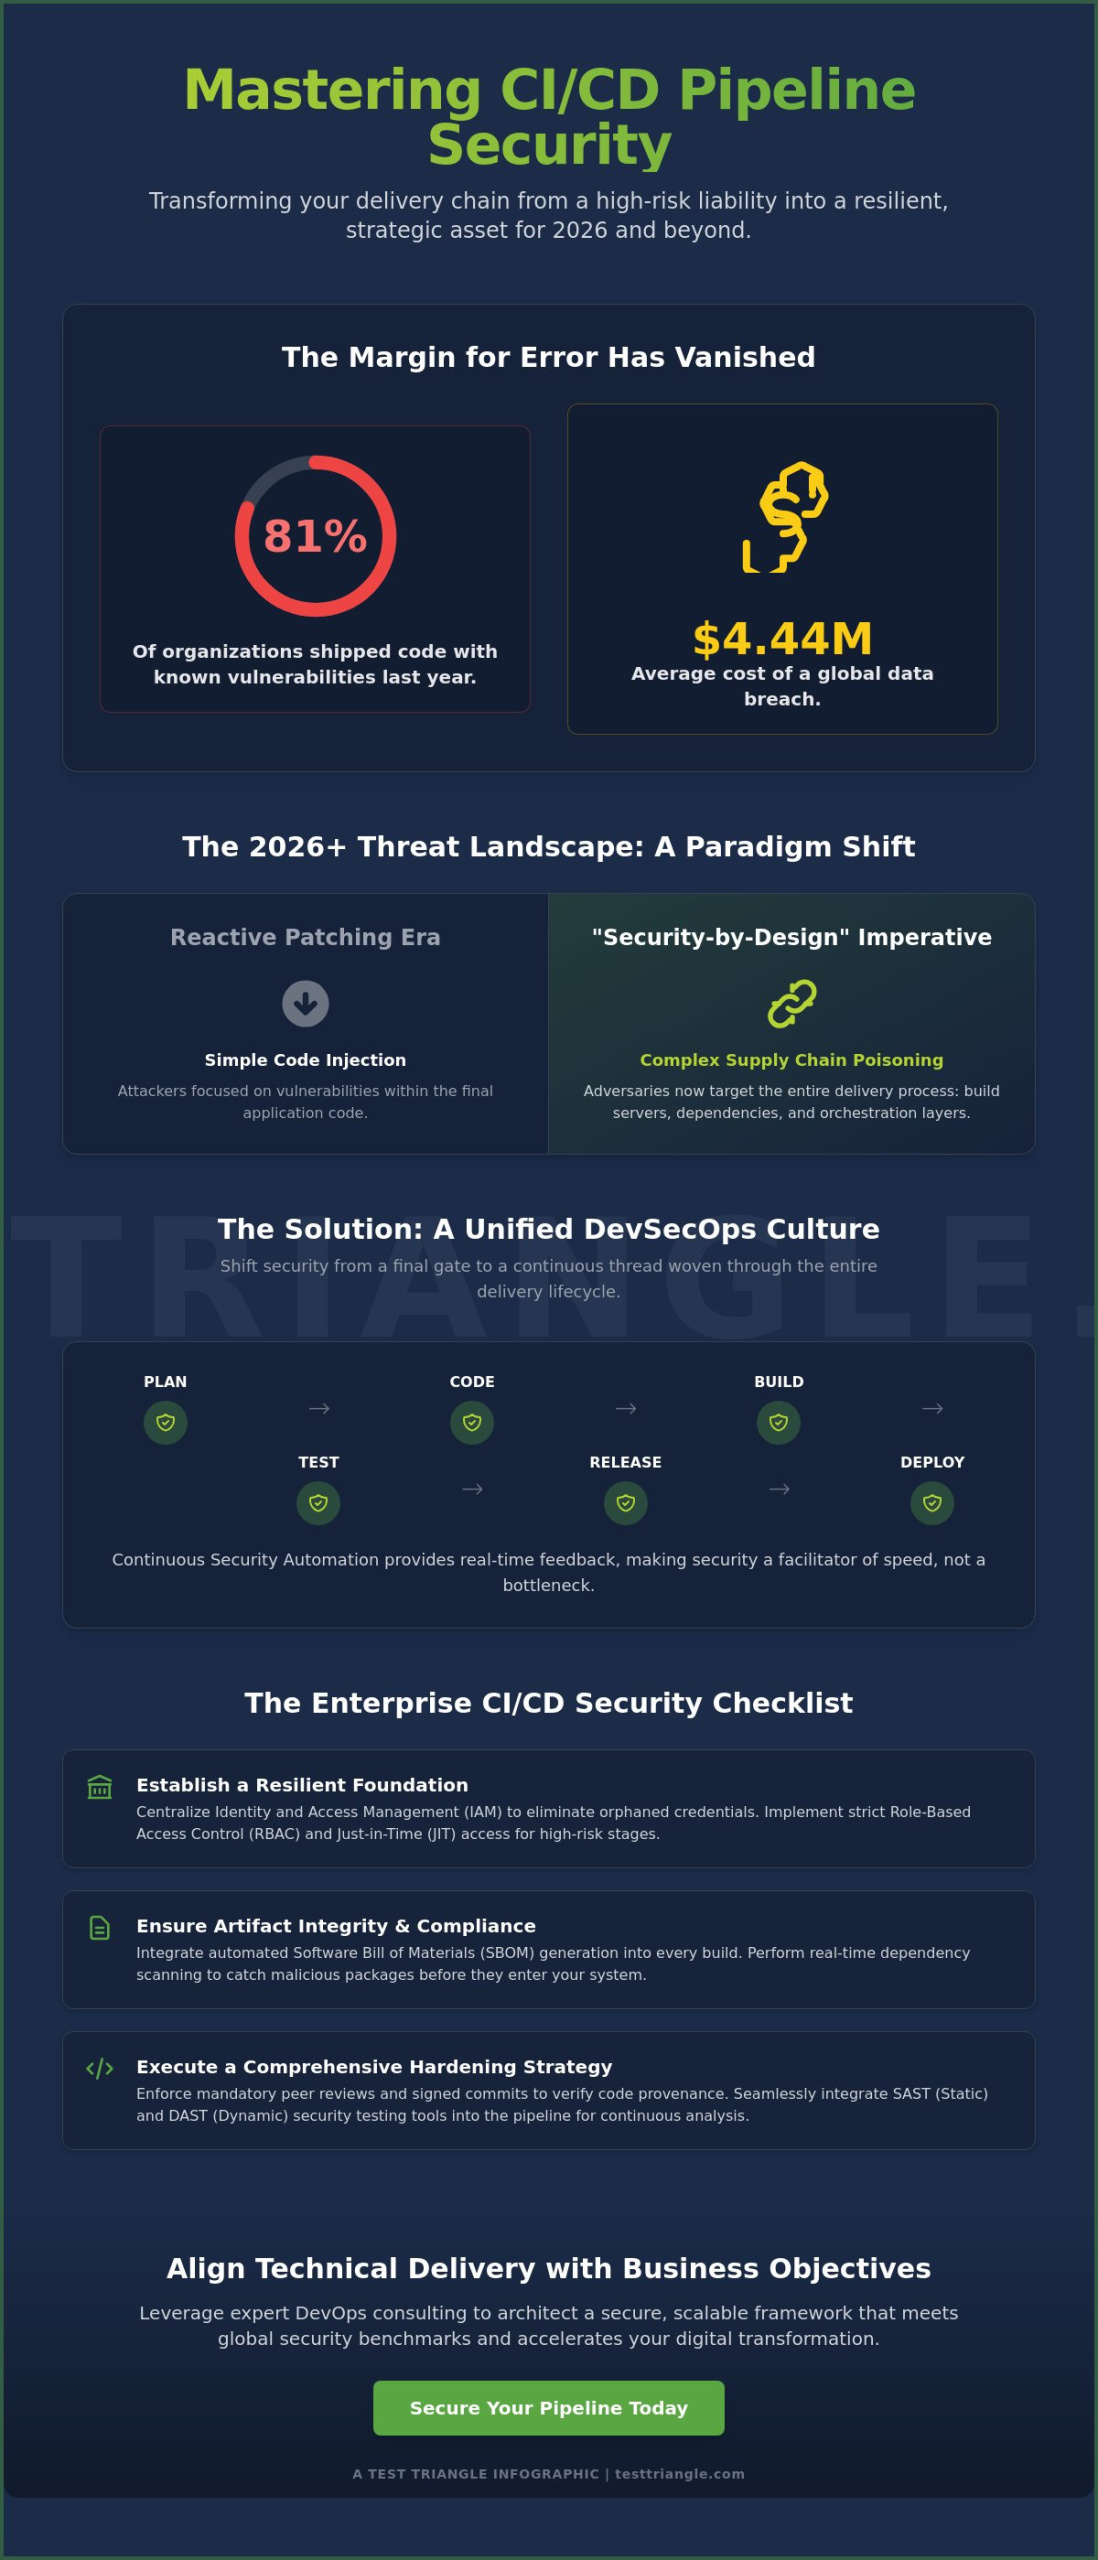

A media company serving 50TB of content monthly currently pays approximately $4,500 every month in AWS egress fees alone, illustrating how data gravity often evolves into a significant barrier to organizational agility. While the European Data Act has successfully pressured providers to waive certain exit fees for migrating customers, the true challenge of avoiding vendor lock-in with aws remains embedded in a complex web of proprietary APIs and specialized networking charges. You likely recognize the persistent tension between leveraging high level cloud innovation and the strategic necessity of maintaining long term digital sovereignty. It’s a delicate balance where the immediate speed of deployment must never compromise your future ability to pivot, migrate, or negotiate from a position of strength.

This guide provides a comprehensive roadmap for achieving enterprise autonomy through strategic agnosticism and robust architectural abstractions. You’ll master the frameworks required to evaluate service risks, optimize cross region data transfers, and implement automated testing that validates your portability at every stage. By aligning your technical execution with business outcomes, we’ll explore how to build a cloud smart infrastructure that delivers precision, portability, and progress. Our objective is to ensure your organization remains a steady hand in a fast changing landscape, empowered by a clear strategy for long term operational stability and the peace of mind that comes from true technological independence.

Key Takeaways

  • Assess the multidimensional risks of cloud dependency by identifying the technical, financial, operational, and mental pillars that define your organization’s current migration readiness.
  • Master the architectural abstractions required for avoiding vendor lock-in with aws, utilizing containerized runtimes and the adapter pattern to effectively decouple core application logic from proprietary service dependencies.
  • Transition from theoretical exit plans to validated operational reality by implementing contract testing suites that ensure consistent microservice behavior across heterogeneous cloud environments.
  • Strengthen your strategic leverage through a Cloud Center of Excellence that integrates Atlassian-driven governance into standard ITSM cycles for continuous, collaborative, and compliant portability oversight.
  • Apply the Test Triangle framework to synthesize DevOps discipline with digital assurance, ensuring your enterprise infrastructure remains versatile, scalable, and inherently exit-ready.

Understanding the Dimensions of AWS Vendor Lock-in in 2026

The 2026 cloud environment demands a sophisticated grasp of Understanding Vendor Lock-in, which manifests across four distinct pillars: technical, financial, operational, and mental. Technical lock-in occurs through the adoption of proprietary service architectures, while financial lock-in is reinforced by complex discount structures. Operational lock-in stems from rigid internal processes tailored to a specific provider. Mental lock-in represents the most subtle barrier, reflecting an organizational bias that treats one provider’s ecosystem as the only viable path for innovation. Successfully avoiding vendor lock-in with aws requires addressing these dimensions simultaneously to maintain true strategic autonomy and operational stability.

Data gravity has emerged as the most significant migration hurdle in 2026. As enterprises accumulate petabytes of information, the sheer mass of data creates a pulling force that makes moving workloads prohibitively expensive. Egress fees remain a primary weapon for restricting movement; for instance, a SaaS API handling 10TB of monthly response payloads can face roughly $900 in egress costs. This creates a friction-filled environment where the cost of data extraction often outweighs the benefits of platform diversification. Organizations must weigh the “Innovation Premium” of using native, high-level services against the “Portability Tax” incurred when building cloud-agnostic layers that require additional management overhead.

Technical vs. Economic Lock-in

Proprietary APIs create a sticky architecture by embedding cloud-specific logic directly into your application code, necessitating expensive and time-consuming rewrites during any migration attempt. This technical debt is often compounded by economic commitments such as Reserved Instances and Savings Plans, which provide immediate cost relief but significantly reduce your future bargaining power. By locking into multi-year contracts for compute capacity, enterprises often find themselves unable to capitalize on emerging price wars or superior performance tiers from competitors. Economic lock-in occurs when the cumulative costs of migration exceed the projected long-term savings of moving to a new provider.

The Skills Gap: Operational Dependency

Operational dependency often hides within your engineering team’s expertise. When a DevOps team is exclusively certified in AWS technologies, they become a form of silent lock-in that limits your organization’s ability to explore alternative platforms or hybrid strategies. Cultivating a cross-cloud mindset through diverse training programs is essential for maintaining agility and avoiding vendor lock-in with aws at the human capital level. Many enterprises are now leveraging specialized IT Staffing Services to bridge these talent gaps, ensuring they have access to the versatile expertise required to manage platform transitions without disrupting their core business functions or long-term growth objectives.

Architectural Strategies for Cloud-Agnostic Resilience

Architectural autonomy is not a binary state but a spectrum that requires a disciplined approach to service selection and abstraction. By adopting containerization via EKS or Kubernetes as the universal runtime layer, organizations can establish a consistent execution environment that remains portable across disparate cloud providers. This methodology allows teams to leverage AWS innovation for immediate speed while ensuring that the underlying application logic isn’t inextricably tied to proprietary compute features. Implementing the “Adapter Pattern” further decouples your core business logic from cloud-native services by creating a standardized interface for external dependencies. When using Infrastructure as Code (IaC), prioritizing tools like Terraform ensures that your environment definitions remain provider-agnostic, allowing for the rapid recreation of infrastructure in alternate ecosystems if strategic priorities shift. Balancing the strategic implications of cloud adoption involves identifying which services provide a competitive advantage and which simply contribute to unnecessary dependency.

Abstraction Layers and Middleware

Service meshes like Istio or Linkerd provide a critical layer of abstraction by moving networking and security concerns away from AWS-specific tools into a platform-independent control plane. This approach is further strengthened by utilizing runtimes like Dapr to decouple code from stateful services such as SQS or DynamoDB, which effectively neutralizes the risk of deep API integration. Engaging in DevOps Consulting allows enterprises to design these exit-ready architectures with precision, ensuring that every component is evaluated for its impact on long-term flexibility. This strategic foresight transforms cloud infrastructure from a potential trap into a versatile engine for growth, providing the stability, scalability, and sovereignty required for modern digital operations.

Database Portability and Data Gravity

Data gravity remains a formidable obstacle when avoiding vendor lock-in with aws, particularly when relying on proprietary engines like Aurora or DynamoDB. While managed NoSQL offers high performance, it creates a rigid data layer that’s difficult to port without significant refactoring. Strategies for data decoupling, such as Change Data Capture (CDC), enable real-time portability by streaming data changes to external repositories, thereby reducing the friction of a potential exit. Planning for “The Big Move” also necessitates a clear understanding of egress timelines. Moving 50TB of data can take considerable time depending on throughput and costs around $4,500 in fees. If you require assistance in mapping your cloud-agnostic roadmap, our specialists can help you evaluate your current architecture to ensure it remains robust and portable.

Automated Testing: The Secret Weapon for Cloud Portability

A sophisticated architecture provides the skeleton of autonomy, but it is through rigorous validation that an enterprise breathes life into its cloud-agnostic vision. While many organizations focus on the initial deployment, avoiding vendor lock-in with aws requires a shift in perspective toward continuous testability. An exit strategy remains a theoretical paper exercise until it’s subjected to a validated test suite that proves an application’s resilience across heterogeneous environments. By implementing contract testing, DevOps teams can ensure that microservices maintain identical behavioral patterns regardless of the underlying cloud provider, thereby neutralizing the subtle risks of proprietary API dependencies. This methodical approach to validation allows leadership to view cloud exit strategies not as a defensive fallback, but as a proactive measure of operational health and strategic flexibility.

Benchmarking serves as a critical component of this validation process, utilizing performance testing to compare AWS metrics against potential alternative providers to ensure that migration does not compromise service levels. Establishing a dedicated Portability Test Bed allows for the simulation of real-world workloads in secondary environments, providing the empirical data necessary to confirm that an application is truly exit-ready. This environment acts as a crucible where architectural choices are tested against the realities of network latency, storage performance, and resource orchestration, ensuring that the enterprise maintains a steady hand in a fast changing technological landscape.

Continuous Portability Validation

Integrating cross-cloud smoke tests into your Software Test Automation Services ensures that portability remains a constant priority rather than an after-thought. While automation provides the speed required for large-scale operations, Manual Testing is essential for uncovering nuanced UI/UX discrepancies that arise from regional latency or platform-specific rendering differences. Automated validation provides the only objective measure of cloud independence, offering the peace of mind that comes from verified, repeatable results.

Digital Assurance and Risk Mitigation

Leveraging Software and Digital Assurance Testing enables a comprehensive audit of vendor-specific dependencies that architectural diagrams might overlook. By simulating catastrophic cloud outages, organizations can test the efficacy of multi-cloud failover strategies and measure the speed of their “Exit Trigger” to see how quickly critical workloads can be moved under pressure. This disciplined approach to risk reduction empowers enterprises to pursue large-scale technological evolution with confidence, knowing their digital sovereignty is protected by a framework of precision, portability, and progress.

Avoiding Vendor Lock-in with AWS: A Strategic Guide for Enterprise Autonomy in 2026

Governance and Managed Services: Maintaining Strategic Leverage

Establishing a robust governance framework is the cornerstone of long-term digital sovereignty, ensuring that architectural choices remain aligned with business objectives. A Cloud Center of Excellence (CCoE) serves as the institutional guardian of this mission, moving beyond mere technical oversight to actively monitor vendor dependency levels across the entire enterprise. By integrating cloud portability audits into the standard ITSM review cycle, leadership can transform avoiding vendor lock-in with aws from a reactive concern into a proactive governance discipline. This strategic oversight includes negotiating AWS contracts with explicit exit clauses and return guarantees for data, specifically leveraging the policy updates from March 2024 where AWS began waiving data transfer fees for customers departing the platform. While these regulatory shifts provide a foundation, true leverage is maintained through the constant evaluation of service alternatives and the enforcement of agnostic standards.

The methodical application of governance ensures that every cloud investment is scrutinized for its impact on future flexibility. This involves a shift from a “cloud-first” to a “cloud-smart” strategy, where the focus remains on organizational progress through the combination of human expertise and technical tools. By maintaining a steady hand in a fast-changing landscape, enterprises can achieve a state of institutional maturity that values stability, precision, and scalable growth above the convenience of proprietary features.

ITSM and Vendor Management

Aligning your cloud strategy with comprehensive IT Service Management Solutions provides the visibility required to manage complex, multi-provider ecosystems with precision. Through ServiceNow Consulting Services, organizations can implement automated discovery tools that track cloud assets and their portability status in real-time. This level of transparency is vital for identifying “Shadow IT” instances where individual departments may have adopted proprietary AWS services without considering the long-term migration risks. By centralizing asset management, enterprises ensure that every technological investment contributes to a versatile and exit-ready infrastructure.

Managed Outsourcing as a Portability Bridge

Managed services act as a strategic buffer, neutralizing the operational debt that often accumulates when internal teams become overly specialized in a single provider’s toolset. By utilizing Managed Outsourcing Services, enterprises can maintain a balanced talent portfolio that bridges the gap between AWS-specific execution and broader industry standards. This approach ensures that your organization retains the “Exit-as-a-Service” capability, where external partners provide the diverse skills necessary to facilitate a platform transition if market conditions change. Embracing this model is a critical component of avoiding vendor lock-in with aws, as it ensures your human capital remains as portable as your code. If you are ready to fortify your governance framework and reclaim strategic control over your digital assets, consult with our cloud governance experts today to build a roadmap for enduring autonomy.

The Test Triangle Framework: Ensuring Cloud Sovereignty

The Test Triangle Framework represents a sophisticated synthesis of technical precision and strategic foresight, specifically engineered to empower global enterprises in avoiding vendor lock-in with aws. By combining DevOps rigor with comprehensive Digital Assurance, we enable organizations to build systems that are inherently exit-ready from the moment of inception. Our structured 12-month roadmap facilitates a methodical transition from deep, proprietary AWS-native dependency to a resilient, cloud-agnostic architecture. This journey is grounded in a “Validation First” philosophy, which asserts that an infrastructure’s portability is only as real as the automated test suites that verify it. We don’t just design for autonomy; we implement the rigorous testing protocols necessary to prove that your applications can thrive in any environment.

Central to this framework is our 2026 approach to Atlassian Implementation, which serves as the collaborative engine for cross-functional cloud governance. By integrating Jira and Confluence directly into your cloud strategy, we create a transparent ecosystem where portability risks are documented, tracked, and mitigated in real-time. This level of visibility ensures that both technical managers and executive leadership maintain a clear understanding of the organization’s digital sovereignty. It’s about creating a culture of accountability where technical execution is always aligned with long-term business stability and operational agility.

Partnering for Long-Term Success

Test Triangle acts as a steady hand, providing the reliability and expertise required to navigate the complexities of large-scale technological evolution. We recently collaborated with a global financial firm to reduce their cloud dependency through automated verification protocols, demonstrating the peace of mind that stems from systemic risk reduction. This partnership approach ensures that your organization isn’t just surviving a migration, but is actively evolving into a more versatile and disciplined entity. If you’re ready to secure your autonomy and evaluate your current infrastructure, contact Test Triangle today for a comprehensive Cloud Portability Audit.

A Holistic View of Digital Transformation

Integrating cloud autonomy into your broader Digital Transformation Services is essential for maintaining a competitive edge in a fast-changing landscape. The synergy between Atlassian, ServiceNow, and AWS creates a unified operational layer that supports stability, precision, and scalable growth. By treating your cloud infrastructure as a modular asset rather than a permanent fixture, you empower your enterprise to pivot as market conditions dictate. Ultimately, vendor lock-in is a choice made through accumulated technical debt and administrative inertia, but with a reliable long-term collaborator, it’s never an inevitability. We remain deeply invested in your success, providing the tools and human expertise needed to ensure your digital future remains entirely in your own hands.

Mastering Enterprise Autonomy and Strategic Flexibility

Achieving true operational independence requires a disciplined transition from proprietary dependency to a validated, cloud-agnostic architecture. By prioritizing architectural abstraction and rigorous automated testing, your organization can successfully navigate the complexities of avoiding vendor lock-in with aws while maintaining the high pace of innovation your business demands. This strategic shift ensures that your digital infrastructure remains a versatile asset rather than a permanent constraint, allowing you to negotiate from a position of strength and pivot with precision as market conditions evolve.

Test Triangle serves as a reliable long-term collaborator for global enterprises across Europe, North America, and Asia, providing the human expertise and technical tools necessary to manage these complex transitions. With strategic partnerships spanning AWS, Atlassian, and ServiceNow, we bring institutional maturity and deep experience in highly regulated sectors like Pharma and Finance to every engagement. Secure Your Cloud Autonomy with Test Triangle’s Strategic Consulting today to begin building an exit-ready future. Your journey toward digital sovereignty is a path we are ready to walk together, ensuring your organization remains a steady hand in a fast-changing technological landscape.

Frequently Asked Questions

What is the most common cause of AWS vendor lock-in?

The primary catalyst for lock-in is the deep integration of proprietary APIs and specialized data services into an application’s core logic. When developers utilize high level services like DynamoDB or Aurora without abstraction layers, the resulting “sticky” architecture requires extensive code rewrites to migrate. This technical dependency is often compounded by financial commitments that prioritize immediate cost savings over long term architectural flexibility.

How does multi-cloud strategy help in avoiding vendor lock-in?

A multi-cloud posture facilitates autonomy by forcing teams to adopt standardized deployment patterns and provider agnostic tooling. By maintaining workloads across different ecosystems, enterprises naturally move toward avoiding vendor lock-in with aws through the use of universal runtimes like Kubernetes. This approach prevents any single provider from becoming a point of failure or a barrier to strategic negotiation during contract renewals.

Can I use AWS Lambda without getting locked in?

Yes, you can leverage serverless innovation without sacrificing portability by decoupling your business logic from the specific cloud trigger. Utilizing frameworks like the Serverless Framework or wrapping your logic in standard containers allows you to move functions between providers with minimal friction. The key is to treat the cloud specific event as a simple input that passes data to a platform independent execution layer.

What are the hidden costs of cloud migration and exit strategies?

Beyond the obvious egress fees, enterprises often overlook “hidden” networking charges such as NAT Gateway processing fees at $0.045 per GB and public IPv4 address hourly rates. There is also a significant “skills gap” cost associated with retraining a specialized workforce to manage a new platform’s unique operational nuances. These operational and financial frictions can often exceed the direct costs of data transfer during a platform transition.

How does Infrastructure as Code (IaC) improve cloud portability?

Infrastructure as Code allows for the creation of repeatable, documented environment definitions that can be redeployed across different regions or providers with high precision. Tools like Terraform enable a provider agnostic approach to resource provisioning, ensuring that your infrastructure remains a modular asset rather than a manual configuration trap. This methodology accelerates the “Exit Trigger” by allowing teams to recreate complex environments in hours rather than months.

Is it possible to achieve 100% cloud-agnostic architecture?

While theoretically possible, achieving total agnosticism often introduces a “portability tax” in the form of increased complexity and reduced access to provider specific innovations. Most successful organizations in 2026 pursue “strategic agnosticism,” focusing their portability efforts on high risk data layers while accepting managed services for non critical functions. This balanced approach ensures operational efficiency while maintaining the ability to pivot when business needs dictate.

What role does data egress play in vendor lock-in?

Data egress acts as a formidable financial barrier, with rates reaching $0.09 per GB after the initial 100GB monthly allowance. For a media company serving 50TB of content, these fees can quickly scale to $4,500 per month, creating a gravity effect that makes avoiding vendor lock-in with aws a significant budgetary challenge. Organizations must implement data decoupling strategies, such as Change Data Capture, to mitigate these costs before they become prohibitive.

How often should an enterprise test its cloud exit strategy?

Enterprises should validate their exit strategy at least annually or whenever a major architectural change is implemented. Integrating these tests into your standard ITSM review cycle ensures that portability remains a live capability rather than a theoretical document. Regular validation through automated smoke tests and performance benchmarking provides the empirical data required to maintain a steady hand in a fast changing technological landscape.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.

Beyond Two Levels: How N-Level Cascade Select Transforms Data Capture in Jira
Jira Cascade Select Limitations: Why Two Levels Aren’t Enough

Jira is trusted by organisations worldwide to manage projects, service requests, software development, HR processes, procurement workflows and more. However, one limitation continues to challenge teams across industries: Jira’s native Cascade Select field only supports two levels of hierarchy. For many organisations, data structures are far more complex.

Consider a simple classification hierarchy:
Food Type → Fruits → Tropical → Citrus → Orange → Navel Orange → Organic

Or a location structure:
Continent → Country → State → City → District → Area

These are natural, logical hierarchies that businesses use every day. Yet Jira’s standard field configuration stops at a parent and child selection. As organisations scale, this limitation often leads to workarounds, inconsistent data capture and reporting challenges.

N-Level Cascade Select from Test Triangle

That is exactly why Test Triangle developed
N-Level Cascade Select for Jira and Jira Service Management.


The Challenge of Multi-Level Data Capture in Jira

When Jira’s native fields cannot represent real-world data structures, teams often resort to:

  • Large dropdown lists containing hundreds of options
  • Multiple disconnected custom fields
  • Complex automation rules
  • Manual data validation processes
  • Custom development and scripting

While these approaches may work temporarily, they frequently create new challenges:

  • Poor user experience
  • Inconsistent data entry
  • Reduced reporting accuracy
  • Increased administration overhead
  • Greater risk of user error

The result is often messy data and inefficient workflows. Businesses need a better way to capture structured information without sacrificing usability.


What is N-Level Cascade Select for Jira?

N-Level Cascade Select extends Jira’s native capabilities by allowing organisations to create cascading dropdown fields with virtually unlimited depth.
Instead of being restricted to two levels, teams can create:

  • 3-level hierarchies
  • 5-level hierarchies
  • 10-level hierarchies
  • Any structure required by the business

Each selection dynamically filters the available options at the next level, creating a guided and intuitive user experience.
For example: Food Type → Fruits → Citrus → Orange → Navel Orange → Organic

Each choice narrows the next set of options, ensuring users only see relevant selections.The result is cleaner data, faster form completion and significantly improved reporting accuracy.


Key Features of N-Level Cascade Select

1. Dynamic Labels at Every Level

One of the most powerful features of N-Level Cascade Select is the ability to display unique labels at every stage of the hierarchy.
Rather than presenting users with generic dropdown menus, each level clearly communicates what information is required.

Example:

  • Food Type → Fruits
  • Fruit Category → Citrus
  • Citrus Type → Orange
  • Orange Variety → Navel
  • Production Method → Organic
  • Packaging Size → 500g

Users always understand where they are in the selection process, even across six or more levels.

Benefits:

  • Improved user experience
  • Reduced data entry mistakes
  • Faster form completion
  • Better adoption by end users

N-Level Cascade Jira App


2. Native Integration with Jira Service Management Request Types

N-Level Cascade Select works directly within Jira Service Management (JSM) Request Types and customer portals. This enables organisations to capture highly detailed information before a ticket is even created.

Example Customer Request:

  • Beverage
  • Coffee
  • Espresso-Based
  • Latte
  • Milk Type
  • Oat Milk
  • Iced

Instead of relying on follow-up questions from support agents, the entire request is captured during intake.

Benefits

  • Higher quality requests
  • Reduced triage effort
  • Faster resolution times
  • Improved customer experience

For service desk teams managing large request volumes, structured intake can dramatically improve efficiency.

N-Level Cascade Test Triangle


3. Real-Time Configuration Preview

Building complex hierarchies can be challenging without visibility into the final user experience.
That’s why N-Level Cascade Select includes a live preview panel within the configuration interface.
As administrators build their hierarchy, they can immediately see how the field will behave for end users.


Example –
As you create:

  • Category
  • Vegetables
  • Leafy
  • Dark Leafy
  • Spinach
  • Baby Spinach
  • Organic

The preview updates instantly. This removes guesswork from the configuration process and significantly reduces setup time.

Benefits

  • Faster configuration
  • Improved accuracy
  • Easier administration
  • Reduced testing cycles

4. JSON Import and Export Capabilities

Many organisations already maintain structured classifications outside Jira. N-Level Cascade Select supports full hierarchy import and export using JSON.

Import Use Cases

  • Product catalogues
  • Asset structures
  • Location hierarchies
  • Service catalogues
  • Department structures

Instead of manually creating hundreds or thousands of options, administrators can import complete hierarchies in seconds.

Export Use Cases

  • Backup configurations
  • Replicate structures across environments
  • Update existing hierarchies
  • Version control

This capability makes the solution highly scalable for enterprise environments.

N-Level Cascade Atlassian


5. Workflow Transition Screen Support

Unlike many field extensions, N-Level Cascade Select also works on Jira workflow transition screens.
When issues move between statuses, users can complete structured selections without leaving the transition process.

Example: A hardware support ticket moves from: Open → In Development
During the transition, users can select: Electronics → Mobile Devices → Smartphones → Android → Samsung → Galaxy Series
The selected value is stored directly against the issue.

Benefits

  • Better workflow governance
  • Improved process compliance
  • Accurate classification at key workflow stages

N-Level Cascade Select JSM Atlassian


Built on Atlassian Forge for Enterprise Security

Security and compliance are critical for modern organisations.
N-Level Cascade Select was built entirely on Atlassian Forge, Atlassian’s cloud-native development platform.

This means:

  • Data remains within Atlassian infrastructure
  • No external servers are required
  • No third-party hosting environments
  • Simplified compliance requirements
  • Enhanced security controls

For organisations operating in regulated sectors such as:

  • Healthcare
  • Financial Services
  • Government
  • Legal Services
  • Education

Forge-native architecture provides confidence that data remains within the Atlassian ecosystem.

Cloud Migration Ready
As organisations continue moving from Jira Server and Data Centre to Atlassian Cloud, Forge apps provide future-ready compatibility and alignment with Atlassian’s long-term cloud strategy.


Use Cases Across Every Department

IT Service Management Teams. Capture detailed request information:

Issue Type → System → Component → Sub-Component → Priority → SLA Tier

Benefits:

  • Faster triage
  • Better routing
  • Improved reporting

HR Teams

Structure onboarding and employee requests:

Division → Department → Team → Role Level → Employment Type → Location

Benefits:

  • Consistent HR processes
  • Improved employee experience
  • Reduced administrative effort

Finance & Procurement

Classify expenses accurately:

Company → Cost Centre → Budget Category → Expense Type → Vendor Type → Currency

Benefits:

  • Improved financial reporting
  • Better budget governance
  • Reduced manual corrections

Legal & Compliance

Capture regulatory information:

Contract Type → Jurisdiction → Country → Regulatory Body → Standard → Review Status

Benefits:

  • Better audit readiness
  • Improved compliance tracking
  • Easier record retrieval

Product & Engineering Teams

Mirror product architecture directly within Jira:

Product Line → Module → Feature → Sub-Feature → Release Version → Priority

Benefits:

  • Cleaner backlog management
  • Better reporting
  • Improved product governance

Why Structured Data Matters in Jira

The quality of reporting, automation and decision-making in Jira depends on the quality of the data being captured.
Flat drop downs and disconnected fields often result in:

  • Duplicate values
  • Inconsistent classifications
  • Reporting inaccuracies
  • Increased administration effort

N-Level Cascade Select ensures data is captured consistently and logically from the beginning.
The deeper the hierarchy, the more valuable structured data becomes.


Getting Started with N-Level Cascade Select

N-Level Cascade Select is available on the Atlassian Marketplace with a free trial.
We recommend testing the app using a real business classification structure rather than a simple demonstration hierarchy.
This provides the fastest way to evaluate how the solution will perform within your environment.
Comprehensive documentation is available covering:

  • Installation
  • Configuration
  • JSON Import and Export
  • Jira Service Management Integration
  • Best Practices

The Test Triangle team is also available to assist with implementation, configuration and support.


Conclusion

Jira is one of the world’s most powerful workflow platforms, but many organisations require deeper classification structures than native Cascade Select fields can provide.
N-Level Cascade Select removes the two-level limitation and enables businesses to capture structured data exactly as their processes require.
Whether you’re managing service requests, HR workflows, procurement processes, compliance records or product development, the app helps deliver:

  • Better data quality
  • Improved user experience
  • Faster reporting
  • Reduced administrative overhead
  • Stronger governance

If your business relies on complex hierarchical data, N-Level Cascade Select provides a scalable and intuitive solution built specifically for Jira and Jira Service Management.

Start Your Free Trial Today. Ready to go beyond two levels?

Explore N-Level Cascade Select for Jira and Jira Service Management
on the Atlassian Marketplace and discover how structured data capture can transform your Jira environment.


With the global AI in ecommerce market projected to reach $45.3 billion by late 2026, the margin for manual error has effectively vanished. You likely recognize that legacy scripts and high maintenance costs aren’t just operational hurdles; they’re active threats to your stability during peak traffic seasons. As retail ecosystems become increasingly fragmented across mobile, web, and physical POS systems, the demand for sophisticated automation testing for retail ecommerce platforms has transitioned from a technical preference to a core business necessity. We understand the pressure of maintaining a steady hand when a critical payment gateway risks failure during a high-stakes promotion because your testing suite couldn’t keep pace with rapid DevOps cycles.

This article provides the strategic blueprint you need to architect a scalable, AI-driven automation framework that secures omnichannel revenue while significantly accelerating your time-to-market. We’ll explore how modern tools like Playwright 1.60 are redefining framework adoption and how to ensure your deployments remain zero-defect amidst the complexities of the EU AI Act and evolving data privacy regulations. By aligning your QA strategy with systematic DevOps integration, you’ll discover how to transform testing from a bottleneck into a high-performance engine for organizational growth and long-term stability.

Key Takeaways

  • Transition from reactive manual regression to AI-orchestrated continuous testing to safeguard mission-critical revenue streams and ensure operational stability during peak traffic.
  • Identify the core pillars of robust automation testing for retail ecommerce platforms, focusing on end-to-end validation of the ‘Golden Path’ and high-concurrency performance simulations.
  • Resolve the inherent complexities of omnichannel integration by implementing specialized testing strategies for seamless ‘Buy Online, Pick Up In-Store’ (BOPIS) customer journeys.
  • Leverage AI-augmented codeless automation and Atlassian-driven workflows to enhance project transparency, streamline communication, and accelerate your organization’s time-to-market.
  • Establish a reliable foundation for large-scale digital transformation by aligning your QA framework with high-level business objectives through a strategic, long-term partnership model.

The Strategic Necessity of Automation in the 2026 Retail Landscape

Global retail leaders now view digital stability as an inseparable component of brand equity. In a market where ecommerce sales are rapidly climbing toward nearly $8 trillion by 2028, the technical infrastructure supporting these transactions must be flawless. Implementing comprehensive automation testing for retail ecommerce platforms has evolved from a back-office efficiency project into a mission-critical revenue safeguard. It ensures that complex promotional logic, diverse payment integrations, and high-velocity inventory updates function correctly under the intense pressure of global traffic. Relying on outdated methods isn’t just risky; it’s a direct threat to the bottom line.

The transition from traditional manual regression to AI-orchestrated continuous testing reflects the reality of 2026 consumer behavior. Modern shoppers expect 99.99% uptime and instantaneous responses. Even a momentary glitch during a checkout process can lead to permanent cart abandonment and long-term reputational damage. By utilizing advanced test automation, organizations can maintain architectural integrity while delivering the rapid updates that keep them competitive. This shift allows for a proactive stance on quality, identifying potential failures before they ever reach the end user.

Evolving Retail Ecosystems and Testing Complexity

As brands move away from monolithic platforms toward headless commerce architectures, the number of integration points increases exponentially. AI-driven personalization engines now create unique user journeys for every visitor, which means testing a single “happy path” is no longer sufficient. While Manual Testing remains the vital foundation for validating human-centric UX and exploratory edge cases, it cannot address the sheer scale of modern data-driven environments. Automation provides the necessary coverage for these hyper-personalized scenarios, ensuring that dynamic content doesn’t break the underlying transaction logic across various touchpoints.

Economic Drivers for Automation Adoption

The financial implications of system failure during high-concurrency events like Black Friday are staggering, often resulting in millions of dollars in lost revenue within minutes. Strategic automation testing for retail ecommerce platforms reduces the long-term “QA tax” that typically slows down new feature deployments, allowing teams to innovate without compromising stability. We’ve seen that when a robust framework is implemented, retailers can achieve a 50% reduction in QA cycle times, directly translating into faster time-to-market and a superior return on investment for digital initiatives. This efficiency allows global enterprises to reallocate human capital toward high-value strategic growth rather than repetitive maintenance.

Core Pillars of a Robust Ecommerce Automation Framework

Building a resilient foundation for automation testing for retail ecommerce platforms requires moving beyond siloed script execution toward an integrated ecosystem of quality. This framework must prioritize the “Golden Path,” which encompasses the entire user journey from initial product discovery and AI-assisted search to the final checkout confirmation. By validating these critical workflows under diverse conditions, organizations ensure that high-value transactions remain uninterrupted, even as underlying codebases evolve daily. A truly strategic approach balances functional precision with high-level operational oversight, providing the stability, security, and scalability required for global growth.

Performance and load testing must simulate high-concurrency events that mirror the volatility of seasonal peaks. It’s no longer enough to test for average traffic; your systems must withstand the sudden surges characteristic of limited-edition drops or flash sales. Simultaneously, security testing has become a non-negotiable pillar to maintain PCI-DSS compliance and adhere to the stringent requirements of the EU AI Act, which is fully implemented as of summer 2026. With new data privacy laws taking effect in states like Indiana, Kentucky, and Rhode Island in early 2026, your automation suite must verify that personalization algorithms remain ethical, transparent, and compliant with regional data deletion mandates.

API and Microservices Testing for Omnichannel Flow

In a headless commerce environment, the seamless exchange of data between the frontend, inventory management systems, and CRM is the lifeblood of the operation. Our API testing services focus on validating these invisible connections to prevent catastrophic checkout failures. We meticulously verify third-party integrations, including payment gateways, complex shipping APIs, and multi-tiered loyalty programs, ensuring that a failure in one microservice doesn’t trigger a total system collapse. This rigorous validation of the middle tier is what allows for the “buy anywhere, fulfill anywhere” promise that modern consumers demand.

Data Migration and Integrity Validation

Synchronizing real-time inventory across physical storefronts and digital channels presents a significant technical hurdle. During platform re-platforming or major updates, data migration testing ensures that product catalogs, pricing logic, and customer profiles transition without corruption. Automating the verification of these massive datasets prevents the “ghost inventory” issues that lead to overselling and customer dissatisfaction. If you’re currently evaluating how to strengthen these pillars within your own infrastructure, consulting with a strategic advisor can help identify the most impactful starting point for your transformation.

Compatibility testing rounds out the framework by addressing the fragmented landscape of 2026 devices and browsers. As Playwright 1.60 and Cypress 15 dominate the framework landscape, your strategy must ensure a consistent experience across diverse OS versions and mobile hardware. This comprehensive coverage transforms automation testing for retail ecommerce platforms from a simple bug-finding exercise into a powerful engine for cross-channel brand reliability.

Overcoming Omnichannel Complexity and Integration Hurdles

The most common objection to modernizing quality assurance is the belief that legacy systems are too rigid for advanced frameworks. However, strategic automation testing for retail ecommerce platforms doesn’t require a total architectural overhaul. By wrapping aging backend systems in modern API layers, we can implement automated validation that bridges the gap between heritage databases and contemporary frontends. This incremental approach allows global enterprises to achieve stability without the risks associated with a “rip and replace” strategy. It’s about creating a steady hand that manages both the old and the new with equal precision.

Managing test data privacy has become a legal mandate in the 2026 retail environment. With the EU AI Act fully implemented and new comprehensive privacy laws in effect in Indiana, Kentucky, and Rhode Island, using production data for testing is no longer an option. Automated data masking and synthetic data generation are now essential components of a compliant framework. These tools allow teams to simulate complex customer profiles and transaction histories across all channels while ensuring that sensitive information remains secure and regulatory requirements are met across every jurisdiction.

Headless Commerce and Frontend Agnostic Testing

Decoupling the frontend experience from backend logic is essential for the rapid iteration cycles modern retail demands. By utilizing software test automation services, brands can validate multiple presentation layers against a single set of business rules. Whether a customer is interacting via a traditional web browser, a mobile app, or a voice assistant, the underlying transaction logic must remain consistent. This frontend-agnostic approach ensures a unified brand experience across the entire IoT ecosystem, protecting revenue regardless of how the customer chooses to shop.

Continuous Integration and DevOps Alignment

Speed shouldn’t come at the expense of reliability. Embedding automated suites directly into the CI/CD pipeline enables a ‘shift-left’ quality mindset where defects are identified and resolved during the development phase. This is where DevOps Consulting provides the greatest value. It bridges the gap between development velocity and operational stability. Utilizing containerization allows for isolated and scalable test environments, ensuring that your automation testing for retail ecommerce platforms remains performant and reliable as your digital infrastructure evolves.

Implementing Scalable QA: Tools, AI, and Managed Services

Selecting the right technical architecture in 2026 requires a balanced approach between established frameworks and emergent AI capabilities. While Playwright 1.60 and Cypress 15 remain the standard for high-performance scripting, many global enterprises are now integrating AI-augmented codeless automation to lower the technical barrier for non-engineering stakeholders. A truly mature strategy for automation testing for retail ecommerce platforms doesn’t view these as competing choices but as complementary layers within a unified quality ecosystem. This hybrid model allows for the precision of traditional code alongside the speed of AI-driven test generation, ensuring your infrastructure remains both robust and adaptable.

To achieve full operational visibility, testing results must be integrated directly into your broader IT management framework. We specialize in connecting automated QA outputs to Atlassian Consulting workflows, ensuring that every identified defect is automatically triaged and tracked within Jira or Confluence. Simultaneously, leveraging ServiceNow Implementation for automated incident reporting allows your service desk to respond to system anomalies in real time. This closed-loop system transforms QA from a siloed activity into a transparent, organization-wide asset that informs executive decision-making and accelerates release cycles.

The fluctuating demands of the retail calendar often make maintaining a large, permanent in-house QA team financially inefficient. Many leading brands are shifting toward Managed Outsourcing Services to secure elastic capacity that can scale alongside seasonal traffic peaks. This model provides the peace of mind that comes from expert-led execution without the overhead of long-term internal expansion. By partnering with a reliable collaborator, you can maintain high standards of quality while focusing your core team on high-value digital transformation initiatives. Contact our strategic advisors today to design a scalable QA model tailored to your 2026 growth targets.

AI and Machine Learning in Test Orchestration

Modern retail UIs change frequently to accommodate new promotions and personalization logic, often breaking traditional automation scripts. Self-healing scripts utilize machine learning to automatically adjust to minor DOM changes, drastically reducing the maintenance burden on your engineering team. Predictive analytics can now identify high-risk areas in your ecommerce codebase by analyzing historical failure patterns, allowing you to prioritize testing where it matters most. Additionally, automating visual regression ensures that your brand experience remains pixel-perfect across an ever-growing landscape of mobile devices and screen resolutions.

Strategic Staffing and Talent Acquisition

Bridging the skills gap in advanced automation requires access to specialized talent that understands both retail logic and modern toolstacks. Our IT Staffing Services provide the versatility needed to augment your existing team with seasoned experts who can hit the ground running. When evaluating the ROI of QA outsourcing versus in-house team building, consider the speed and precision that offshore or contract resources bring to peak-load testing cycles. This strategic staffing approach ensures you have the right human expertise to manage the technical tools effectively, maintaining organizational progress regardless of market volatility.

Strategic Automation Testing for Retail Ecommerce Platforms in 2026

Test Triangle’s Strategic Partnership Approach for Retailers

In a technological landscape defined by rapid evolution and high-velocity commerce, we position ourselves as more than a vendor; we are a reliable long-term collaborator dedicated to your digital transformation. Implementing automation testing for retail ecommerce platforms is a critical first step, yet true operational maturity requires a broader, multi-disciplinary perspective. By combining our deep expertise in Atlassian, ServiceNow, and AWS, we provide a unified framework that ensures your infrastructure is not only robust today but remains scalable for the demands of 2026 and beyond. This approach focuses on stability, precision, and growth, allowing your leadership team to navigate complexity with absolute confidence.

Our engagement models are designed with the flexibility needed to address the unique pressures of the retail sector. Whether you require comprehensive managed services to oversee your entire QA ecosystem or specialized IT staffing to augment your internal engineering team during peak seasons, our delivery remains consistent and high-quality. We provide tailored technology roadmapping that identifies potential risks before they impact revenue, ensuring that your digital assets are protected against the volatility of the global market. This strategic alignment between technical execution and business outcomes is the cornerstone of our partnership model.

Holistic IT Service Management: Continuity, Compliance, Confidence

Operational continuity is the lifeblood of global retail, where even a few minutes of downtime can result in significant financial loss. Our IT Service Management solutions are engineered to provide 24/7 oversight, ensuring that your platforms remain performant under any load. By integrating ServiceNow Consulting, we streamline post-release support and automate incident management, creating a seamless bridge between your development teams and your end users. For retail executives, a strategic technology roadmap serves as a vital blueprint that mitigates operational risk while accelerating long-term digital evolution.

Empowering Global Retail: Talent, Tools, Transformation

Accessing the right human expertise is often the greatest hurdle in scaling a modern automation framework. Through our staffing solutions, we provide access to a global pool of elite QA engineers who specialize in the intricacies of automation testing for retail ecommerce platforms. Industry-leading retailers consistently trust our Atlassian Consulting to optimize their internal workflows, ensuring that project management remains transparent and efficient. This combination of human expertise and technical rigor allows your organization to maintain a steady hand in a fast-changing market. Partner with Test Triangle to secure your ecommerce future.

Securing Your Omnichannel Revenue through Strategic Digital Assurance

The transition toward AI-driven automation has moved from a technical preference to a fundamental requirement for maintaining operational stability in a landscape defined by hyper-personalization and strict data regulations. By architecting a framework that addresses the core pillars of functional precision and high-concurrency performance, your organization can effectively mitigate the risks associated with legacy systems and fragmented omnichannel journeys. Implementing automation testing for retail ecommerce platforms ensures that your digital infrastructure remains resilient, compliant, and prepared for the rapid surges of a global market.

As an Atlassian Gold Solution Partner and ServiceNow Specialist Partner, we offer the institutional maturity and technical rigor required to integrate quality assurance directly into your long-term business objectives. With global delivery centers strategically located across Europe, North America, and Asia, we provide the versatility and scale necessary for sustained organizational progress. We invite you to Explore our Digital Assurance and Testing Services to discover how a dedicated collaborator can empower your technological evolution. Your journey toward a zero-defect deployment future begins with a steady hand and a visionary approach to quality.

Frequently Asked Questions

What is the primary benefit of automation testing for retail ecommerce platforms?

The primary benefit of automation testing for retail ecommerce platforms is the systemic protection of mission-critical revenue streams through the reduction of operational risk. By implementing a robust framework, global enterprises ensure that high-value transactions remain uninterrupted even during high-velocity update cycles. This strategic approach allows for consistent system stability while significantly accelerating the release of new features to a competitive global market.

How does ecommerce testing differ from standard website testing in 2026?

Ecommerce testing in 2026 is distinguished by the extreme complexity of third-party integrations and the necessity of validating hyper-personalized user journeys. Unlike standard websites, retail platforms must synchronize real-time inventory, manage diverse payment gateways, and adhere to strict regional data privacy mandates like the EU AI Act. This requires a sophisticated testing strategy that accounts for the dynamic nature of transactional logic across multiple digital touchpoints.

When is the best time to automate ecommerce test cases vs. keeping them manual?

You should prioritize automation for repetitive, high-volume regression suites and critical “Golden Path” workflows that directly impact your transaction success rates. Manual testing remains the superior choice for exploratory scenarios, human-centric UX validation, and early-stage features where the interface is still undergoing significant architectural changes. A balanced strategy ensures that human expertise is reserved for qualitative assessment while technical tools handle the scale of systematic validation.

Can automation testing help with Black Friday and peak season preparation?

Automation is an essential component of peak season readiness because it allows for the simulation of high-concurrency traffic events that mirror Black Friday surges. By executing automated performance and load tests, retailers identify architectural bottlenecks before they lead to catastrophic system failure during high-traffic periods. This proactive validation provides the peace of mind that your infrastructure can withstand sudden traffic spikes without compromising the customer experience.

What are the essential tools for automating a mobile ecommerce application?

How do we integrate automation testing into our existing DevOps pipeline?

Integrating automation testing for retail ecommerce platforms into a DevOps pipeline involves embedding automated suites directly into the CI/CD workflow to enable a “shift-left” quality mindset. This process is enhanced by utilizing containerization for isolated test environments and connecting results to Atlassian or ServiceNow for transparent incident tracking and triaging. This alignment ensures that every code change is validated automatically, reducing the cycle time from development to production.

What is the role of AI in modern retail software testing?

AI transforms modern retail testing by enabling self-healing scripts that automatically adjust to frequent UI changes, which drastically reduces the long-term maintenance burden on engineering teams. Machine learning models also provide predictive analytics to identify high-risk areas in the codebase based on historical failure patterns. This intelligence allows organizations to prioritize their testing efforts strategically, focusing on the components most likely to impact system stability or customer satisfaction.

How much does it cost to implement an enterprise-grade automation framework?

The cost of implementing an enterprise-grade framework depends on the complexity of your digital ecosystem, the selected toolstack, and your preferred service engagement model. While the initial investment accounts for framework architecture and tool licenses, the long-term value is derived from reduced QA cycle times and the prevention of costly system downtime. We recommend consulting with a strategic partner to design a scalable model that aligns with your specific organizational growth targets.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.

By the end of 2026, nearly 30% of all medical visits in the U.S. will occur remotely, yet many organizations remain shackled by legacy technical debt that threatens both patient safety and regulatory standing. For leadership navigating devops adoption in healthcare industry frameworks, the challenge isn’t just about speed; it’s about maintaining absolute integrity under the FDA’s Quality Management System Regulation (QMSR) that became enforceable on February 2, 2026. You likely feel the tension between the need for rapid digital evolution and the heavy burden of mandatory multi-factor authentication and annual penetration testing required by the latest HIPAA Security Rule updates. It’s a high-stakes environment where the traditional “move fast and break things” mentality is rightfully viewed as a risk to clinical outcomes.

We believe that high-velocity innovation doesn’t have to compromise your compliance posture. This strategic roadmap provides the clarity you need to balance rigorous GxP standards with the agility of modern engineering, transforming your pipeline into a source of automated trust. By integrating sophisticated platforms like Atlassian and ServiceNow into a cohesive ecosystem, your team can achieve reduced deployment downtime and automated auditing. You’ll discover how a disciplined approach to DevOps empowers your organization to deliver life-saving digital solutions with precision, pace, and protection. We’ll preview the essential shifts in AI model governance and ISO/IEC 27001:2022 standards that will define the healthcare landscape through 2026.

Key Takeaways

  • To address rising patient expectations for remote monitoring, this guide explores the methodology for migrating from monolithic legacy systems to secure, microservices-based healthcare architectures.
  • By implementing Infrastructure as Code within your devops adoption in healthcare industry strategy, your team can ensure that every environment is consistent, auditable, and reproducible.
  • By bridging the gap between development agility and validated stability, you will learn to engineer automated pipelines that satisfy stringent GxP and HIPAA requirements without sacrificing deployment frequency.
  • Through the integration of industry-leading Atlassian platforms, organizations can build a culture of shared responsibility that ensures every digital health solution is founded on transparency, traceability, and trust.

The Paradigm Shift: Why Healthcare is Embracing DevOps in 2026

The global healthcare sector is undergoing a fundamental restructuring as organizations migrate from rigid, monolithic legacy systems toward agile, microservices-based architectures. This transition is no longer a peripheral IT project; it’s a strategic necessity driven by a global artificial intelligence in healthcare market valued at 51.20 billion dollars in 2026. By decoupling core functionalities, providers can update specific clinical modules without jeopardizing the entire patient data ecosystem. This modular approach aligns with core DevOps principles, allowing for the continuous refinement of digital health tools while maintaining the high standards of safety required in a clinical setting.

Achieving successful devops adoption in healthcare industry frameworks requires a sophisticated understanding of the 2026 regulatory environment. With the FDA’s Quality Management System Regulation (QMSR) having gone into effect on February 2, 2026, cybersecurity is now an enforceable component of medical device quality. Organizations must balance operational efficiency with the mandatory implementation of technical controls, such as the required multi-factor authentication and encryption protocols finalized by the Department of Health and Human Services. The business case is clear: automation isn’t just about speed, it’s about engineering a fail-safe environment where patient safety and data integrity are hard-coded into the deployment process.

Beyond the Pandemic: The 2026 Healthcare IT Landscape

The digital acceleration of the early 2020s left many hospitals with significant technical debt, characterized by fragmented systems and rushed software deployments. By 2026, the focus has shifted from reactive maintenance to a proactive, predictive management model. With remote visits predicted to comprise 25% to 30% of all U.S. medical consultations by the end of this year, the underlying infrastructure must be resilient enough to support high-occupancy telemedicine platforms without latency or security breaches. This requires a transition from manual oversight to automated monitoring that can anticipate system failures before they impact patient care.

Strategic Drivers for DevOps Adoption

The business case for devops adoption in healthcare industry initiatives rests on the dual pillars of risk mitigation and clinical excellence. Automated pipelines eliminate the manual configuration errors that frequently lead to downtime, directly reducing the operational costs associated with system failures. More importantly, these methodologies accelerate the delivery of diagnostic software updates, ensuring that clinicians have access to the latest AI-powered documentation tools. We view these capabilities as fundamental to our broader digital transformation services, positioning technology as a steady hand that guides organizational progress toward scalable growth and enhanced patient outcomes.

The Technical Pillars: Building a Compliant Healthcare DevOps Pipeline

Healthcare DevOps represents a specialized methodology that integrates software development, operations, and compliance into a unified, high-integrity lifecycle. Unlike standard enterprise environments, devops adoption in healthcare industry frameworks must treat regulatory requirements as functional specifications rather than external constraints. This approach ensures that every code commit undergoes rigorous verification before it reaches a clinical setting. By engineering a pipeline that prioritizes stability, security, and scalability, organizations can maintain the pace of innovation required by 2026 market demands without compromising the stringent standards of patient safety.

Infrastructure as Code (IaC) serves as the bedrock of this transformation, allowing teams to define medical environments through version-controlled scripts. This methodology ensures that every deployment is consistent, auditable, and reproducible, which is essential for aligning with the FDA’s Quality Management System Regulation (QMSR). When infrastructure is treated as code, manual configuration errors are eliminated; this provides a clear audit trail that simplifies premarket submissions. Continuous Integration and Deployment (CI/CD) pipelines must be specifically tailored for these validated environments, incorporating automated gates that prevent non-compliant code from advancing through the delivery lifecycle.

Compliance as Code (CaC)

In the 2026 regulatory landscape, manual compliance checks are no longer sufficient to manage the complexity of modern health data. Compliance as Code (CaC) automates the enforcement of HIPAA and GDPR policies directly within the delivery pipeline, ensuring that data at rest and in transit remains encrypted by default. By integrating software and digital assurance testing into the earliest stages of development, teams can identify vulnerability risks before they manifest in production. These automated systems generate real-time auditing logs, providing a transparent record of security posture that satisfies the annual penetration testing mandates of the updated HIPAA Security Rule.

Infrastructure Resilience and Scalability

Modern clinical applications require high-availability architectures that can scale dynamically to meet patient demand. Utilizing cloud-native tools allows for the implementation of self-healing systems that automatically detect and remediate service interruptions, preventing critical downtime during remote surgical procedures or diagnostic sessions. Containerization technologies, such as Docker and Kubernetes, play a vital role in isolating sensitive medical data, ensuring that microservices remain decoupled and secure. This modularity allows for rapid updates to telemedicine platforms while maintaining a hardened perimeter around Electronic Health Records. If you’re ready to modernize your infrastructure, you can discuss your compliance architecture with our strategic advisors to ensure your pipeline is future-proofed for 2026.

High-Impact Applications: Transforming EHR, Telemedicine, and AI

The strategic implementation of devops adoption in healthcare industry frameworks manifests most clearly through the modernization of patient-facing and diagnostic applications. As the global telemedicine market is estimated to exceed 188.93 billion dollars in 2026, the demand for low-latency, high-security connections has become a clinical imperative. Modern DevOps practices enable the seamless automation of Electronic Health Record (EHR) updates, ensuring that critical patient data remains accessible without the disruptive downtime that historically plagued legacy maintenance windows. This creates a foundation of resilience, reliability, and responsiveness that is essential for maintaining continuity of care in high-pressure environments.

Beyond EHRs, the integration of AI-powered diagnostics in radiology and pathology requires a robust MLOps lifecycle to manage model retraining and deployment. With the global artificial intelligence in healthcare market predicted to reach a valuation of approximately 744.34 billion dollars by 2035, managing these complex models through automated pipelines ensures diagnostic accuracy and regulatory alignment. Similarly, pharmacy management systems benefit from streamlined supply chain integrations. Real-time inventory tracking prevents medication shortages and enhances patient safety through precise distribution, illustrating how automation bridges the gap between logistical efficiency and clinical outcomes.

Modernizing EHR with Atlassian and ServiceNow

Effective EHR management requires a high degree of transparency and structured collaboration between IT departments and clinical staff. Utilizing Jira allows organizations to maintain compliance-ready task management, where every modification to a clinical workflow is documented and traceable for future audits. For rapid incident response within these complex systems, leveraging ServiceNow consulting services ensures that EHR anomalies are identified and remediated before they impact patient care. This synergy between industry-leading platforms fosters a culture of institutional accountability, allowing teams to navigate digital transformations with a sense of security and precision.

Scaling AI and Remote Patient Monitoring (RPM)

Remote patient monitoring is set to manage a significant portion of chronic conditions as medical visits shift toward outpatient settings through 2026. Scaling these services requires securing the “Internet of Medical Things” (IoMT) through automated security testing that identifies vulnerabilities across diverse device integrations. By implementing MLOps, healthcare providers can ensure continuous model retraining, which is vital for maintaining the integrity of diagnostic AI. This disciplined approach to model governance ensures that data remains consistent across the entire patient journey, from initial remote consultation to long-term chronic care management, while satisfying the EU AI Act’s requirements for human oversight.

Achieving successful devops adoption in healthcare industry frameworks requires a fundamental reconciliation between the velocity of Agile development and the rigidity of GxP validation. While traditional validation processes often relied on manual, paper-based documentation that created significant bottlenecks, modern healthcare DevOps leverages “Compliance as Code” to automate these requirements. By implementing automated verification and validation (V&V) protocols, organizations can ensure that every software iteration meets predefined safety and efficacy standards before it ever reaches a clinical environment. This transition replaces reactive auditing with proactive, continuous compliance, allowing technical managers to maintain a steady hand over increasingly complex digital health ecosystems.

GxP compliance in DevOps is the automated alignment of technical output with regulatory safety standards. Managing risk in this high-stakes environment depends on granular access controls and sophisticated identity management. By restricting system access based on specific clinical or technical roles, organizations can prevent unauthorized modifications that might compromise patient data. This strategy is particularly vital given the 2026 HIPAA Security Rule updates, which have shifted many previously addressable safeguards to mandatory requirements. Through the integration of these controls directly into the deployment pipeline, healthcare providers can achieve a state of Validation, Verification, and Visibility that satisfies both internal stakeholders and external auditors.

GxP-Validated DevOps Pipelines

A validated pipeline must serve as a “Single Source of Truth,” capturing every change control and audit trail automatically. Within a continuous delivery model, the software validation lifecycle is no longer a separate phase but an integrated stream of automated tests and electronic signatures. This ensures that the documentation required for ISO 13485:2016 or QMSR compliance is generated in real-time, reducing the burden on quality assurance teams. For organizations seeking the specialized expertise to build these complex systems, partnering with IT staffing agencies for pharmaceutical industry can provide the compliance-focused talent necessary to bridge the gap between engineering and regulation.

Security by Design in Healthcare

Security by design requires the integration of OWASP standards and automated vulnerability scanning at the very beginning of the development lifecycle. By treating security as a non-negotiable stage of the pipeline, organizations can identify potential breaches before they pose a threat to patient safety. This is especially critical as the 2026 regulatory landscape mandates biannual vulnerability scans and annual penetration testing. Automation ensures these checks are performed consistently and documented thoroughly, providing the peace of mind that comes from a hardened, resilient infrastructure. To begin architecting your compliant pipeline, consult with our DevOps experts today.

DevOps Adoption in Healthcare Industry: A Strategic Roadmap for 2026

Strategic Execution: Partnering for Scalable Digital Transformation

Strategic execution within the healthcare sector requires a deliberate departure from siloed departmental operations toward a culture of shared responsibility. For leadership, successful devops adoption in healthcare industry frameworks depends on the seamless alignment of developers, operations teams, and clinicians. This unified approach ensures that technical decisions are always informed by clinical realities, fostering an environment where innovation serves patient outcomes without compromising safety. By utilizing a robust Atlassian implementation, organizations can achieve the transparency required to manage complex workflows, providing stakeholders with real-time visibility into the development lifecycle and regulatory status of critical health applications.

Building this infrastructure requires more than just tools; it demands a partner who possesses a deep understanding of both high-velocity engineering and the rigid constraints of life sciences. Selecting a collaborator who can provide comprehensive DevOps Consulting ensures that your digital evolution is anchored in institutional maturity rather than temporary fixes. We position ourselves as a reliable long-term collaborator, offering the Precision, Performance, and Peace of mind necessary to navigate the complexities of 2026 and beyond. Measuring maturity involves tracking specific Key Performance Indicators (KPIs) such as deployment frequency for EHR updates, Mean Time to Recovery (MTTR) for clinical systems, and the success rate of automated compliance audits.

Managed Services and Talent Acquisition

The persistent healthcare IT skills gap often prevents organizations from realizing the full potential of their devops adoption in healthcare industry initiatives. Addressing this challenge requires access to engineers who understand the delicate intersection of cloud-native technology and life sciences compliance. By leveraging managed outsourcing services, healthcare providers can augment their teams with specialized talent without the overhead of lengthy recruitment cycles. This strategic staffing model allows for the rapid scaling of automation efforts while maintaining the high standards of quality and security expected in a safety-critical industry.

Phased Implementation Roadmap

Transforming a complex healthcare ecosystem is most effective when approached as a methodical, phased progression. The journey begins with Phase 1, which involves assessing current maturity levels and identifying the legacy constraints that hinder agility. In Phase 2, organizations should establish a compliant pilot pipeline for non-critical systems, allowing teams to refine their automated verification protocols in a controlled environment. Finally, Phase 3 focuses on scaling these validated automation patterns across the entire enterprise. This structured cadence ensures that every step forward is supported by a stable foundation, mirroring the operational efficiency promised to our global partners.

Future-Proofing Healthcare Through Automated Integrity

The 2026 healthcare landscape demands a departure from reactive maintenance toward a future defined by resilience, rigor, and reliability. As we’ve explored, successful devops adoption in healthcare industry frameworks allow organizations to navigate the complexities of QMSR and HIPAA updates while accelerating the delivery of life-saving digital health solutions. By engineering “Automated Trust” through Compliance as Code and high-availability architectures, providers can focus on clinical excellence rather than the fear of regulatory breaches. These methodologies transform technical debt into a strategic advantage, ensuring that telemedicine and AI-powered diagnostics operate on a foundation of absolute data integrity.

Achieving this level of maturity requires more than just technical tools; it requires a steady hand and a reliable long-term collaborator. As an Atlassian Gold Solution Partner with extensive experience in pharmaceutical and healthcare IT, we offer a global delivery model supported by specialized compliance experts who understand your unique operational constraints. We’re deeply invested in your long-term success, helping you bridge the gap between technical execution and high-level business outcomes through disciplined ServiceNow and Atlassian implementations.

Take the first step toward a more secure and agile future today. Explore our Strategic DevOps Consulting for Healthcare to begin your transformation. We look forward to supporting your journey toward scalable, compliant growth.

Frequently Asked Questions

Is DevOps safe for life-critical healthcare applications?

DevOps is inherently safer than traditional manual deployments because it replaces human error with automated, reproducible pipelines. By engineering “Automated Trust,” organizations ensure that every software iteration undergoes rigorous verification before reaching a clinical setting. This methodology provides the Precision, Pace, and Protection required to maintain patient safety in high-stakes environments where manual configuration errors could lead to catastrophic system failures.

How does DevOps impact HIPAA compliance and data privacy?

DevOps strengthens HIPAA compliance by transforming addressable safeguards into mandatory, automated technical controls within the delivery pipeline. Modern devops adoption in healthcare industry frameworks integrate multi-factor authentication and encryption protocols directly into the code, ensuring that data at rest and in transit remains protected by default. This shift allows for continuous monitoring and real-time remediation of privacy risks that manual audits might overlook.

What is the role of “Compliance as Code” in medical software development?

Compliance as Code translates complex regulatory requirements into executable scripts that automatically audit and enforce policies during the development lifecycle. This approach ensures that every code commit is checked against GxP and HIPAA standards before it can advance to production. It provides a transparent, version-controlled record of compliance that simplifies premarket submissions and satisfies the increasingly stringent demands of global health authorities.

Can DevOps be implemented in organizations with heavy legacy infrastructure?

DevOps is highly effective for legacy environments when implemented through a phased approach that utilizes containerization to isolate and modernize specific modules. By wrapping monolithic cores in microservices, organizations can update patient-facing features without disrupting the stability of underlying systems. This strategy allows healthcare providers to gradually reduce technical debt while maintaining the operational continuity of their critical clinical services.

What are the most common challenges when adopting DevOps in healthcare?

The primary hurdles include cultural resistance to rapid change, significant legacy technical debt, and the perceived conflict between Agile speed and validated stability. Successful devops adoption in healthcare industry initiatives require a fundamental shift in mindset where compliance is viewed as a functional requirement rather than a bottleneck. Overcoming these challenges necessitates a disciplined roadmap that balances engineering agility with the rigorous documentation standards required for medical software.

How do Atlassian tools like Jira and Confluence support healthcare DevOps?

Atlassian tools provide the essential “Single Source of Truth” required for maintaining comprehensive audit trails and transparent change management. Jira allows teams to track clinical workflows and compliance tasks with granular precision, while Confluence serves as a centralized repository for validated documentation and standard operating procedures. This integration fosters a culture of shared responsibility, ensuring that every stakeholder has visibility into the software’s regulatory status.

What is the difference between standard DevOps and GxP-validated DevOps?

Standard DevOps focuses on velocity and efficiency, whereas GxP-validated DevOps prioritizes rigorous proof that software performs its intended function safely and consistently. Validated pipelines require electronic signatures, automated verification protocols, and detailed traceability matrices that satisfy Good Practice regulations. This specialized approach ensures that the speed of continuous delivery never compromises the high standards of efficacy required for medical devices and pharmaceutical applications.

How long does it typically take to see ROI from healthcare DevOps adoption?

Organizations typically begin to see measurable ROI within six to twelve months as deployment downtime decreases and manual auditing costs are reduced. Long-term value is realized through faster time-to-market for digital health solutions and the mitigation of expensive compliance breach risks. While the initial investment in devops adoption in healthcare industry frameworks is significant, the resulting operational efficiency and scalable growth provide a sustainable competitive advantage.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.

What if your primary development platform could double as your most vigilant regulatory guardian? In an era where the cost of non-compliance can reach millions, many financial institutions still treat audit preparation as a manual, reactive exercise that stalls innovation. Leveraging jira for financial services compliance isn’t just about tracking tickets; it’s about architecting a strategic framework that bridges the gap between high-velocity engineering and the uncompromising standards of EBA, BaFin, and DORA. We understand the persistent tension between maintaining developer speed and the fear of audit failure due to fragmented documentation.

This guide demonstrates how to transform your existing workflows into a centralised, immutable audit trail that provides real-time visibility for risk management teams. You’ll learn the methodology for automating compliance reporting and securing data residency to meet the strict thresholds set by regulators in 2026. By the end of this article, you’ll have a clear roadmap for integrating governance directly into your technical delivery; this ensures that regulatory excellence becomes a natural byproduct of your operational rhythm rather than a bottleneck to your growth.

Key Takeaways

  • Discover how to pivot from reactive, manual documentation to a “Compliance as Code” model that ensures continuous oversight across the Atlassian ecosystem.
  • Understand the strategic advantages of Jira Cloud Enterprise, focusing on how robust data residency controls satisfy stringent national and regional sovereignty laws.
  • Learn to architect immutable workflows and automated history logs that prevent unauthorized approval bypasses while maintaining a centralized, audit-ready evidence trail.
  • Explore the integration of automated testing and DevOps pipelines to achieve seamless, end-to-end traceability from requirement to deployment.
  • Gain a structured roadmap for optimizing jira for financial services compliance, ensuring a secure and efficient migration of regulated workloads to modern cloud environments.

The financial sector is witnessing a fundamental shift in how governance is executed. Traditional oversight, once characterized by periodic, retrospective reviews, has been replaced by a demand for persistent, real-time visibility. As organizations face the complexities of Navigating the Regulatory Landscape, the limitations of manual spreadsheets and fragmented documentation have become clear. These legacy methods fail under the scrutiny of 2026 regulatory standards because they lack the immutability and granular traceability required to prove that every decision follows a defined risk protocol. By adopting jira for financial services compliance, global enterprises can transition to a “Compliance as Code” model, where regulatory requirements are baked directly into the technical lifecycle. This strategic approach creates a single source of truth that aligns software development with high-level risk management, ensuring that every action is documented, authorized, and ready for inspection.

Addressing EBA, BaFin, and DORA Requirements

The Digital Operational Resilience Act (DORA) demands that institutions demonstrate robust ICT risk management and reporting capabilities. Jira serves as the central engine for these requirements, allowing teams to map specific tickets to the five pillars of DORA, from risk management to third-party oversight. For firms adhering to European Banking Authority (EBA) outsourcing guidelines, the platform provides the necessary transparency to monitor external partners and ensure that security standards are consistently met. By utilizing jira for financial services compliance, organizations can build a framework where every ticket represents a record of trust. This creates an unbreakable chain of evidence that satisfies the rigorous expectations of BaFin and other national regulators, transforming compliance from a manual burden into a standardized, automated process. This focus on verified participation is increasingly vital across the fintech landscape, where platforms like tyriantrade.com are setting new standards for transparency in modern financial markets.

The Shift Toward Continuous Compliance

The objective for modern financial leaders is to move away from the frantic preparation of “audit season” and toward a state of constant, real-time readiness. By automating the collection of evidence through custom fields and history logs, firms drastically reduce the operational cost and human error associated with proving adherence to standards. This proactive stance allows technical managers to identify and remediate gaps before they escalate into regulatory findings. It fosters an environment where security and speed coexist, rather than compete. Continuous compliance is a strategic business enabler that accelerates market entry by ensuring that every release is born in a state of regulatory readiness.

Jira Cloud Enterprise: Architecting Security and Data Sovereignty

Jira Cloud Enterprise represents a strategic evolution for global financial institutions, offering a sophisticated security framework designed to meet the rigorous demands of modern regulators. While Atlassian manages the underlying cloud infrastructure, including physical security and platform availability, the institution retains responsibility for data classification, user permissions, and configuration. This shared responsibility model is essential for maintaining jira for financial services compliance, as it empowers organizations to tailor their security posture to specific operational risks. By leveraging Atlassian Access, technical leaders can implement centralized identity and access management, ensuring that only authorized personnel can interact with sensitive financial workflows; this creates a robust defensive layer that simplifies the complexities of user lifecycle management.

Data Residency and Sovereignty Strategies

In an increasingly fragmented regulatory environment, the ability to pin data to specific geographic regions is a non-negotiable requirement for compliance with local mandates such as those from BaFin in Germany. Global entities must navigate the complexities of international data transfers and the implications of the Schrems II ruling, which necessitates a granular approach to data sovereignty. Jira Cloud Enterprise allows for the management of multi-region instances, enabling firms to store data locally while maintaining a unified global operation. This capability is vital for institutions monitored by the Financial Crimes Enforcement Network, where the intersection of data location and reporting accuracy is critical for anti-money laundering efforts and the detection of illicit financial activity.

Advanced Security Layers for High-Stakes Environments

To further fortify the digital perimeter, Jira Cloud Enterprise introduces advanced security features like Bring Your Own Key encryption, providing organizations with total control over their data encryption keys. This level of technical rigor is complemented by IP allow-listing and mobile device management integrations, which restrict access to trusted networks and devices. Such measures provide the demonstrable governance that regulators now expect in 2026, where evidence of proactive risk mitigation is as important as the mitigation itself. Utilizing the Atlassian Trust Center offers auditors the necessary transparency and reassurance regarding the platform’s independent security certifications. For organizations seeking to align these technical capabilities with their unique regulatory obligations, a consultation with a strategic implementation partner can help bridge the gap between platform features and audit readiness. This collaborative approach ensures that your infrastructure provides visibility, verification, and validity at every level of the organization.

Implementing Robust Audit Trails: Workflows and Governance in Jira

Establishing a defensible regulatory posture requires more than just high-level policy; it necessitates the technical translation of those policies into the daily tools used by development and operations teams. When utilizing jira for financial services compliance, the primary objective is to move beyond simple task management toward a framework of “Precision, Proof, and Protection.” This is achieved by architecting workflows that act as unassailable gates, ensuring that no code reaches production without passing through every mandatory approval stage. By automating the collection of evidence through custom fields and background history logs, organizations create a persistent record of every decision made. This transformation allows technical managers to present a comprehensive, immutable audit trail to regulators, proving that the institution’s governance standards are being enforced at the level of individual tickets rather than just on paper.

A critical component of this strategy involves leveraging Jira Service Management to formalize Change Advisory Board (CAB) processes. By integrating change requests directly with development issues, teams achieve end-to-end traceability that links a specific business requirement to its technical execution and final approval. This structured approach balances team autonomy with organizational accountability, allowing developers to move quickly within the safety of defined guardrails. To ensure these configurations are optimized for both performance and scrutiny, many institutions rely on specialized Atlassian implementation services to bridge the gap between out-of-the-box functionality and the complex demands of financial audits.

Designing Immutable Workflows for Regulatory Approval

To satisfy the strict requirements of 2026 audits, workflows must be designed to prevent retrospective editing of records. By configuring specific workflow properties, such as setting jira.issue.editable to false in “Closed” or “Approved” states, administrators can lock issues once they reach a terminal status. This technical safeguard is often supplemented by digital signature requirements and mandatory multi-factor approval steps, ensuring that high-risk changes are verified by the correct stakeholders. Automating “Definition of Done” checklists further reinforces this by requiring that all compliance-related tasks, such as security scans or peer reviews, are completed before a ticket can transition to the next stage.

Advanced Permissions and Access Control Strategies

Effective governance relies on the principle of least privilege, where access is granted only to the extent necessary for a specific role. Configuring project-level permissions and issue security levels allows institutions to wall off sensitive data while maintaining operational transparency for the broader team. For external audits, organizations can establish “View Only” security levels, providing regulators with direct access to the evidence they need without risking the integrity of the data. The underlying audit log serves as the final layer of defense, meticulously tracking who changed what, where, and when, providing the granular visibility required to maintain a state of continuous regulatory readiness.

Beyond Tracking: Integrating Quality Assurance and DevOps for Compliance

Achieving true regulatory excellence requires a fundamental shift from passive ticket tracking to active, integrated validation within the software delivery lifecycle. By establishing a seamless connection between Jira, Bitbucket, and CI/CD pipelines, financial institutions can create an unbreakable link between a regulatory requirement and the specific code change that addresses it. This level of end-to-end traceability is indispensable for maintaining jira for financial services compliance, as it allows auditors to verify that every deployment has undergone the necessary security scans and peer reviews before reaching production. It effectively eliminates the visibility gap between development teams and risk management officers, providing executive leadership with a clear, data-driven view of the organization’s security posture. This approach ensures that compliance is not a final hurdle but a continuous thread woven into the fabric of technical delivery.

Automated Testing as a Compliance Validator

Automated testing serves as a primary engine for validating complex regulatory requirements at scale without sacrificing operational agility. By linking test execution results directly to Jira requirements, teams provide immediate evidence of adherence to standards like DORA or the EBA guidelines. Utilizing Software Test Automation Services empowers organizations to accelerate regression audits, ensuring that rapid release cycles don’t inadvertently introduce compliance vulnerabilities. These integrated systems can generate automated “Compliance Reports” that aggregate test data and coverage metrics, offering a transparent and objective record for internal and external stakeholders. This methodology transforms quality assurance from a cost center into a strategic asset that supports “Security, Speed, and Stability.”

Compliance as Code: Bridging Dev and Risk Management

While automation handles repetitive validation, Manual Testing remains a critical component for verifying complex financial logic and nuanced edge cases that automated scripts might overlook. This human oversight is essential for ensuring that subjective regulatory interpretations are correctly translated into technical functionality. Integrating these manual checks into a unified DevOps framework helps reduce “Compliance Debt” by identifying and remediating risks early in the development process. Expert DevOps Consulting helps organizations align their technical velocity with the necessary regulatory rigor, creating a culture where risk management is a shared responsibility. To ensure your QA framework meets the highest standards of audit readiness, reach out to our strategic advisors for a comprehensive evaluation of your integrated compliance workflows.

Jira for Financial Services Compliance: A Strategic Guide to Regulatory Excellence

Strategic Implementation: Optimising Jira for Financial Compliance

The successful deployment of jira for financial services compliance requires more than technical configuration; it demands a phased, strategic roadmap that accounts for the intricate dependencies of regulated data. Moving from legacy on-premise environments to a modernised cloud infrastructure is a transition that must be managed with surgical precision to avoid operational disruption. A specialized Atlassian Consulting partner provides the necessary expertise to navigate these complexities, ensuring that every workflow is optimised for auditability before a single byte of data is moved. By positioning compliance as a core component of your broader digital transformation, your organisation can leverage these rigorous standards to drive systemic improvements in efficiency and security. This proactive approach transforms regulatory obligations into a competitive advantage, establishing a foundation for “Stability, Scalability, and Success.”

Migration Strategies: Moving Regulated Data Safely

A secure transition begins with a comprehensive pre-migration audit of all existing workflows, custom fields, and permission schemes to identify potential compliance gaps. As organisations move away from Jira Data Center, following the end of new subscription sales on March 30, 2026, the focus shifts to maintaining continuity while adopting the advanced features of Jira Cloud Enterprise. Managing this transition without downtime requires a parallel-run strategy where workloads are migrated in calculated waves. This process provides an ideal opportunity for “pruning” legacy data; by removing obsolete records and streamlining configurations, institutions ensure a lean instance that’s easier to govern and defend during regulatory inspections. Such meticulous preparation ensures that jira for financial services compliance remains a robust, high-performance engine throughout the migration lifecycle.

Managed Support for Sustained Operational Stability

Ensuring long-term adherence to evolving standards requires more than a one-time implementation; it necessitates continuous oversight and proactive environment management. The role of Managed Outsourcing Services is vital here, providing the dedicated expertise needed for quarterly compliance health checks and iterative system tuning. These regular reviews identify emerging risks and ensure that the platform remains aligned with the latest requirements from DORA or the European Banking Authority. Training your internal teams to uphold the integrity of the compliance engine is equally critical, as human expertise must complement technical tools to maintain a state of perpetual readiness. This collaborative model ensures that your institution remains a reliable long-term collaborator with regulators, projecting an image of institutional maturity and operational excellence.

Future-Proofing Your Regulatory Framework with Atlassian

Transitioning to jira for financial services compliance allows your institution to move beyond manual oversight toward a model of continuous, automated governance. By architecting immutable workflows and integrating quality assurance directly into your delivery pipeline, you ensure that every technical decision is backed by a verifiable audit trail. This strategic alignment doesn’t just satisfy regulators; it empowers your teams to innovate with confidence within secure, predefined guardrails. As an Atlassian Gold Solution Partner with ISO 9001 and ISO 27001 certifications, we specialize in guiding global enterprises through the complexities of highly regulated sectors like finance and pharma. We understand that operational stability is the cornerstone of your reputation. Our methodology focuses on delivering a resilient infrastructure that bridges the gap between high-velocity engineering and uncompromising security standards. Secure your financial future with Test Triangle’s Atlassian Consulting Services and transform your compliance engine into a catalyst for operational excellence. We’re ready to help you navigate the path toward long-term stability and scalable growth.

Frequently Asked Questions

Is Jira Cloud compliant with the Digital Operational Resilience Act (DORA)?

Jira Cloud supports DORA compliance by providing the necessary framework for ICT risk management, incident reporting, and operational resilience. While Atlassian provides the secure infrastructure, the institution is responsible for configuring workflows that align with the five pillars of DORA. This collaborative model ensures that risk management is integrated directly into technical operations; this provides the transparency and traceability required for modern regulatory inspections.

How does Jira handle data residency for German financial institutions under BaFin?

Atlassian allows German financial institutions to satisfy BaFin requirements by pinning primary data to the Frankfurt region. This geographic control ensures that sensitive financial information remains within the specified jurisdiction, addressing strict national sovereignty laws. By leveraging these data residency settings, organizations maintain high standards of “Privacy, Protection, and Provenance.” This localized approach mitigates the risks associated with international data transfers and ensures a stable regulatory posture.

Can Jira be used to automate evidence collection for financial audits?

Jira automates the collection of audit evidence by utilizing custom fields, mandatory transition screens, and comprehensive history logs that track every issue modification. This systemic approach replaces manual spreadsheets with a centralized, immutable record of all activities and approvals. By configuring jira for financial services compliance in this way, technical managers can generate real-time reports that prove adherence to internal controls. This reduces the administrative burden of audit preparation and enhances the accuracy of regulatory filings.

What is the difference between Jira Standard and Jira Cloud Enterprise for compliance?

Jira Cloud Enterprise offers significant compliance advantages over the Standard plan, including unlimited instances and advanced data residency controls across multiple global regions. While Standard provides basic tracking, Enterprise includes Atlassian Access for centralized identity management and a 99.95% uptime SLA. These high-level features are essential for global institutions that require “Security, Scalability, and Sovereignty” to manage complex digital infrastructures across diverse regulatory landscapes.

Does Atlassian offer a Business Associate Agreement (BAA) or equivalent for financial services?

Atlassian provides a Financial Services Addendum (FSA) and specialized compliance documentation that address the specific regulatory needs of the financial sector. While a Business Associate Agreement (BAA) is specific to healthcare, the FSA covers critical requirements such as audit rights and data security standards. These legal frameworks reassure global enterprises that their partnership with Atlassian is built on a foundation of “Trust, Transparency, and Total Accountability.”

How can we ensure that developers don’t bypass compliance gates in Jira?

Organizations ensure that developers don’t bypass compliance gates by implementing immutable workflow properties and mandatory approval steps that require digital signatures. By setting specific transition conditions and validators, administrators can prevent issues from moving forward until all regulatory requirements are met. This technical enforcement creates a disciplined environment where governance is a natural byproduct of the development lifecycle; this ensures that no code reaches production without authorized verification.

What are the key Jira apps for financial services compliance?

Key apps for enhancing jira for financial services compliance include ScriptRunner for complex automation, Xray for integrated test management, and specialized audit log exporters. These tools extend the native capabilities of the platform to provide the granular visibility and reporting required for financial audits. By integrating these industry-leading software platforms, institutions can build a comprehensive compliance engine that bridges the gap between technical execution and business outcomes.

How does Test Triangle assist with Jira compliance implementation?

Test Triangle serves as a reliable long-term collaborator by providing specialized Atlassian Consulting and managed support tailored to the unique needs of the financial sector. Our team focuses on architecting secure, audit-ready environments that satisfy EBA and DORA requirements while maintaining operational agility. Through proactive environment management and systemic improvement, we empower organizations to achieve “Precision, Performance, and Peace of Mind” in their digital transformation journey.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.

With Gartner predicting that 80% of engineering organizations will adopt internal development platforms by the close of 2026, the era of fragmented, DIY toolchains has reached its expiration. You’ve likely recognized that maintaining high-velocity delivery in complex hybrid environments is becoming unsustainable as specialized talent shortages persist and visibility gaps widen across the development lifecycle. Crafting a resilient devops strategy for chief technology officers is no longer merely an exercise in tool selection; it’s a strategic necessity to orchestrate a unified ecosystem that delivers precision, pace, and performance.

We understand that your objective is to evolve your technical function from a technical cost center into a reliable engine for digital transformation. This framework provides a high-level roadmap to help you transition from fragmented tooling to a capacity-driven ecosystem that scales with your business goals. You’ll gain insights into unifying ITSM and DevOps platforms to reduce time-to-market, ensuring governance through automated compliance, and leveraging the 2026 ServiceNow “Australia” release to secure a sustainable competitive advantage.

Key Takeaways

  • Transition from managing siloed teams to a platform engineering culture where DevOps Capacity serves as a primary metric for executive performance and organizational scalability.
  • Develop a resilient devops strategy for chief technology officers that unifies CI/CD pipelines and integrates DevSecOps into the earliest stages of the development lifecycle.
  • Align executive strategic roadmaps with technical execution by bridging the visibility gap between Atlassian Jira Align and ServiceNow ITSM platforms.
  • Address the persistent talent gap by leveraging flexible staffing models and managed DevOps services to maintain complex, hybrid-cloud infrastructures without compromising security.
  • Implement a 2026 strategic roadmap that converts fragmented tooling into a unified, capacity-driven ecosystem designed to accelerate time-to-market.

The Evolution of DevOps Strategy: A 2026 Mandate for CTOs

The landscape of software delivery has fundamentally changed, moving beyond the era where DevOps was treated as a siloed department or a collection of scripts. For the modern CTO, a devops strategy for chief technology officers now demands a transition toward platform engineering, where the goal is to provide a frictionless, self-service experience for developers. This evolution is driven by the realization that fragmented automation efforts often create more technical debt than they solve. By 2026, successful leaders are those who treat the DevOps philosophy as a foundational cultural asset, ensuring that every automation initiative aligns directly with long-term digital transformation goals. This shift requires a disciplined focus on organizational progress through the combination of human expertise and technical tools, moving away from reactive firefighting toward proactive ecosystem management.

From Tool-Centric to Capacity-Centric Leadership

DevOps Capacity is the primary metric for 2026 CTOs, representing the total bandwidth an organization possesses to innovate while maintaining the stability of current production environments. This metric forces a departure from vanity statistics like the number of deployments per day, focusing instead on the strategic balance between “run” and “build” activities. To optimize this, leaders must evaluate the “Enabler” versus “Doer” ratio within their engineering teams. A high-performing platform team acts as an enabler, creating the guardrails and automated environments that allow product teams to be the doers. When this ratio is balanced, the organization achieves a state of stability, speed, and scalability, significantly reducing the cognitive load on developers and accelerating the delivery of value-added features.

The Business Impact of Strategic DevOps Maturity

Mature DevOps practices aren’t just technical achievements; they’re significant drivers of market share and customer retention. When an organization can deploy with high frequency without security compromises, it responds to market shifts faster than competitors trapped in manual release cycles. Strategic maturity involves reducing operational risk through standardized, repeatable infrastructure that eliminates the inconsistencies of manual environments. By leveraging Atlassian implementation services to unify tracking and managed outsourcing services to handle infrastructure complexity, CTOs can transform DevOps into a predictable engine of business agility. This approach ensures that technical debt reduction isn’t a separate project but a continuous, automated byproduct of a healthy delivery pipeline that empowers the business to scale with confidence.

Designing a Resilient Framework: The Three Pillars of Modern DevOps

A resilient framework requires more than just automation; it demands a structured approach to orchestration across your entire digital estate. When building a devops strategy for chief technology officers, the focus must shift toward three core pillars that ensure stability while accelerating delivery. This framework serves as the strategic blueprint for scaling digital operations without compromising on security or governance. By 2026, the transition from fragmented, siloed automation to a unified ecosystem is the only way to manage the increasing complexity of hybrid and multi-cloud environments.

Pillar 1: Automated Governance and Security

Governance in 2026 means moving beyond basic scripts to intelligent, policy-driven workflows. This is particularly vital for organizations in highly regulated industries like finance or healthcare where Compliance-as-Code is now a requirement to meet standards like GDPR, HIPAA, and PCI-DSS. By integrating software qa services directly into the delivery stream, you ensure that security isn’t a final hurdle but a continuous process. This proactive stance addresses the OWASP Top 10 through automated security testing that runs with every commit. Leaders who succeed in implementing DevOps at this level find that security becomes an enabler of speed rather than a blocker, providing the peace of mind that comes from systemic risk reduction.

Pillar 2: Platform Engineering and Developer Experience (DevEx)

Pillar 3: Data-Driven Continuous Improvement

Data is the final pillar. You can’t improve what you don’t measure. Utilizing DORA metrics to track velocity and stability provides the “Radical Transparency” needed for executive oversight. In 2026, AI-driven insights are no longer optional for maintaining a competitive edge. Analysis shows that teams using AI-powered testing frameworks achieve 83% test coverage, a significant increase from the 54% achieved with traditional methods. These feedback loops allow for predictive failure prevention and the implementation of self-healing systems. This data-driven approach ensures your ecosystem remains resilient under pressure and allows for the continuous optimization of your delivery pipeline.

If you’re ready to modernize your infrastructure, you might consider how a tailored consultation can align these pillars with your specific business objectives.

Platform Synergy: Leveraging Atlassian and ServiceNow for Governance

Achieving a “Single Pane of Glass” across the entire software development lifecycle (SDLC) remains a top priority for technology leaders seeking to eliminate visibility gaps. A robust devops strategy for chief technology officers in 2026 relies on the synergy between Atlassian and ServiceNow to bridge the historic divide between engineering velocity and operational stability. By integrating these industry-leading platforms, you create a unified governance layer that translates raw technical output into actionable business intelligence. This orchestration ensures that your digital transformation isn’t just fast, but also aligned with the broader corporate mission, providing a disciplined foundation for long-term growth.

Strategic alignment often fails when executive roadmaps don’t reflect real-world engineering capacity. Through specialized Atlassian Consulting, organizations can leverage Jira Align to synchronize high-level objectives with the daily tasks of development teams. A precise Atlassian implementation provides the scalable project tracking necessary to manage complex portfolios, ensuring that resources are allocated to the highest-value initiatives. This visibility allows CTOs to pivot with confidence, backed by real-time data from the engineering floor, while maintaining the rigorous standards required in global enterprise environments.

While Atlassian drives the development journey, ServiceNow implementation acts as the critical bridge to IT Service Management (ITSM). The 2026 ServiceNow “Australia” release, scheduled for broad production upgrades by mid-June, introduces enhanced capabilities for automating the connection between CI/CD pipelines and change management records. This integration reduces manual intervention and eliminates the friction often found in release cycles. By automating the flow of information between Jira and ServiceNow, you achieve Visibility, Velocity, and Value, turning your DevOps function into a transparent and predictable business asset.

Unifying the Enterprise Ecosystem

Consolidating your stack around Jira, Bitbucket, and Confluence creates a seamless developer journey that minimizes context switching and improves team morale. This consolidation directly addresses the pain of tool sprawl, which often leads to fragmented data and security vulnerabilities. When combined with comprehensive IT service management solutions, these platforms provide a disciplined framework for incident response and workflow optimization. It’s about ensuring your teams remain focused on building rather than maintaining their own toolsets, allowing for a more versatile and globally-minded engineering culture.

Strategic Asset Management and Compliance

Automated governance requires more than just code; it requires an immutable audit trail that stands up to scrutiny. Integrating platform logging across the ecosystem ensures that every change is documented, meeting stringent global regulatory standards for data residency and sovereignty. This unified approach also allows for better management of software licenses and cloud spend through centralized oversight. By managing these assets strategically, you reduce unnecessary costs and ensure that your global cloud deployments remain compliant with evolving international laws, providing the peace of mind that comes from systemic risk reduction.

Solving the Talent Gap: Strategic Staffing Models for 2026

The global demand for skilled DevOps professionals continues to outpace supply, creating a strategic bottleneck for organizations aiming to execute a sophisticated devops strategy for chief technology officers. As of 2026, the average salary for a DevOps engineer in the US has reached approximately $140,000, with senior roles often exceeding $180,000. For the CTO, solving this talent gap requires a move away from traditional, slow-moving recruitment toward more agile, capacity-driven models. By leveraging specialized staffing solutions, you can scale your engineering capacity without the prohibitive overhead of permanent headcount, ensuring your roadmap remains on track even in a volatile labor market.

In highly regulated sectors such as Pharmaceuticals or Finance, the challenge is even more acute. Sourcing talent that understands both the technical CI/CD pipeline and the nuances of GxP or banking regulations is exceptionally difficult. A disciplined approach to staffing involves identifying partners who provide pre-vetted experts familiar with automated compliance and security protocols. This ensures that your technical evolution doesn’t stall due to a lack of specialized knowledge, providing the peace of mind that comes from systemic reliability and expertise.

In-House vs. Outsourced DevOps: An ROI Comparison

Evaluating the total cost of ownership (TCO) for a DevOps function reveals that permanent hires often involve hidden expenses, including recruitment fees, training, and retention incentives. Managed DevOps Services offer a compelling alternative by providing immediate access to a broad pool of expertise at a predictable cost. This model is particularly effective for “Burst Capacity,” allowing you to scale up for major cloud migrations or platform upgrades without long-term commitment. The following table illustrates the strategic trade-offs between these two models:

FeatureIn-House Permanent HiresManaged DevOps Services
Hiring CycleTypically 3 to 6 monthsImmediate to 2 weeks
Expertise DepthSpecific to individual hiresAccess to full consultant pool
ScalabilityDifficult and slowHighly flexible and rapid
Risk ProfileHigh (attrition risk)Low (contractual stability)

Remote and Offshore Talent Integration

Managing global, distributed DevOps engineering teams requires a focus on cultural and technical alignment. To succeed, you must establish clear communication protocols and standardized toolsets that transcend time zones. Utilizing specialized IT staffing services allows you to tap into offshore talent pools while maintaining the high standards of quality and security your enterprise demands. This approach not only reduces time-to-hire but also provides a versatile, globally-minded workforce capable of supporting complex infrastructures around the clock. By integrating these resources into your core platform engineering culture, you achieve a state of Stability, Precision, and Scalable Growth.

If you need to scale your engineering team quickly with specialized talent, contact our staffing experts to discuss a customized model for your organization.

DevOps Strategy for Chief Technology Officers: The 2026 Strategic Framework

Executing Your Roadmap: How Test Triangle Accelerates Transformation

Test Triangle acts as more than a service provider; we are a strategic visionary and practical collaborator for global enterprises navigating the complexities of modern software delivery. Executing a devops strategy for chief technology officers requires a nuanced understanding of how technical tools, human talent, and business governance intersect to drive organizational progress. We provide the institutional maturity needed to transition from fragmented, siloed automation to a unified, capacity-driven ecosystem. Our methodology connects deep Atlassian expertise with specialized staffing models to ensure that your transformation roadmap remains both ambitious and achievable in a volatile technological landscape.

A Holistic Approach to IT Service Management

Operational excellence is only achieved when development speed is balanced by rigorous governance and systemic reliability. By integrating comprehensive IT Service Management solutions into your core DevOps strategy, we bridge the historic divide between innovation and stability. Our strategic partnerships with AWS and ServiceNow allow us to orchestrate environments that are secure, compliant, and highly performant. Our proven success in the pharmaceutical sector, for instance, demonstrates our ability to scale DevOps functions while maintaining strict adherence to global compliance standards, ensuring that digital evolution never comes at the cost of regulatory risk. This holistic approach provides the Stability, Security, and Scalability required for high-stakes enterprise environments.

Your Long-Term Collaborator for Scalable Growth

We’re deeply invested in your organization’s long-term success through a disciplined focus on risk reduction and empowerment found in large-scale technological evolution. Whether you require project-based DevOps Consulting or the sustained support provided by Managed Outsourcing Services, our delivery models remain adaptable to your specific business objectives. We don’t just implement tools; we foster a platform engineering culture that empowers your teams to build, deploy, and scale with confidence. This partnership provides the Precision, Pace, and Power necessary to thrive as you navigate the 2026 ServiceNow “Australia” release and beyond, positioning your company as a leader in digital maturity.

The journey from an initial assessment to full-scale platform optimization begins with a clear understanding of your current DevOps capacity and technical debt. By identifying visibility gaps and talent shortages early, we help you build a resilient framework that delivers tangible business value and reduces time-to-market. Contact us today to begin your comprehensive 2026 devops strategy for chief technology officers assessment and secure a steady hand for your digital transformation journey.

Orchestrating Future-Proof Digital Ecosystems

The transition toward platform engineering and capacity-driven metrics represents a fundamental shift in how successful enterprises deliver value. By unifying the Atlassian and ServiceNow ecosystems, you establish the visibility and governance necessary to scale without security compromises. Addressing the specialized talent gap through flexible staffing models ensures your roadmap remains resilient against market volatility, providing the peace of mind that comes from systemic stability. A robust devops strategy for chief technology officers is no longer just a technical objective; it’s a strategic mandate for sustainable growth in 2026.

As an Atlassian Gold Solution Partner and ServiceNow Premier Partner with a global delivery footprint across Europe, North America, and Asia, Test Triangle acts as a reliable long-term collaborator for your digital transformation. We’re committed to helping you navigate this complex landscape with precision and institutional maturity. Partner with Test Triangle for your 2026 DevOps Strategy to secure a steady hand for your organization’s future. We look forward to empowering your engineering teams and driving your long-term operational success.

Frequently Asked Questions

What are the key components of a DevOps strategy for CTOs in 2026?

A successful devops strategy for chief technology officers in 2026 prioritizes platform engineering, DevSecOps, and AI-driven observability. These components work together to create a unified, capacity-driven ecosystem that reduces cognitive load on developers. By focusing on internal development platforms and automated governance, CTOs can ensure that technical execution aligns with long-term digital transformation goals and organizational stability.

How does platform engineering differ from traditional DevOps?

Platform engineering focuses on building internal development platforms (IDPs) that provide “Golden Paths” for developers, whereas traditional DevOps often relied on manual collaboration between siloed teams. Gartner predicts that 80% of software engineering organizations will adopt these platforms by 2026. This shift empowers developers through self-service infrastructure, allowing them to focus on product innovation rather than complex pipeline maintenance.

How can Atlassian tools improve my DevOps delivery speed?

Atlassian tools like Jira Software 12 and Bamboo 13 improve delivery speed by unifying the developer journey from planning to deployment. These major versions support modern requirements like Java 25 and Spring 7, ensuring your stack remains performant and secure. By integrating Jira Align with executive roadmaps, you achieve the visibility needed to allocate resources effectively and accelerate time-to-market.

What is the ROI of outsourcing DevOps to a managed service provider?

The ROI of outsourcing DevOps to a managed service provider is realized through reduced total cost of ownership and immediate access to specialized expertise. Instead of navigating a three to six month hiring cycle for a senior engineer with a $180,000 salary, you gain burst capacity and rapid scalability. This model provides the peace of mind derived from contractual stability and systemic risk reduction.

How do I ensure security and compliance within an automated DevOps pipeline?

Ensuring security within an automated pipeline requires integrating DevSecOps and “Compliance-as-Code” directly into the CI/CD stream. Automated testing frameworks now achieve up to 83% test coverage when powered by AI, significantly mitigating vulnerabilities like the OWASP Top 10. This proactive stance ensures that governance is maintained across global cloud deployments without slowing down the release cycle or compromising data residency.

What are the best staffing models for scaling a DevOps team globally?

The most effective models for 2026 combine permanent core leadership with flexible offshore or managed service resources. This hybrid approach addresses the talent gap by tapping into global expertise while maintaining cultural and technical alignment. Utilizing specialized IT staffing services allows CTOs to scale capacity rapidly for major migrations or platform upgrades without the long-term overhead of permanent headcount.

How does ServiceNow integration benefit a DevOps environment?

ServiceNow integration bridges the visibility gap between engineering velocity and IT Service Management (ITSM). The 2026 “Australia” release enhances this by automating change management records directly from CI/CD pipelines, reducing manual friction. This synergy creates a “Single Pane of Glass” for the entire SDLC, ensuring that every deployment is documented and compliant with stringent global regulatory standards.

Why should a CTO prioritize “DevOps Capacity” over simple automation?

Prioritizing DevOps Capacity over simple automation ensures that your engineering organization has the bandwidth to innovate while maintaining production stability. A comprehensive devops strategy for chief technology officers treats capacity as a primary performance metric. While automation replaces manual tasks, capacity management balances the “Enabler” versus “Doer” ratio to drive long-term business agility and scalable growth.

Paul Guy

Article by

Paul Guy

Paul serves as the Marketing Director at Test Triangle, where he leads a global team in driving growth through strategic B2B marketing and brand communications. With a strong emphasis on measurable outcomes and sustainable performance, he plays a pivotal role in aligning marketing functions to enhance customer engagement and accelerate business impact. Under his leadership, marketing initiatives have consistently delivered significant returns on investment, elevated brand visibility, and strengthened the company's presence across key markets.